

FlowAnalyzer
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
api-securityapi-security-testingauthentication-authorization+5
184
manuelberrueta/flowanalyzerFlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 mohamedation/pwnedcheck
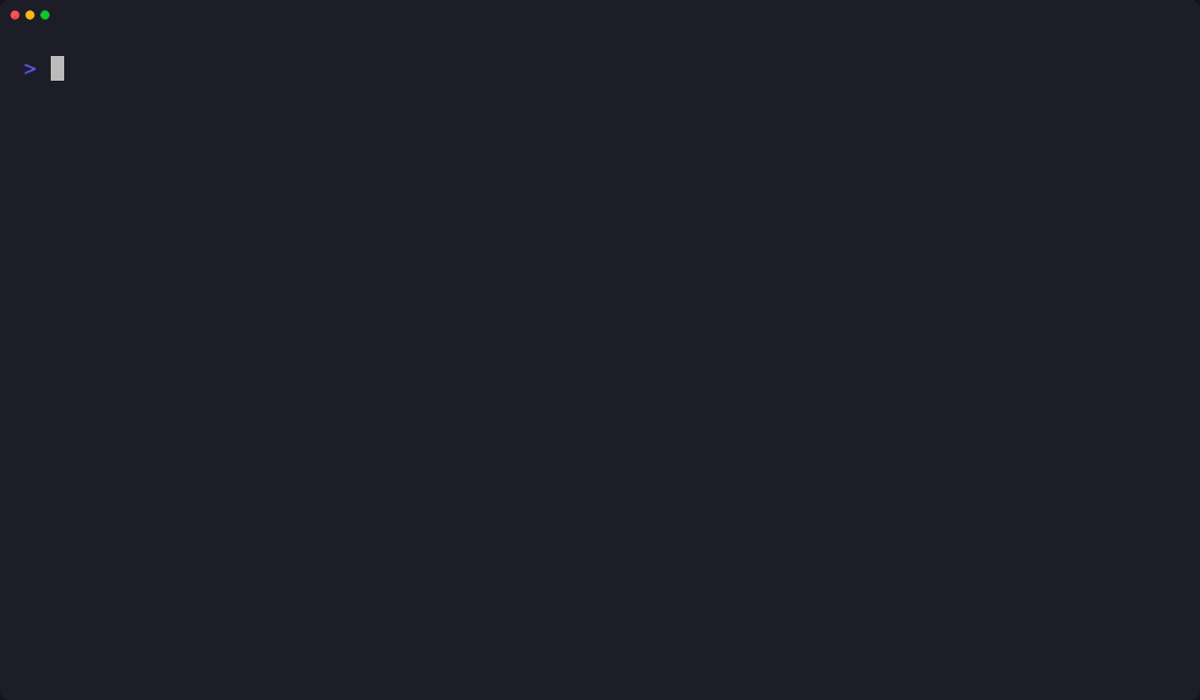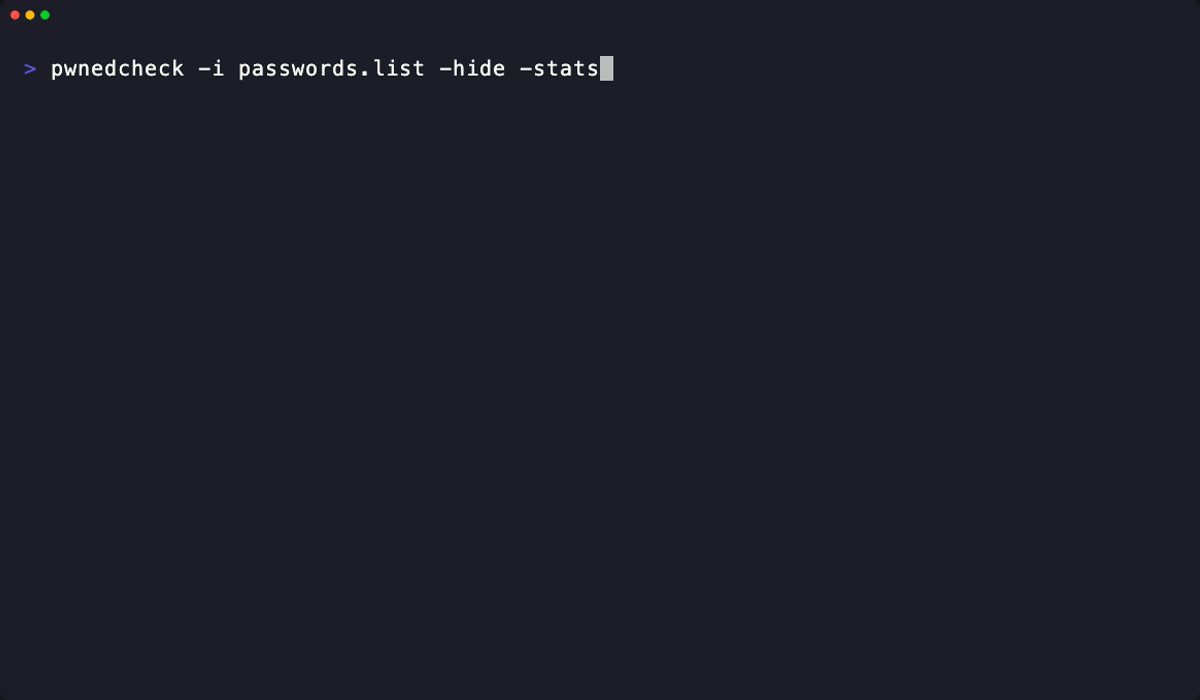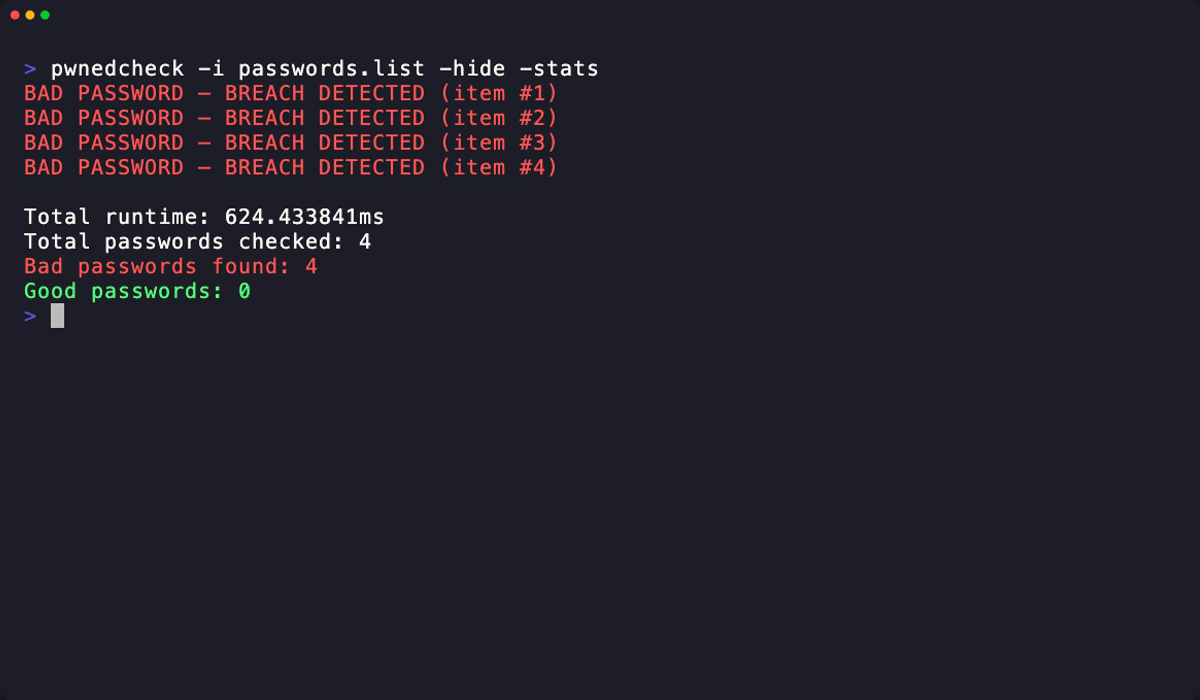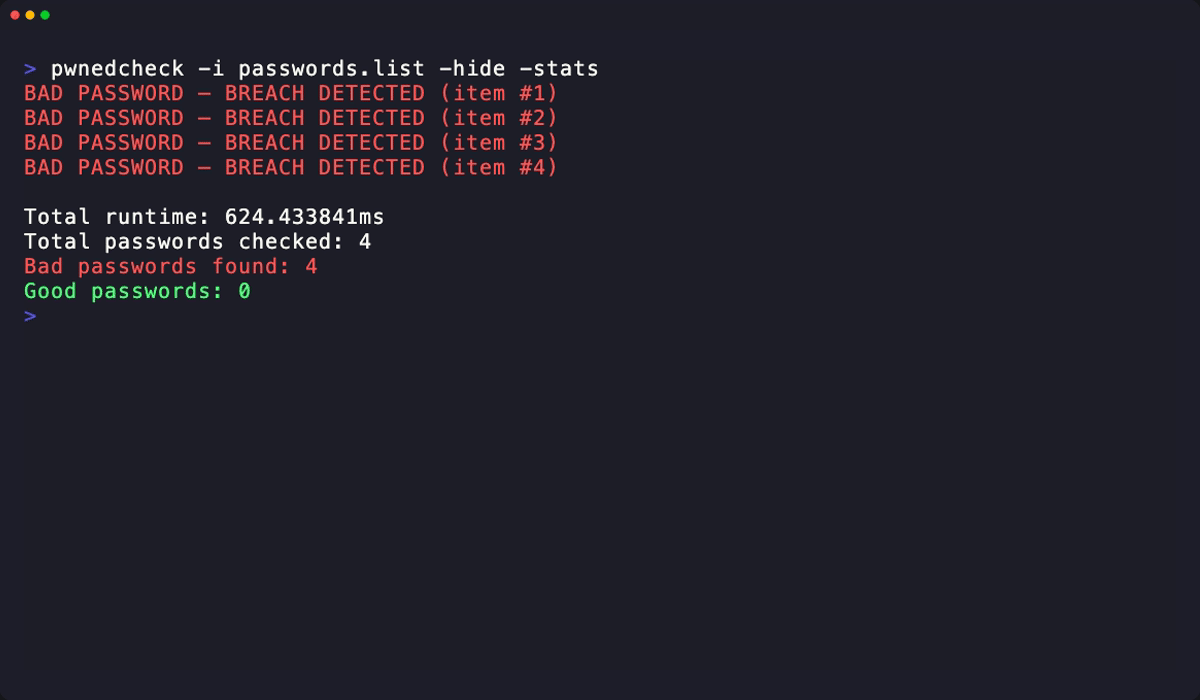
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
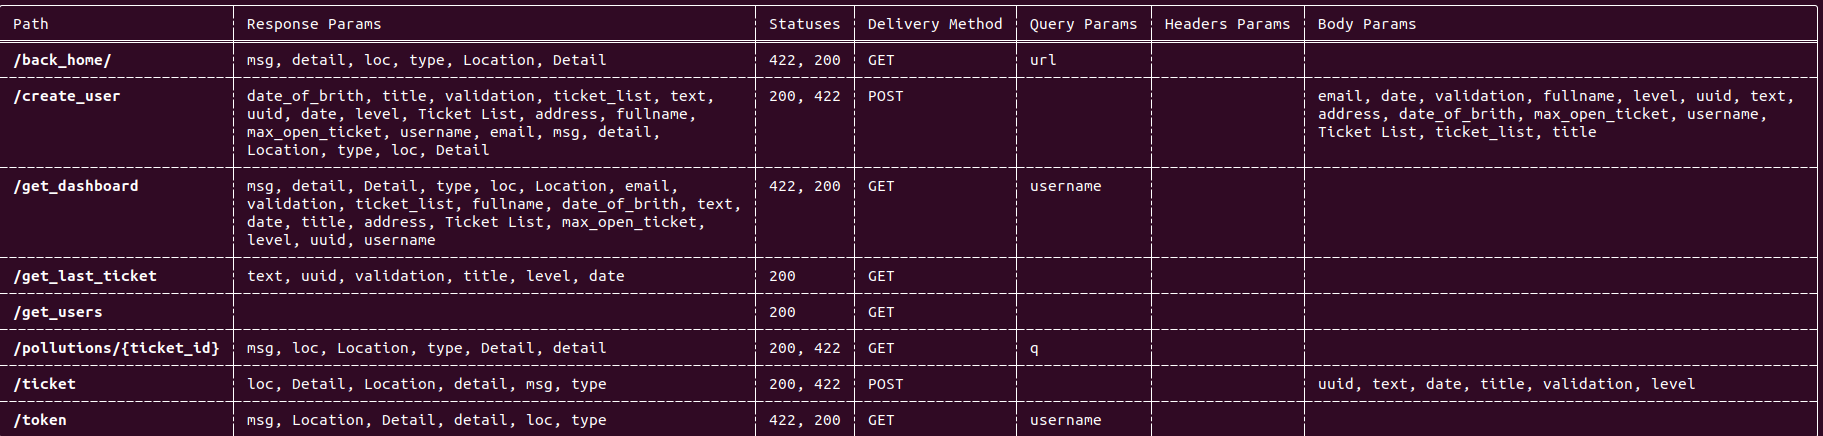 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
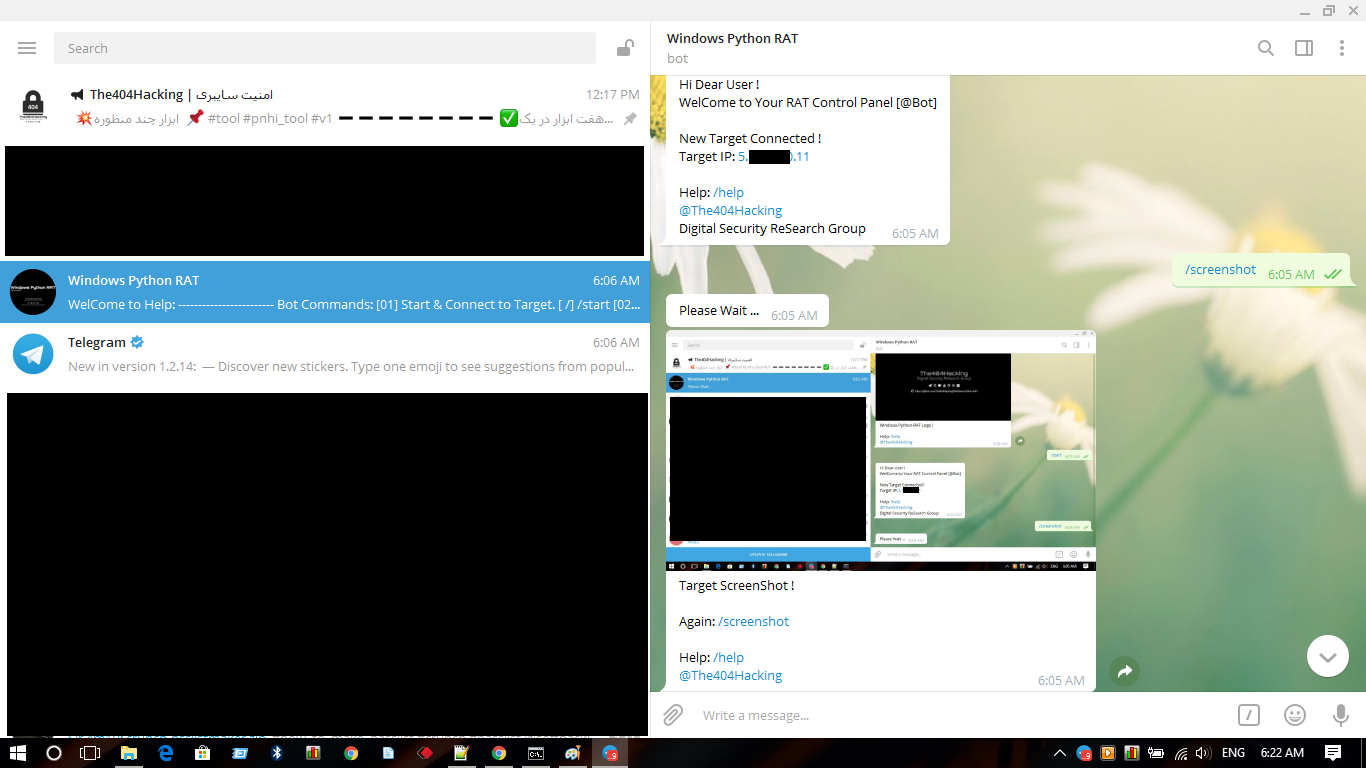 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 ronamosa/cve-2026-18953
PoC for CVE-2026-18953 — arbitrary file write (CWE-22) in awslabs.aws-transform-mcp-server's get_resource tool via the savePath parameter
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 ackemed/cve-2026-1529-poc-keycloak-unauthorized-registration-via-improper-invitation-token-validation
Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…
 george0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-
Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…
 fevar54/cve-2026-35616-detector.py
Detector de CVE-2026-35616: identifica servidores FortiClient EMS vulnerables (7.4.5-7.4.6).
 malhyuk/cve-2026-59243
Proof-of-concept for CVE-2026-59243 demonstrating JWT signature bypass in Apache Airflow FAB Auth Manager's Azure AD OAuth callback due to insecure…
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…