
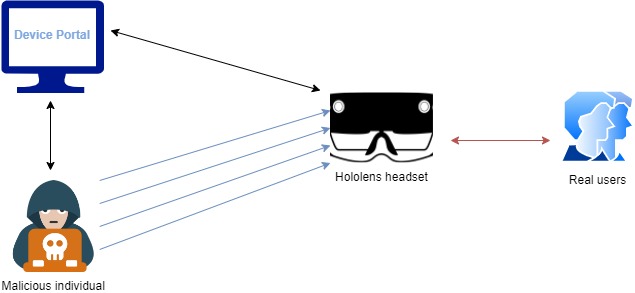
CVE-2024-57972
 tania-silva/cve-2024-57972
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
api-securityexploitationhardware-iot-security+2
tania-silva/cve-2024-57972Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
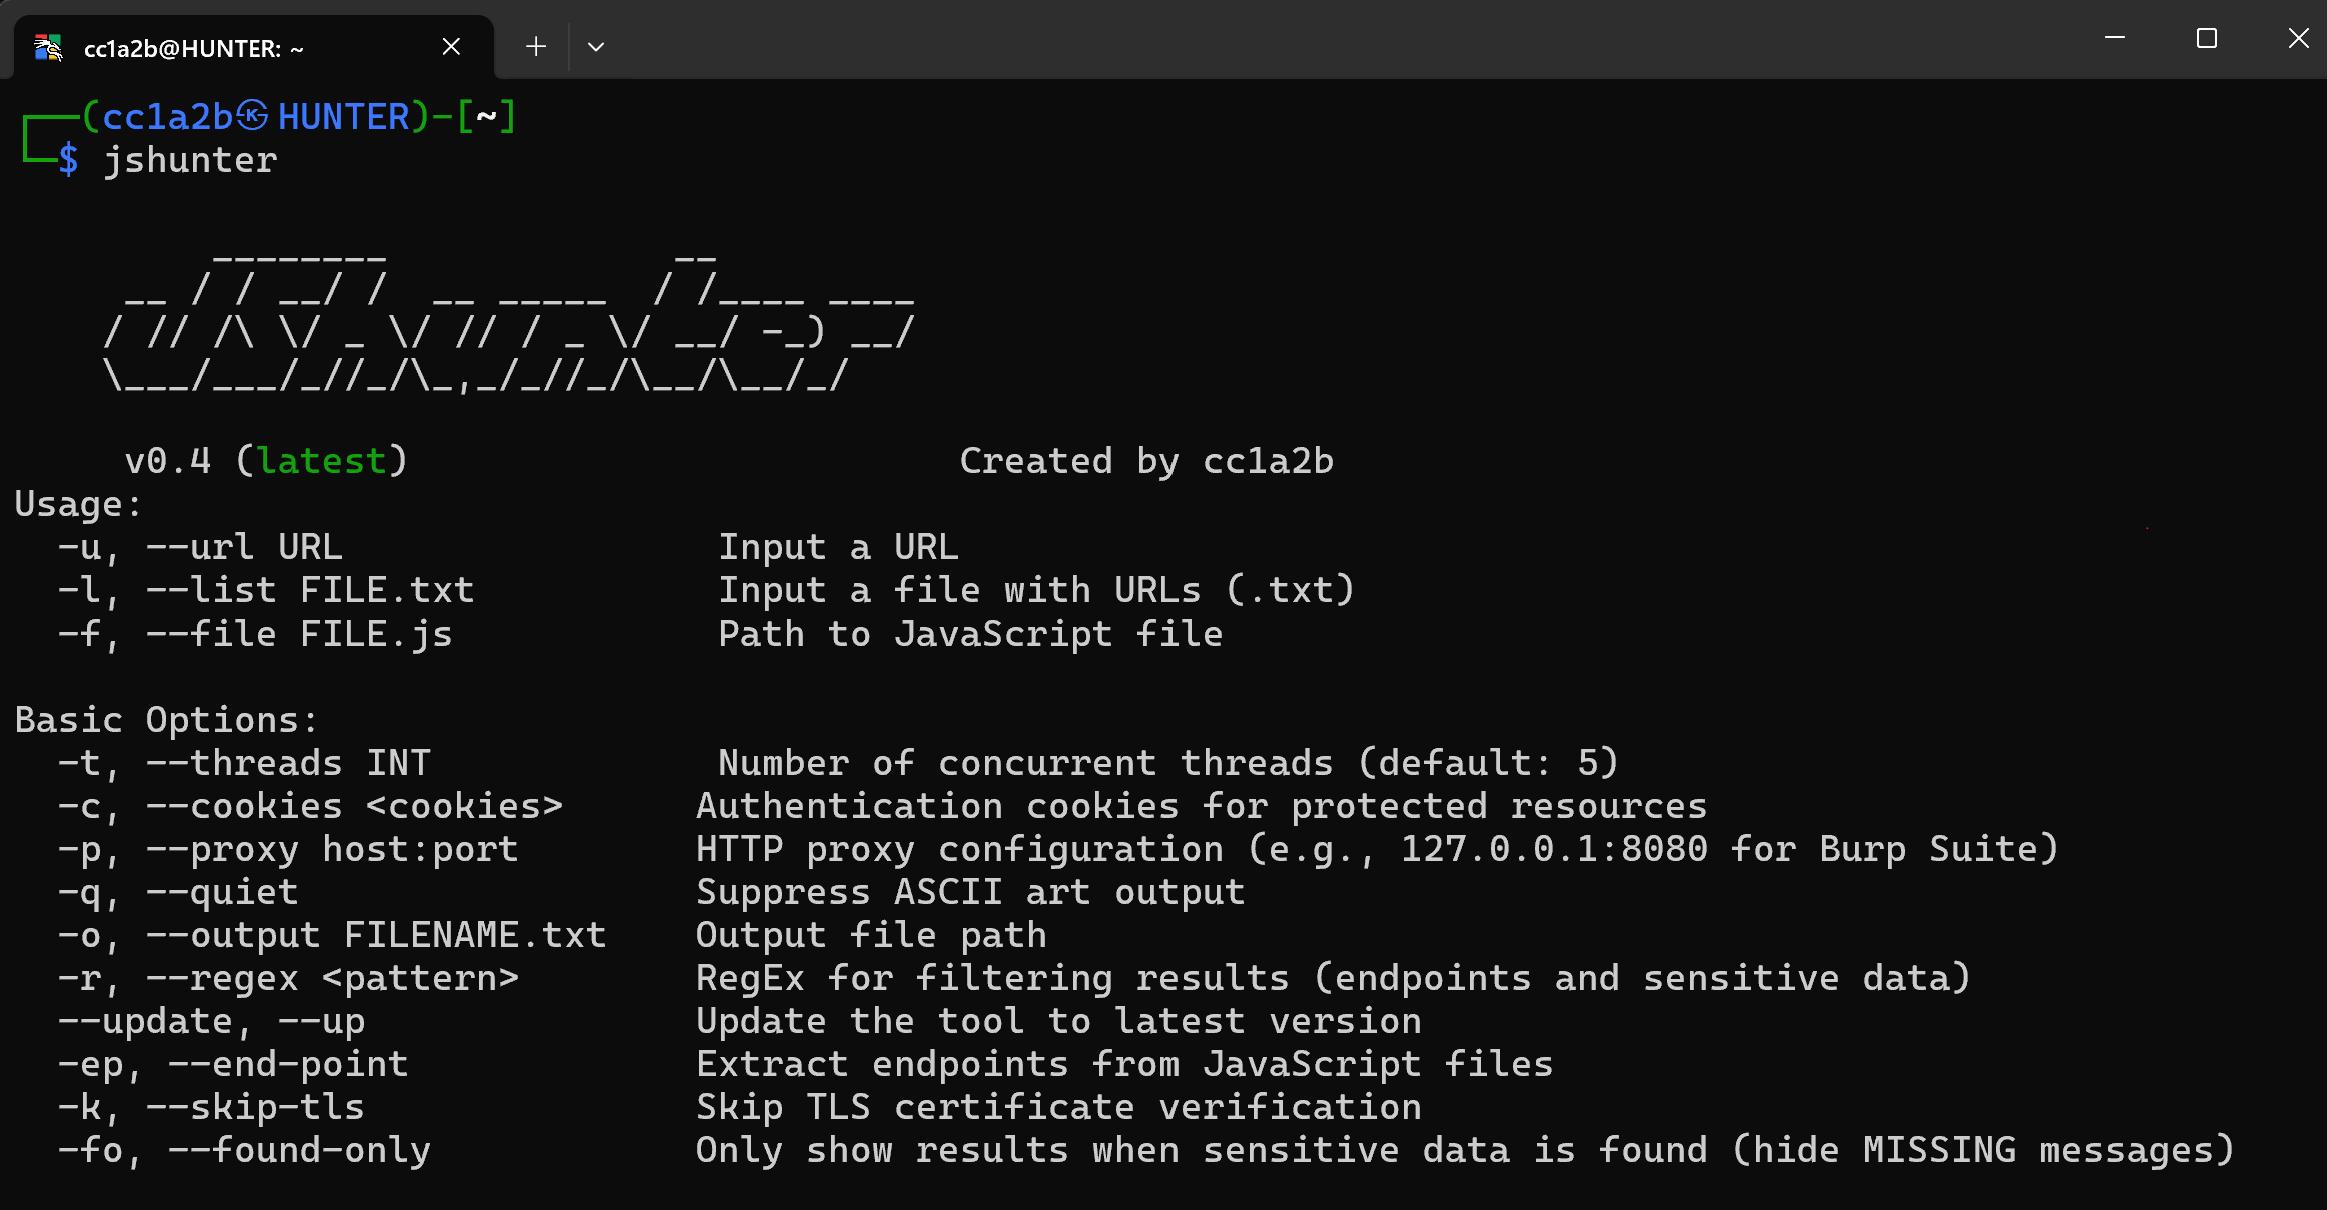 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
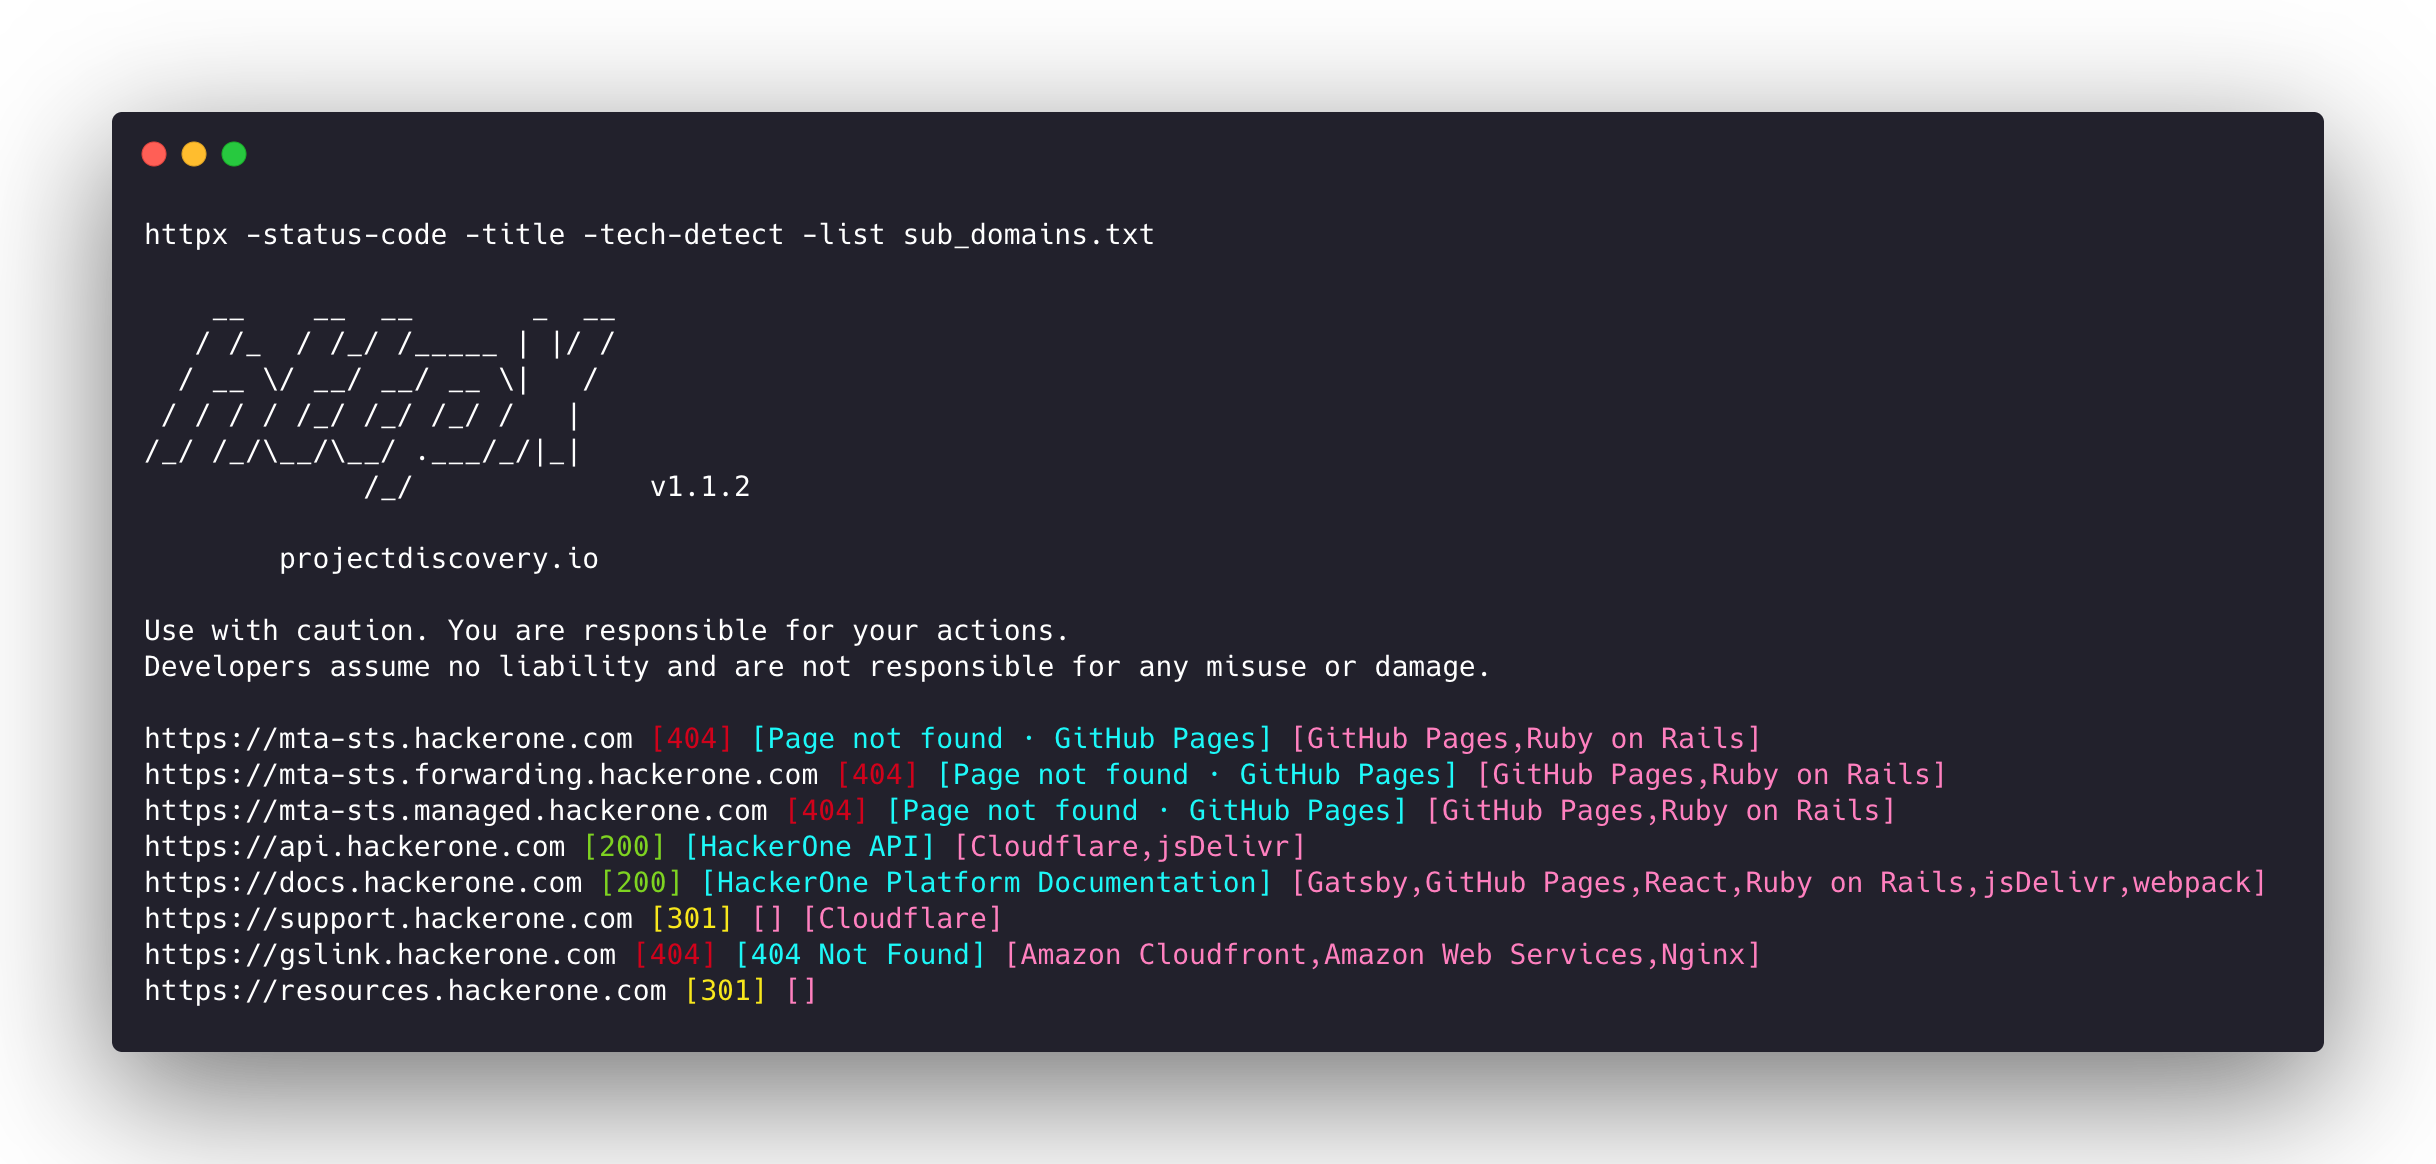 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
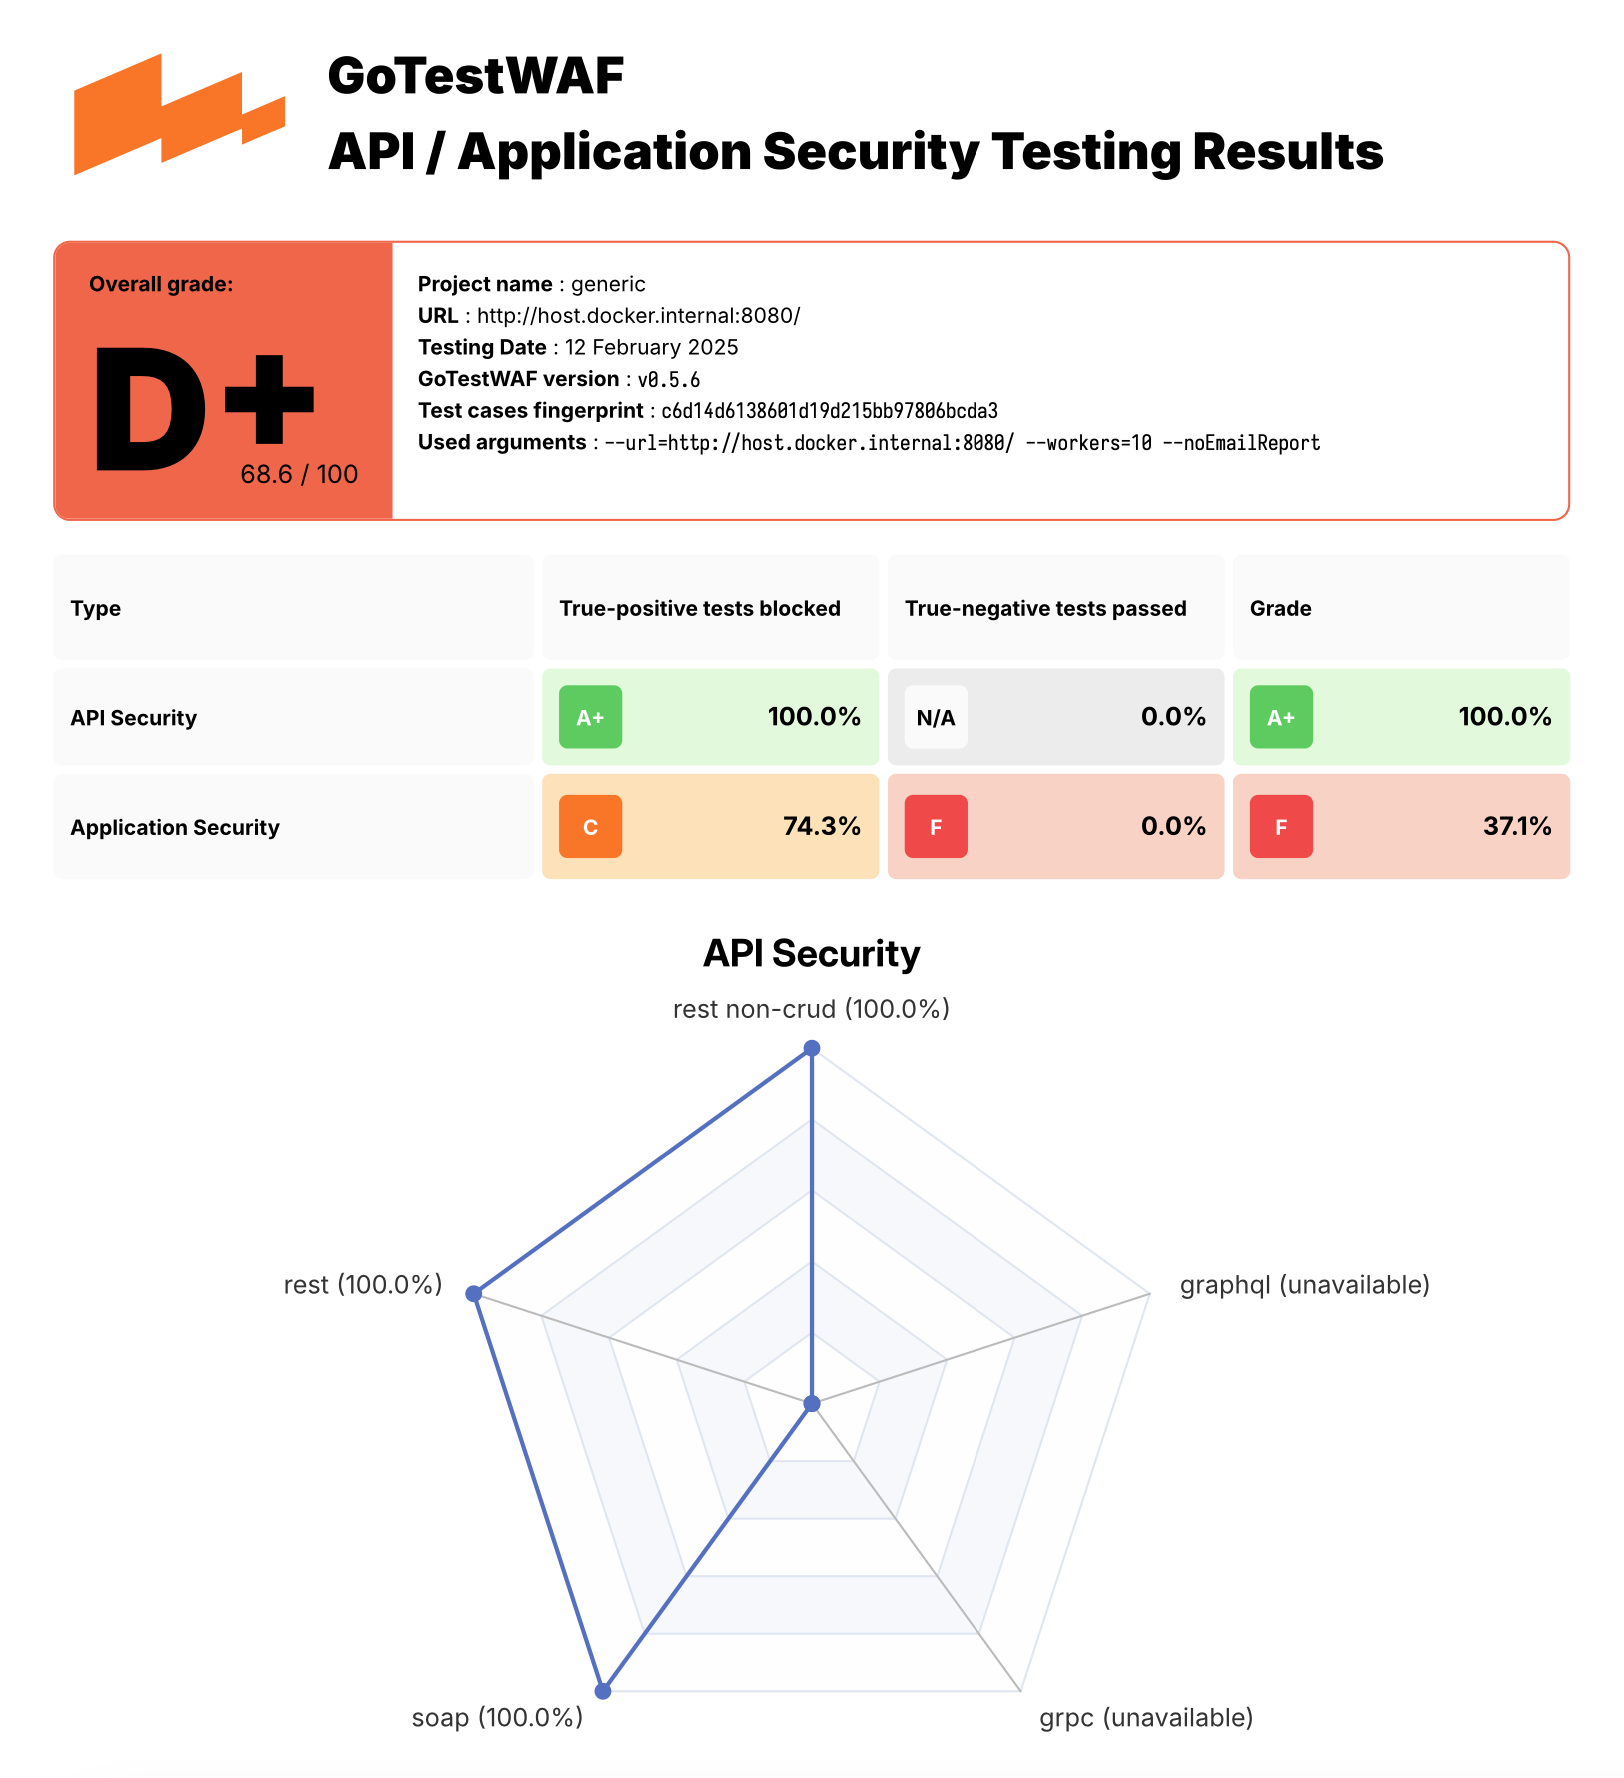 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 openidentityplatform/openam
Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
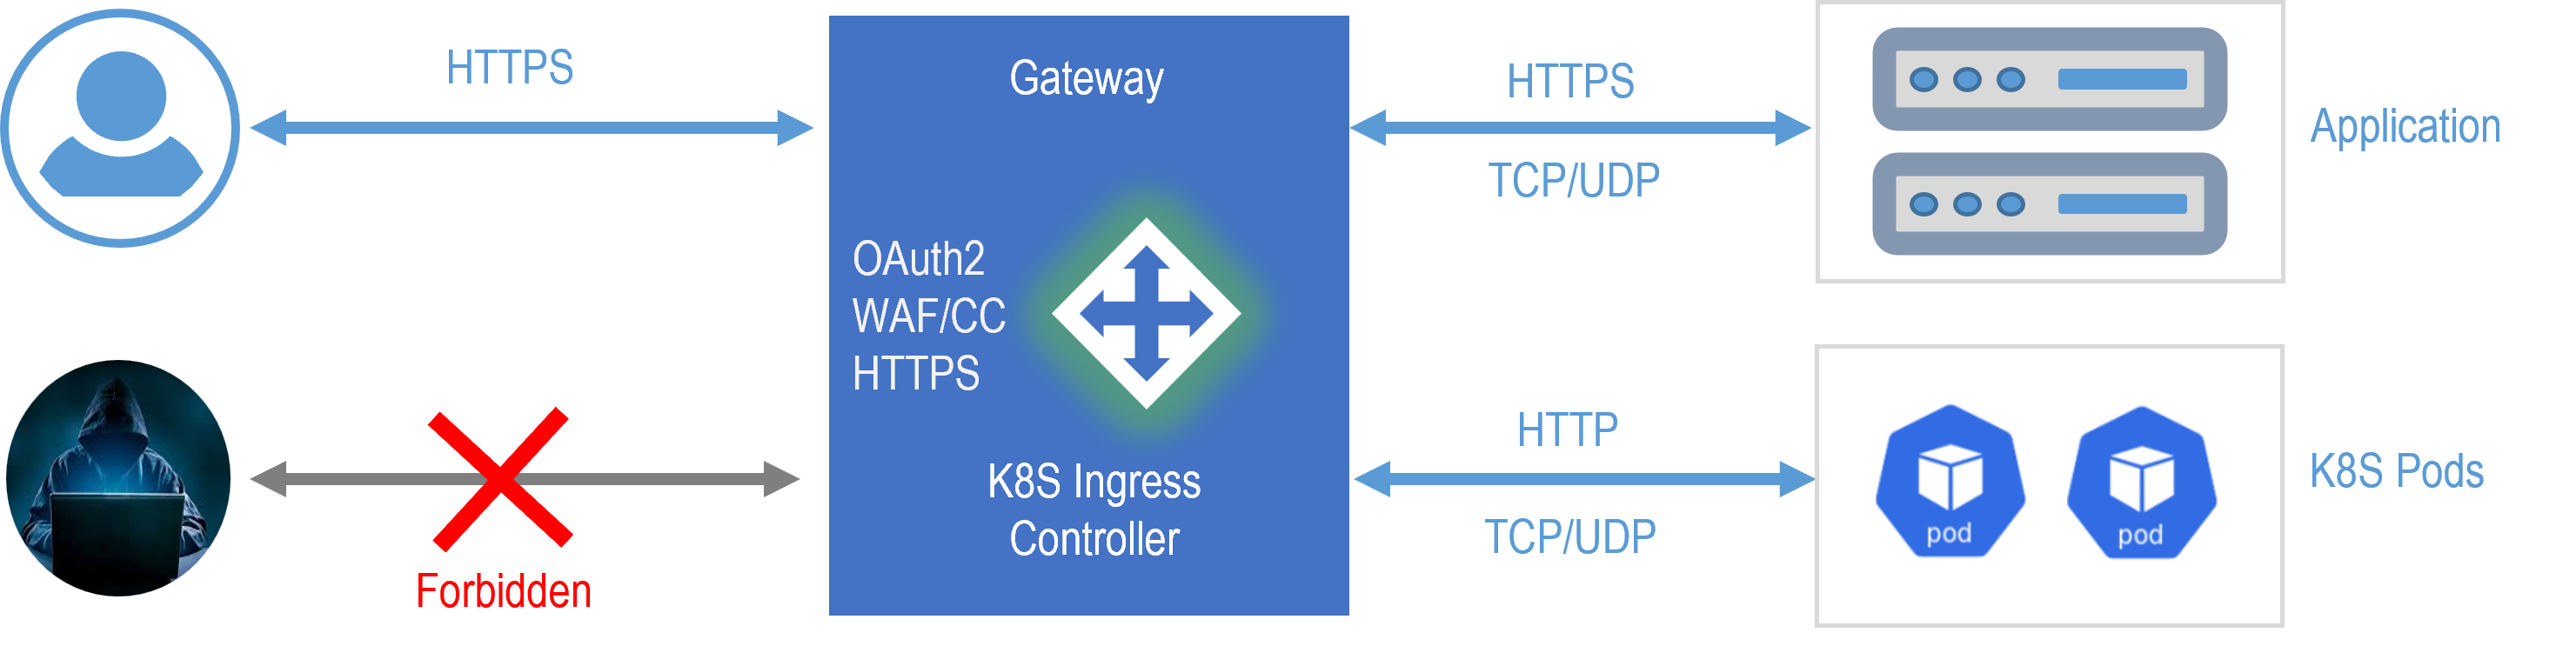 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
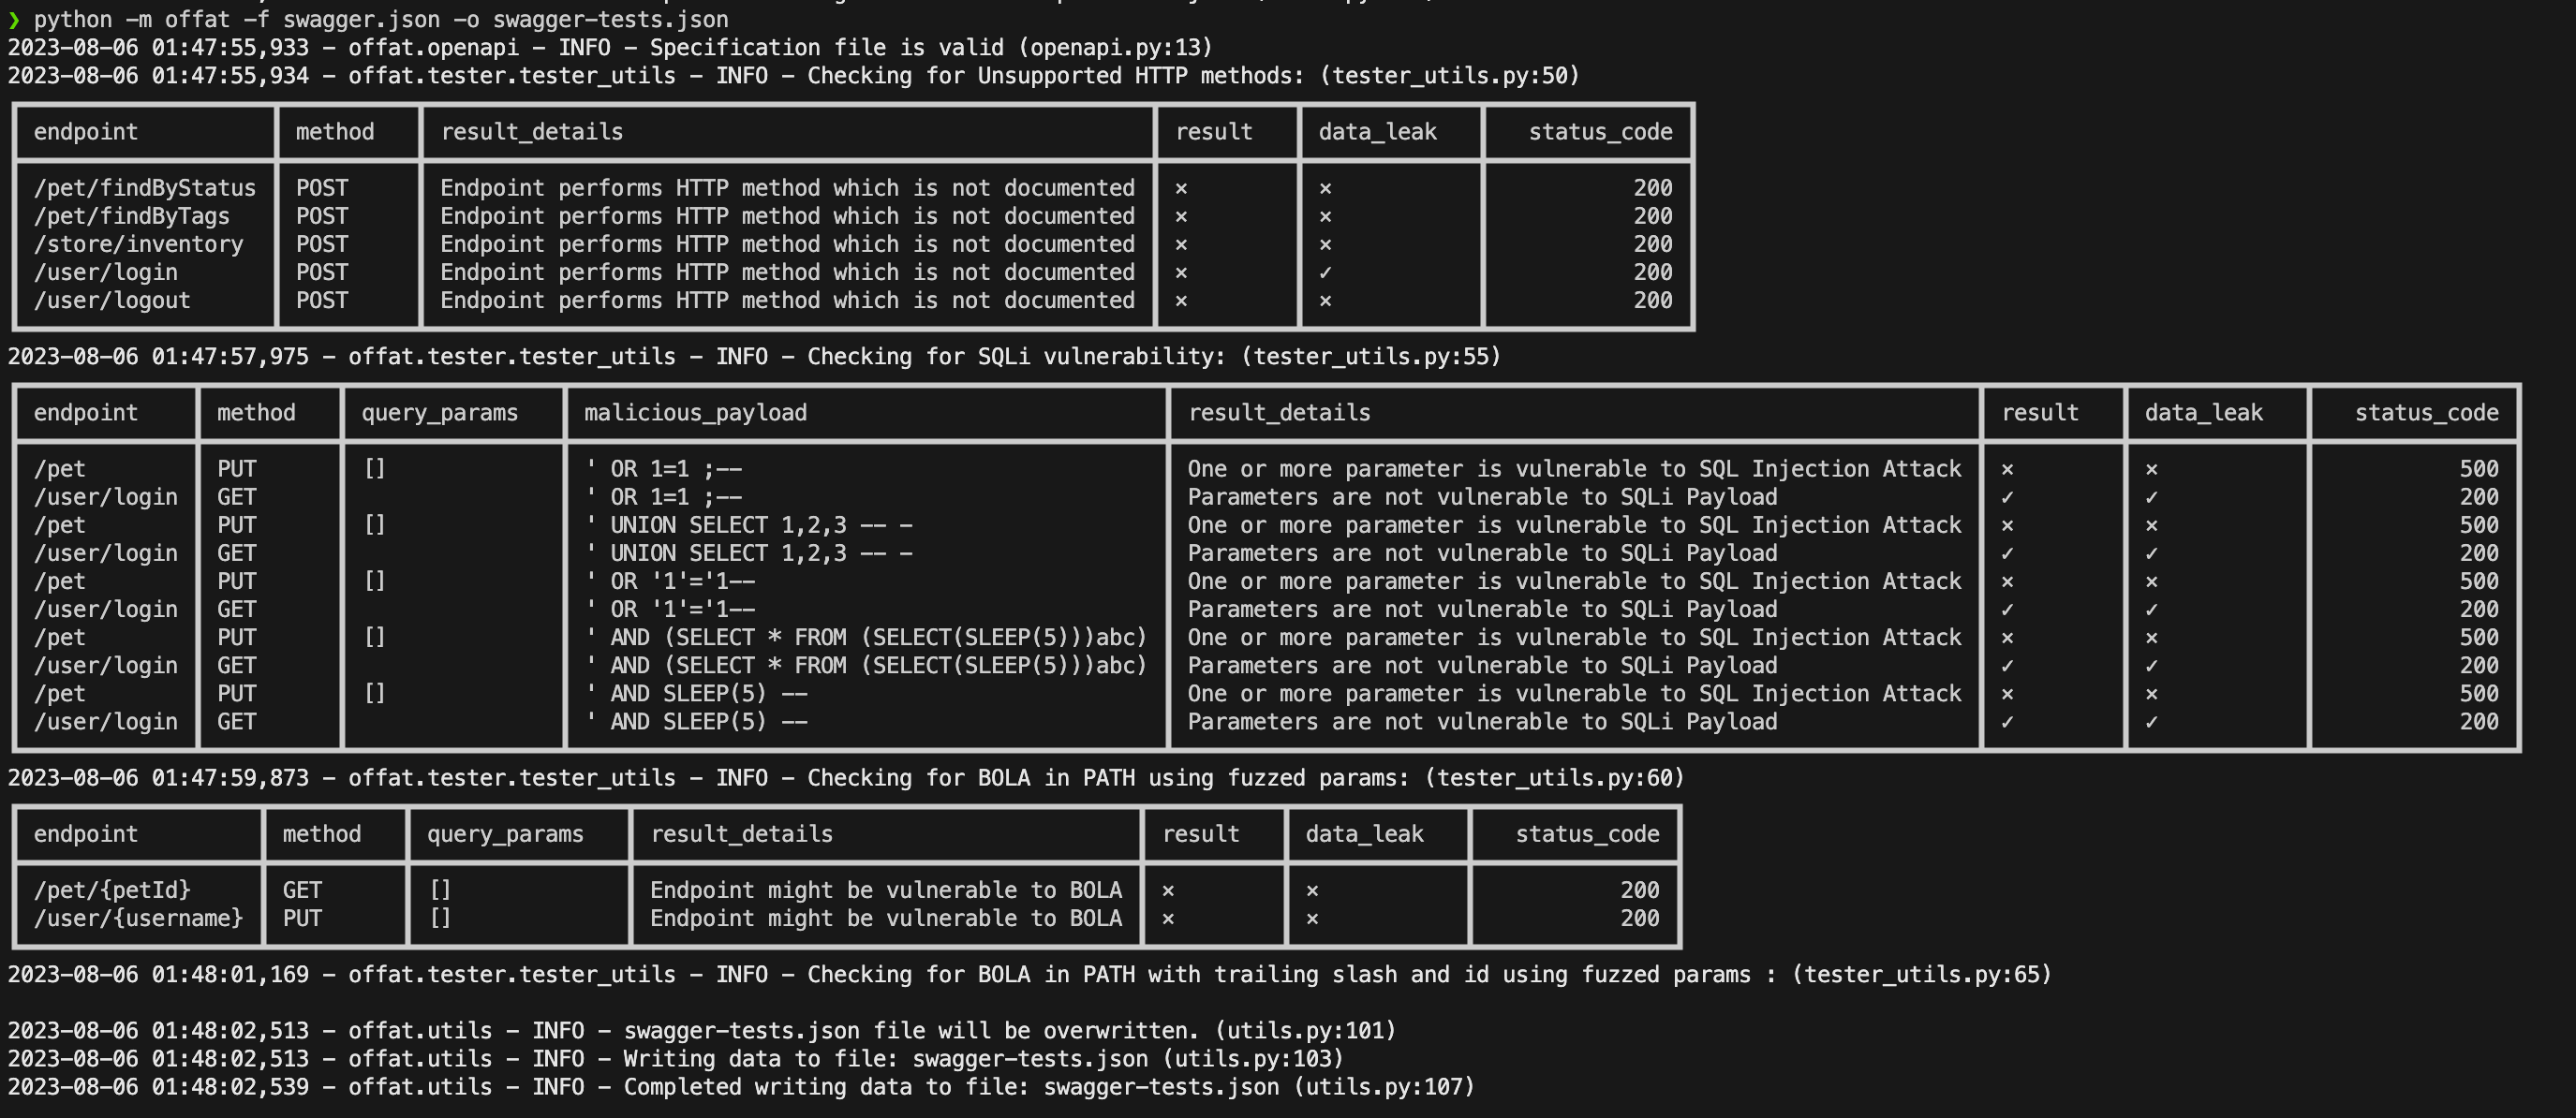 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 momenbasel/keyfinder
Passive API key and secret discovery browser extension for Chrome and Firefox. 80+ detection patterns, zero config.
 wso2/carbon-identity-framework
Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…