

API-Security
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
api-securitycurated-resourceseducation+3
2.3k
owasp/api-securityOWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 blst-security/cherrybomb
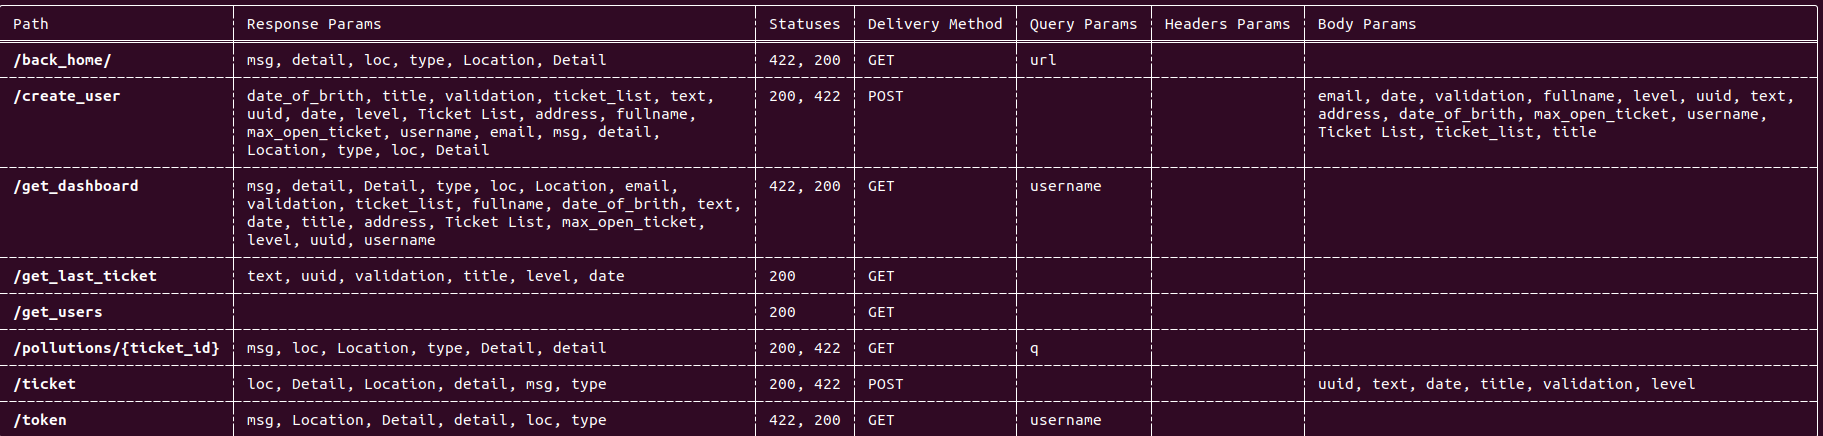
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 owasp/agent-skills-security-standard
Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 owasp/devsecopsguideline
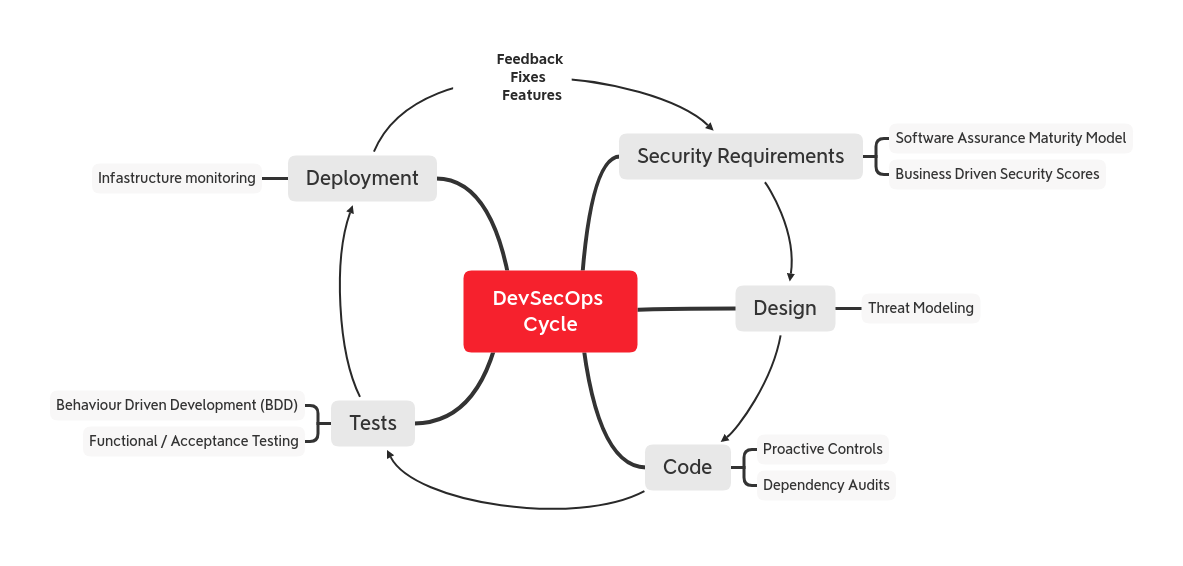
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 kubernetes/ingress-nginx
Ingress NGINX Controller for Kubernetes