
CVE-2025-6514
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
api-securityauthenticationcommand-and-control+3
cyberency/cve-2025-6514mcp-remote exposed to OS command injection
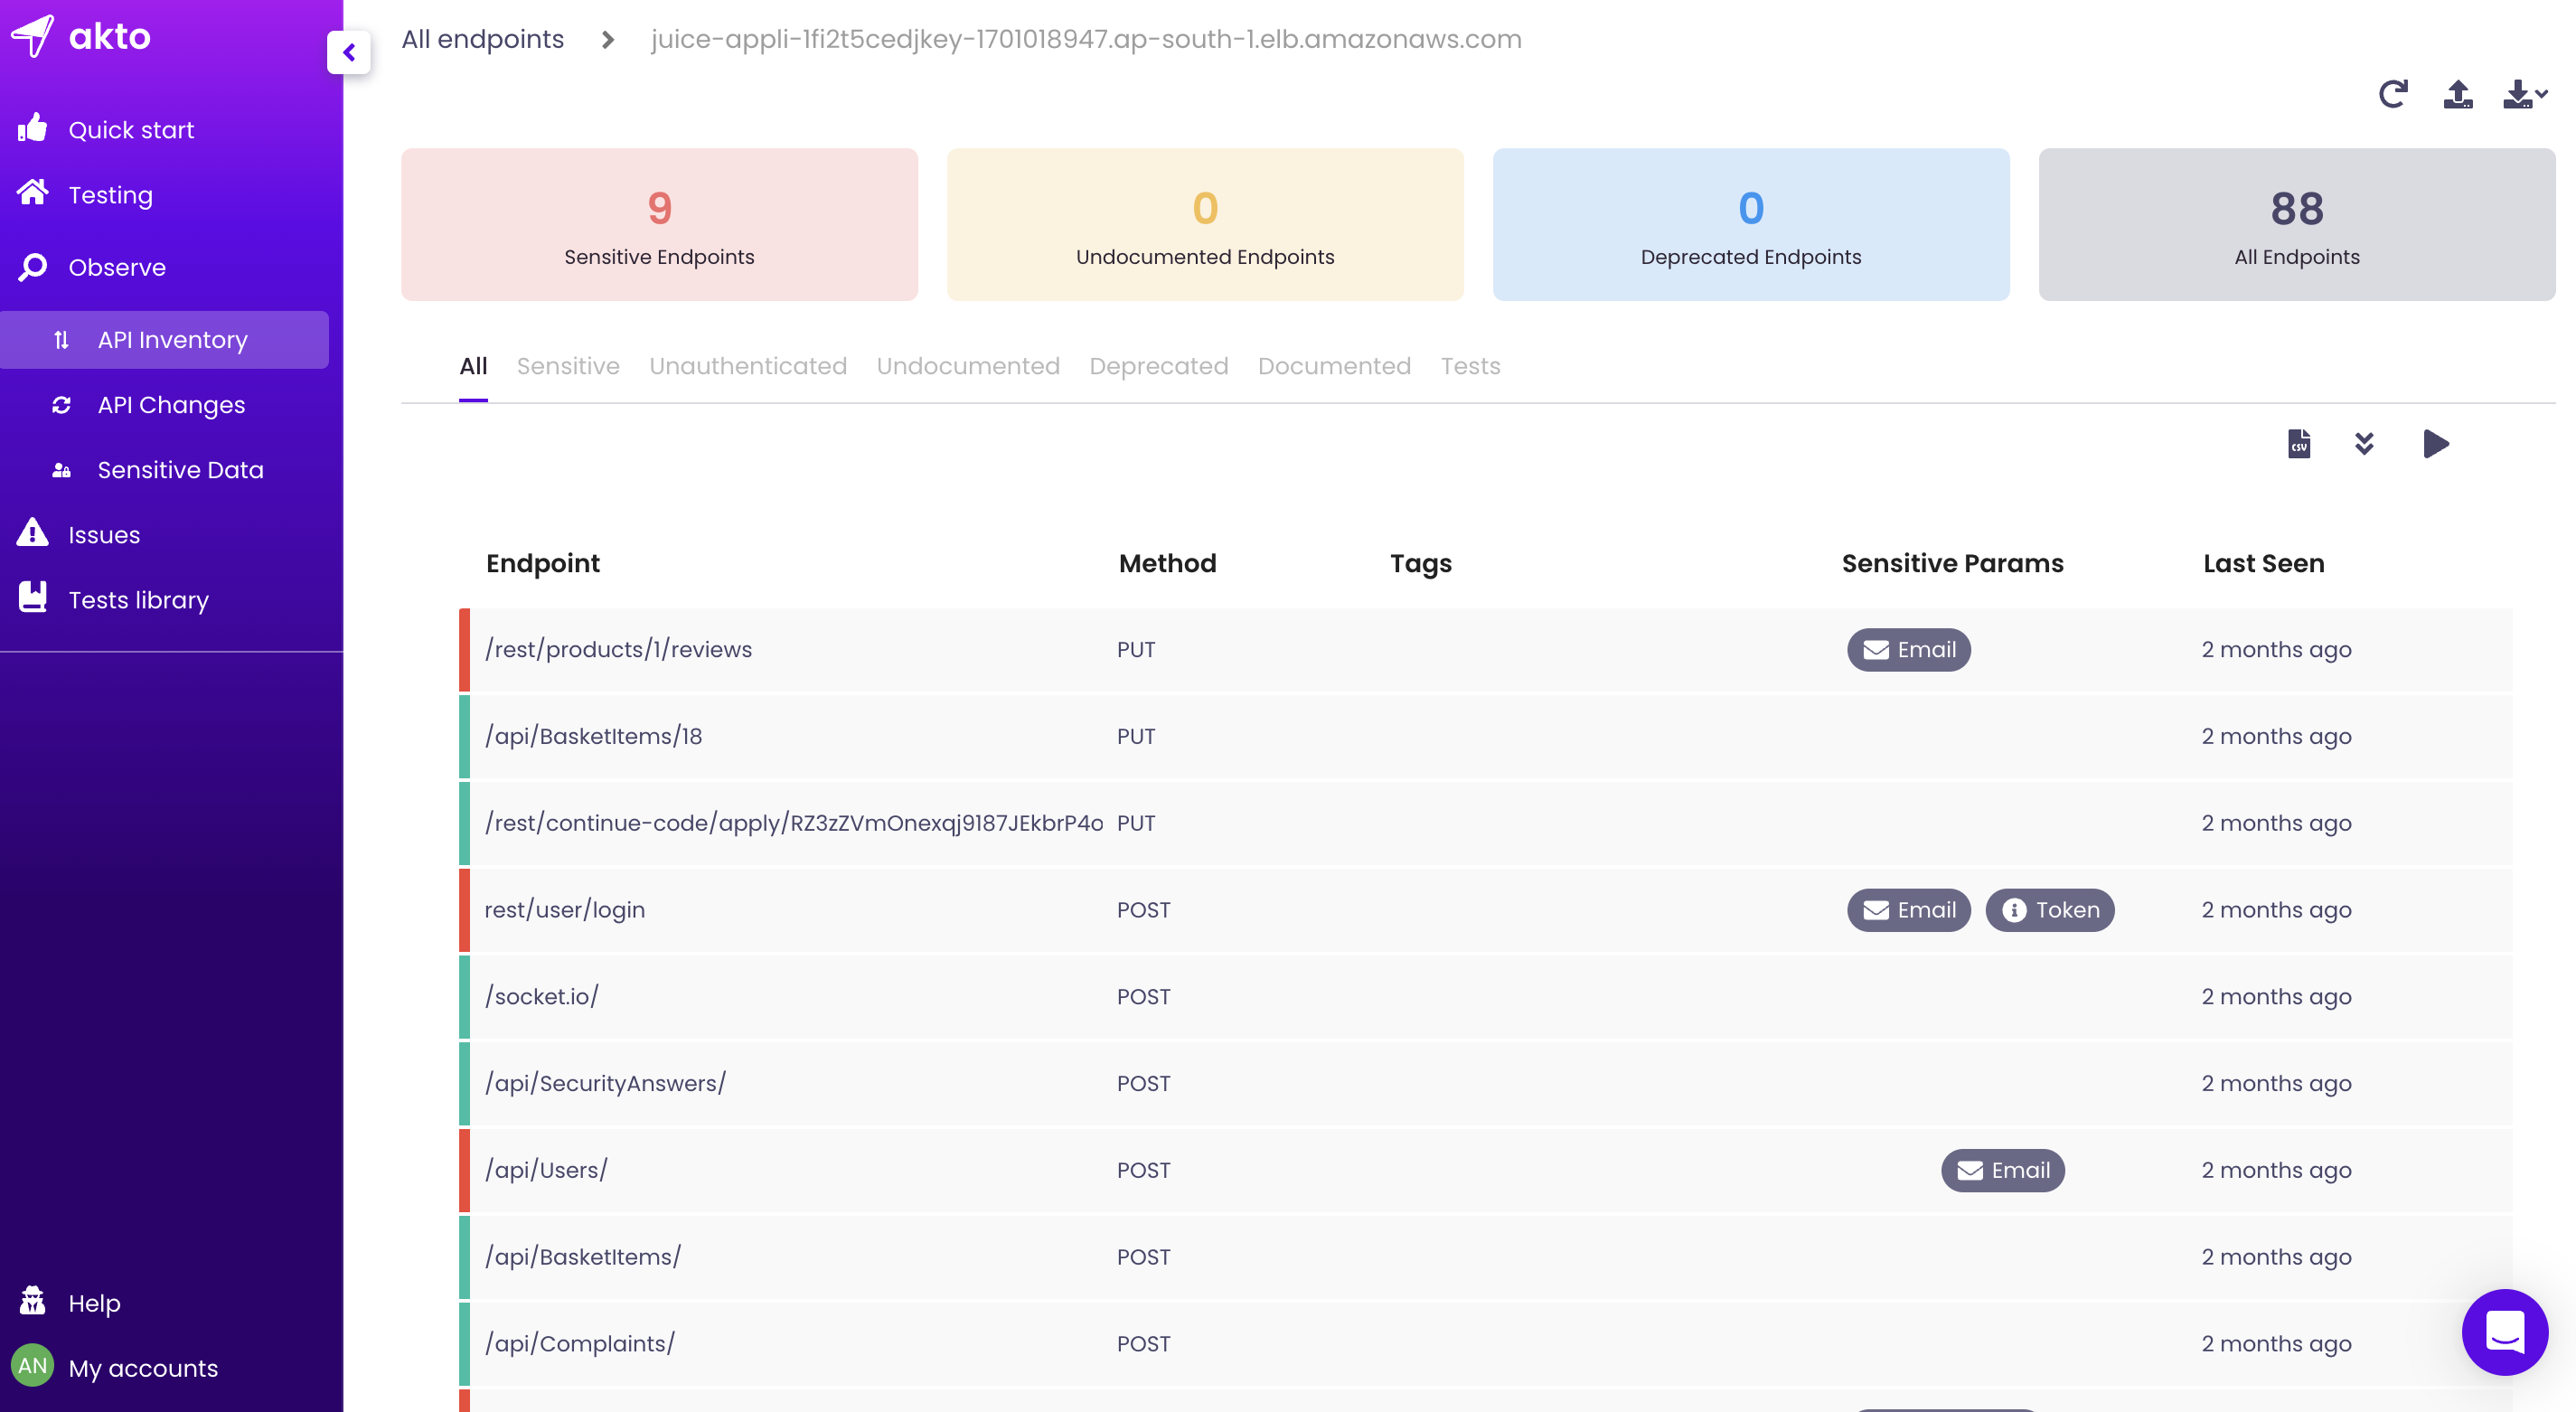 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 placeos/auth
PlaceOS authentication service and API gatekeeper.
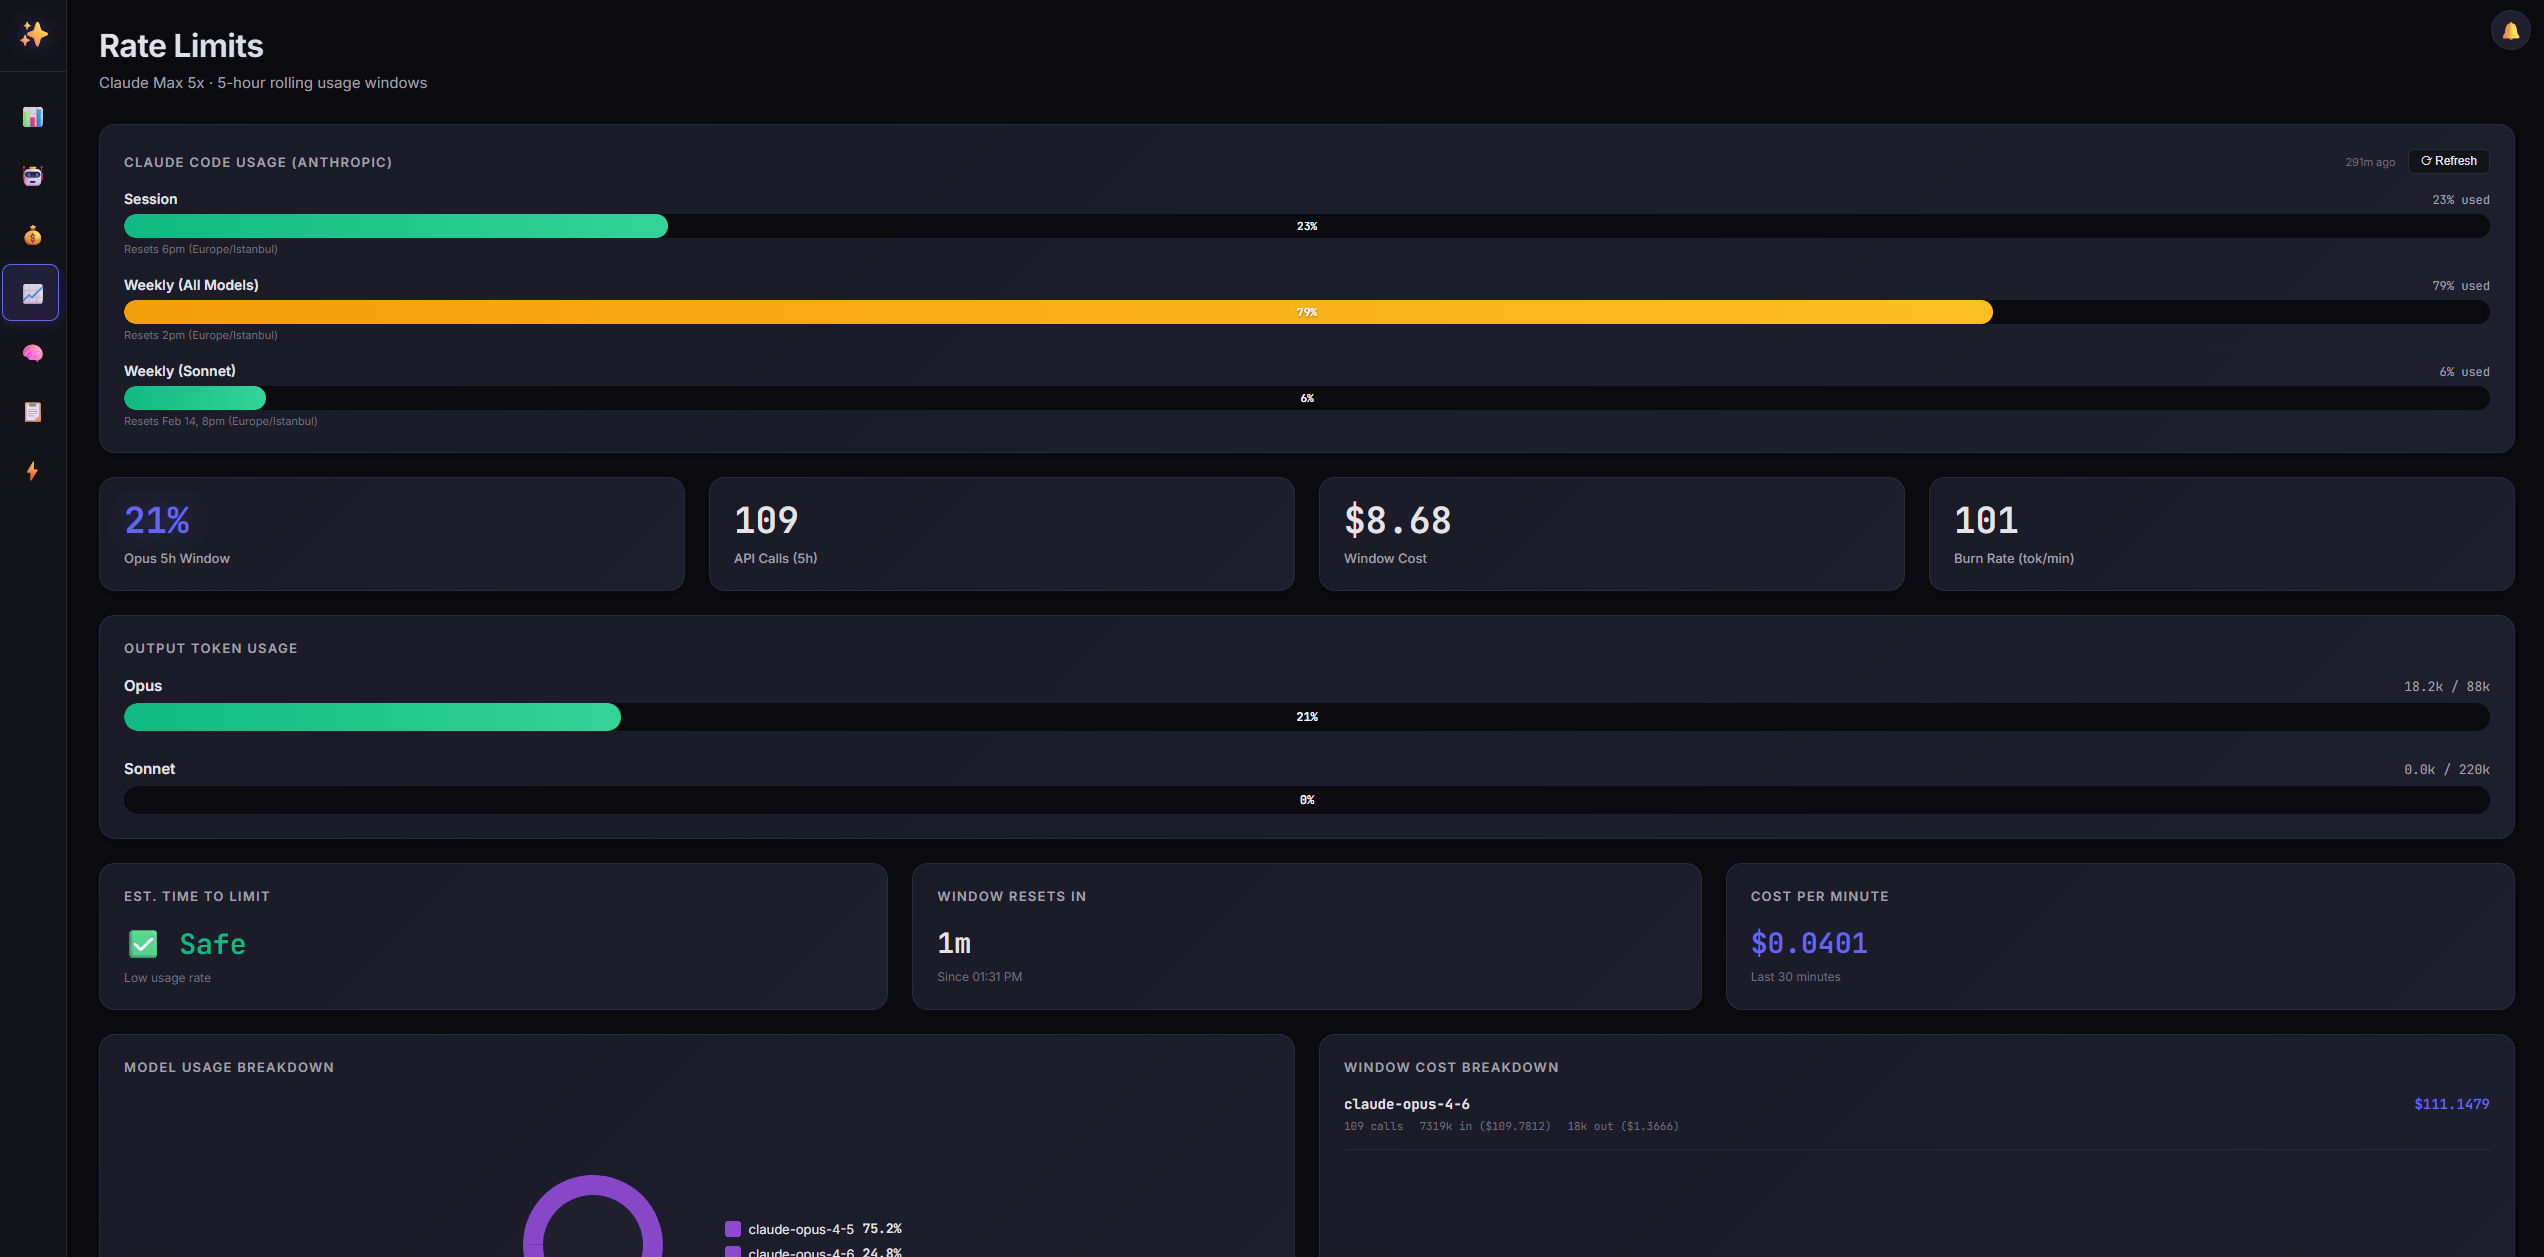 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
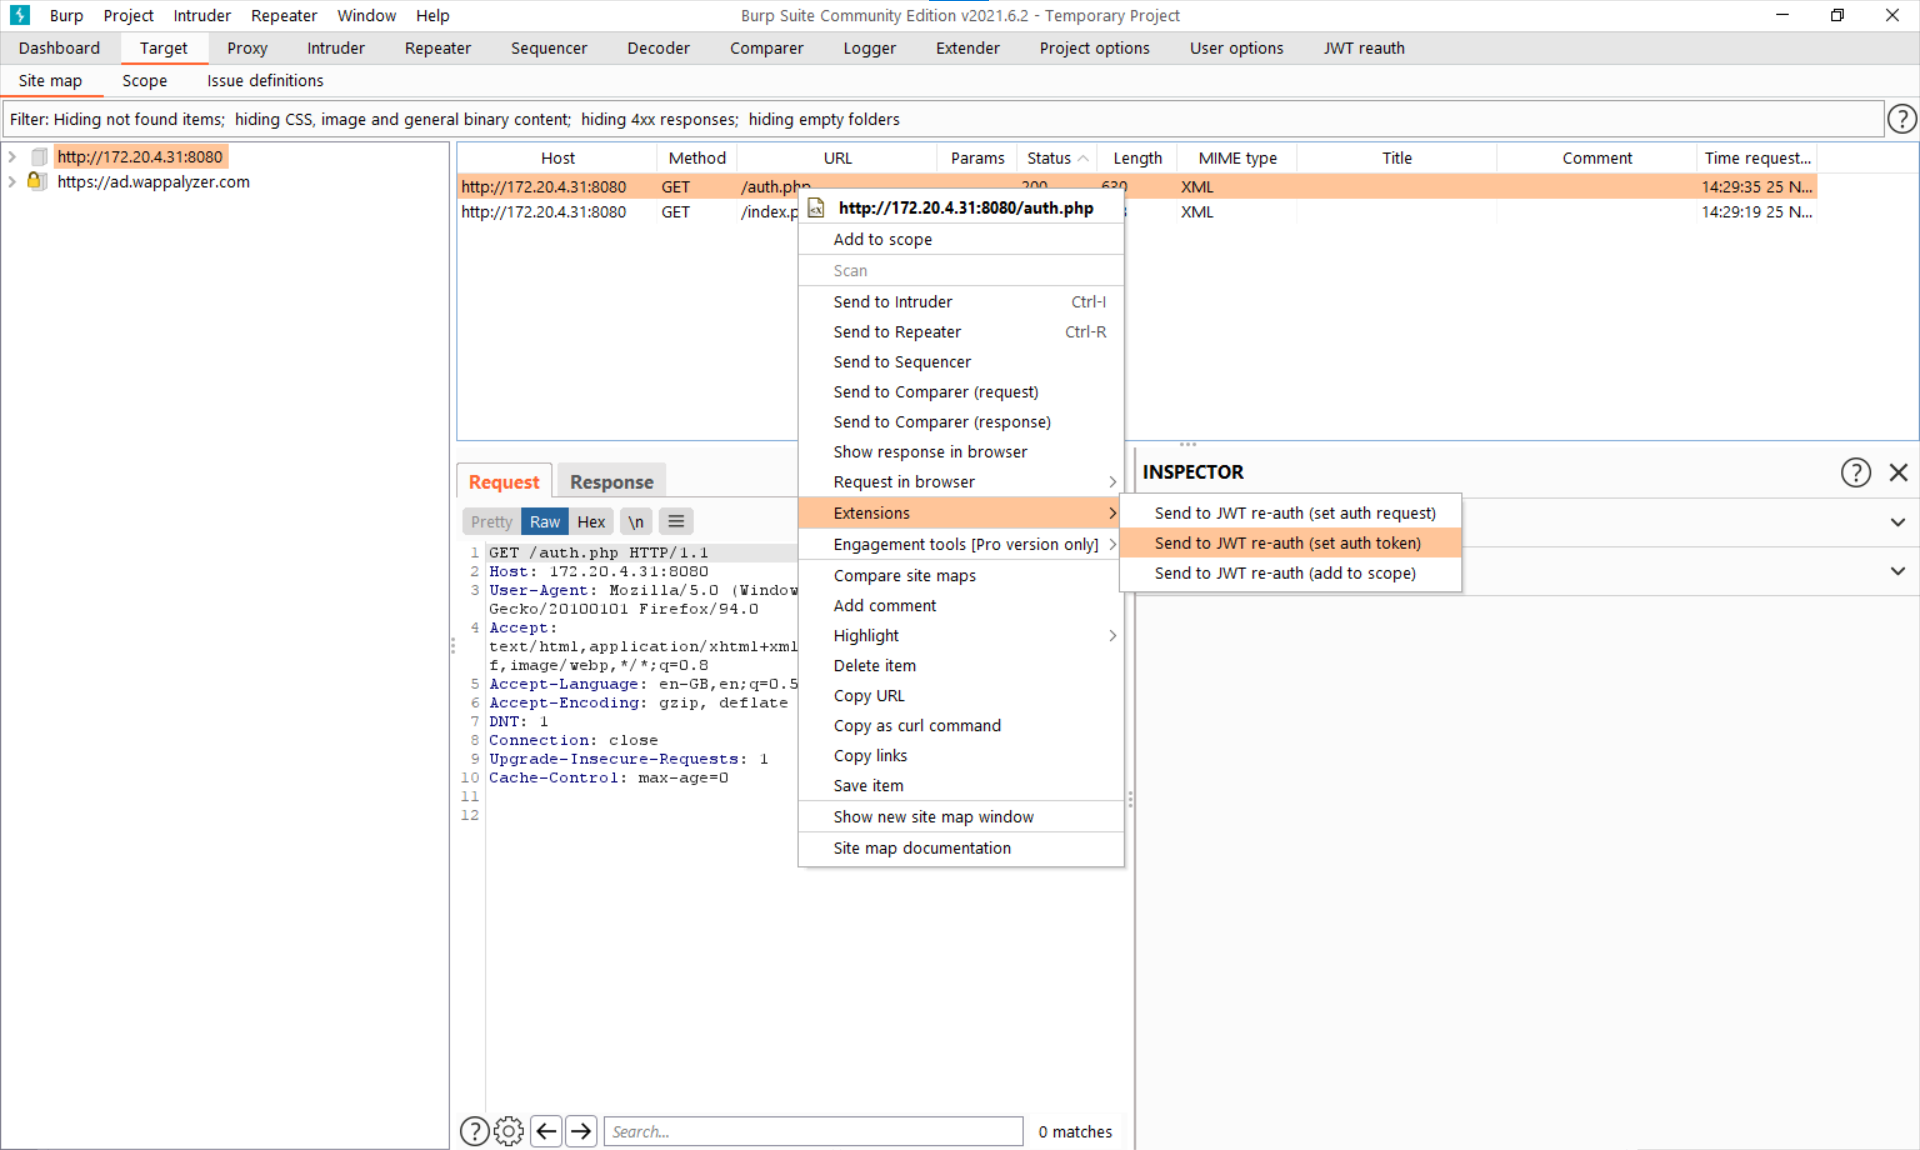 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 george0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-
Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…
 malhyuk/cve-2026-59243
Proof-of-concept for CVE-2026-59243 demonstrating JWT signature bypass in Apache Airflow FAB Auth Manager's Azure AD OAuth callback due to insecure…
 johanneslks/cve-2026-33186
gRPC-Go RBAC Authorization Policy Bypass via Missing `:path` Slash (Auth Bypass)
 sushank05/mcp-doorman
A lightweight mcp to prevent poisoning CVE (CVE-2025-54136), researchers hijacking Claude Code/Copilot/Gemini via prompt injection, and hundreds of…
 isaca0315/cve-2026-44351-poc
Proof-of-concept for CVE-2026-44351, an authentication bypass in fast-jwt <6.2.4 where an empty HMAC key lets attackers forge arbitrary JWTs accepted…
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…