
CVE-2025-55462
 sibikrish001/cve-2025-55462
Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…
api-securityauthenticationmisconfiguration+3
sibikrish001/cve-2025-55462Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
 0xsu3ks/cve-2025-29557
Documents a high-severity ExaGrid EX10 MailConfiguration API access control flaw that leaks plaintext SMTP credentials to authenticated operators,…
 randomrobbiebf/cve-2022-45354
Download Monitor <= 4.7.60 - Sensitive Information Exposure via REST API
 aman-parmar/cve-2025-54554
CVE-2025-54554 – Unauthenticated Access in tiaudit REST API leading to Sensitive Information Disclosure
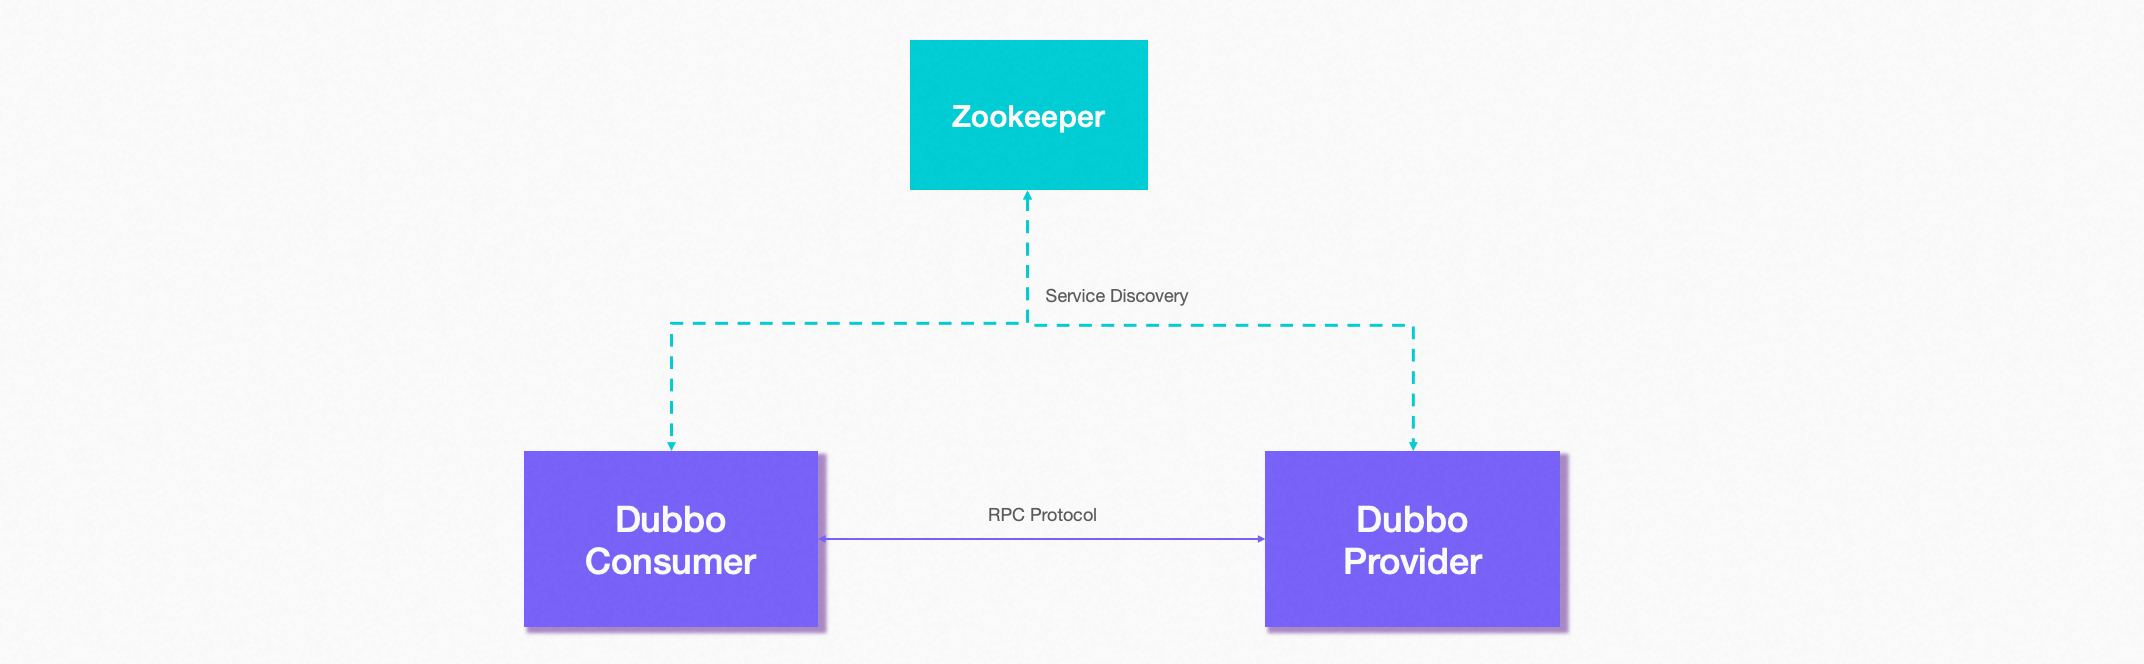 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 imthecopilotnow/cve-2025-492030
Proof-of-concept for CVE-2025-492030: account takeover via session token validation bypass in SecureVPN API endpoint /api/v1/authenticate.
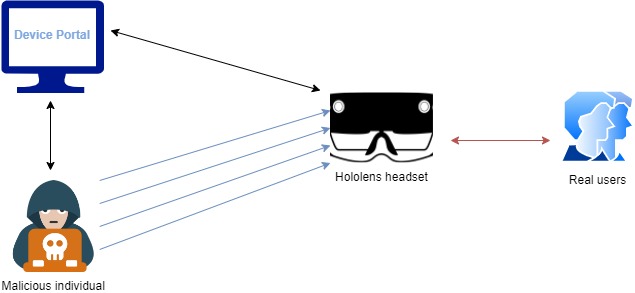 tania-silva/cve-2024-57972
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 matrix-org/synapse
Synapse: Matrix homeserver written in Python/Twisted.
 nbs-system/naxsi
NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX
 kubernetes/ingress-nginx
Ingress NGINX Controller for Kubernetes
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs
 zecure/shadowd
The Shadow Daemon web application firewall server
 ansvar-systems/eu_compliance_mcp
EU focused compliance MCP server