

CVE-2026-94609
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
api-securityauthentication-authorizationeducation+6
anthonyk2923/cve-2026-94609Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 oscerd/cve-2026-46456
Reproducer for CVE-2026-46456 — Apache Camel camel-aws2-sqs inbound message-attribute header injection (Camel control-header injection via…
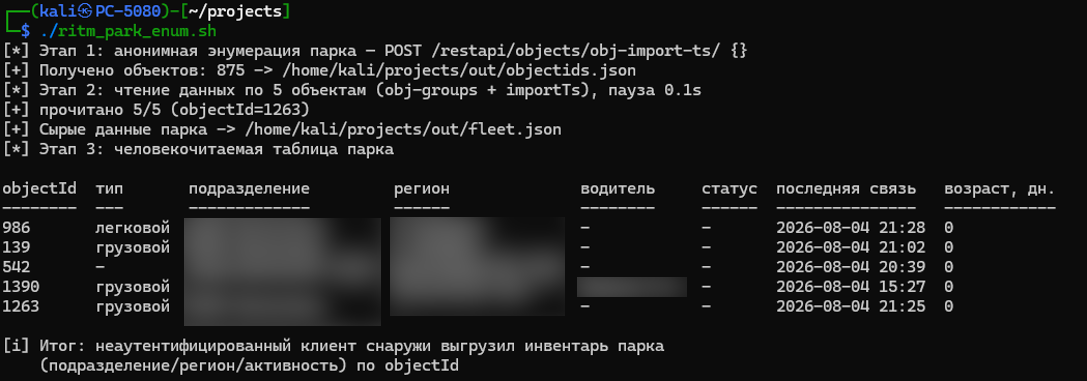 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478
 5qu1n7/cve-2025-55817
ChilliCream Nitro GraphQL version 28.0.13 is vulnerable to multiple Stored Cross Site Scripting (XSS) Vulnerabilities
 0xsu3ks/cve-2025-29557
Documents a high-severity ExaGrid EX10 MailConfiguration API access control flaw that leaks plaintext SMTP credentials to authenticated operators,…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…