

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
16.2k5 days ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
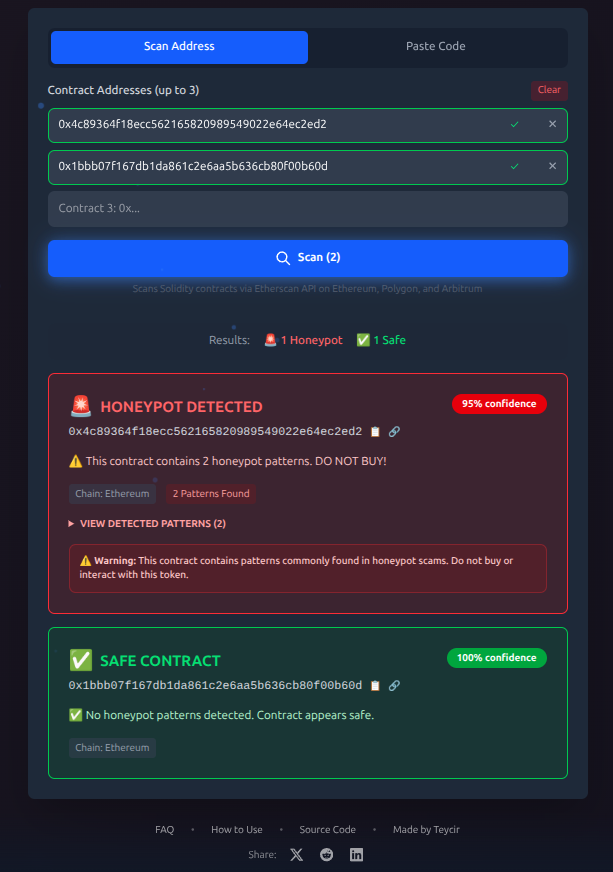 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
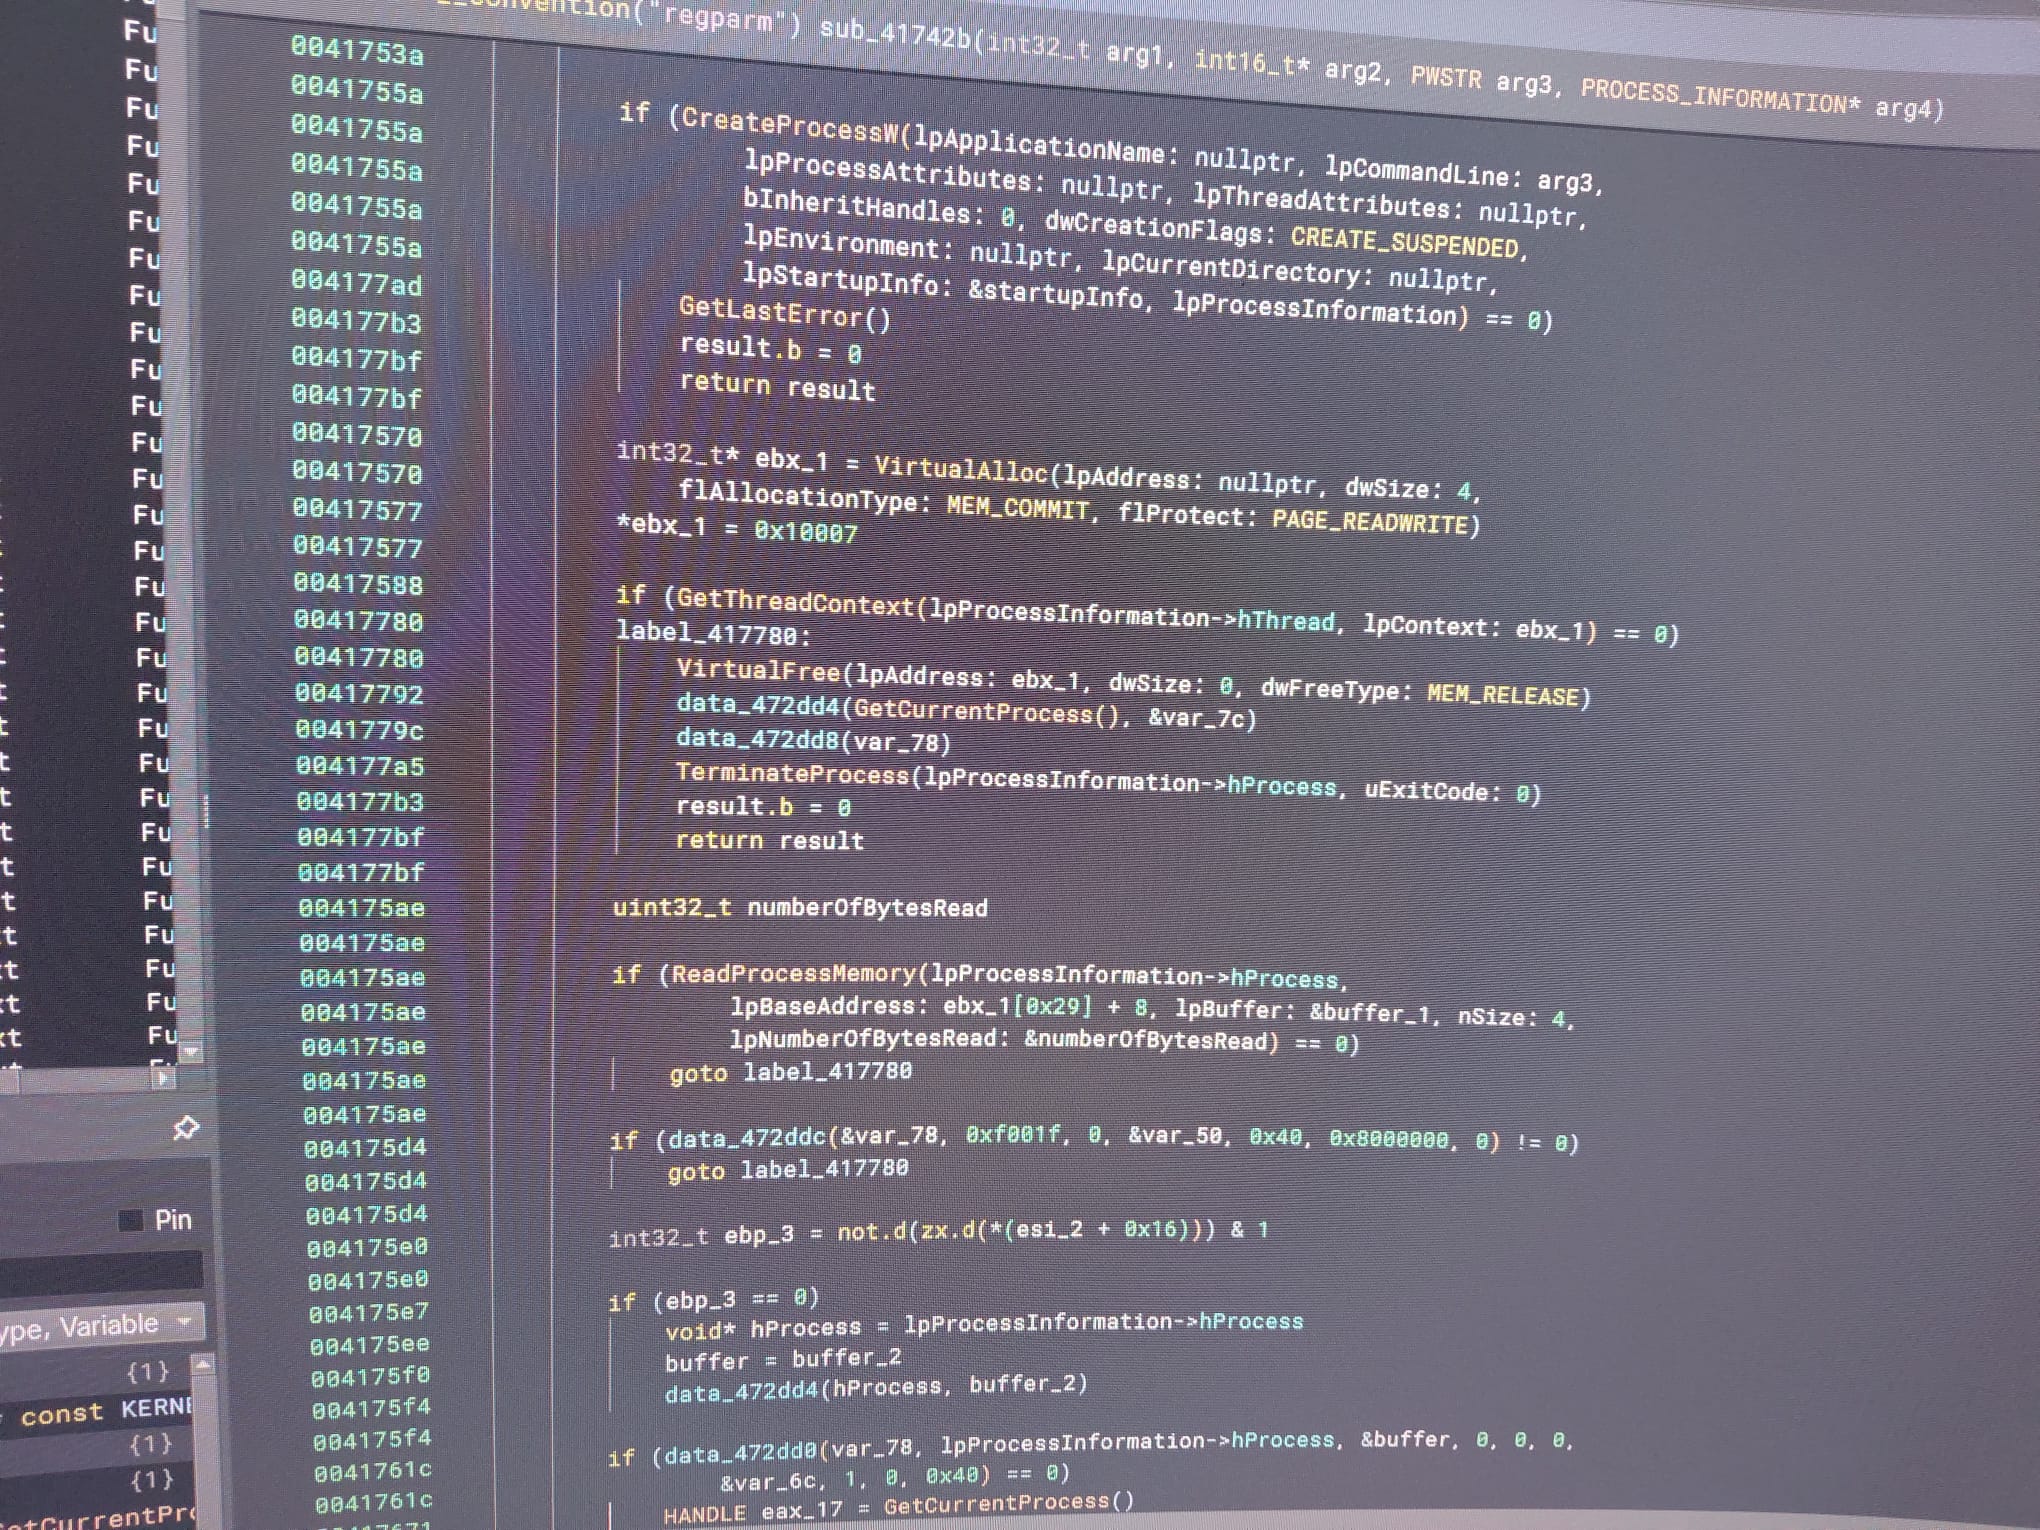 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
 shoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6
Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
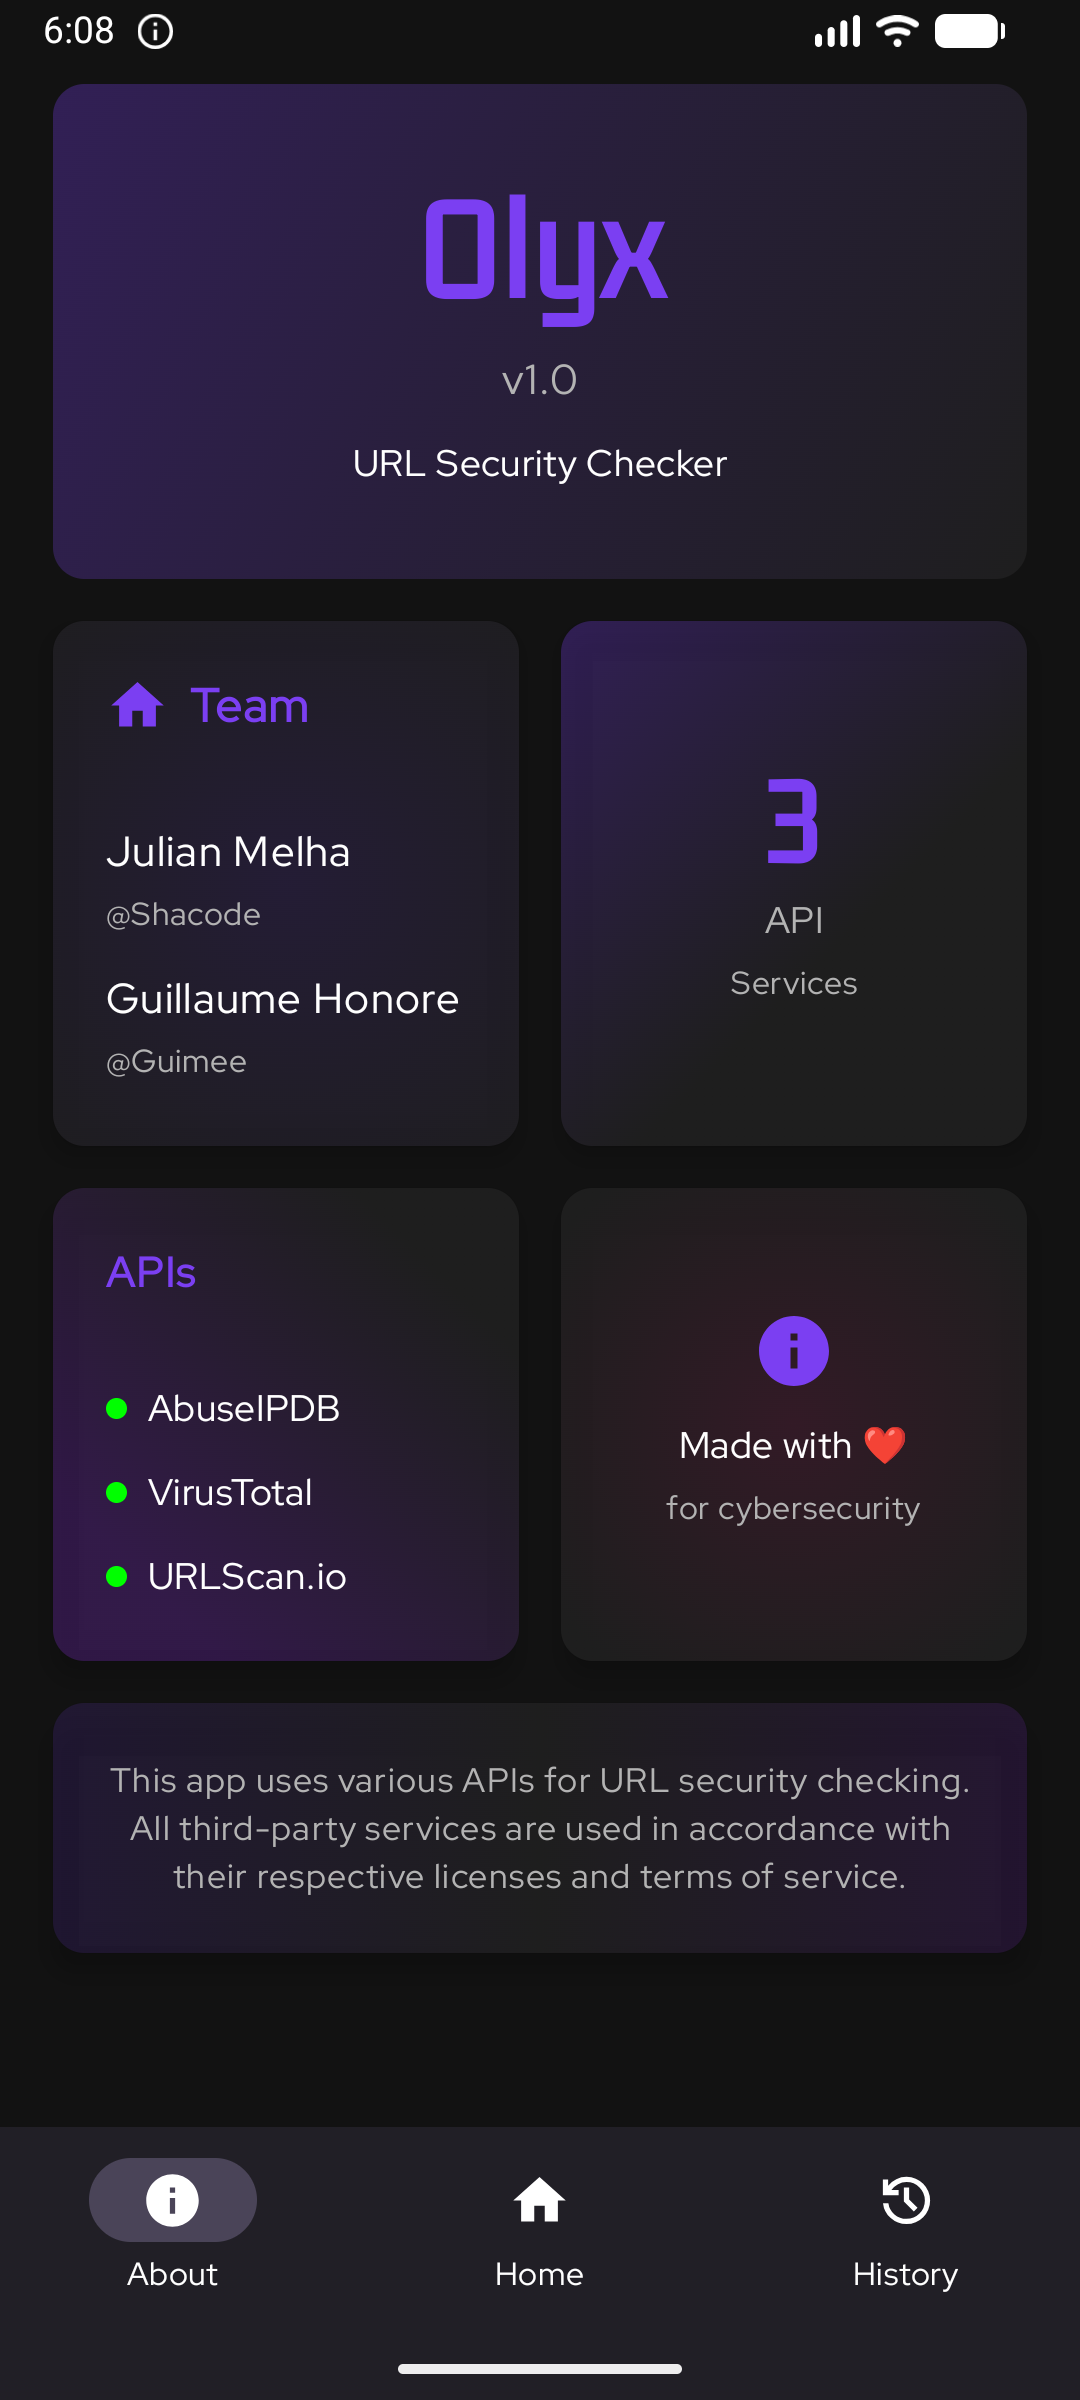
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.