
swaggerHole
 liodeus/swaggerhole
A python3 script searching for secret on swaggerhub
api-securityinformation-gatheringosint+2
liodeus/swaggerholeA python3 script searching for secret on swaggerhub
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
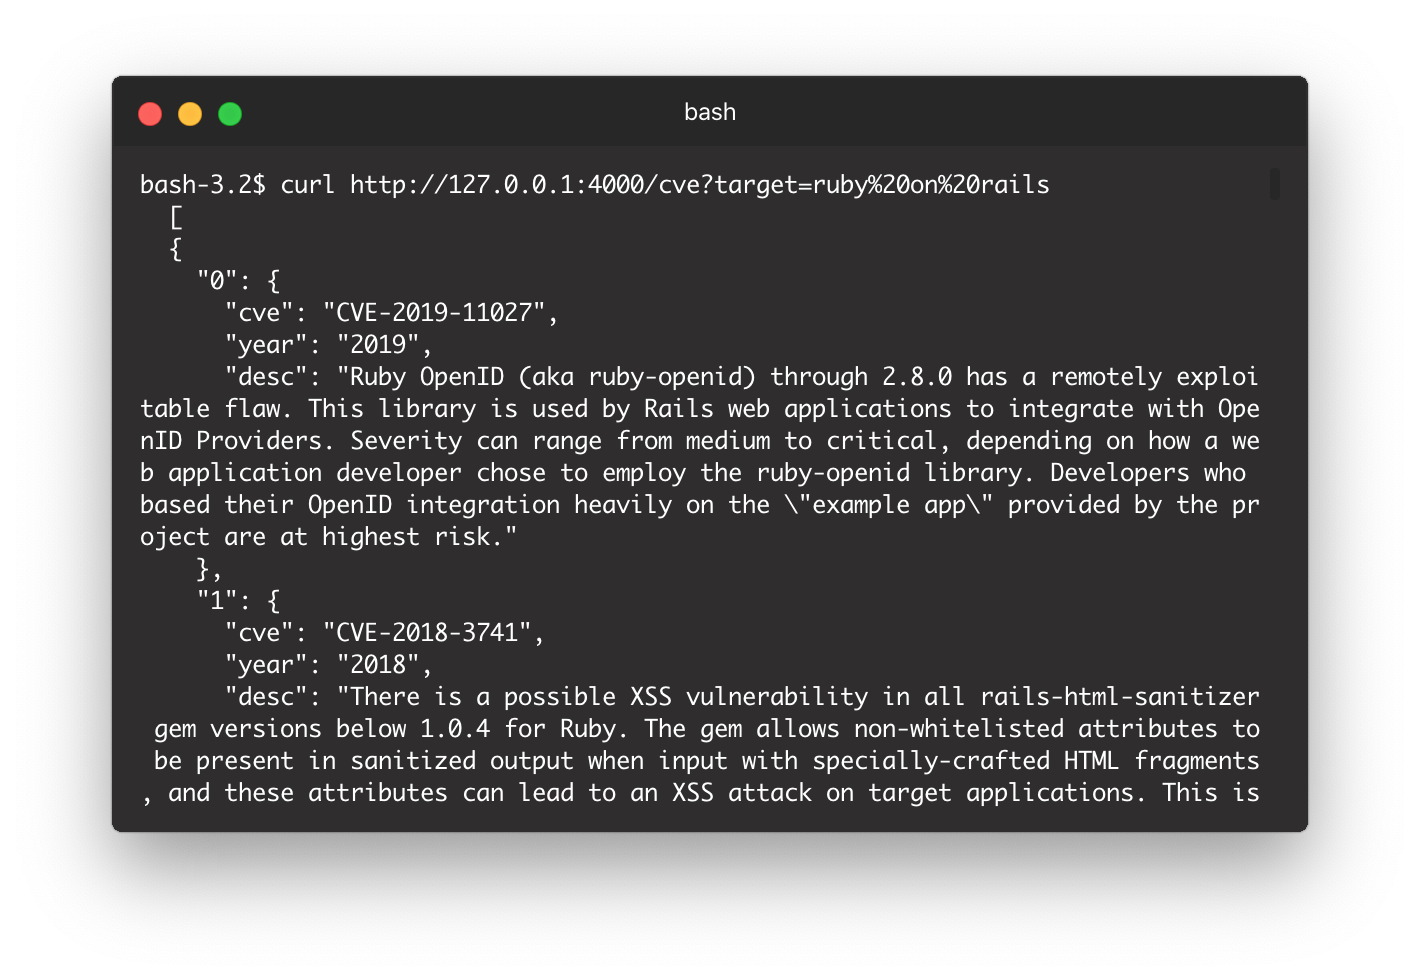 beyarz/cve-api
Unofficial api for cve.mitre.org
 davkharrr/cve-2026-19478-poc
Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 randomrobbiebf/super-secret-finder
Burp Plugin for Secret Matching
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
 mitrecnd/whodat
Pivotable Reverse WhoIs / PDNS Fusion with Registrant Tracking & Alerting plus API for automated queries (JSON/CSV/TXT)
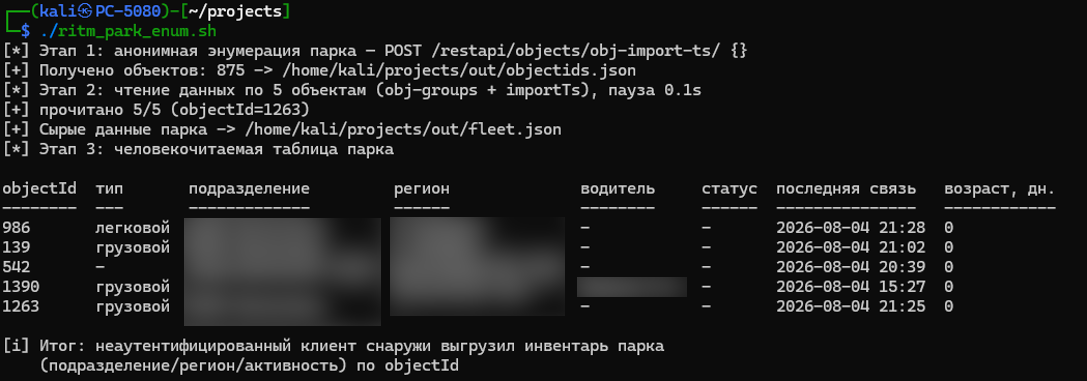 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.