
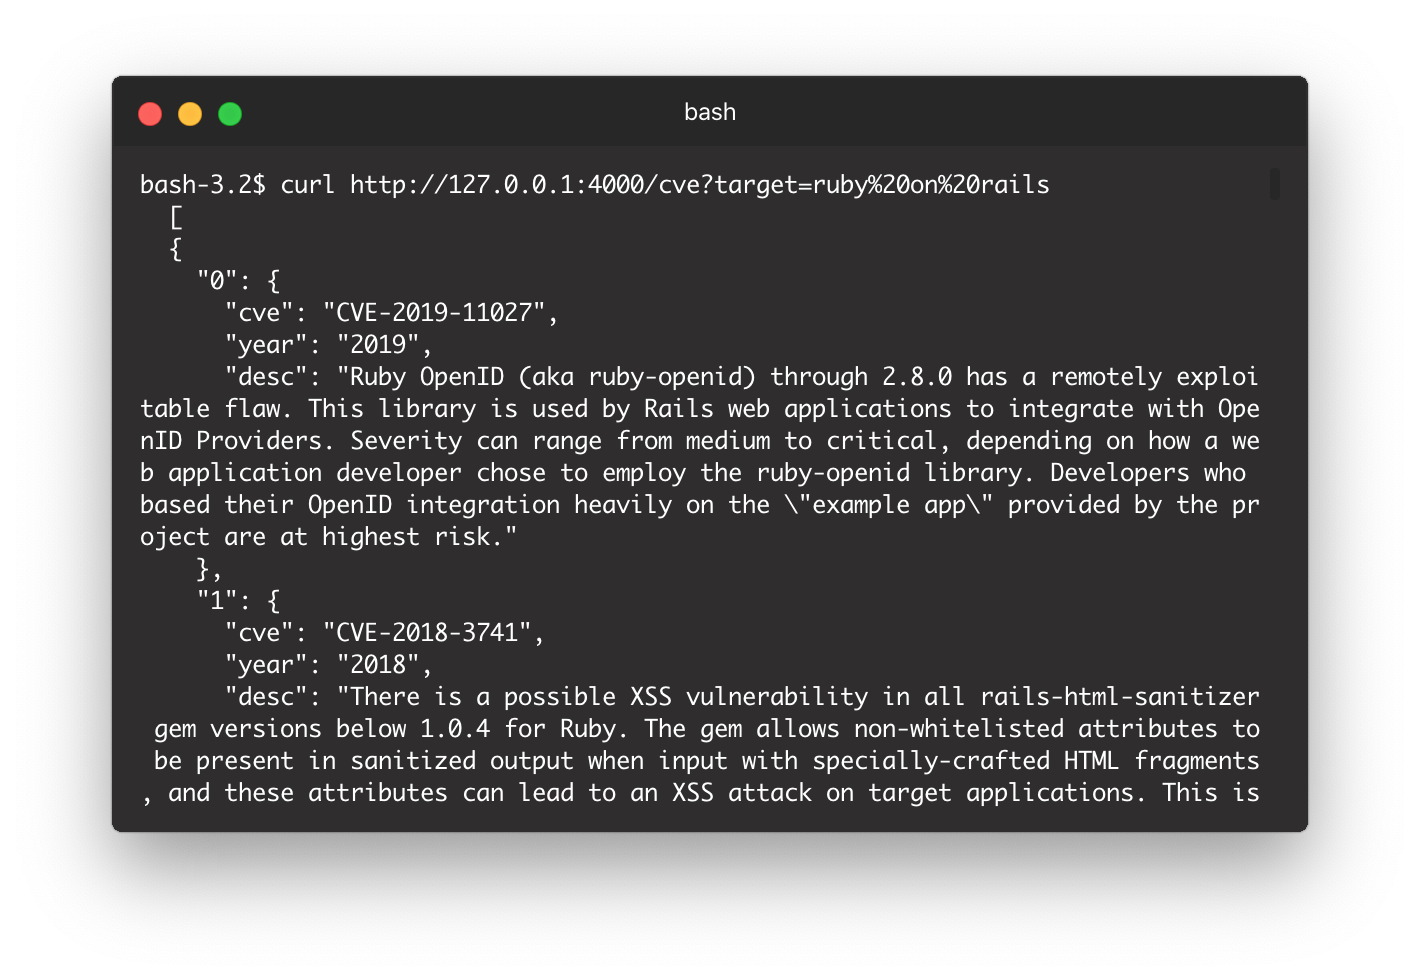
Cve-api
 beyarz/cve-api
Unofficial api for cve.mitre.org
api-securityinformation-gatheringthreat-intelligence+1
406 years ago
beyarz/cve-apiUnofficial api for cve.mitre.org
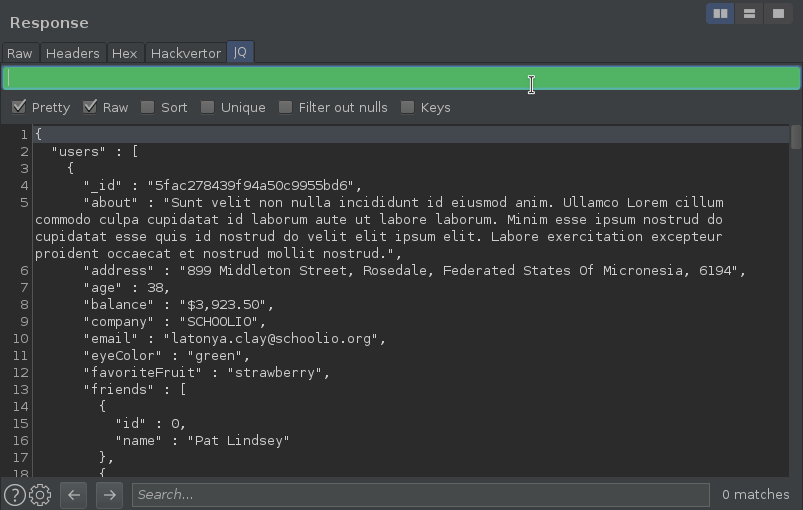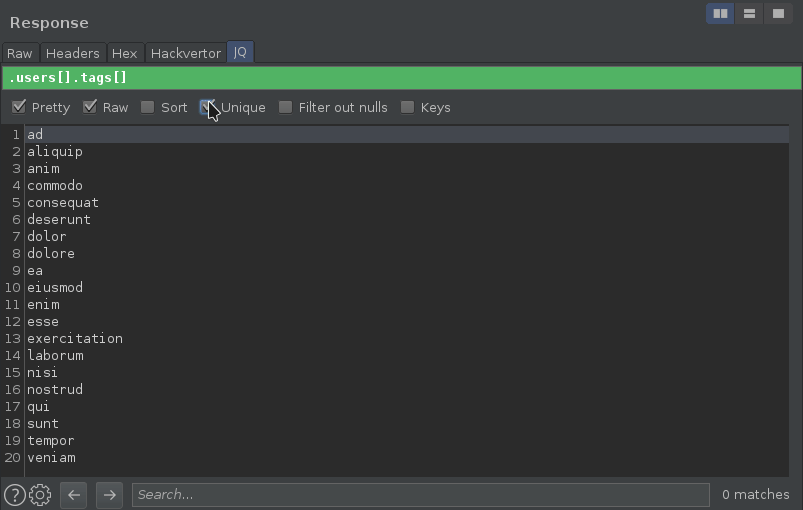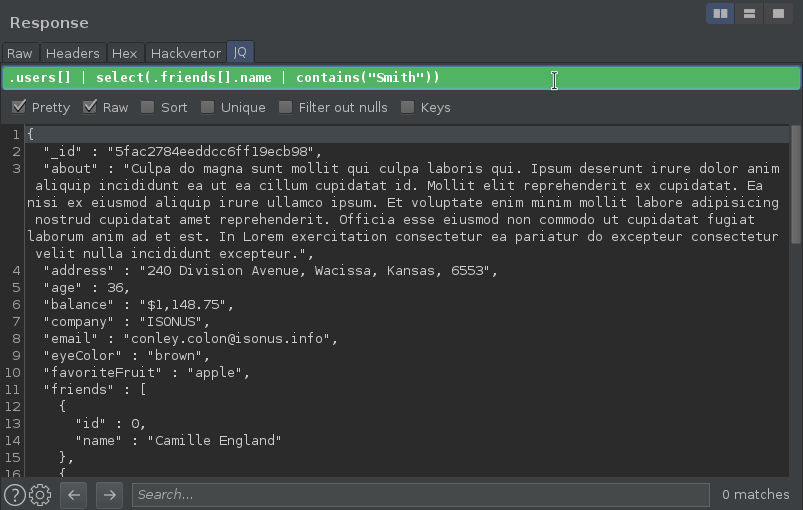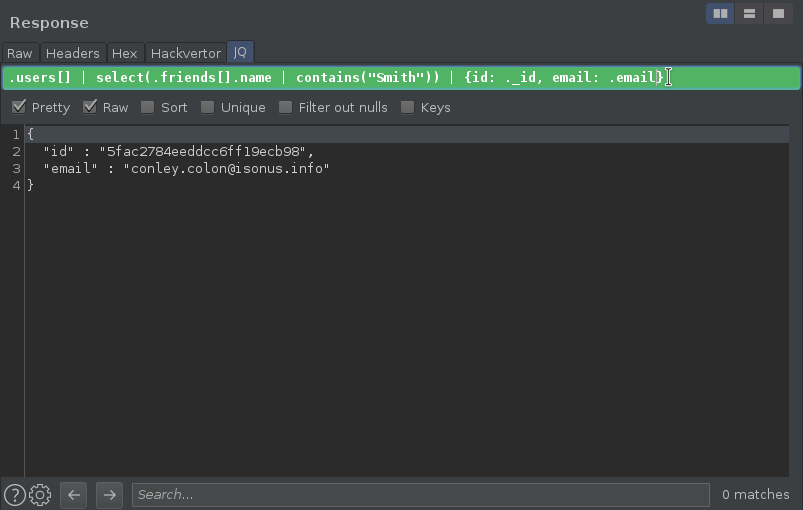 synacktiv/burp-jq
Burp extension to filter JSON on the fly with JQ queries in the HTTP message viewer.
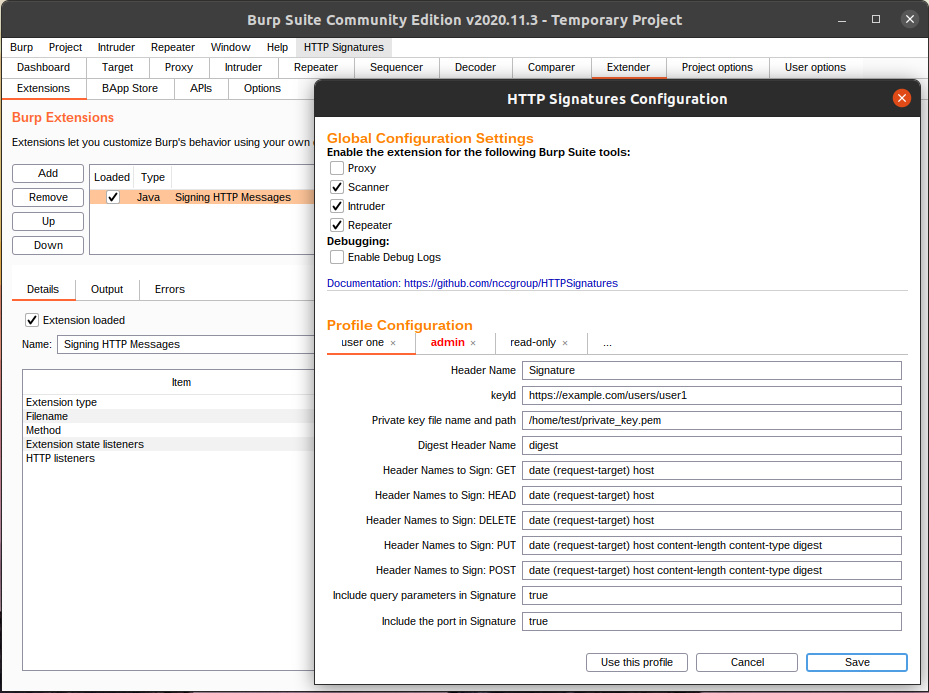 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 corelight/corelight-client
Corelight Sensor API command-line client
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 xvnpw/k8s-cve-2021-43557-poc
PoC for CVE-2021-43557
 qarait/gate0
A small, auditable, terminating, deterministic micro-policy engine
 m4xsec/apache-apisix-cve-2022-24112
Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 secnn/cve-2022-24112
Apache APISIX batch-requests RCE(CVE-2022-24112)
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device
 0xgh057r3c0n/cve-2025-48827
Critical Unauthenticated API Access in vBulletin
 k3ystr0k3r/cve-2020-13945-exploit
A PoC exploit for CVE-2020-13945 - Apache APISIX Remote Code Execution (RCE)
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.