
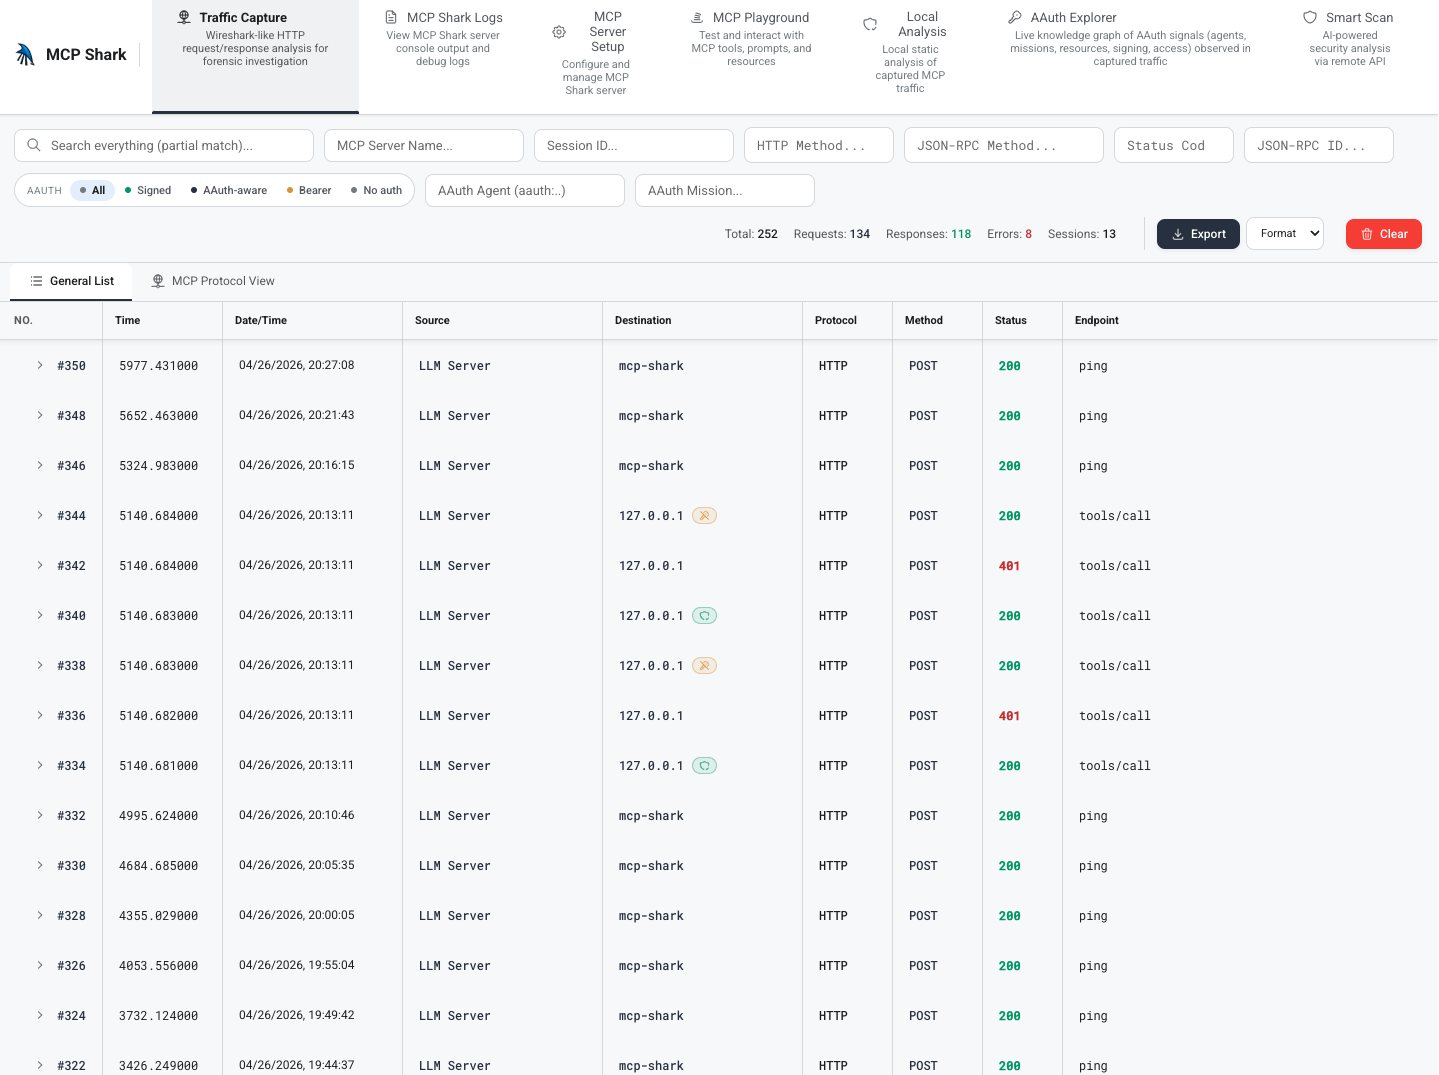
mcp-shark
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
ai-securityapi-securityconfiguration-auditing+7
179
mcp-shark/mcp-sharkWireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 roxanne_ardary/nullify
Automated, policy-driven data retention and deletion system with immutable audit trails, RBAC/ABAC, multi-jurisdiction compliance, and AI/ML…
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…
 aman-parmar/cve-2025-54554
CVE-2025-54554 – Unauthenticated Access in tiaudit REST API leading to Sensitive Information Disclosure
 mbadanoiu/cve-2019-11287
CVE-2019-11287: DoS via Heap Overflow in RabbitMQ Web Management Plugin
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
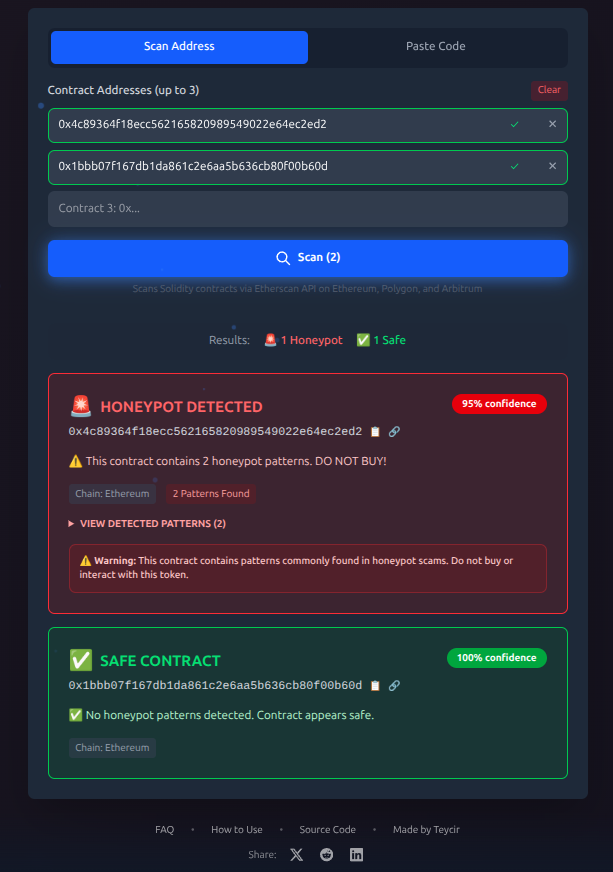 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
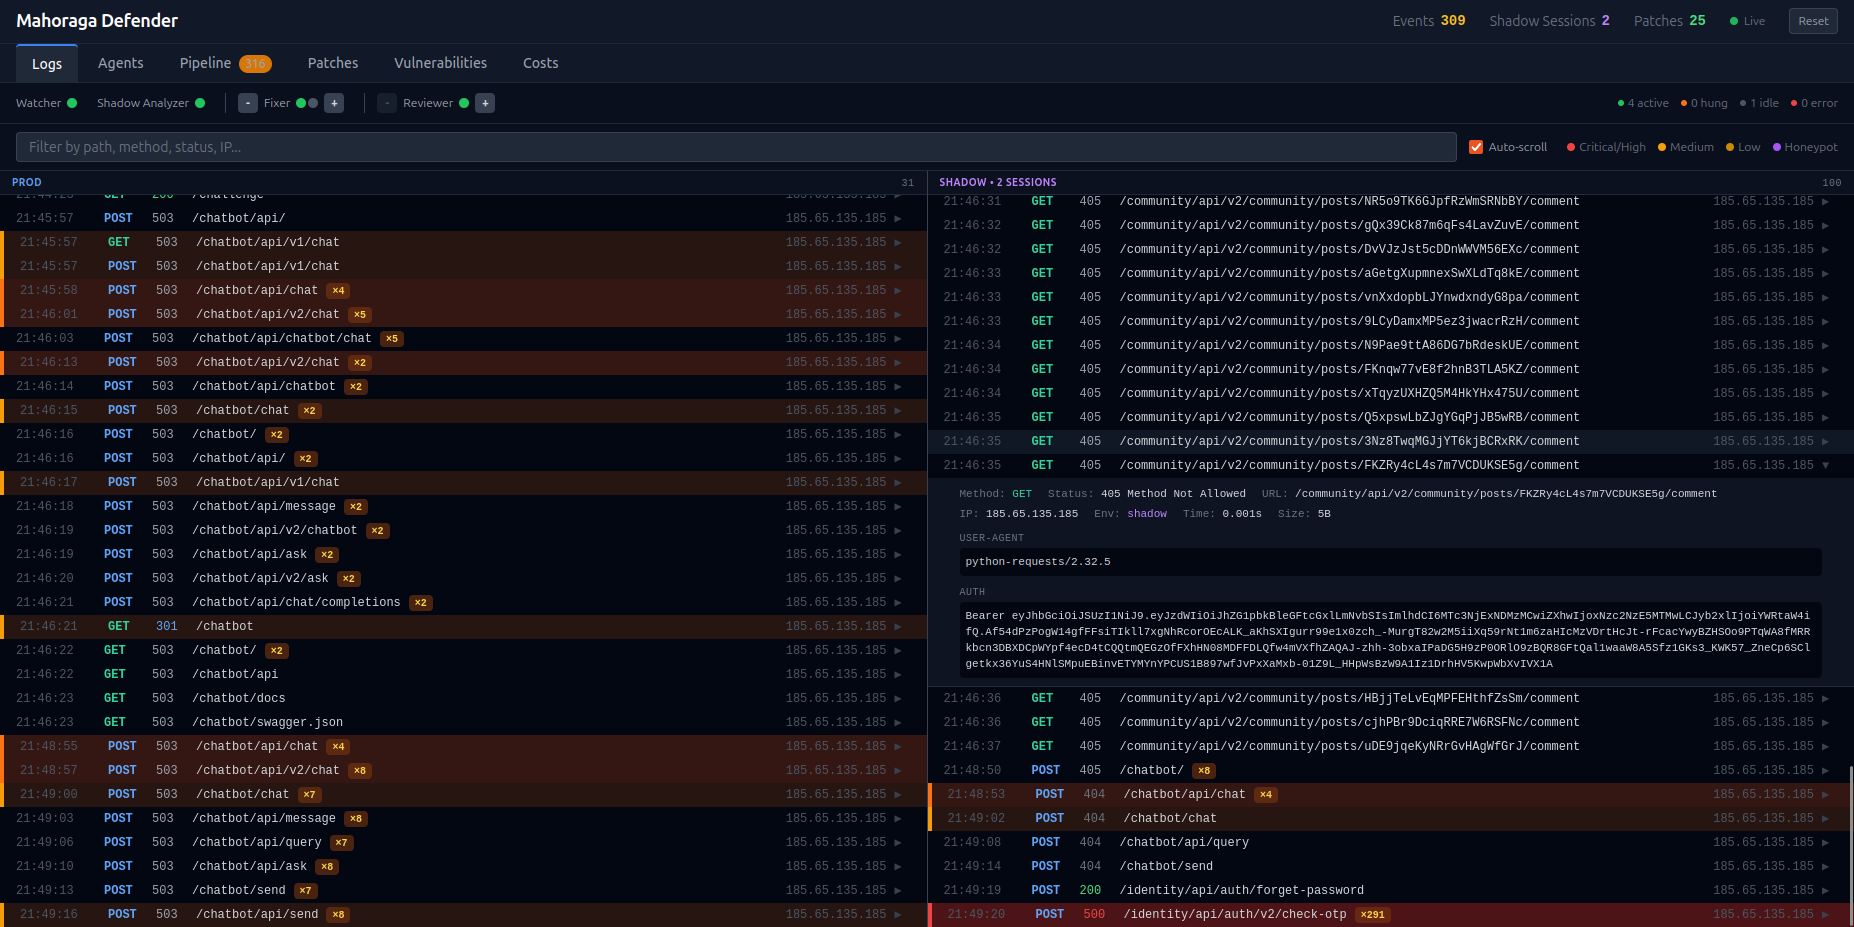 ageofalgorithms/mahoraga-webapp-defender
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.
 itsc1sco/mcpjam-to-root
From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation
 trandonga3/poc-cve-2026-63030-cve-2026-60137-
Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
 george0papasotiriou/cve-2026-3030-prototype-pollution-in-json-merge-patch
Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
 karlemilnikka/cve-2024-1208-and-cve-2024-1210
Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
 karlemilnikka/cve-2024-1209
Sensitive Information Exposure via assignments in LearnDash.