
iac-scan-runner
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
api-securitycloud-infrastructure-securityconfiguration-auditing+2
49
xlab-si/iac-scan-runnerService that scans your Infrastructure as Code for common vulnerabilities
 davkharrr/cve-2026-19478-poc
Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…
 m4xsec/apache-apisix-cve-2022-24112
Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
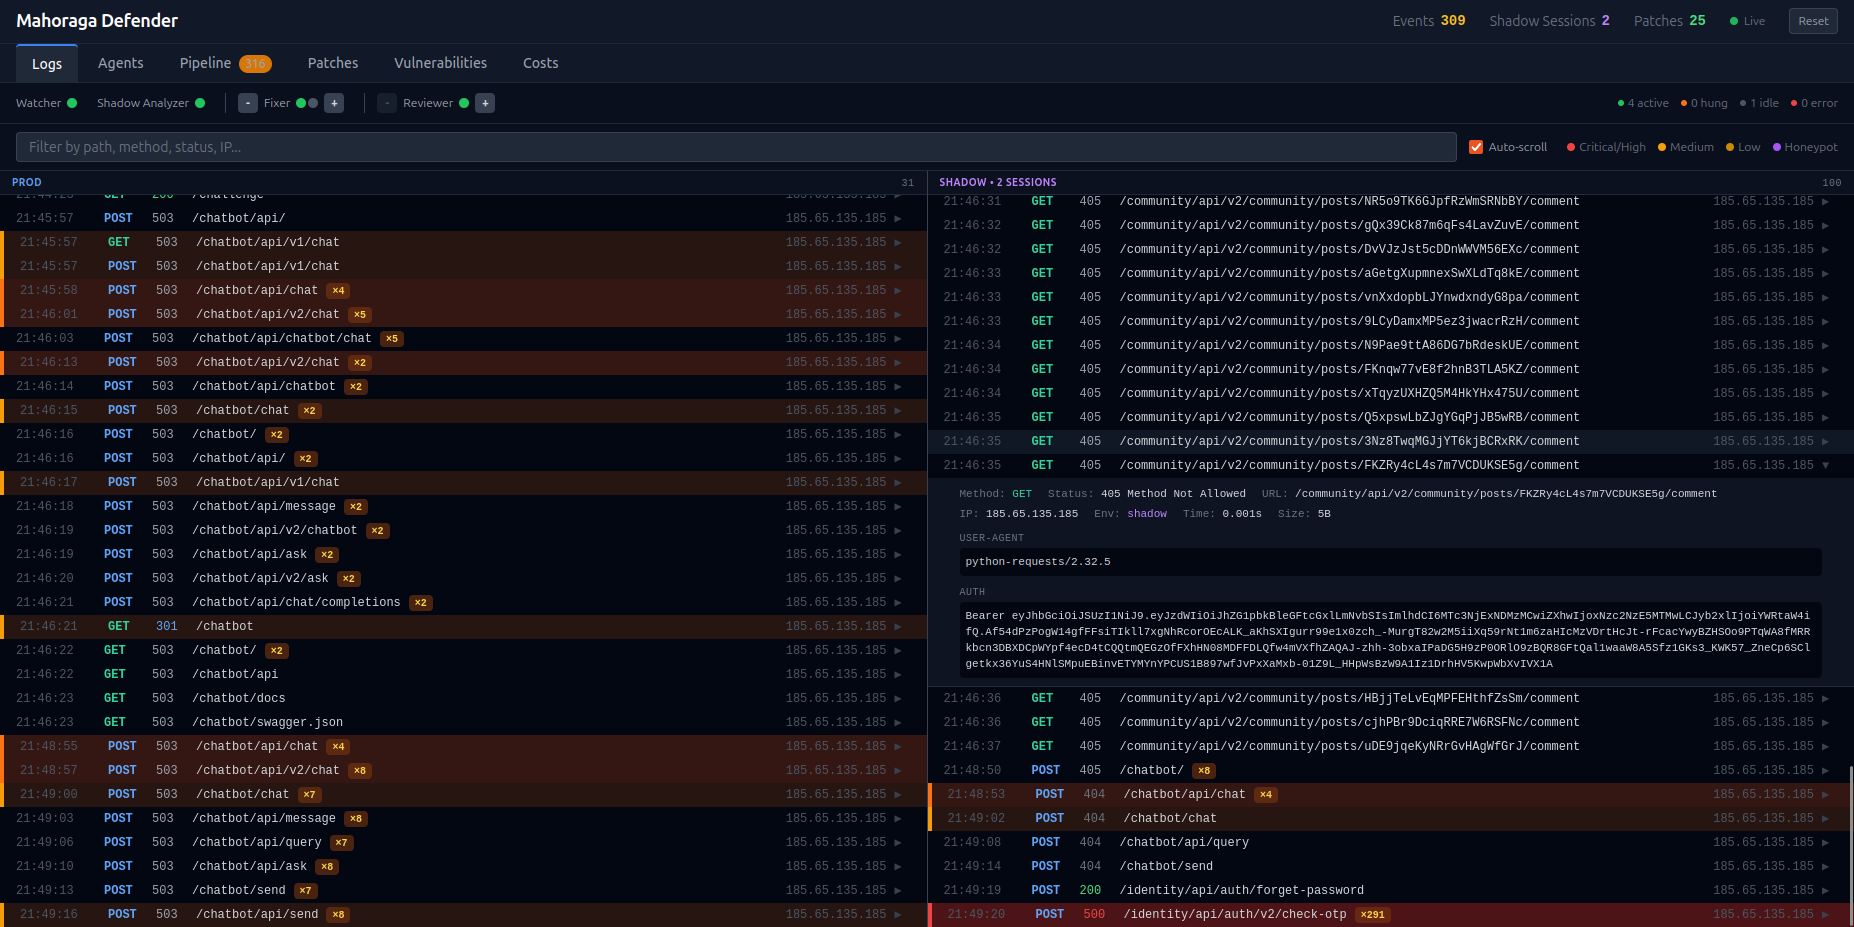 ageofalgorithms/mahoraga-webapp-defender
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 0xdak/cve-2026-59243_exploit
Exploit for Apache Airflow FAB OAuth authentication bypass (CVE-2026-59243) that achieves admin access and remote code execution by triggering a…
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 kit-lang/packages/kit-oauth
OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…
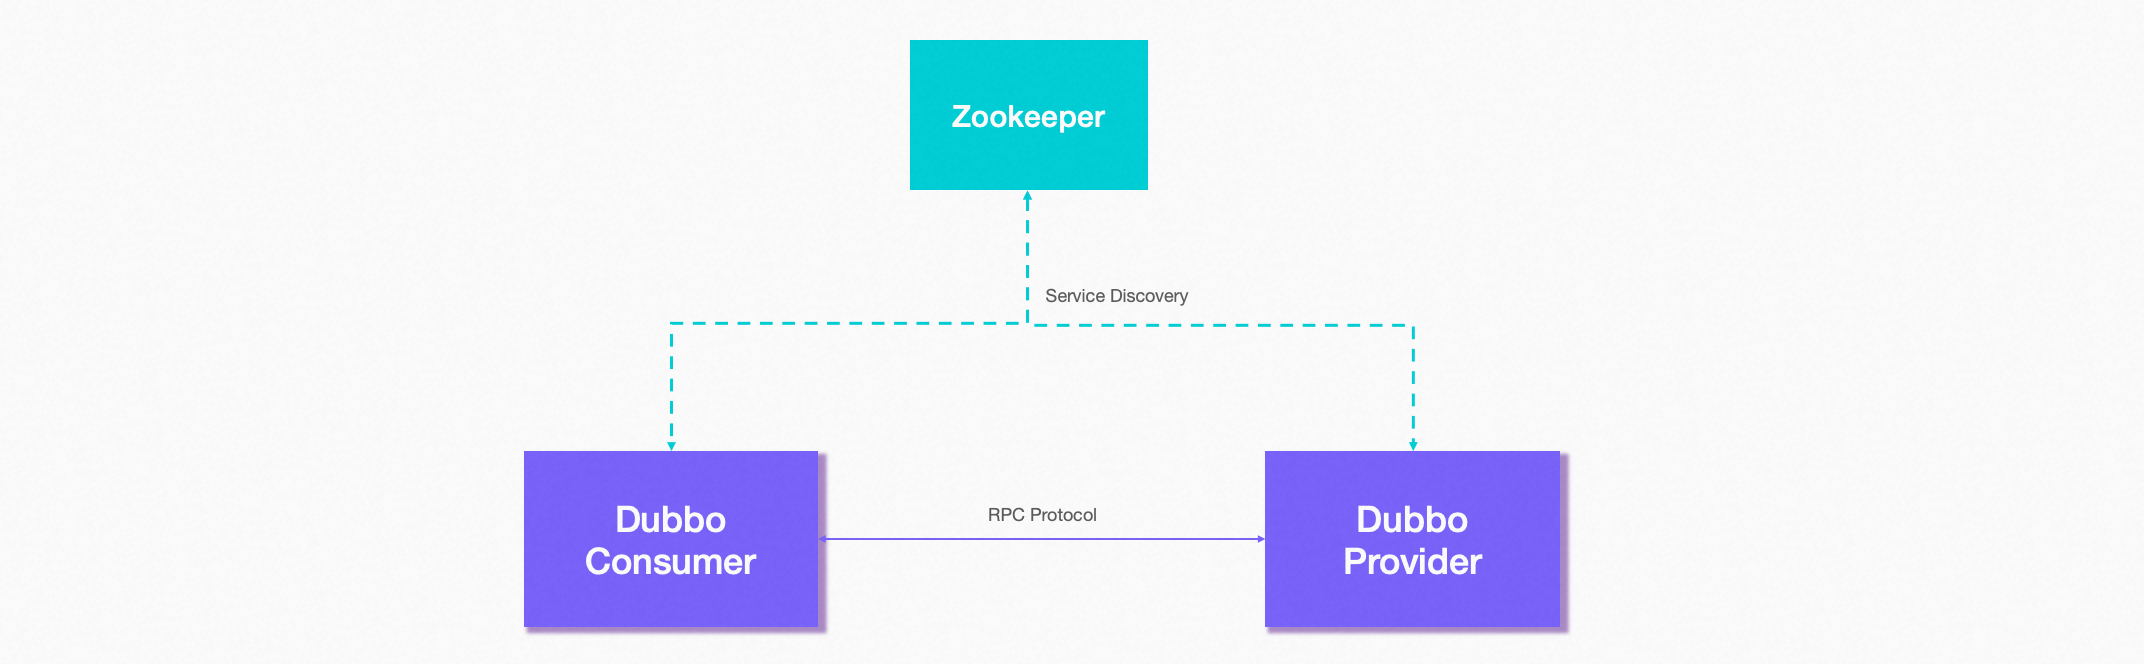 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 opnsense/core
OPNsense GUI, API and systems backend
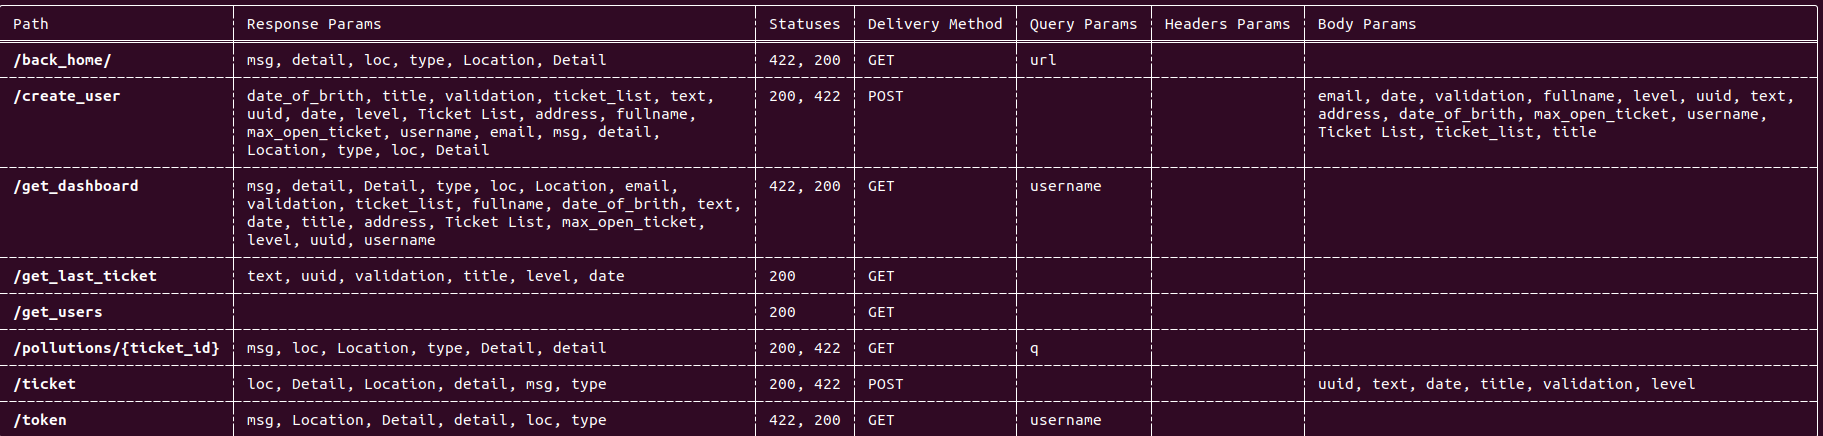 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
 sentrypeer/sentrypeer
Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 placeos/auth
PlaceOS authentication service and API gatekeeper.
 shadowforge-cyber/cve-2026-12944
Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.
 george0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-
Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…