

Nettacker
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
api-securityapi-security-testingdynamic-code-analysis+14
5.5k
owasp/nettackerAutomated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 sanjith1236/cve-2026-8206-kirki-exploit-analysis
Technical reconstruction and proof-of-concept for CVE-2026-8206, an unauthenticated account takeover in the WordPress Kirki plugin, with detection…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 owasp/apts
OWASP Autonomous Penetration Testing Standard
 itsc1sco/mcpjam-to-root
From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation
 trandonga3/poc-cve-2026-63030-cve-2026-60137-
Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
 george0papasotiriou/cve-2026-3030-prototype-pollution-in-json-merge-patch
Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
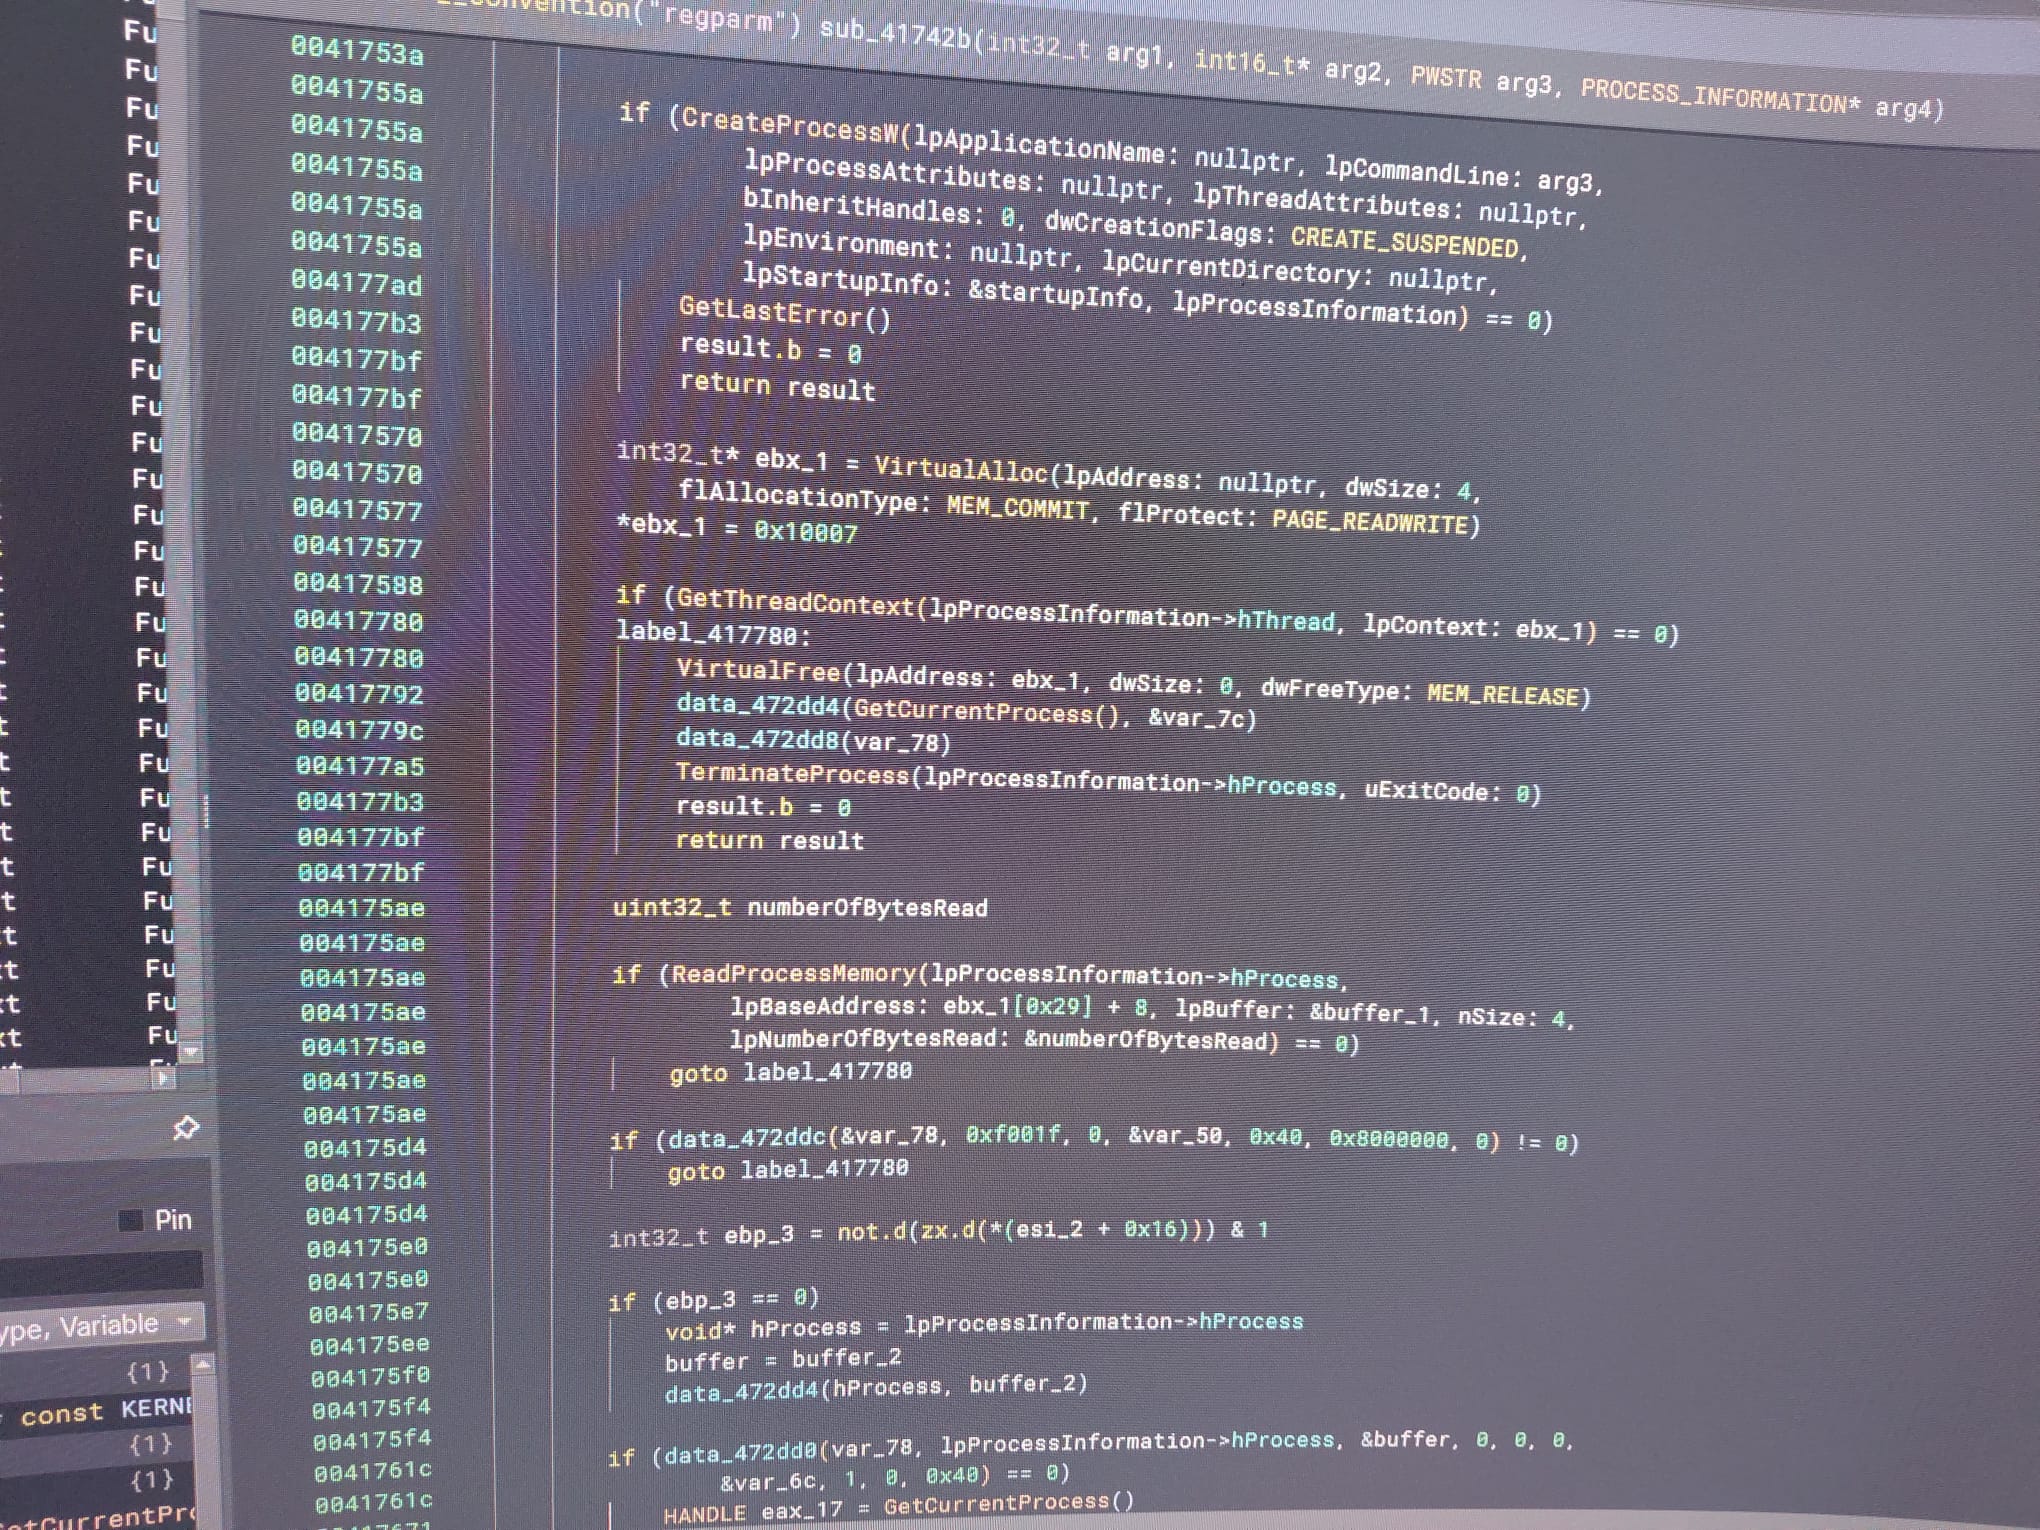 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 biitts/cve-2026-49230-apisix-jwe-decrypt-auth-bypass
PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
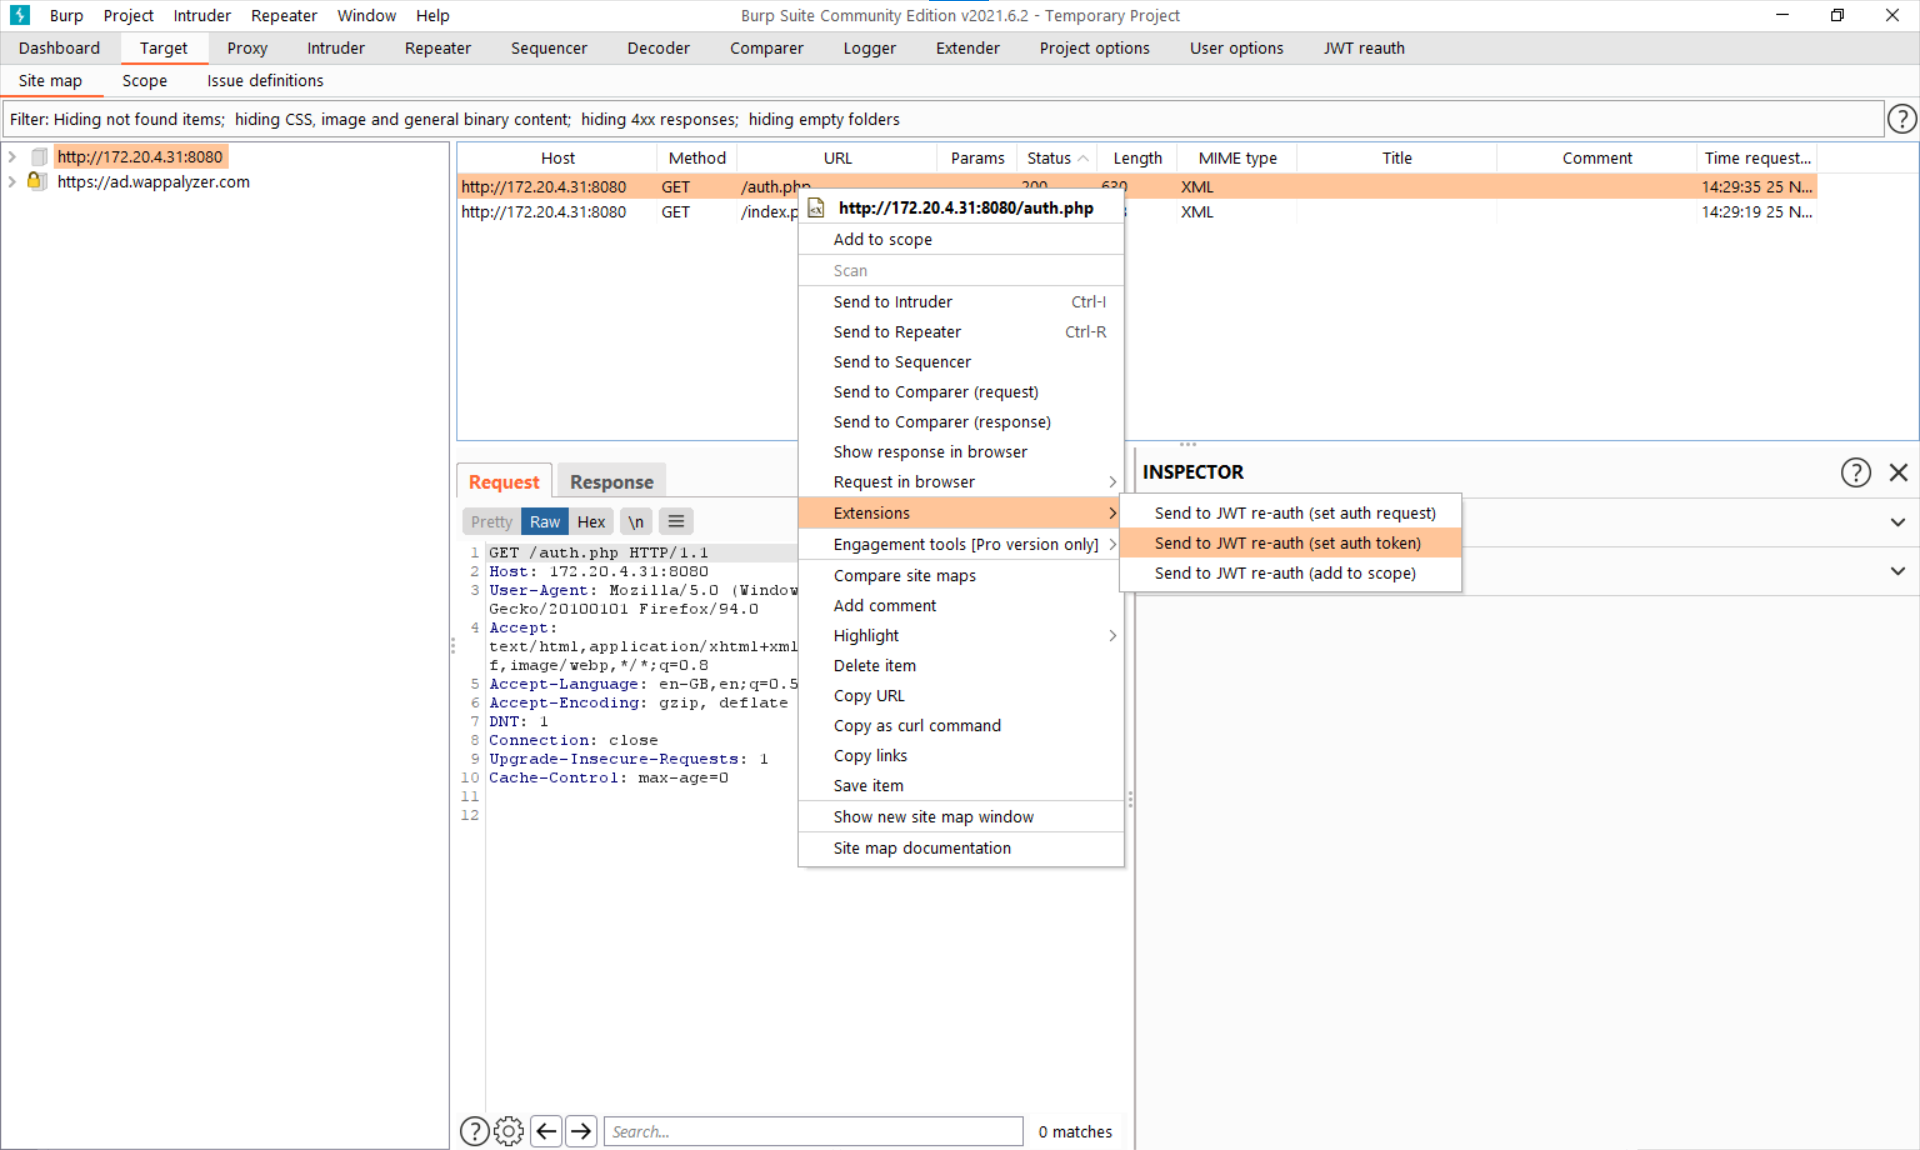 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.