
PentestingEverything
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
api-securitycloud-securityctf+9
2.2k
m14r41/pentestingeverythingComplete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 bytesizedmarius/rewerse-engineering
Rewe API reverse engineering in Go
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 itsc1sco/mcpjam-to-root
From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation
 trandonga3/poc-cve-2026-63030-cve-2026-60137-
Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
 george0papasotiriou/cve-2026-3030-prototype-pollution-in-json-merge-patch
Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 horkimhab/cve-wazuh
Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
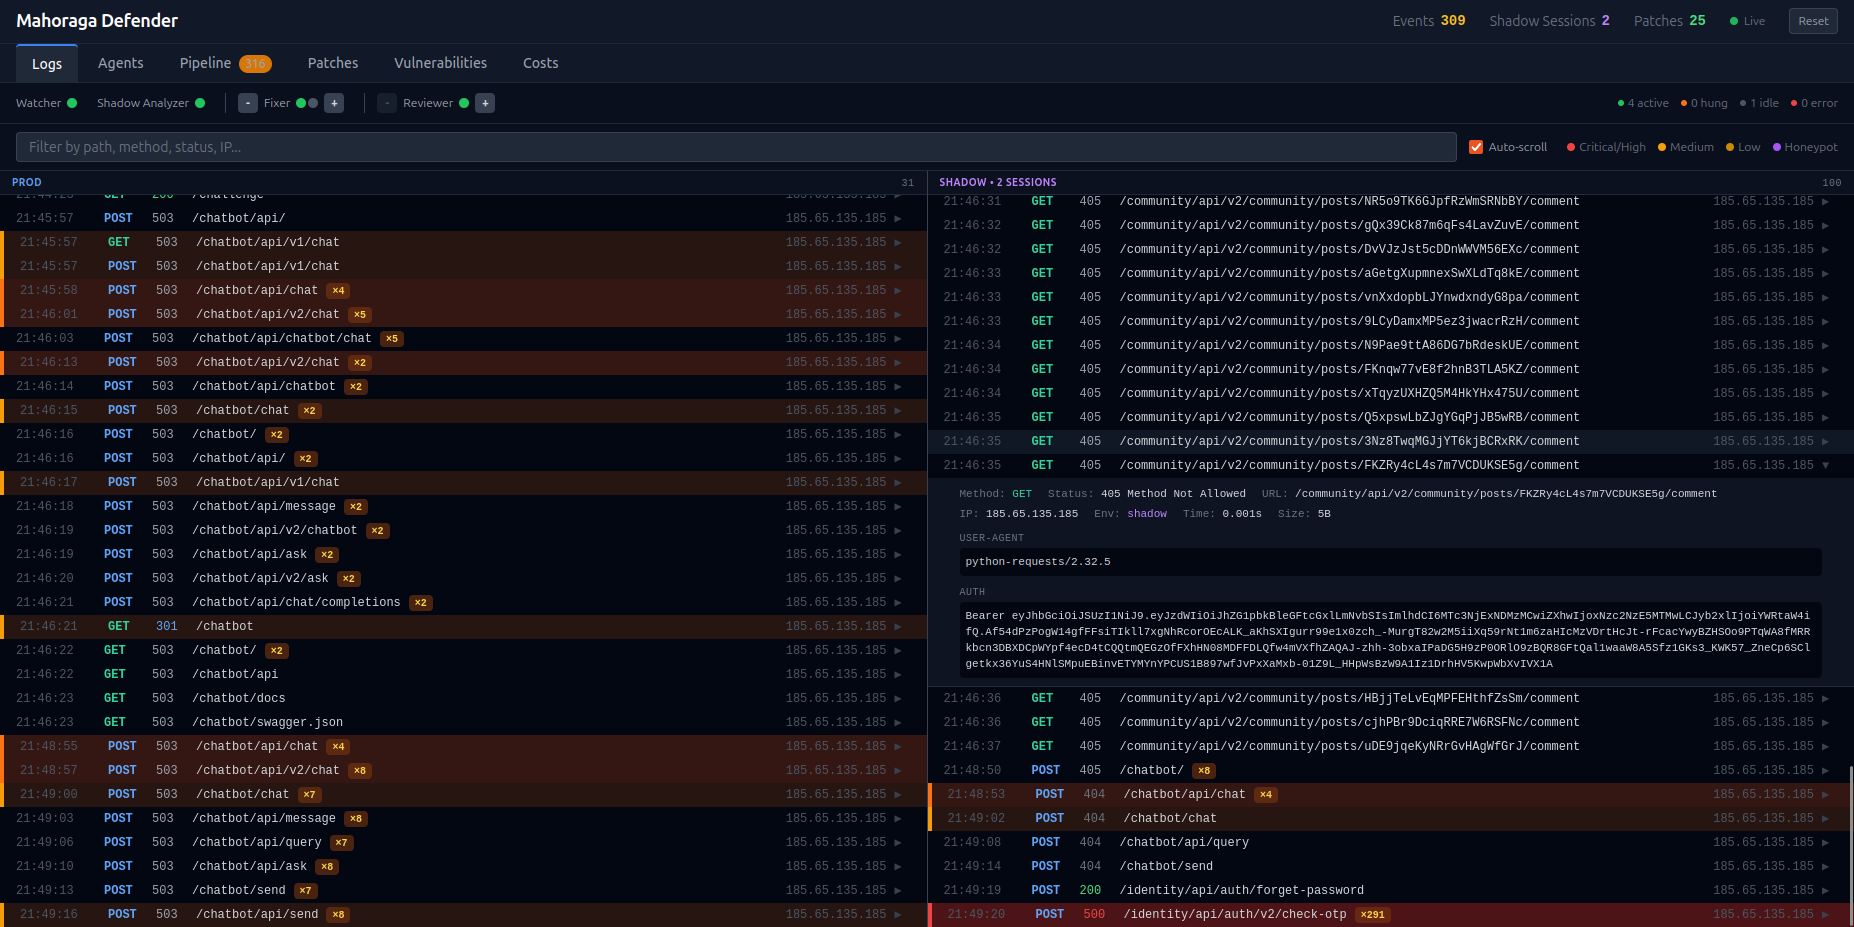 ageofalgorithms/mahoraga-webapp-defender
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
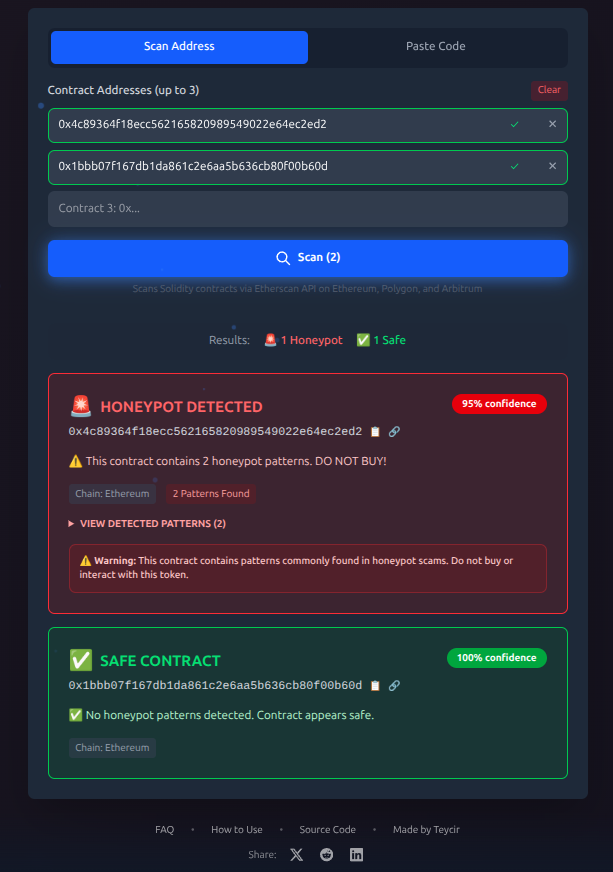 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 filipegaudard/cve-2026-30945-poc
Proof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…