

opa
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
api-securityauthenticationauthentication-authorization+10
12.4k
open-policy-agent/opaDeclarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 cerbos/cerbos
Authorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
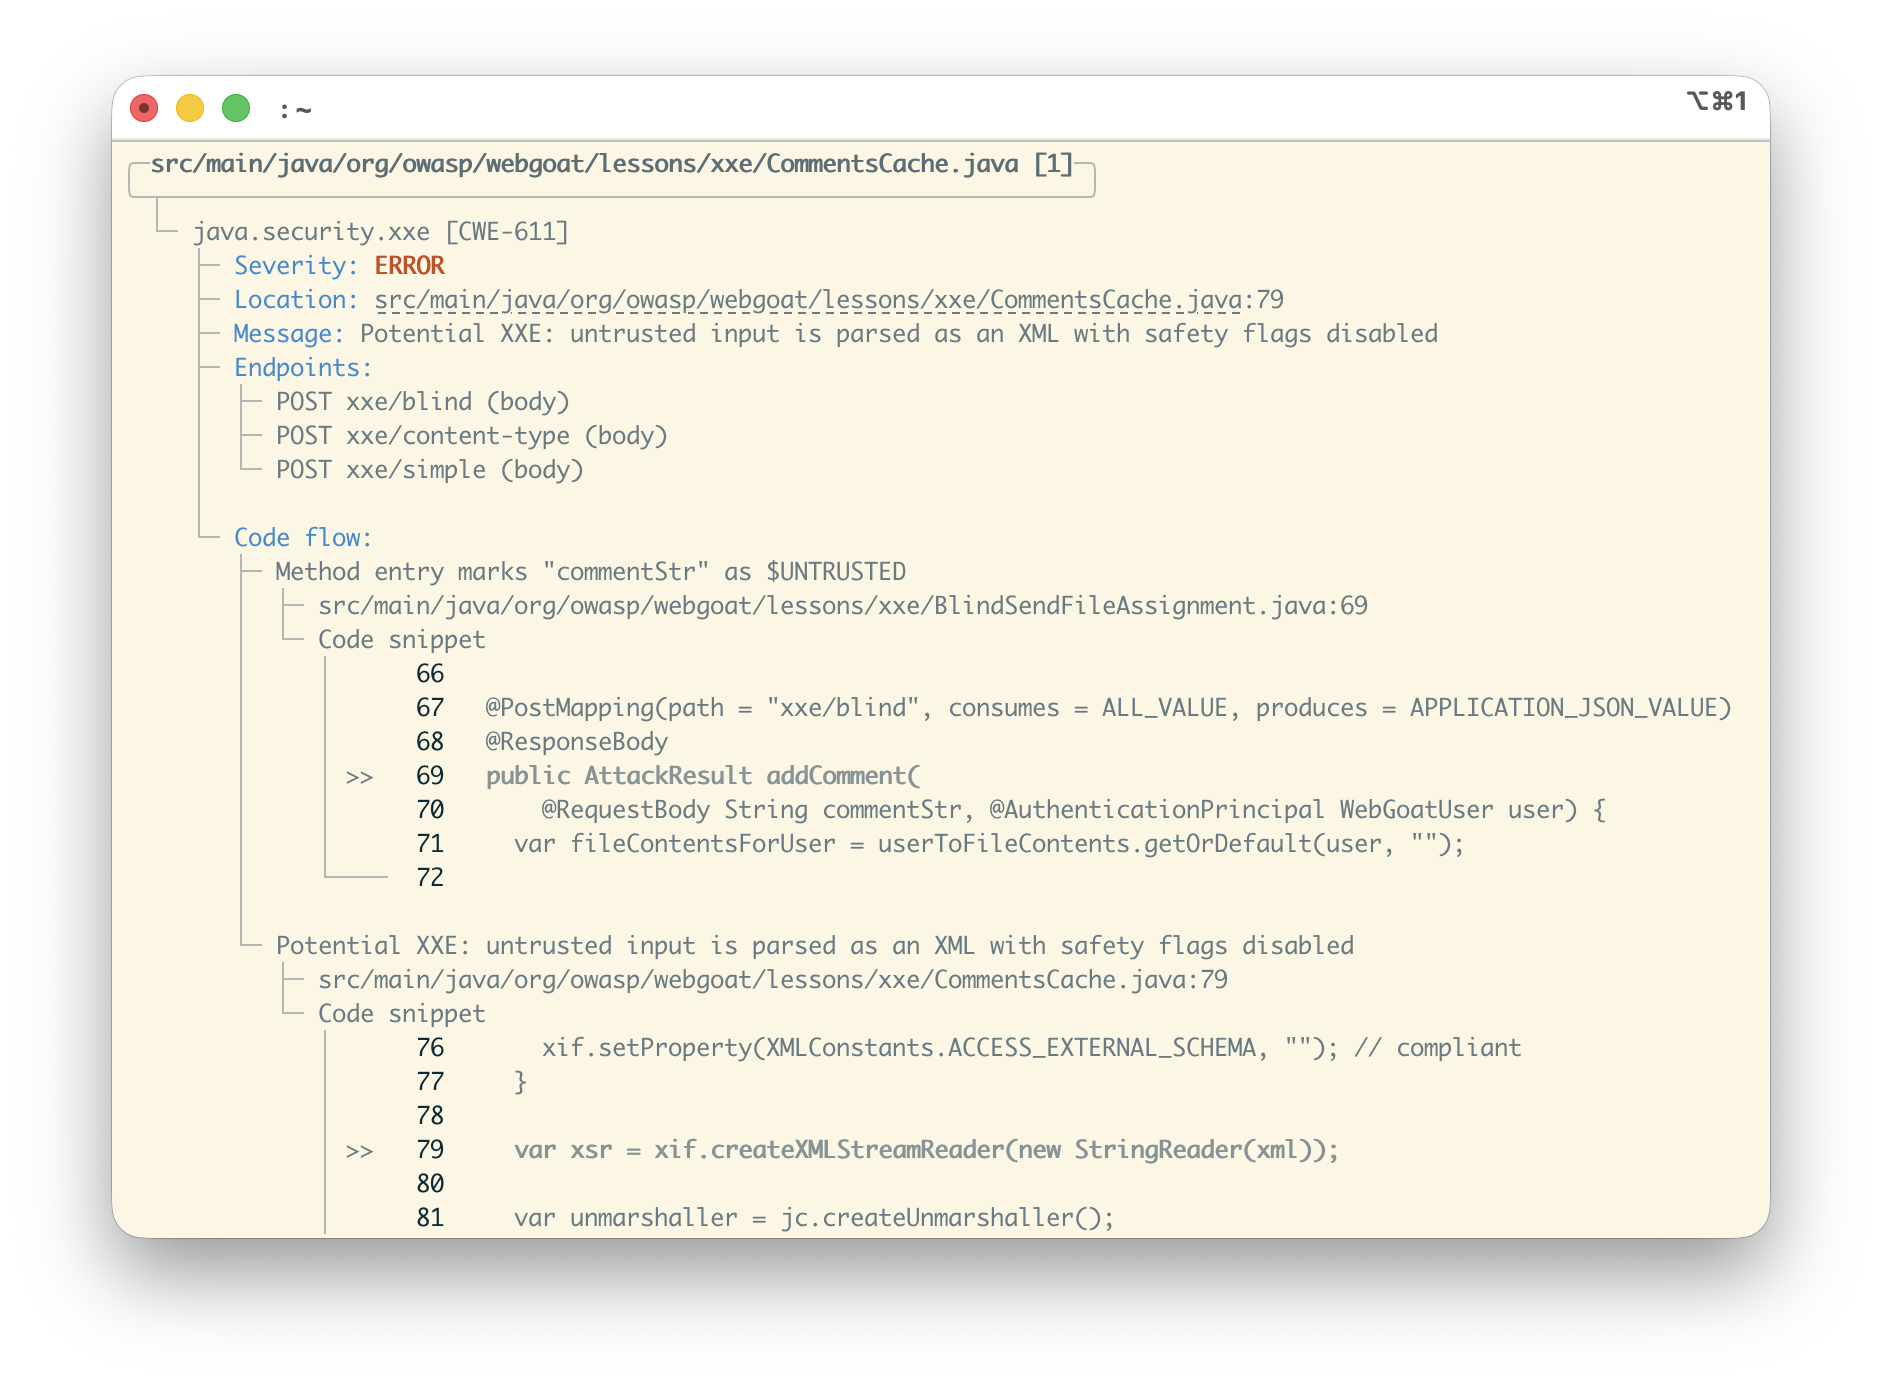 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
 randomrobbiebf/cve-2025-67923
JetEngine <= 3.7.7 — Unauthenticated Stored Cross-Site Scripting via CCT REST API
 qarait/gate0
A small, auditable, terminating, deterministic micro-policy engine
 secsys-fdu/cve-2025-51869
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Liner's chat component, allowing attackers to tamper with other users'…
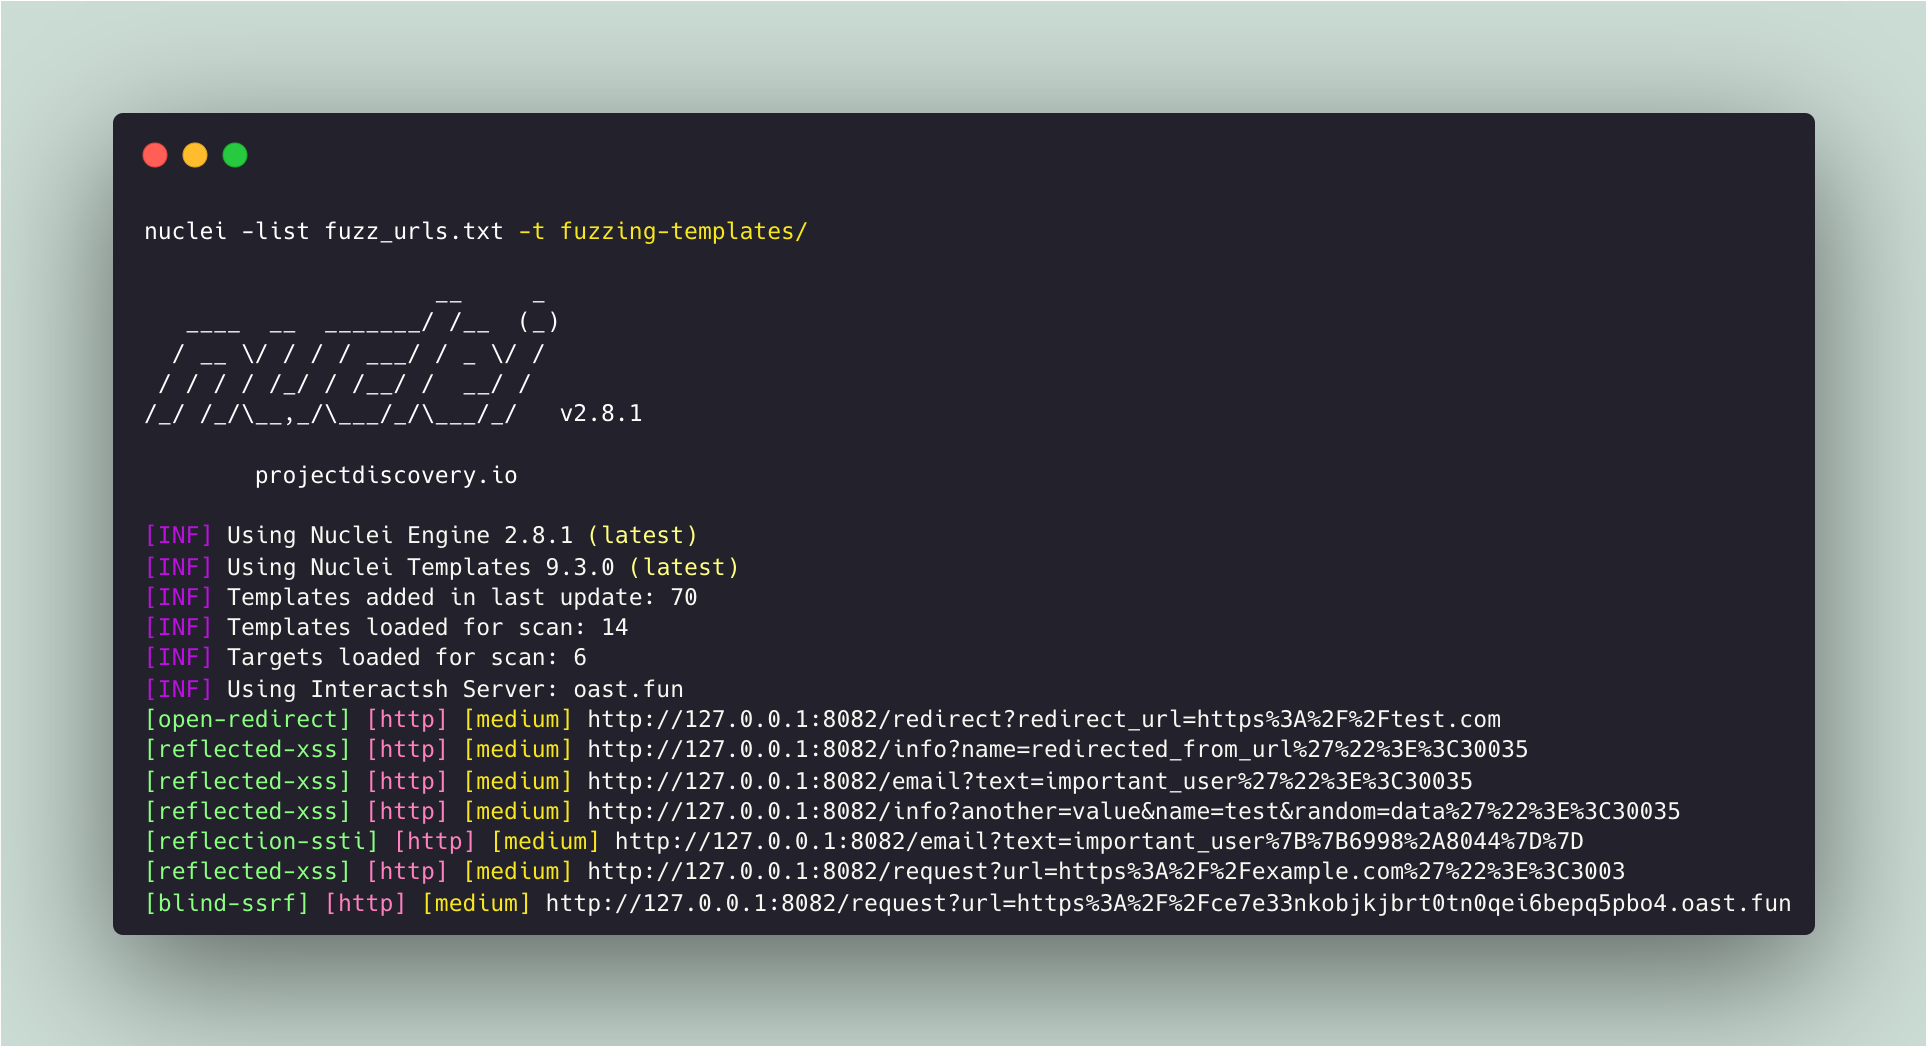 projectdiscovery/fuzzing-templates
Community curated list of nuclei templates for finding "unknown" security vulnerabilities.
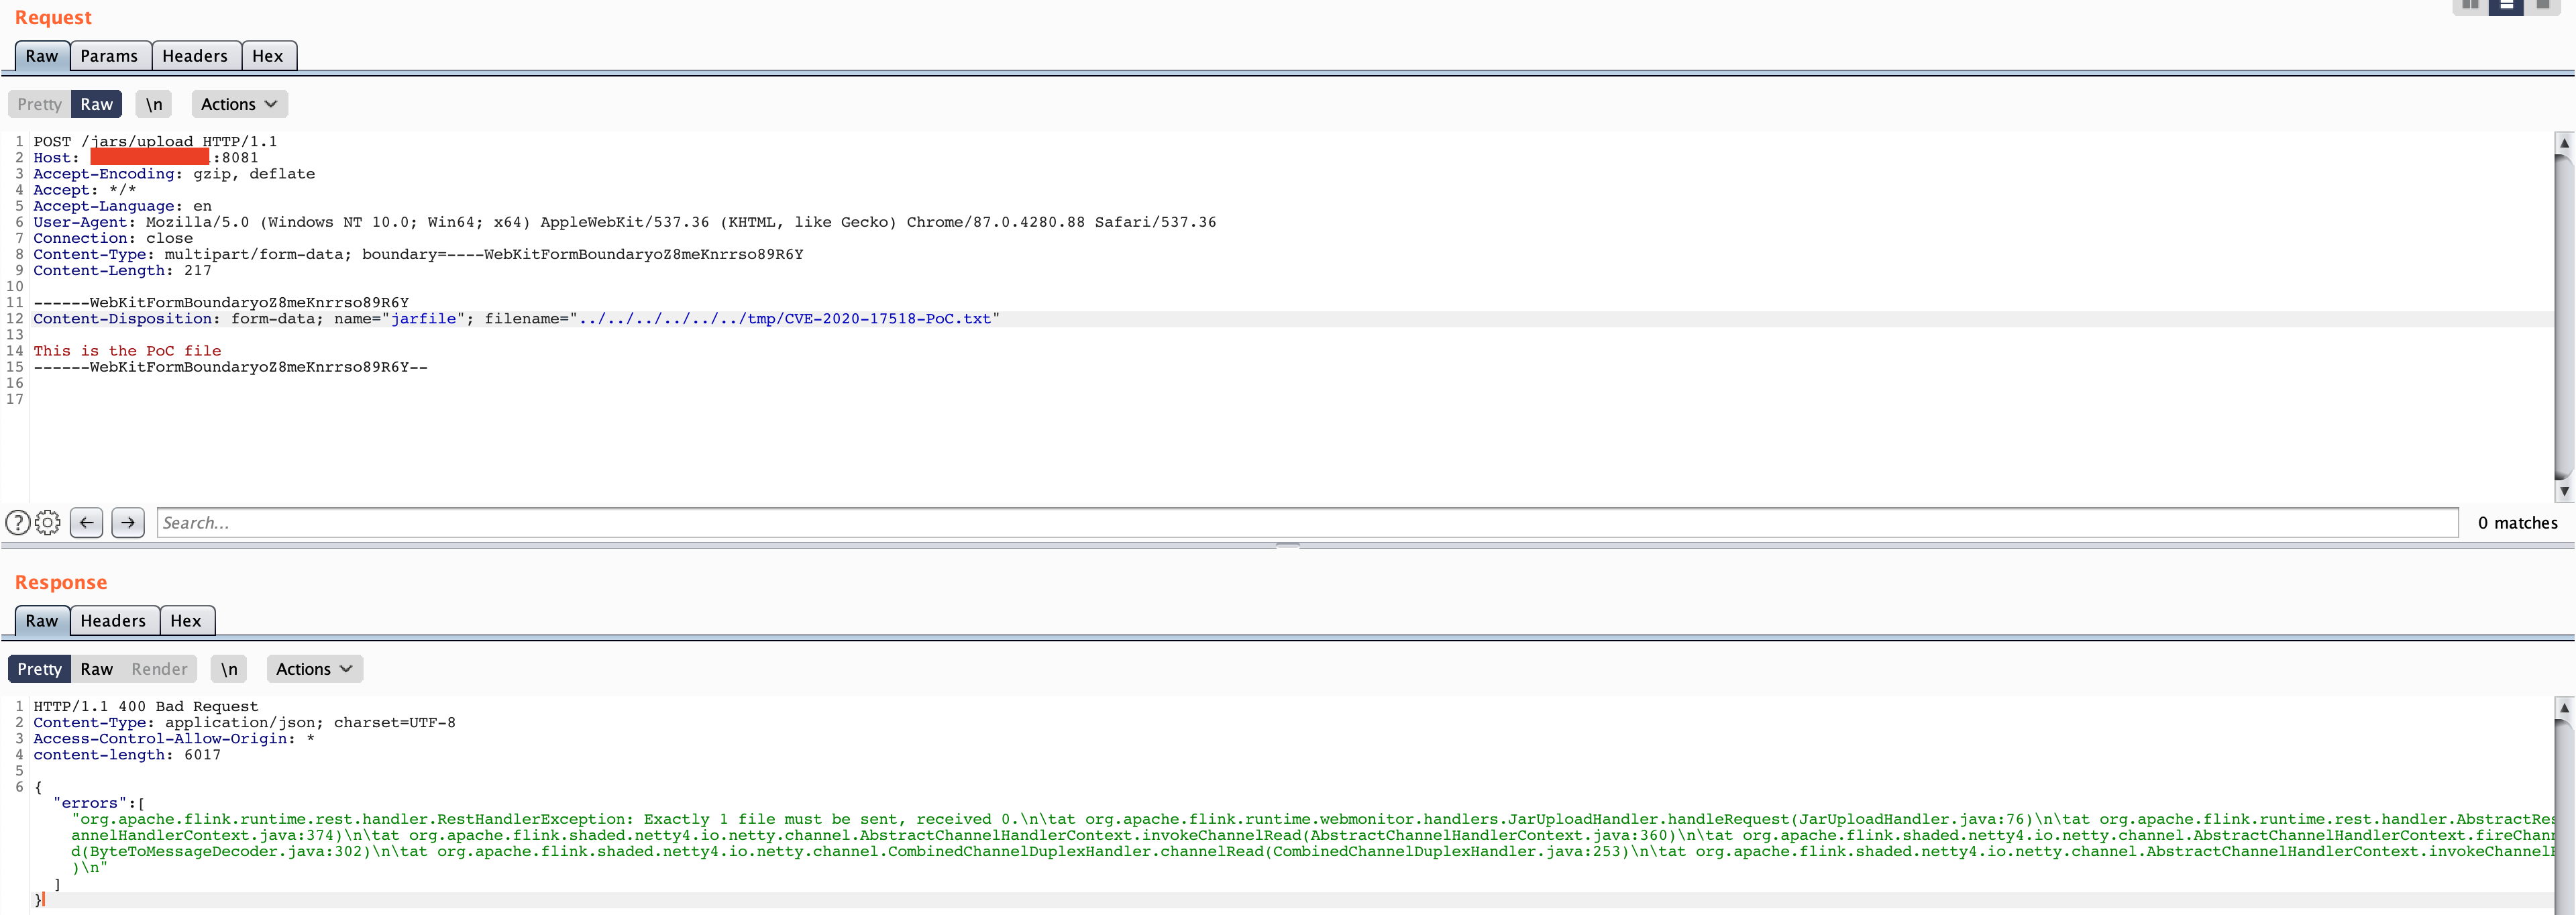 murataydemir/cve-2020-17518
[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal