vulnerability-Checklist

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.

Jellyfin Server 12.2 - High - Remote - IDOR - public playlist ItemIds leftover of GHSA-9x85 then unauth stream

Jellyfin Server 12.2 - High - Remote - IDOR - GET /Items/Suggestions omit-userId dumps hidden library Path and IDs

OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - File read - Snort rules {file} decode-then-join

Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.

Demonstrates a Gitea account-enumeration oracle: authenticated PUT /api/v1/user/following/{username} returns 204 for hidden accounts and 404 for…

Proof-of-concept and lab for an unauthenticated Gitea information disclosure: the stargazers and watchers API leaks usernames that profile endpoints…

Proof-of-concept and lab for a Gitea IDOR (CWE-639) in GET /api/v1/user/keys/{id}, letting an authenticated read:user token enumerate other users'…

Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL

VulnCheck's official command line tool

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks

A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API

Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php

Report summary and local proof-of-concept script demonstrating CVE-2026-103440, a PageTriage API disclosure of suppressed reviewer usernames on…

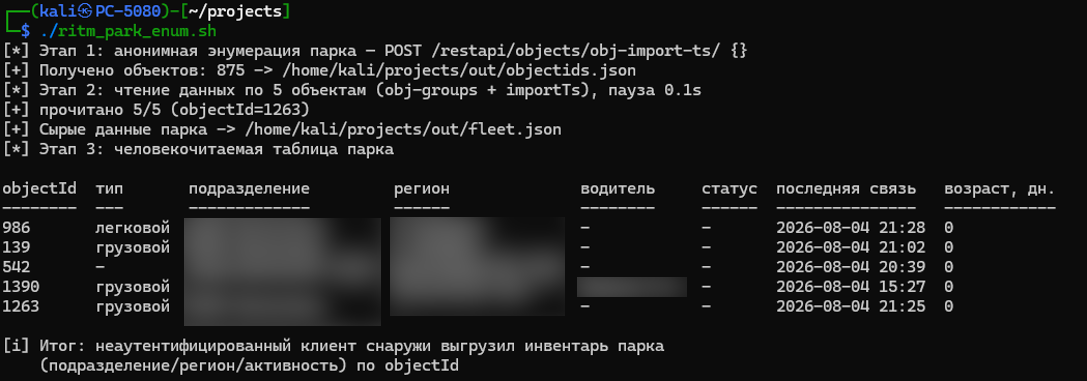
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.

Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…