
pyrasp
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
ai-securityanomaly-detectionapi-security+6
39
rbidou/pyraspRuntime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 ch4n3-yoon/cve-2025-62727-demo
Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
 george0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass
Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…
 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 wadesweaponshed/checkpoint-cve-webscanner
A web version of the bash scripts wrote for Check Point CVE-2026-50751 and CVE-2026-50752. This uses a local server to scan and make changes using…
 qarait/gate0
A small, auditable, terminating, deterministic micro-policy engine
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 jassics/security-study-plan
Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
 cilium/cilium
eBPF-based Networking, Security, and Observability
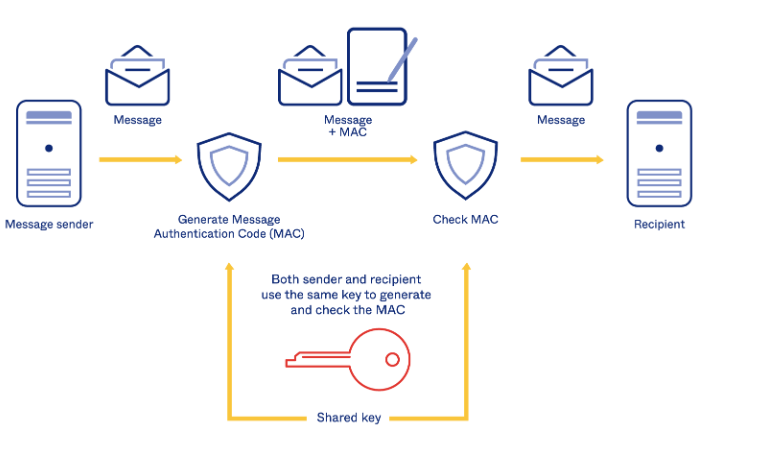 password123456/about-hmac
HMAC Implementation Example and Explanation
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
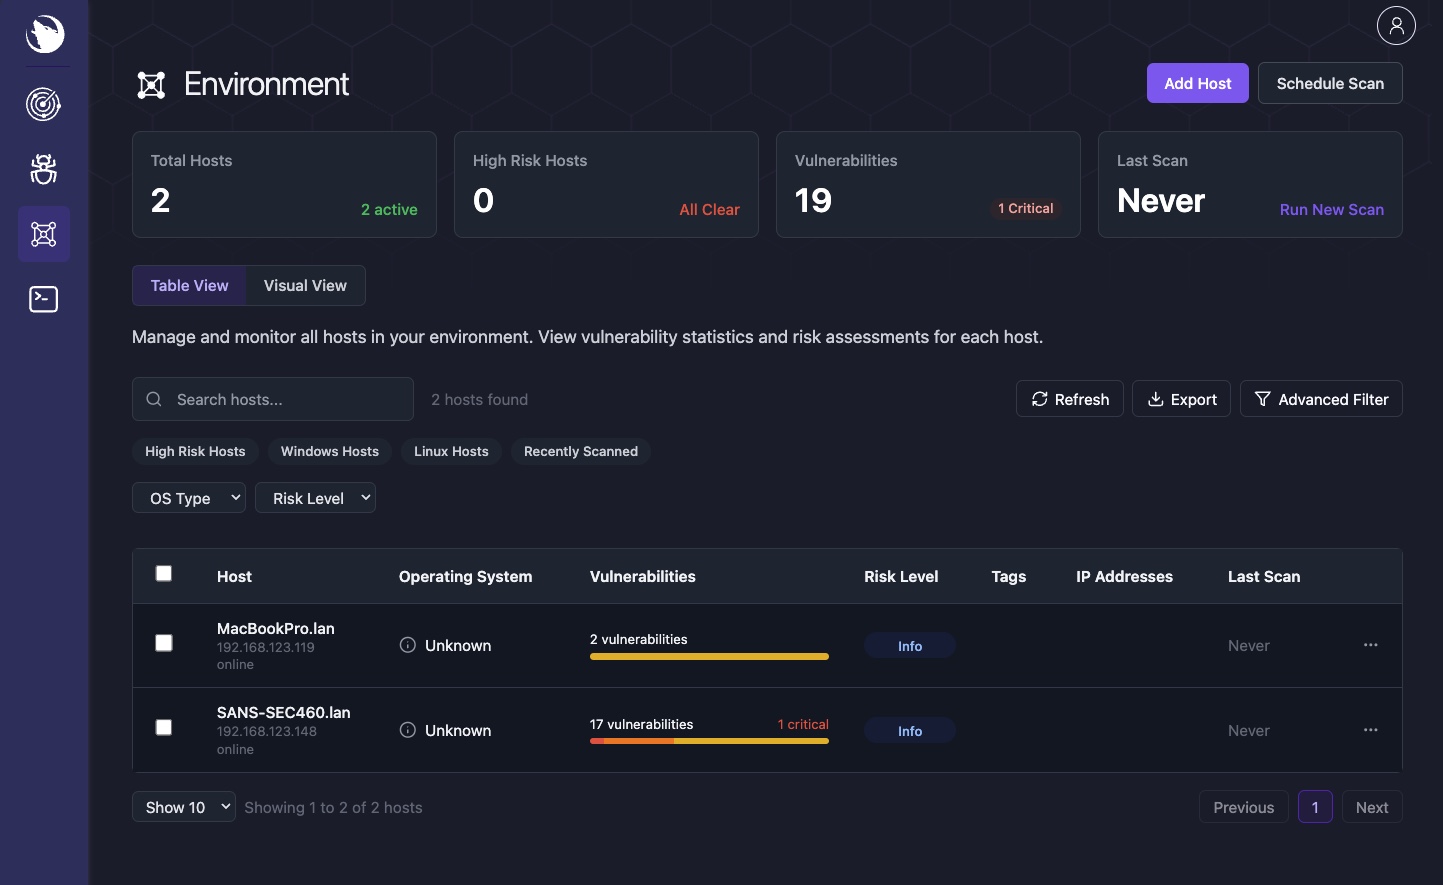 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…