
keycloak
 keycloak/keycloak
Open Source Identity and Access Management For Modern Applications and Services
api-securityauthenticationauthentication-authorization+3
37.1k
keycloak/keycloakOpen Source Identity and Access Management For Modern Applications and Services
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 apache/brpc
Industrial-grade C++ RPC framework for building high-performance distributed systems, supporting multiple protocols (HTTP, gRPC, Redis, Thrift) with…
 roxanne_ardary/nullify
Automated, policy-driven data retention and deletion system with immutable audit trails, RBAC/ABAC, multi-jurisdiction compliance, and AI/ML…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 cloudgraphdev/cli
The universal GraphQL API and CSPM tool for AWS, Azure, GCP, K8s, and tencent.
 ory/hydra
OpenID Certified OAuth 2.0 and OpenID Connect provider for token issuance, client management, JWKS, and login/consent flow orchestration via headless…
 ory/kratos
API-first identity and user management system for cloud-native applications. Handles login, registration, MFA, recovery, and profile management with…
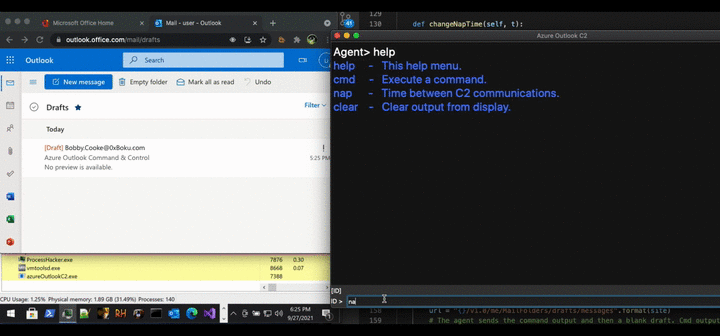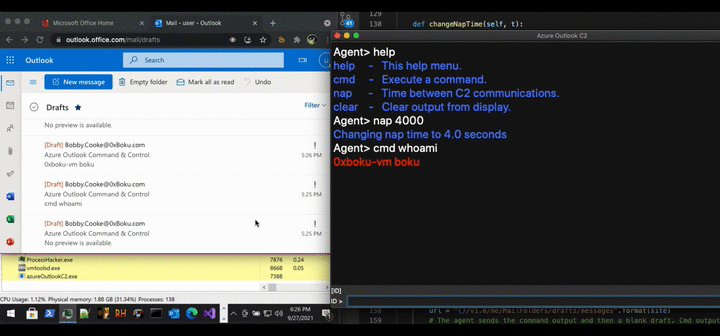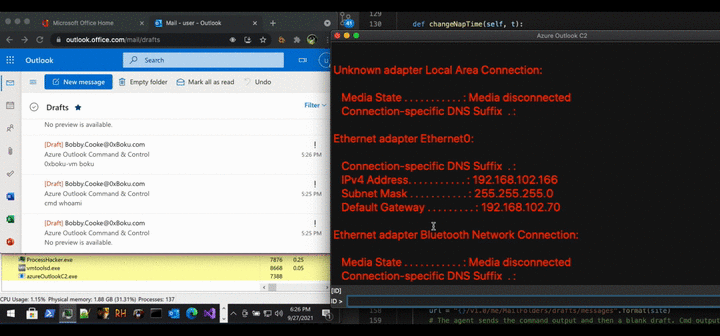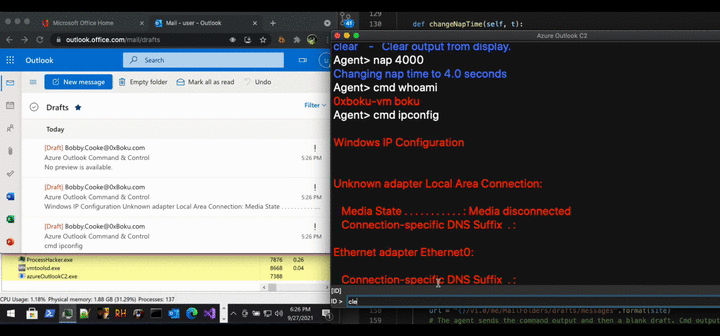 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 rabbitsafe/cve-2021-37580
Proof-of-concept exploit for Apache ShenYu Admin JWT authentication bypass (CVE-2021-37580). Includes a scanning script to detect vulnerable…
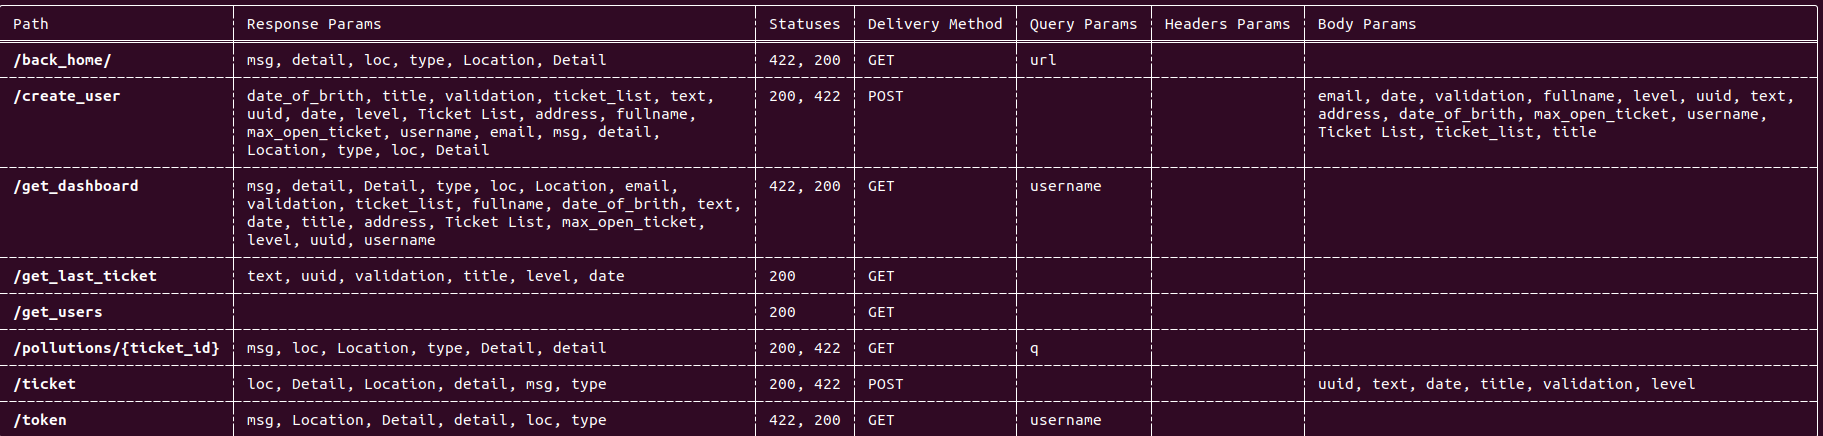 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…