

APIHarvester
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
api-securityapi-security-testingcrawler+9
35
piratesshield/apiharvesterThe one shot API attacker tool - finds the API url from the given root simulate the automated attacks
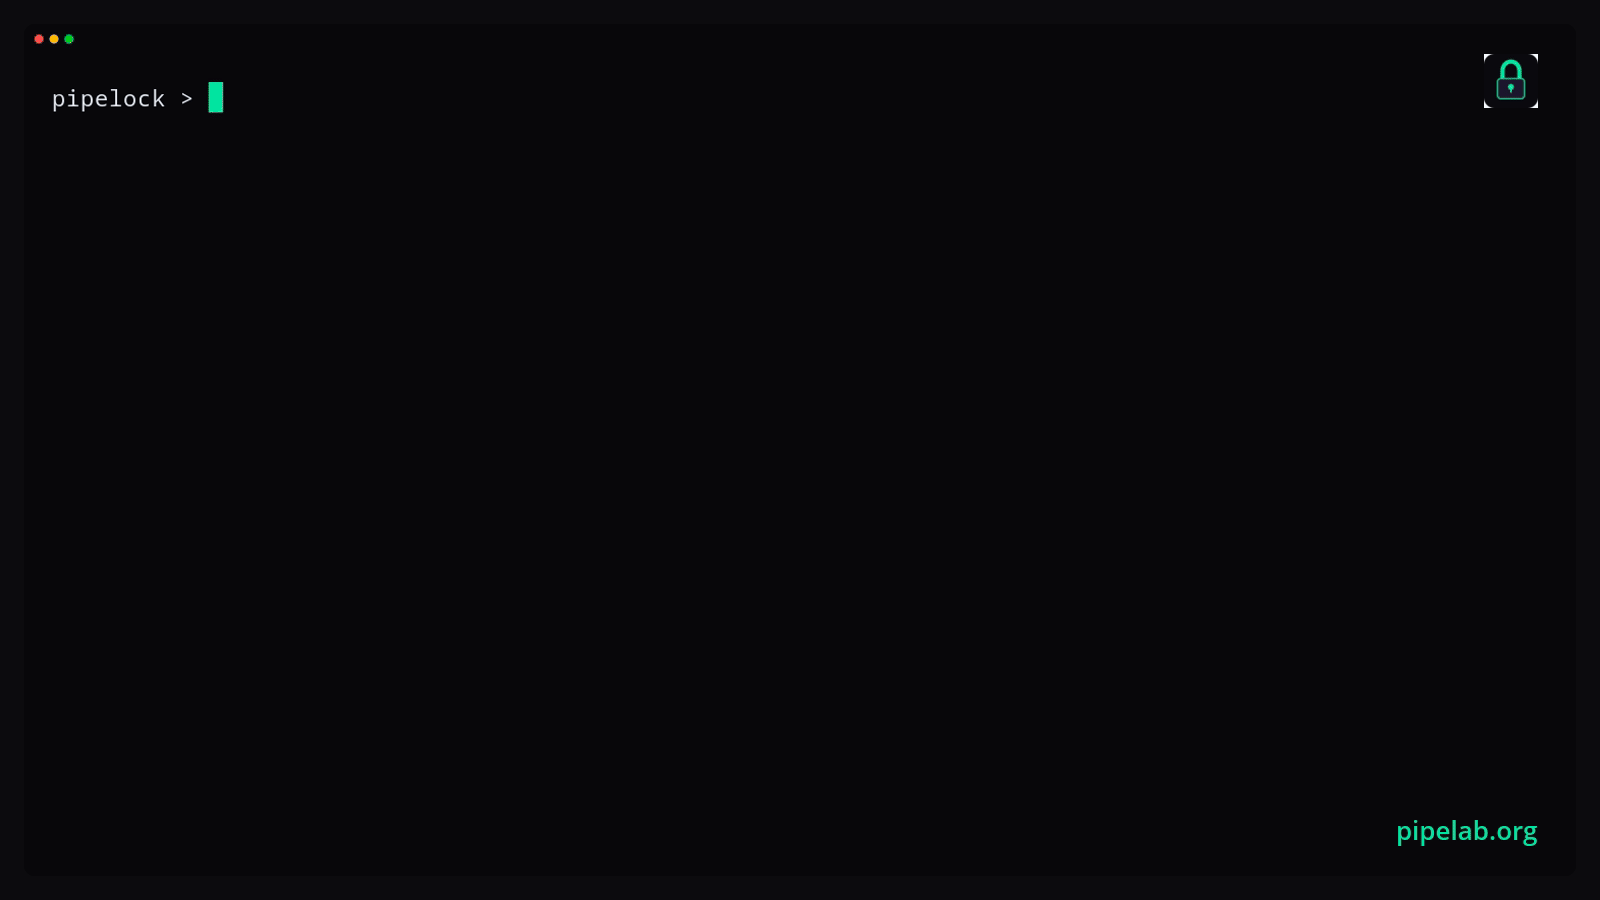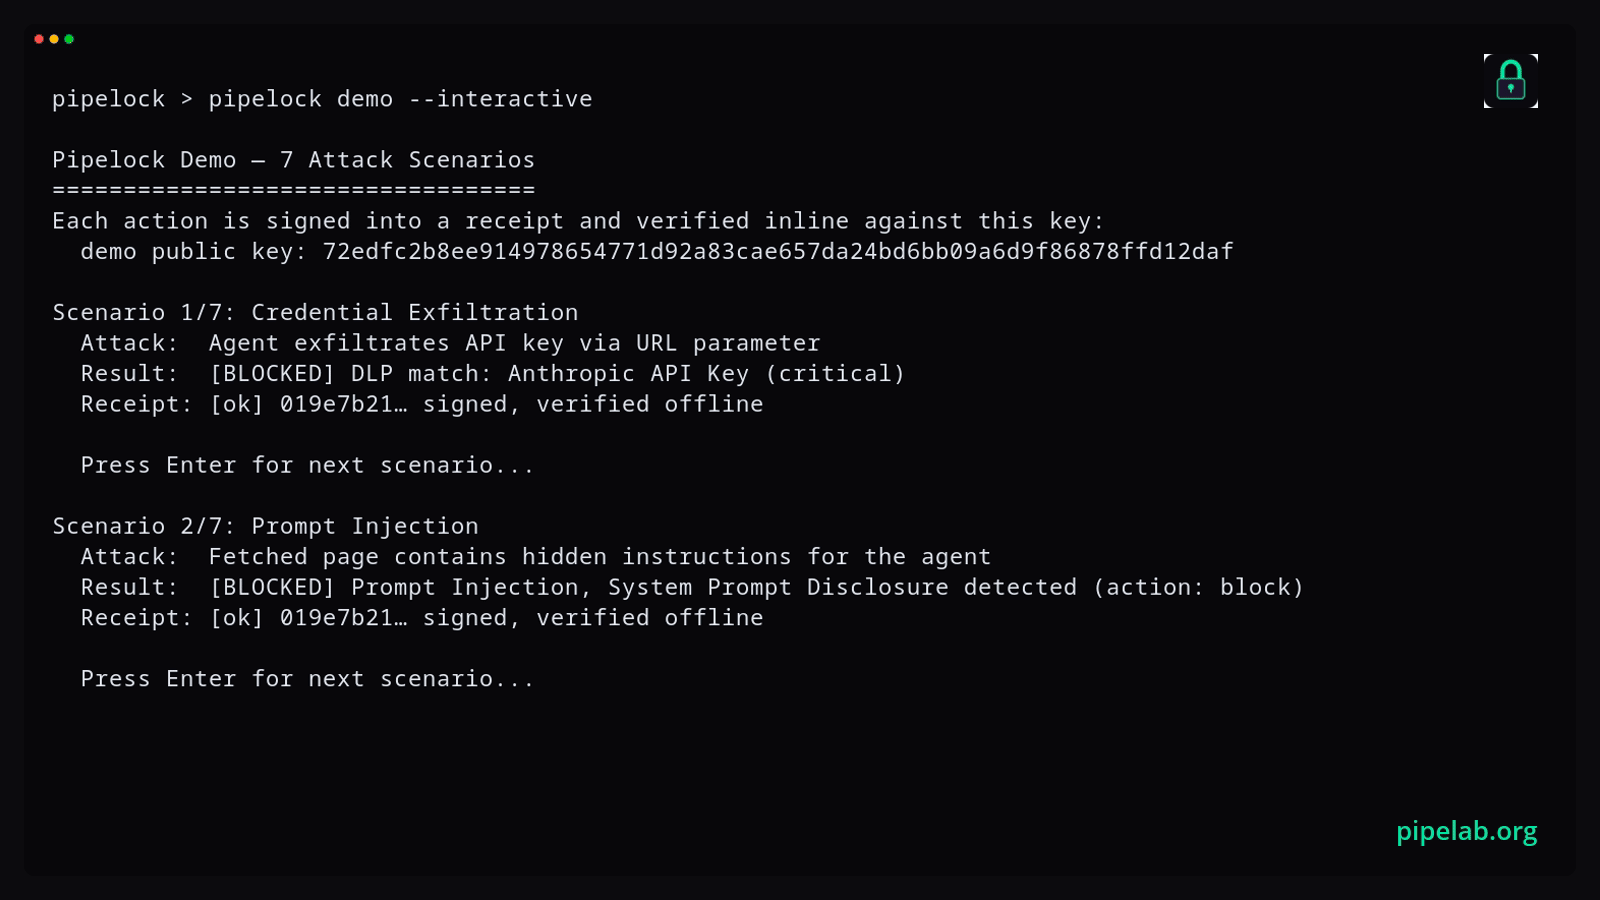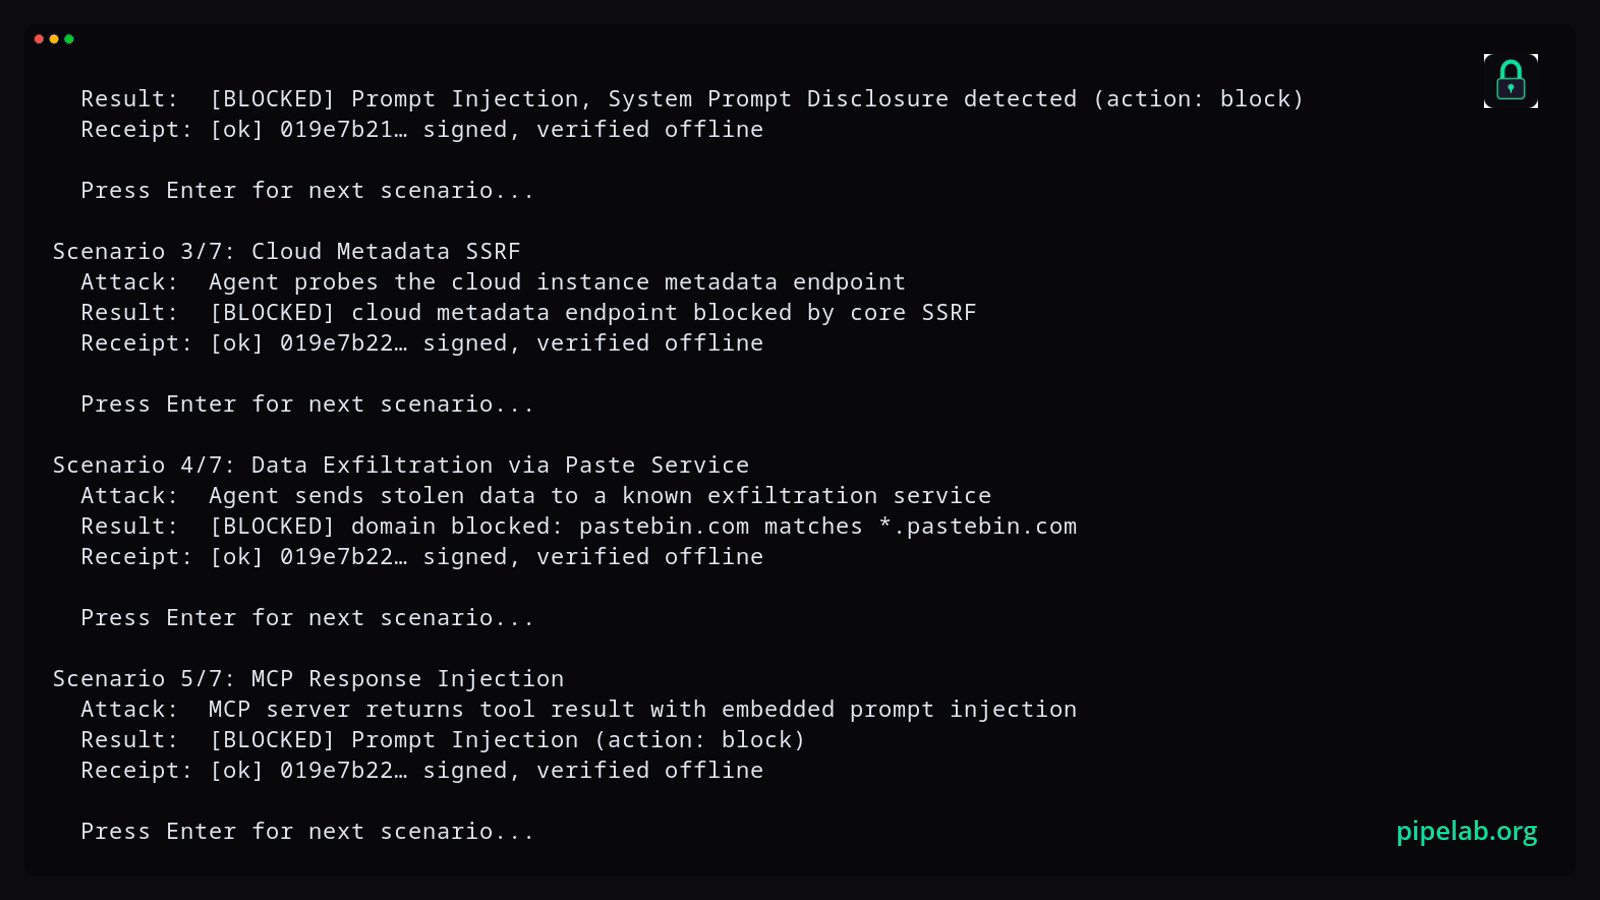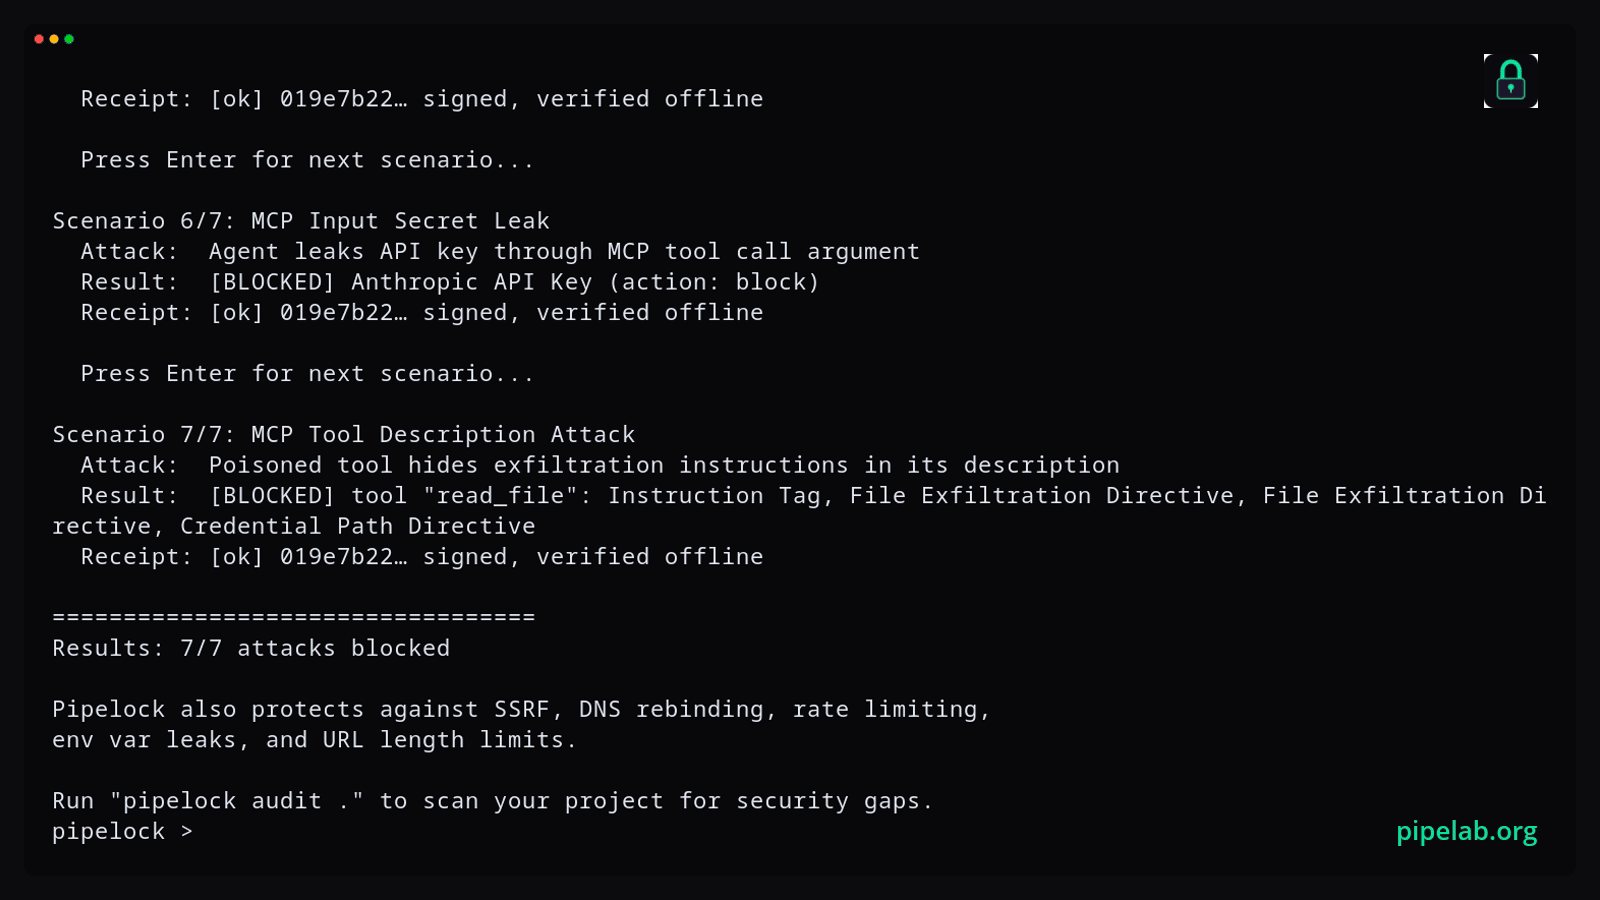 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
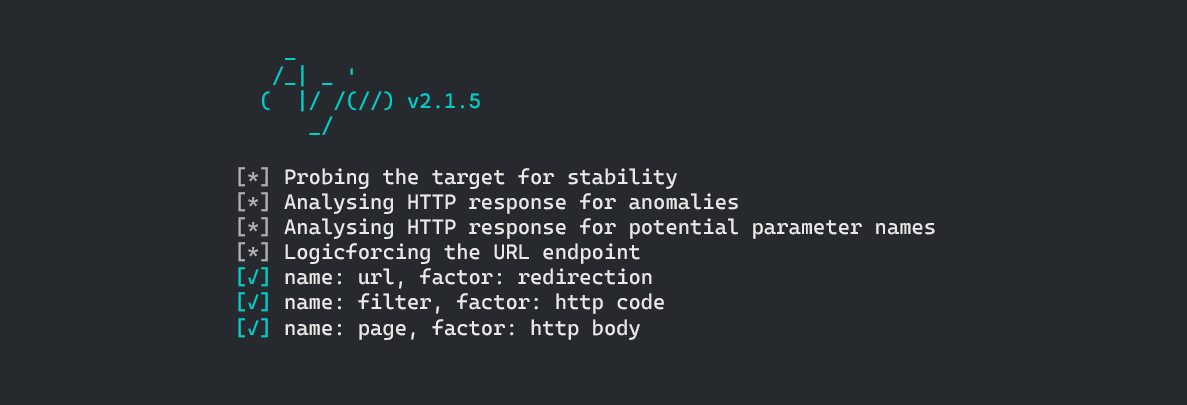 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 vikasudasi/exfil-scan
Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…

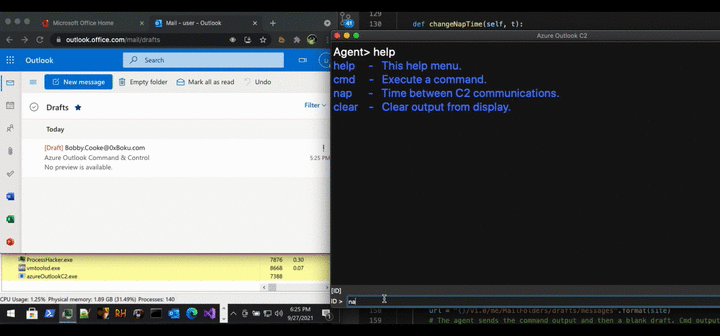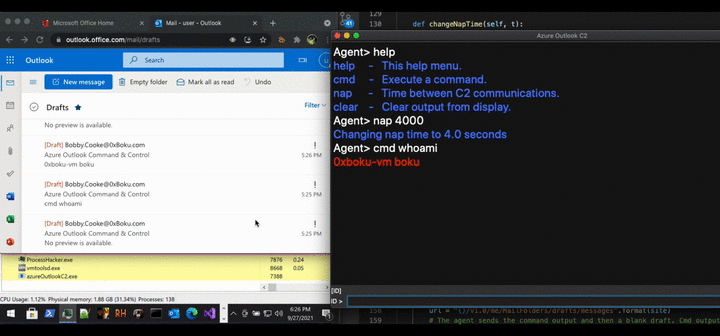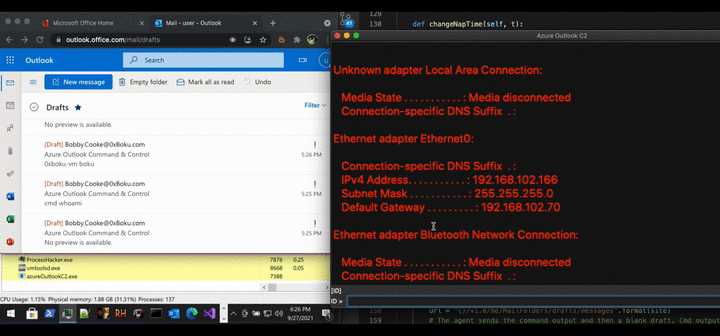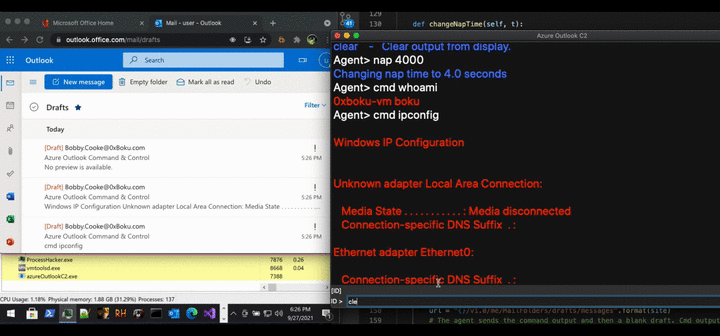 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 owasp/threat-dragon
An open source threat modeling tool from OWASP
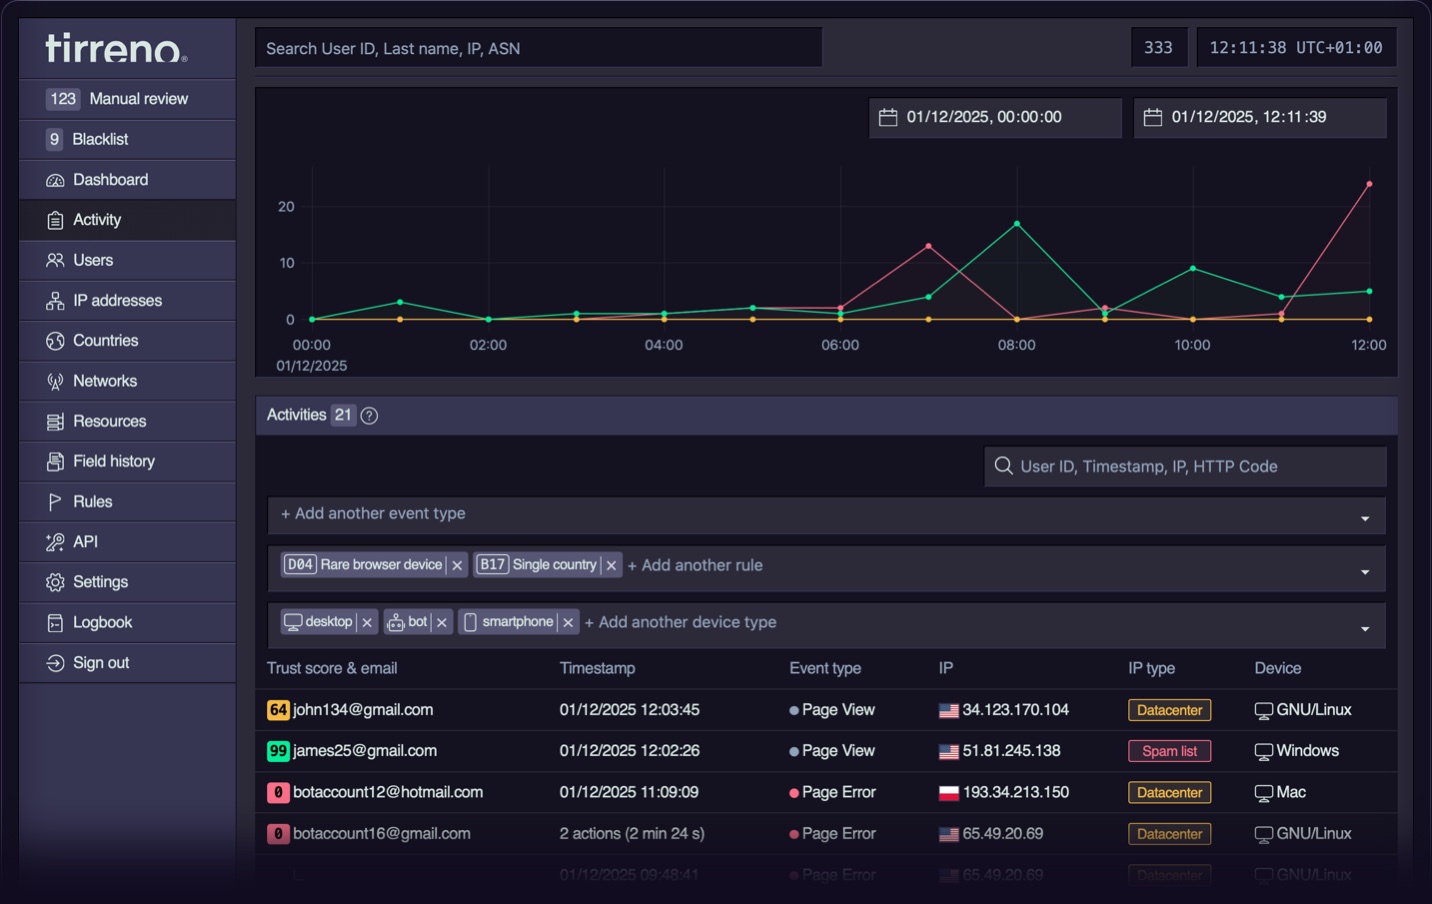 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
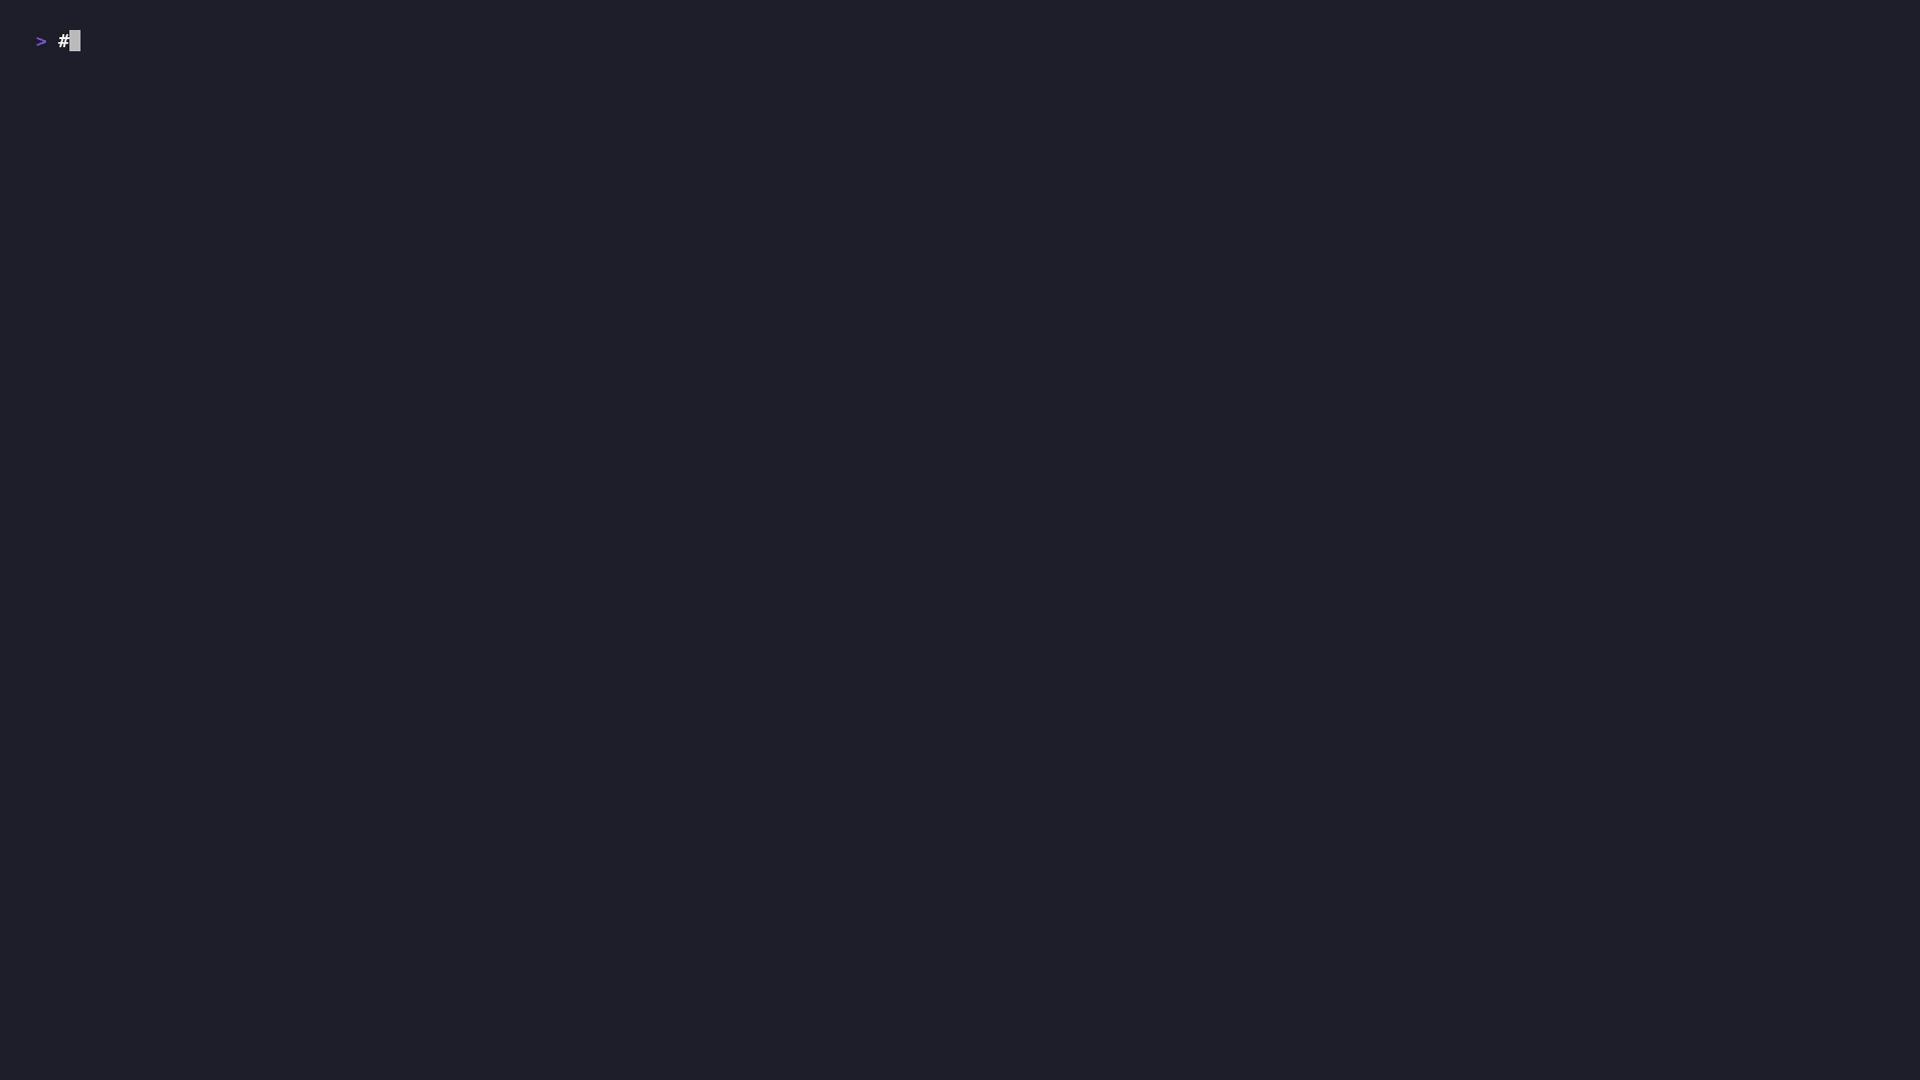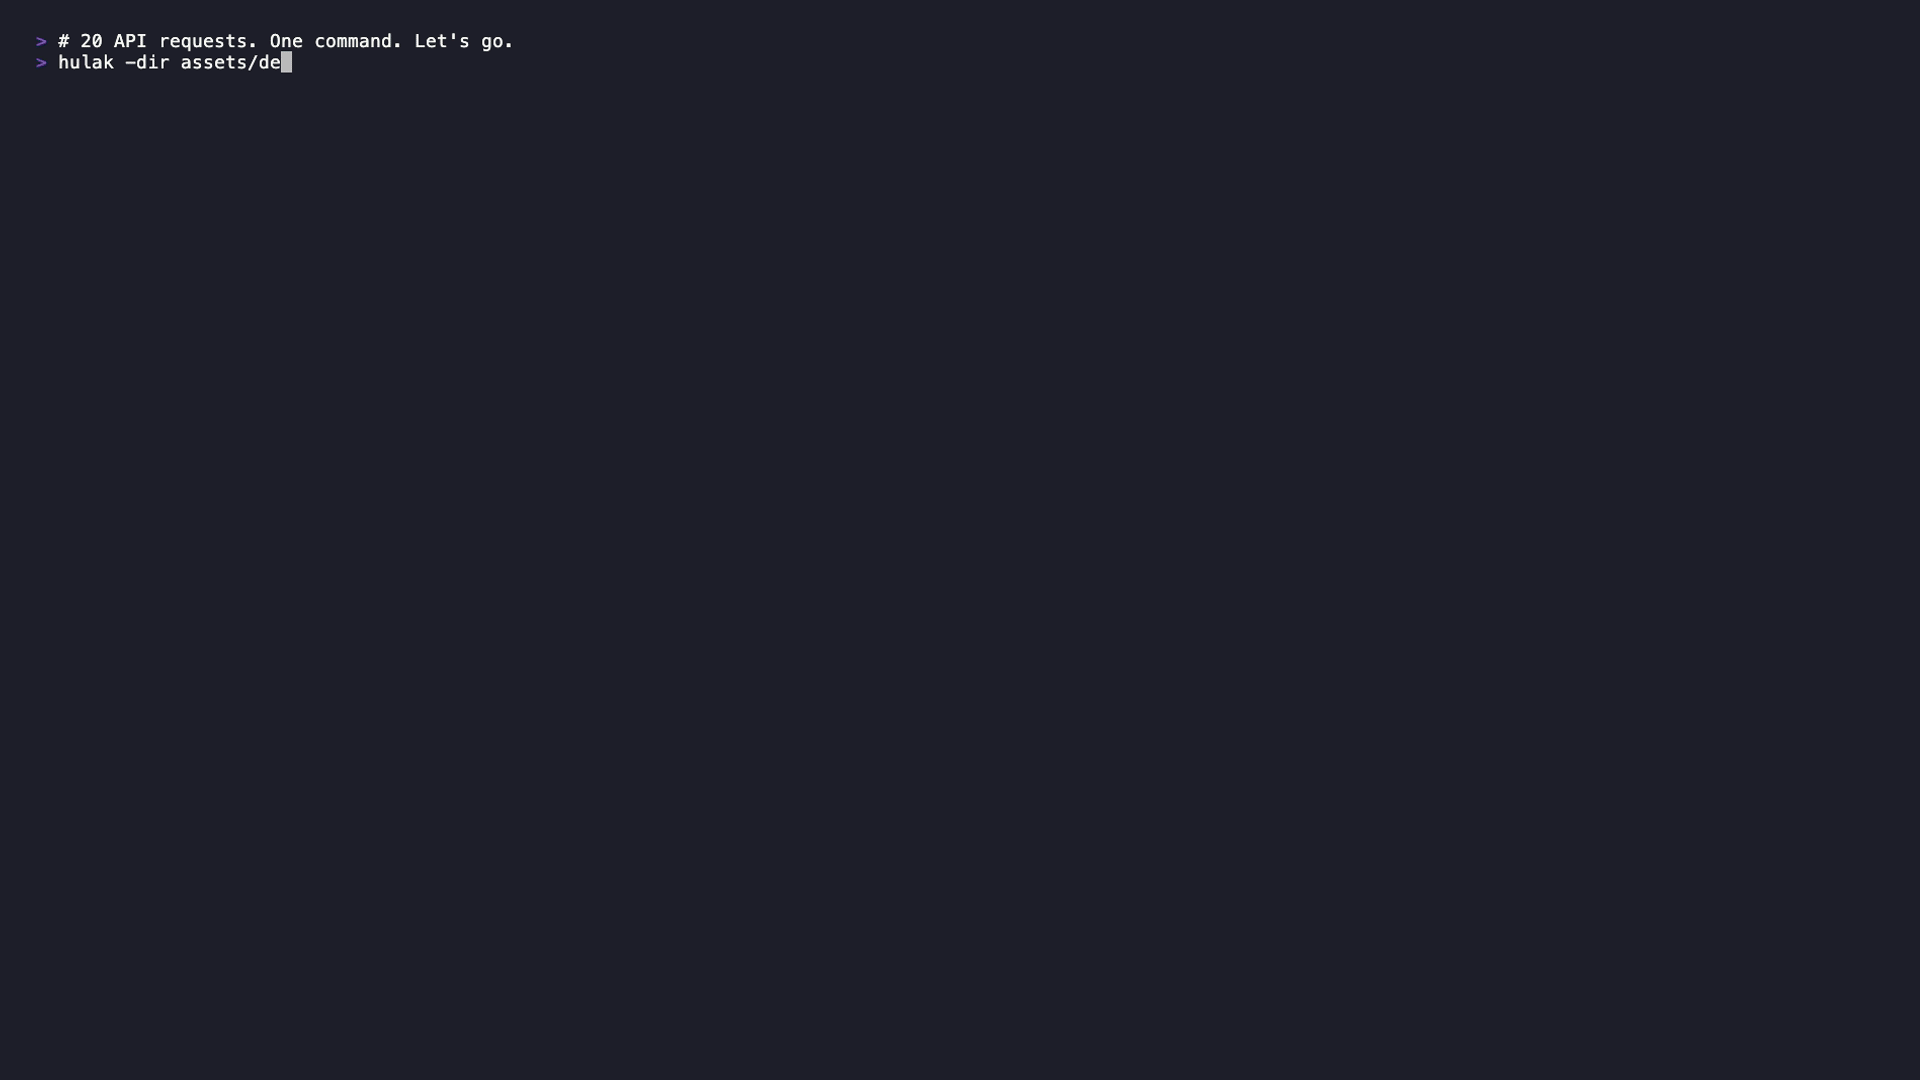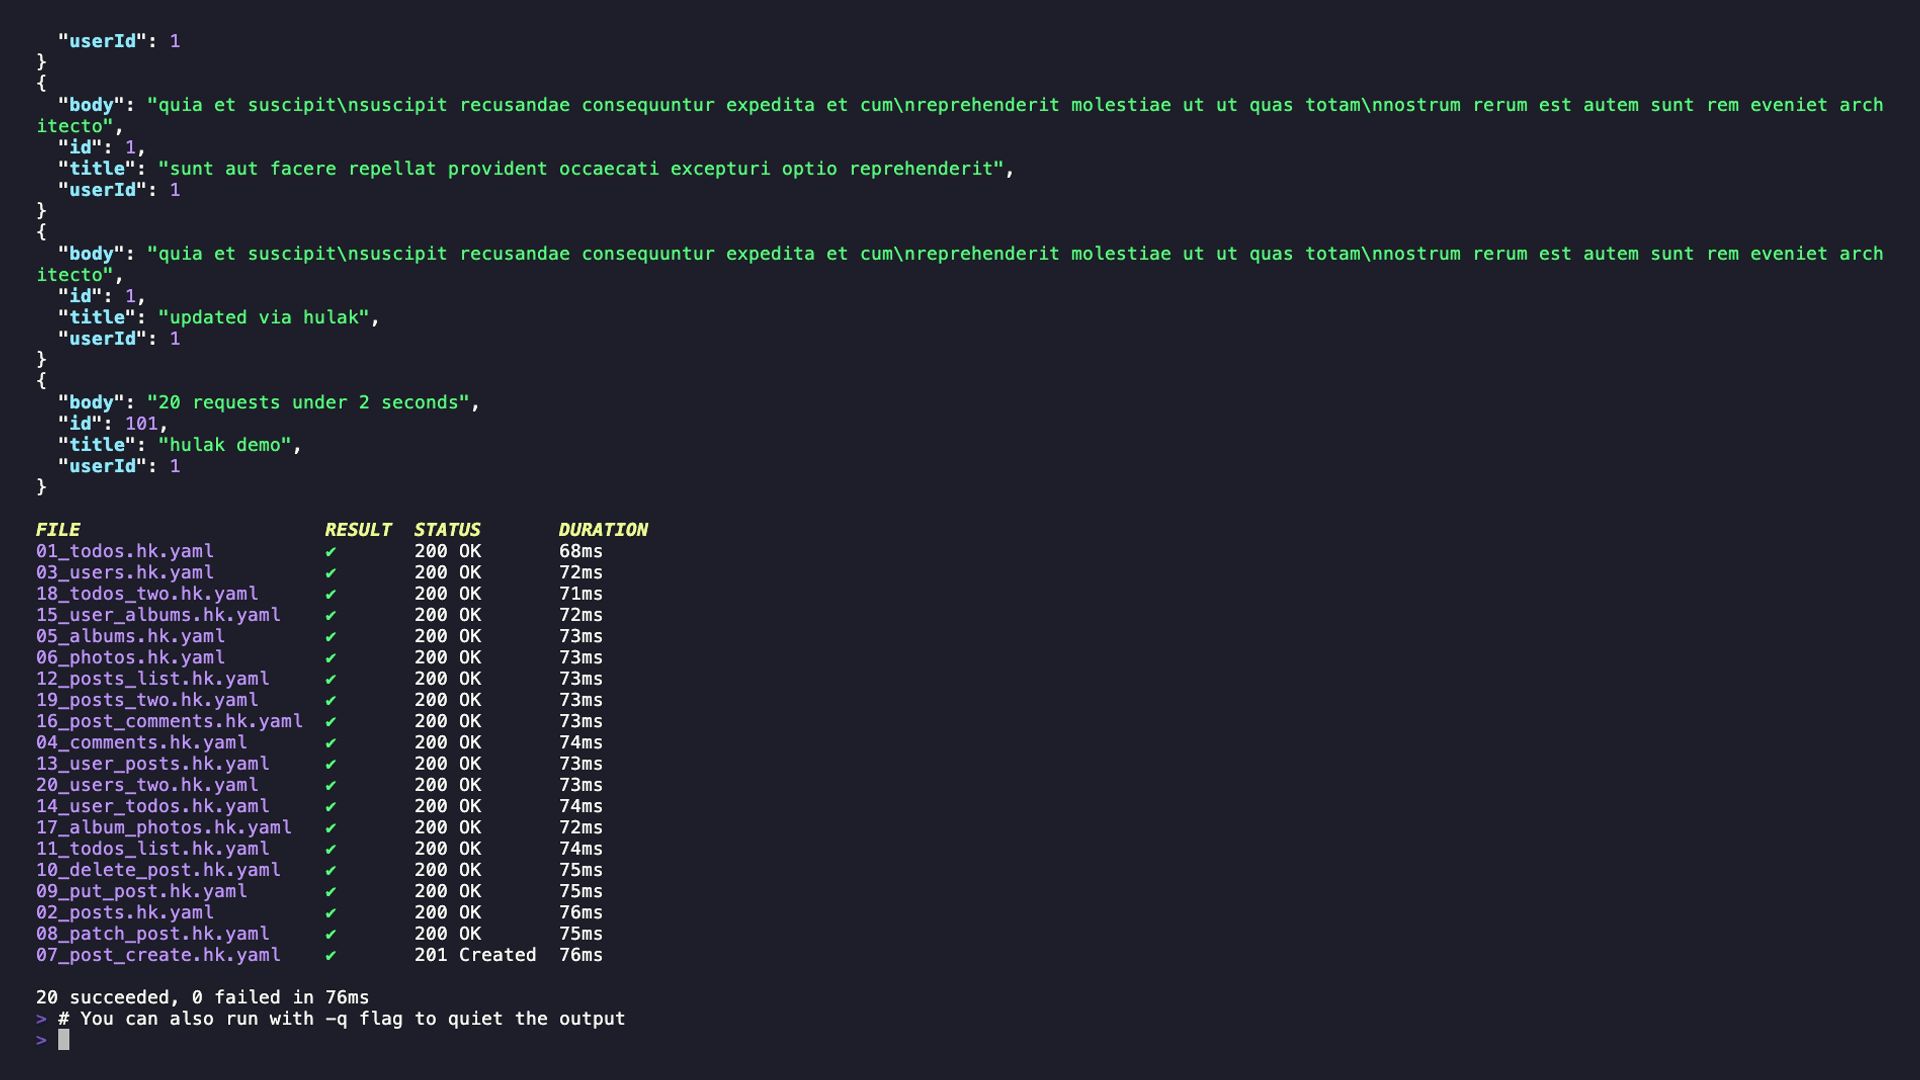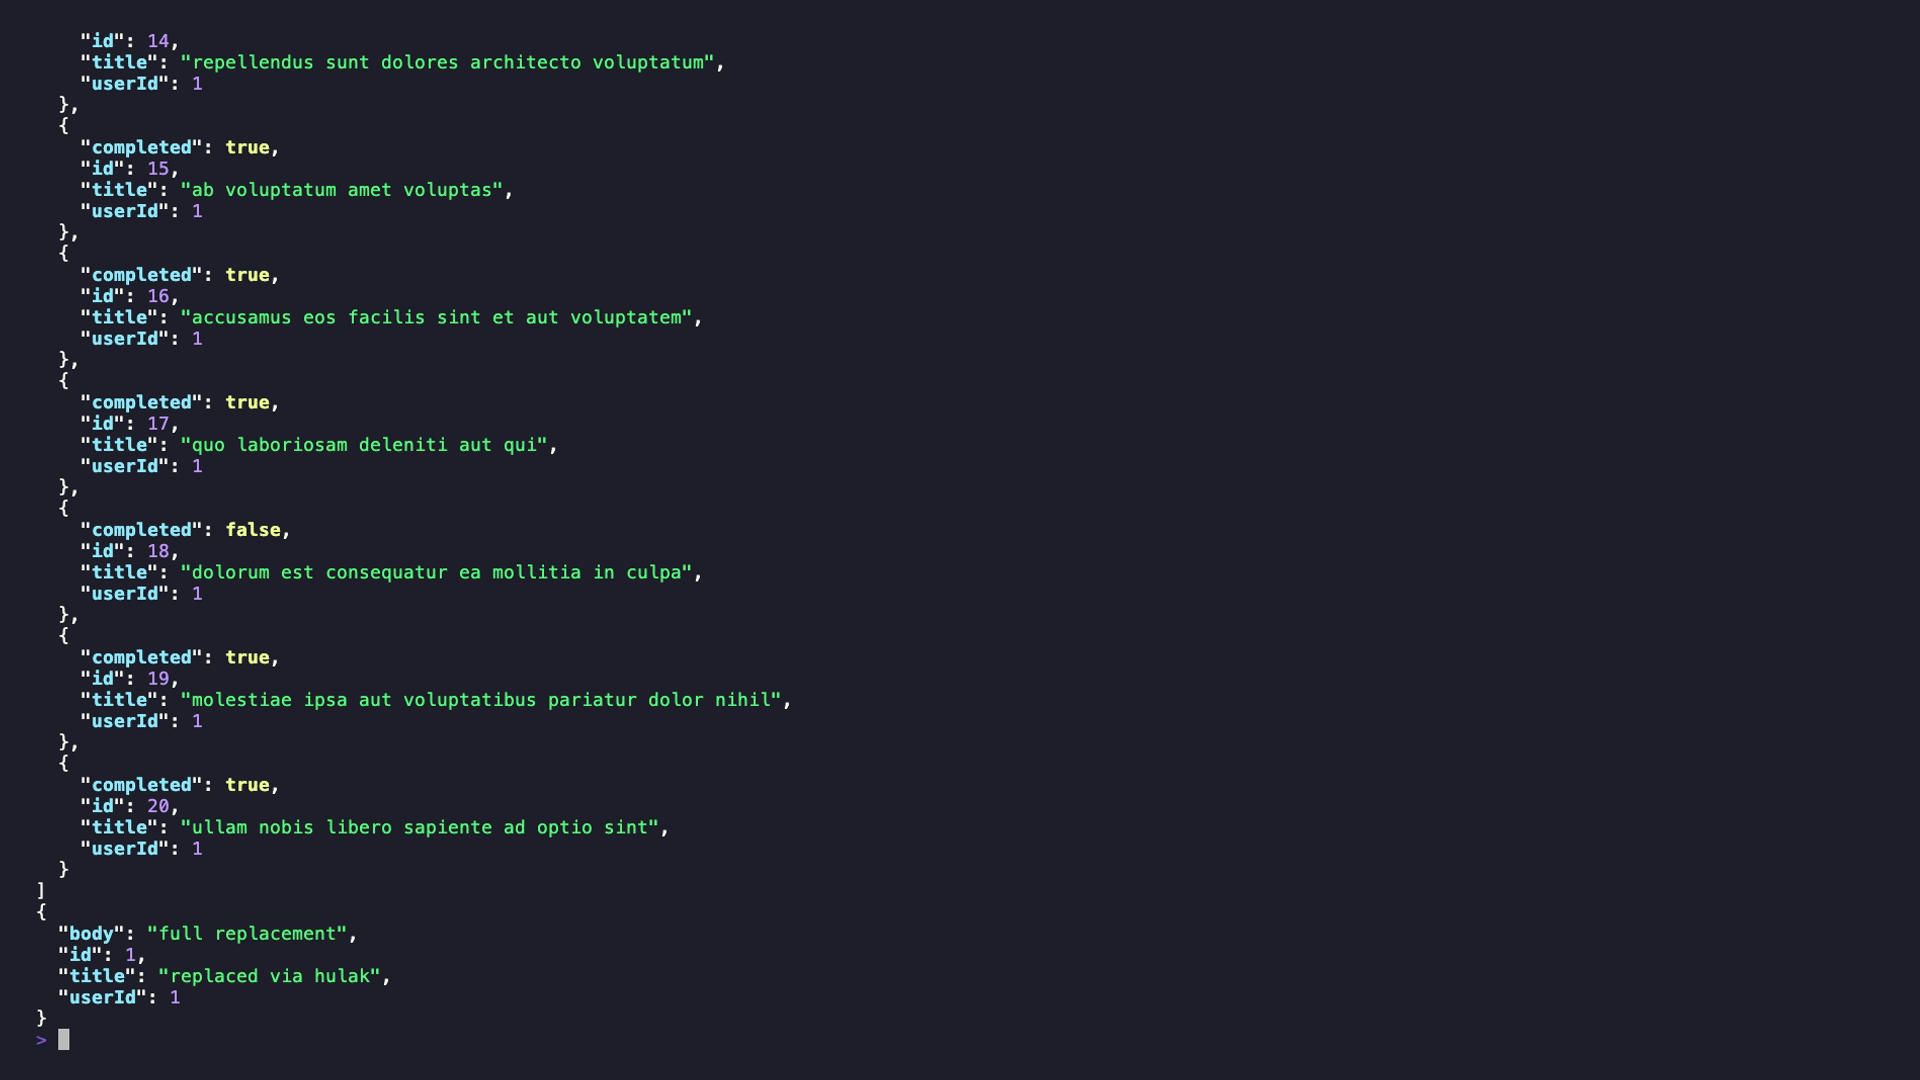 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 matrix-org/synapse
Synapse: Matrix homeserver written in Python/Twisted.
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…