
llm-agent-testbed
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
ai-securityapi-securityeducation+4
16
pie-script/llm-agent-testbedAn empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 bytesizedmarius/rewerse-engineering
Rewe API reverse engineering in Go
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
 leekanghyun/axios-security-guide
Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석
 filipegaudard/cve-2026-30945-poc
Proof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 shoucheng3/hapifhir__org_hl7_fhir_core_cve-2023-28465_5-6-1055
Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
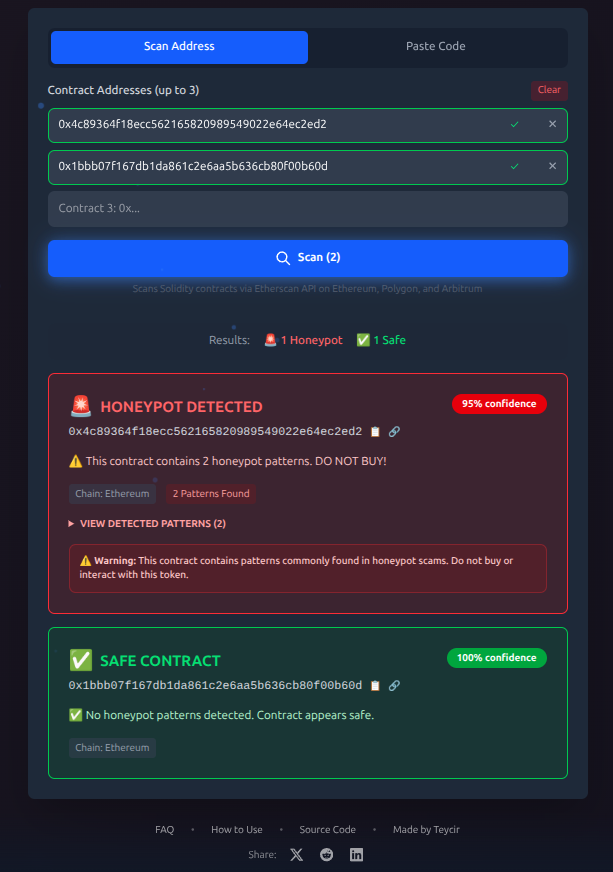 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 karlemilnikka/cve-2024-1208-and-cve-2024-1210
Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
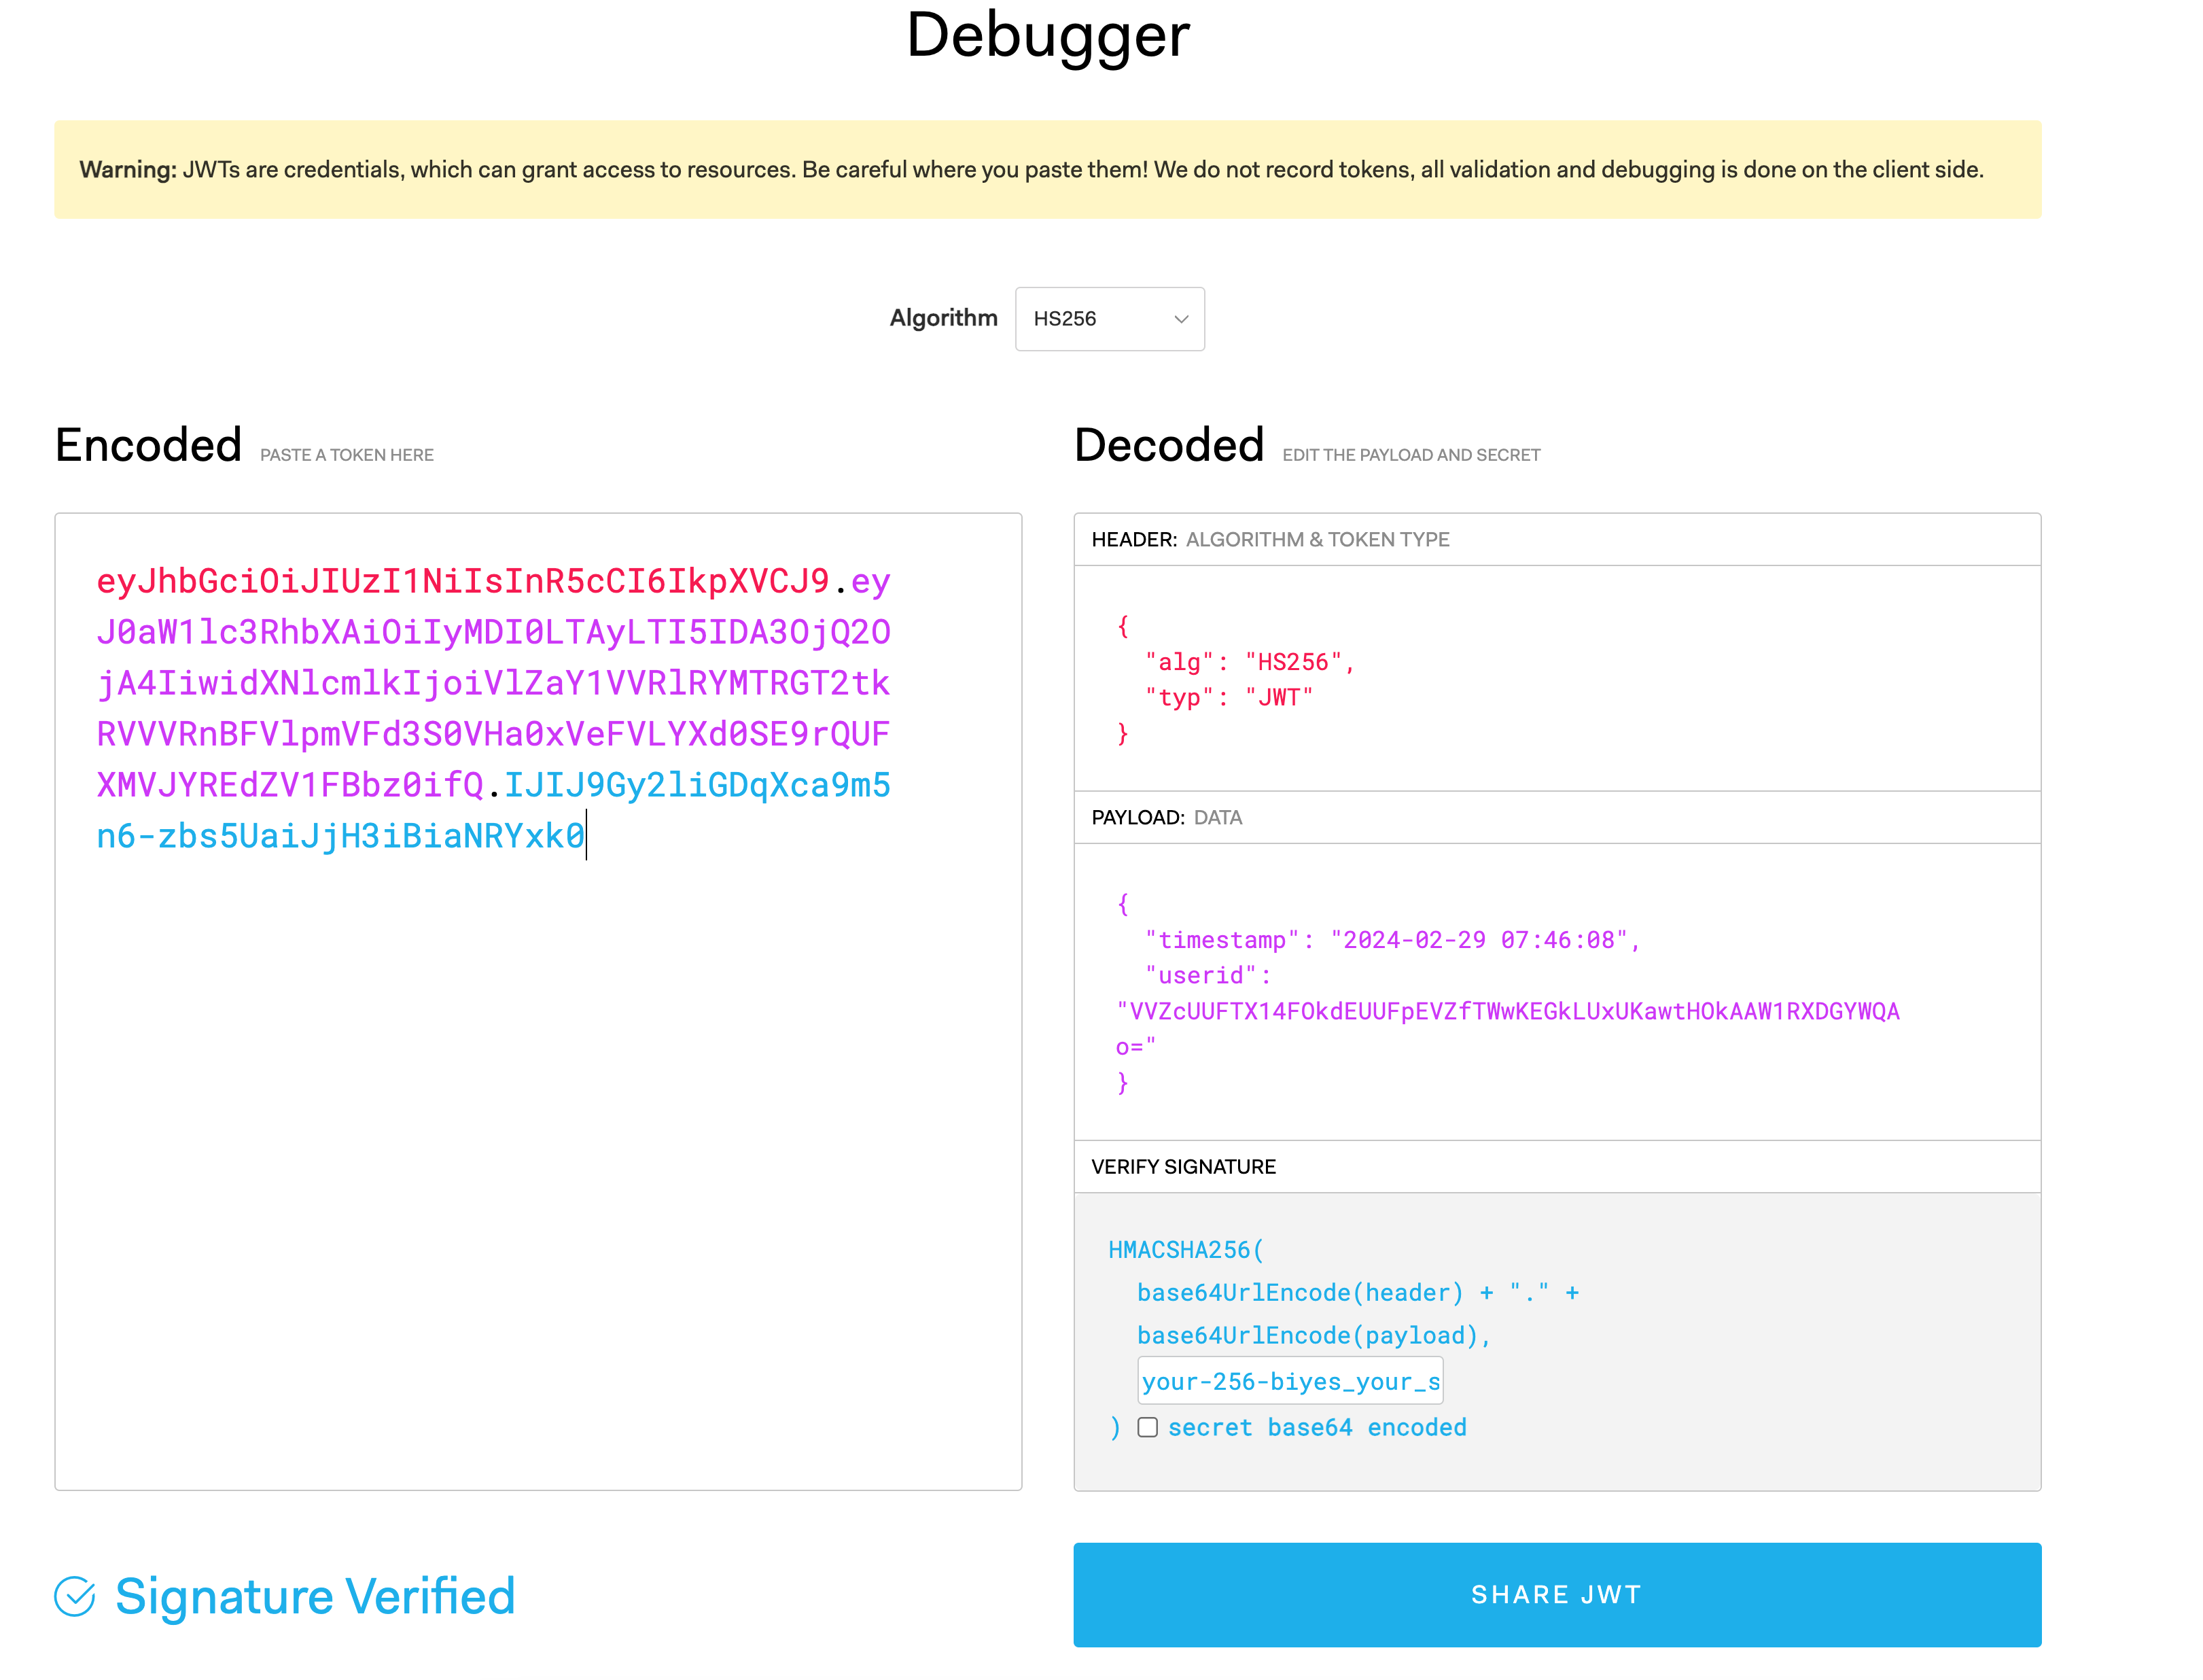 password123456/some-tweak-to-hide-jwt-payload-values
Lightweight Python library for obfuscating JWT payload values using XOR encryption with timestamp-based keys, preventing plaintext decoding of…
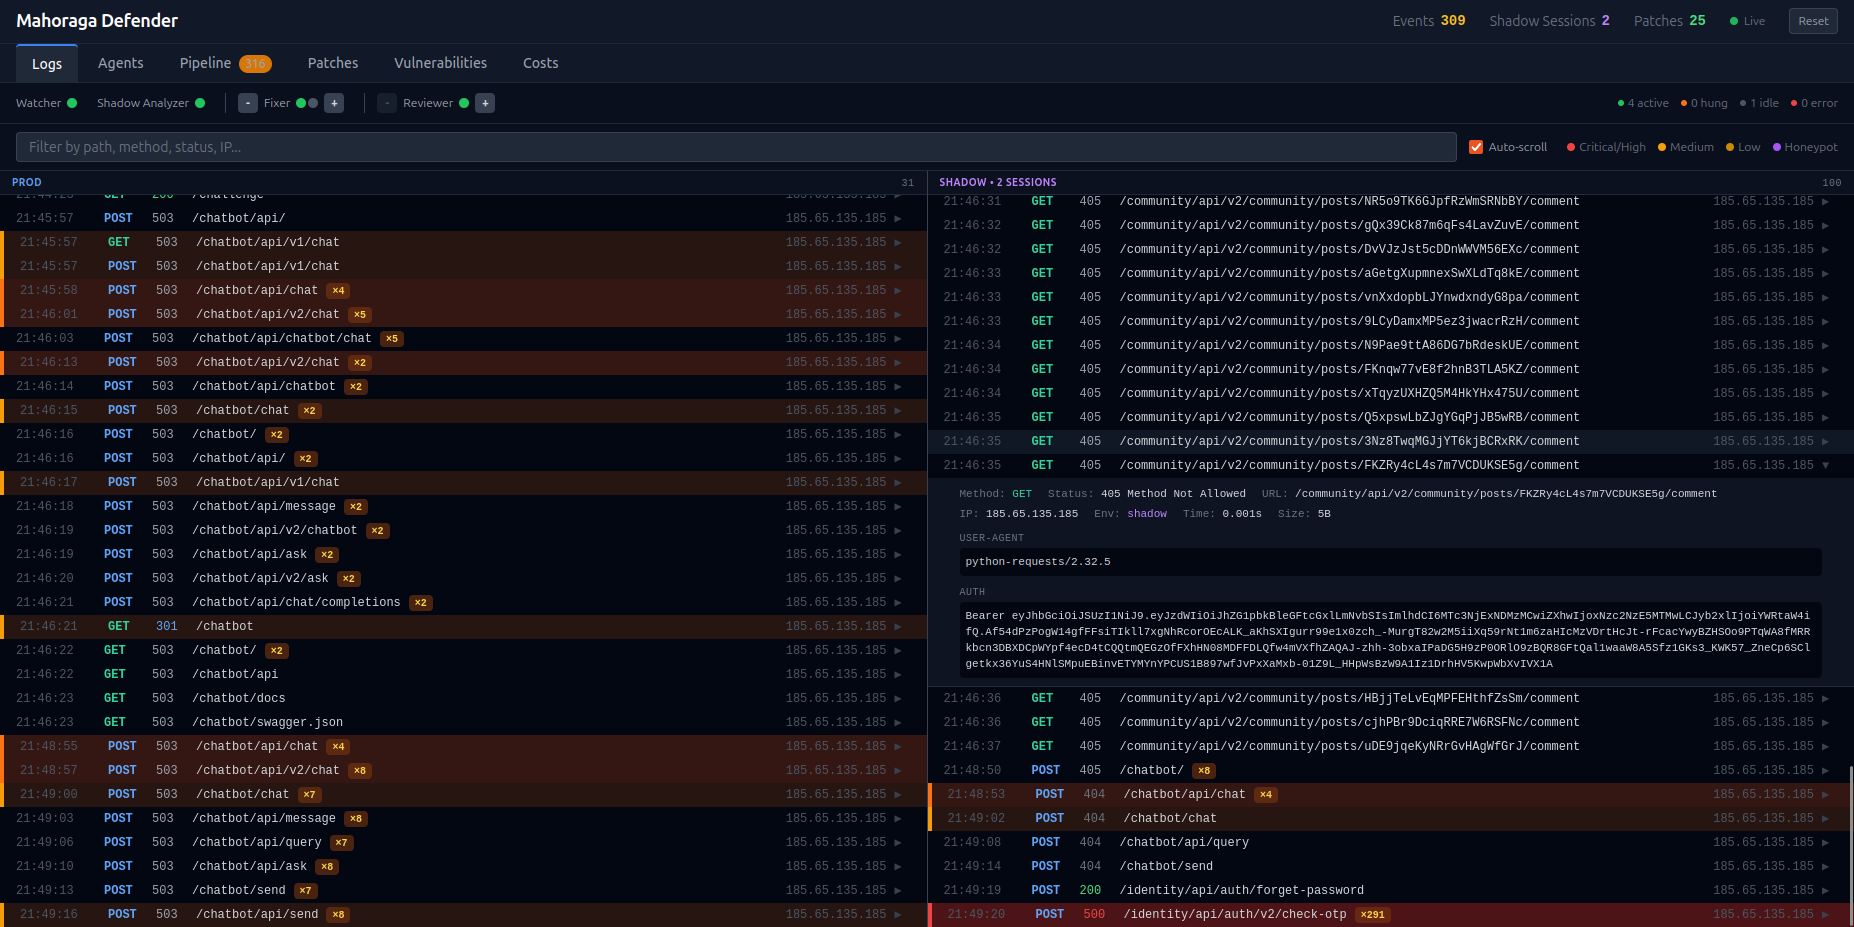 ageofalgorithms/mahoraga-webapp-defender
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.