

CheatSheetSeries
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
api-securityauthenticationcloud-security+6
33.2k
owasp/cheatsheetseriesThe OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
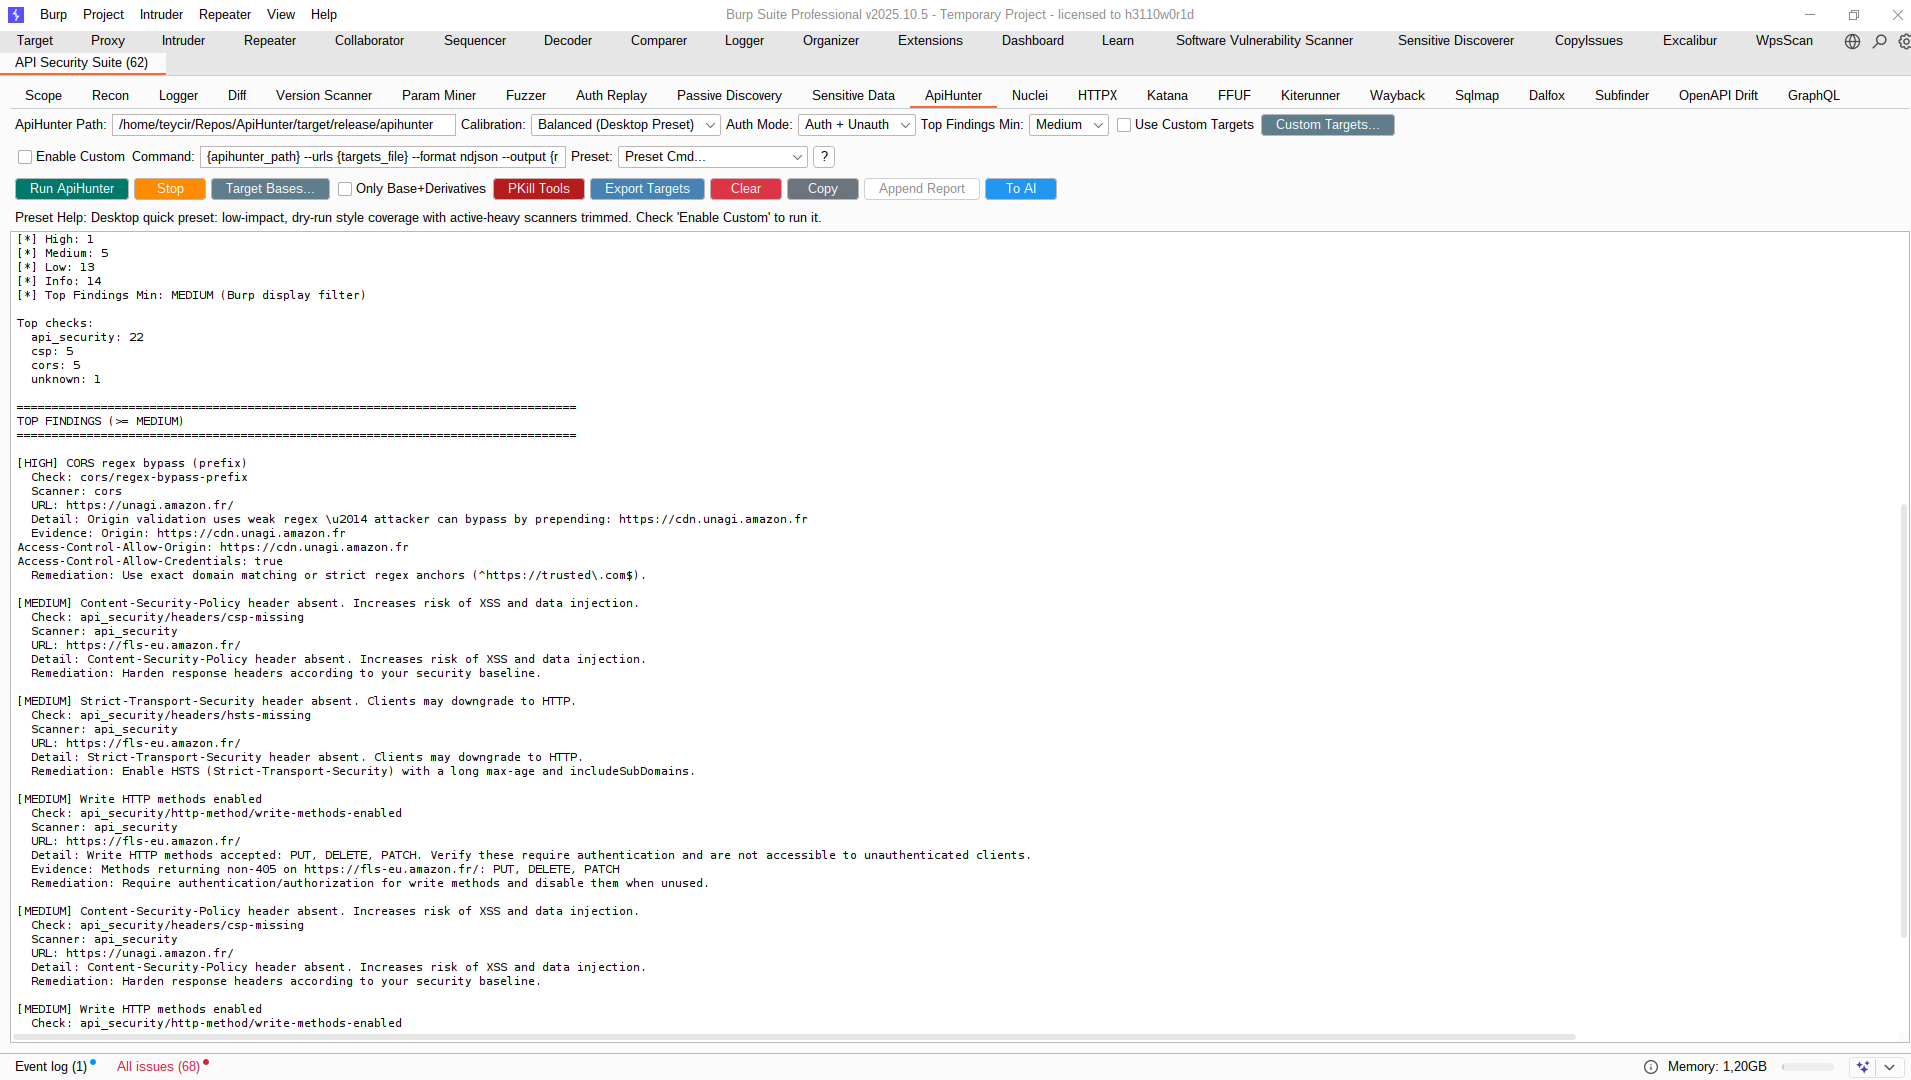 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 owasp/asvs
Application Security Verification Standard
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
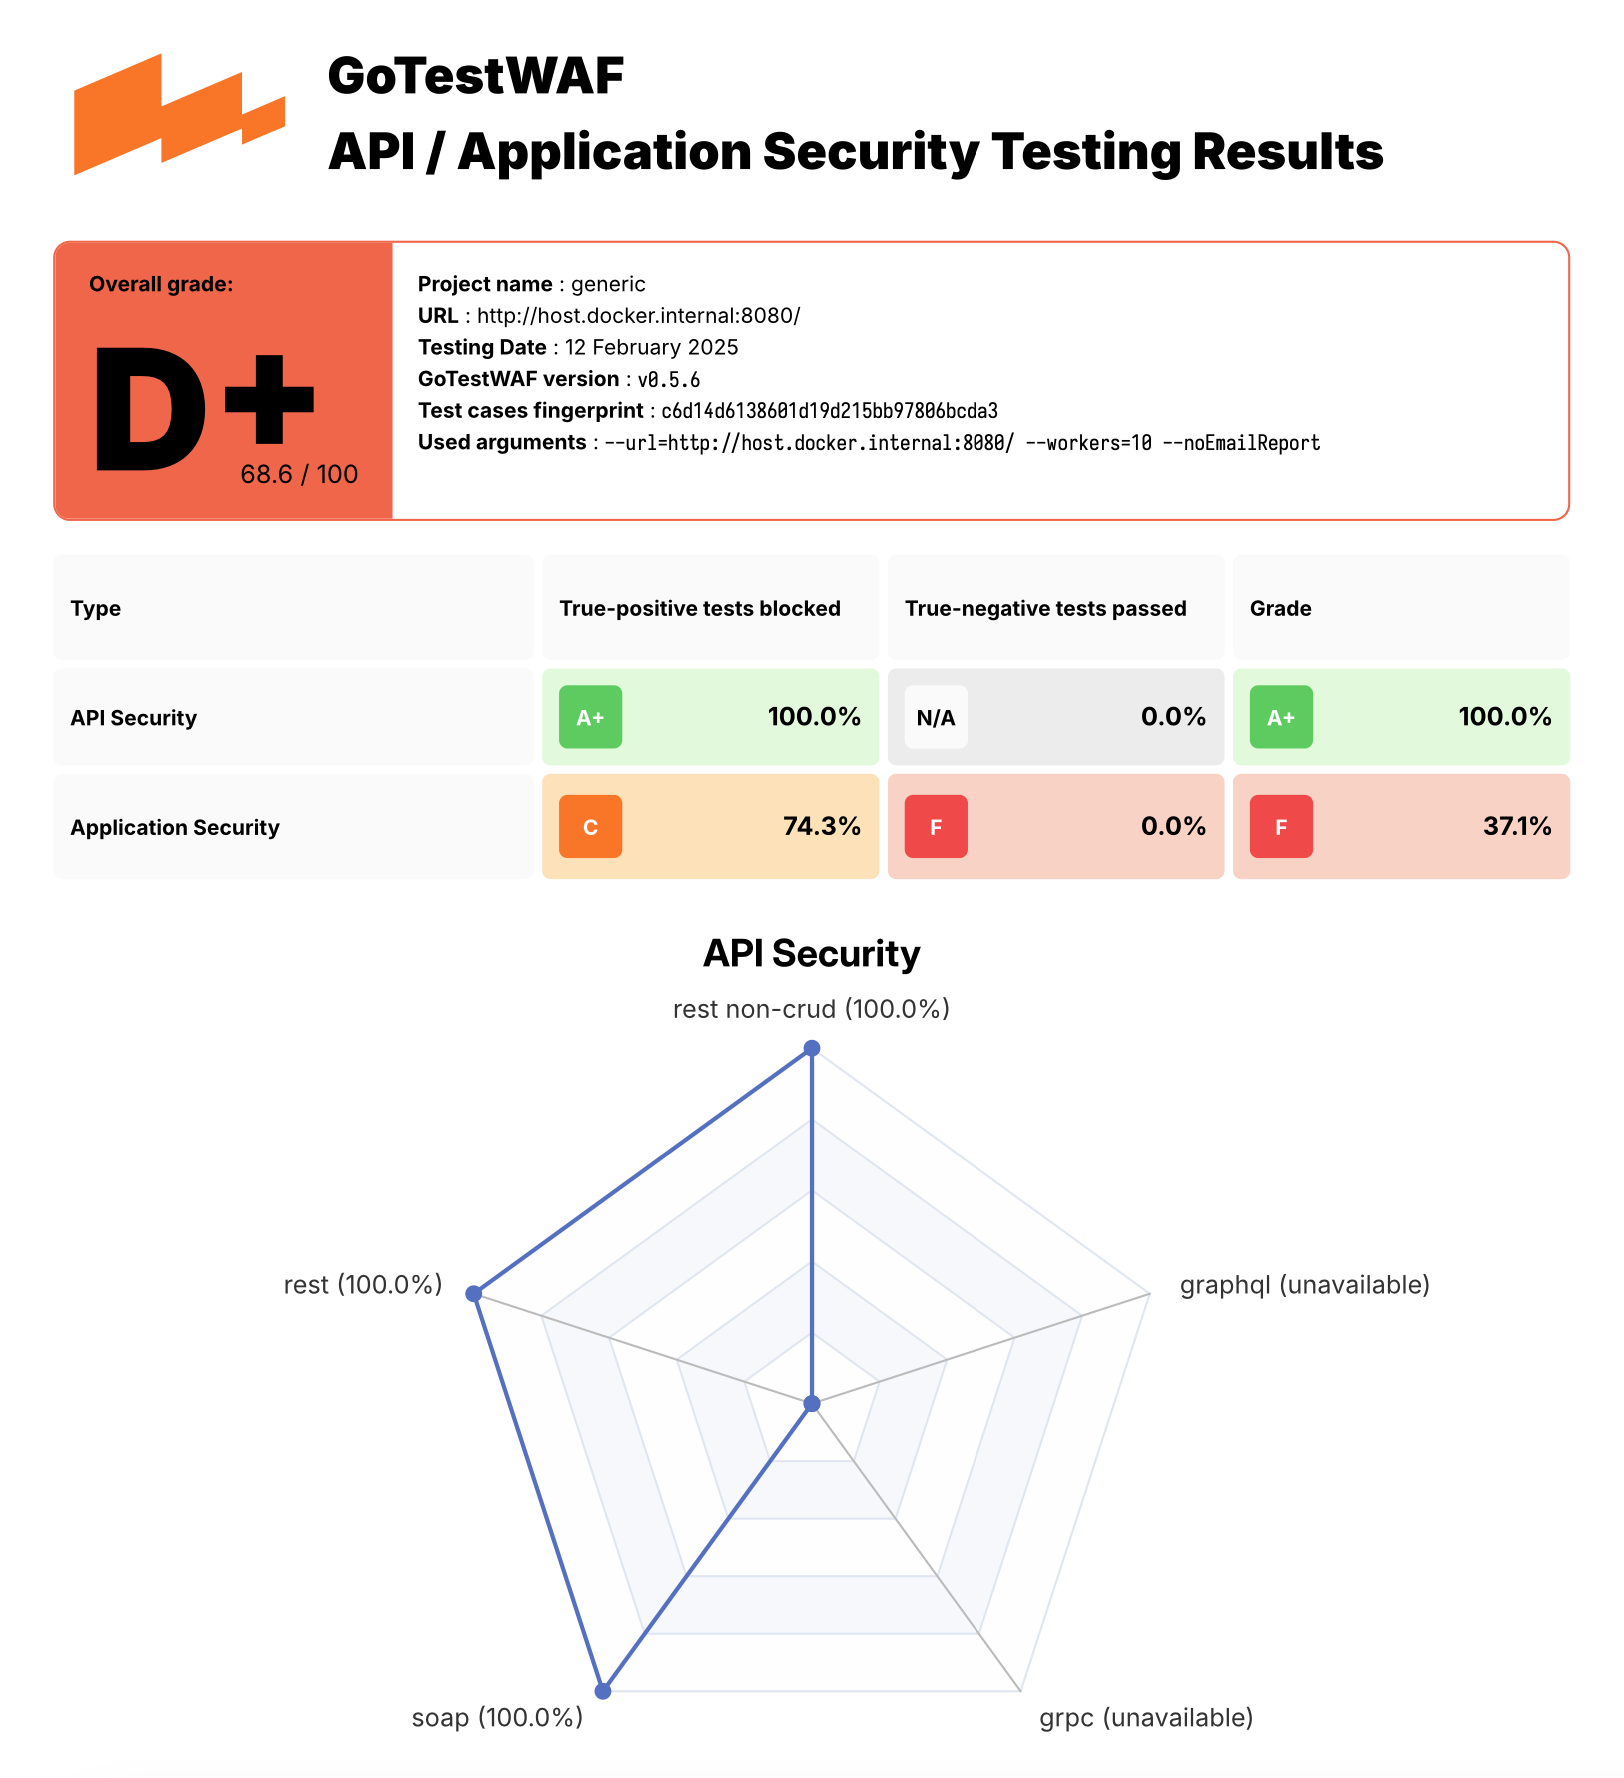 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
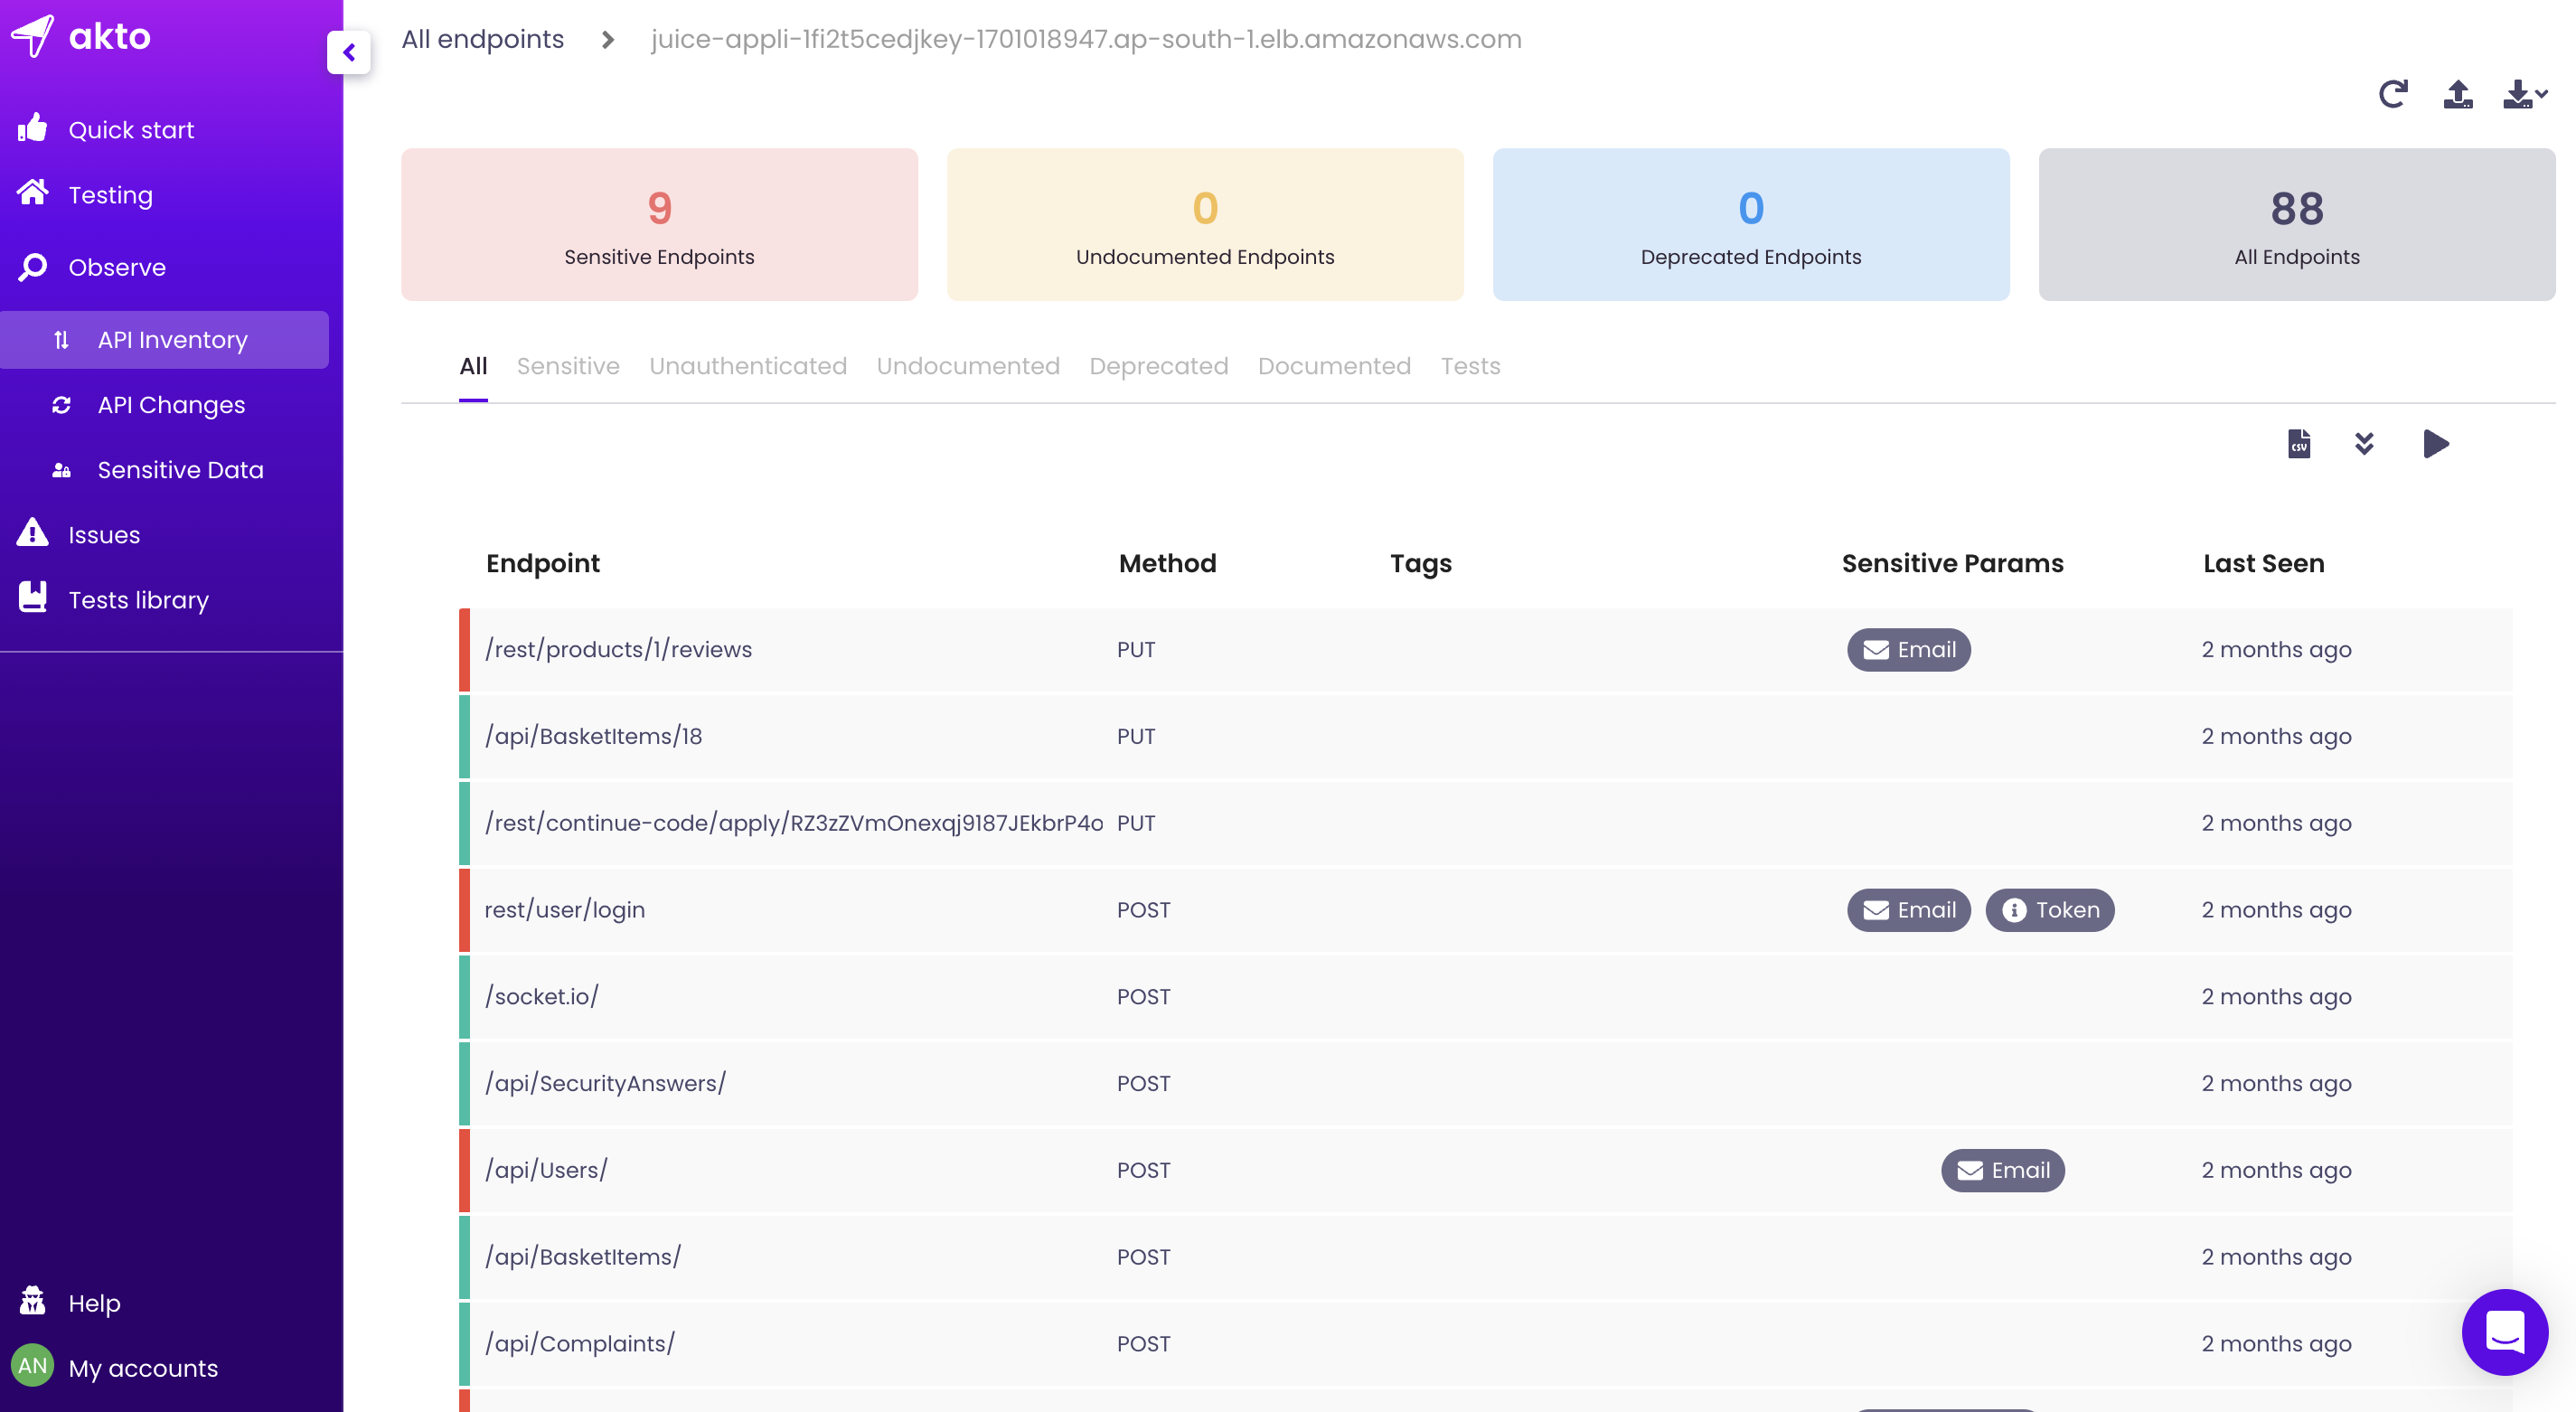 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
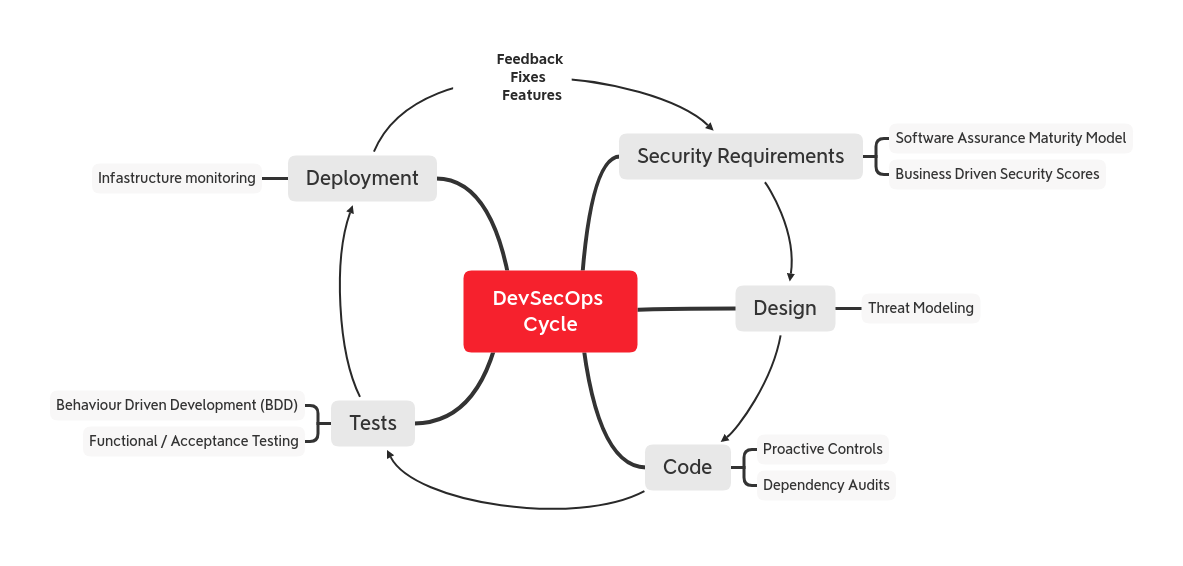 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.