

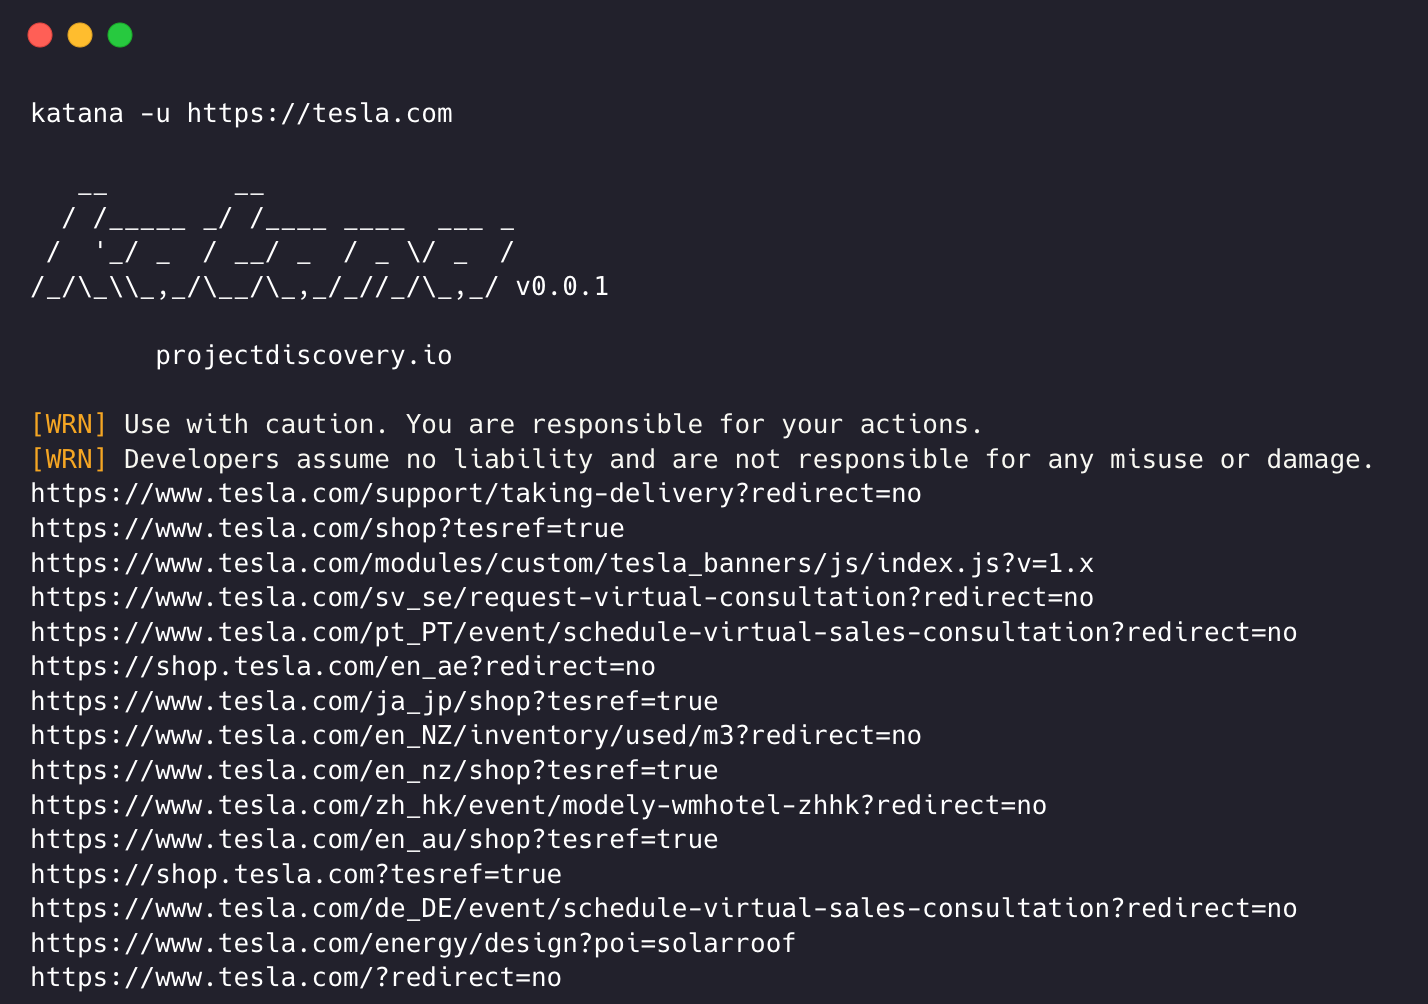
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 vulncheck-oss/cli
VulnCheck's official command line tool
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
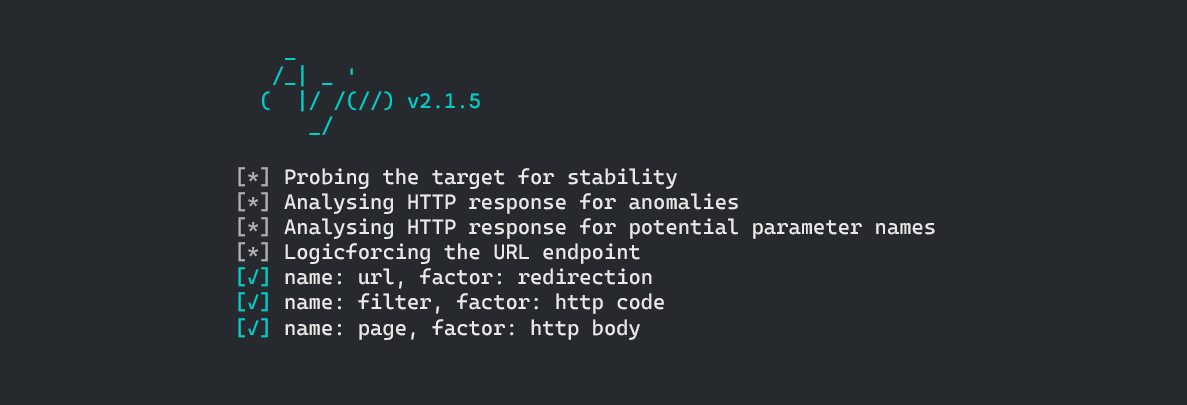 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 cipher387/api-s-for-osint
List of API's for gathering information about phone numbers, addresses, domains etc
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 elementalsouls/claude-bughunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…