
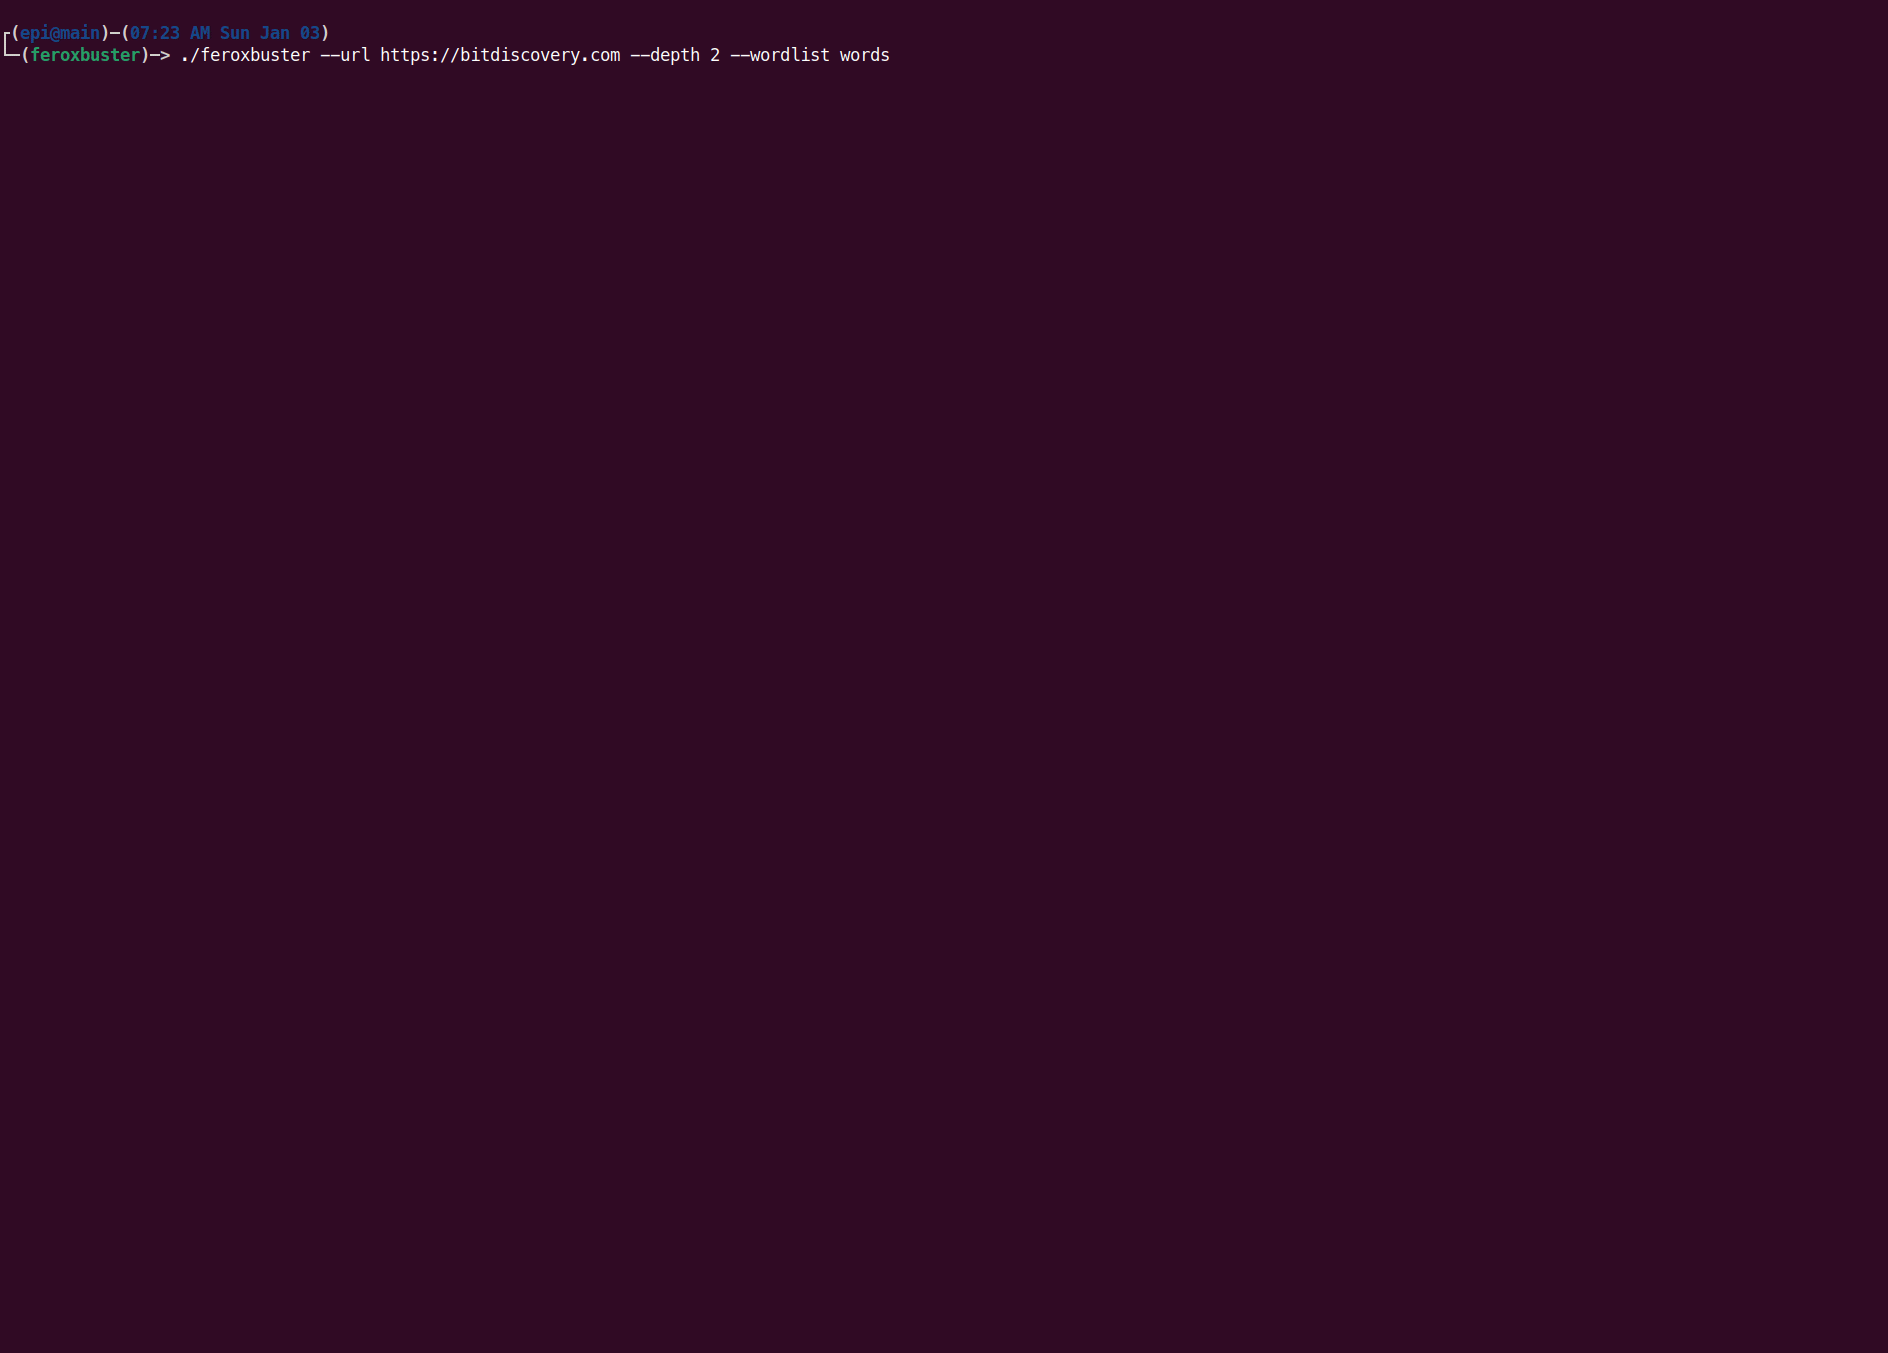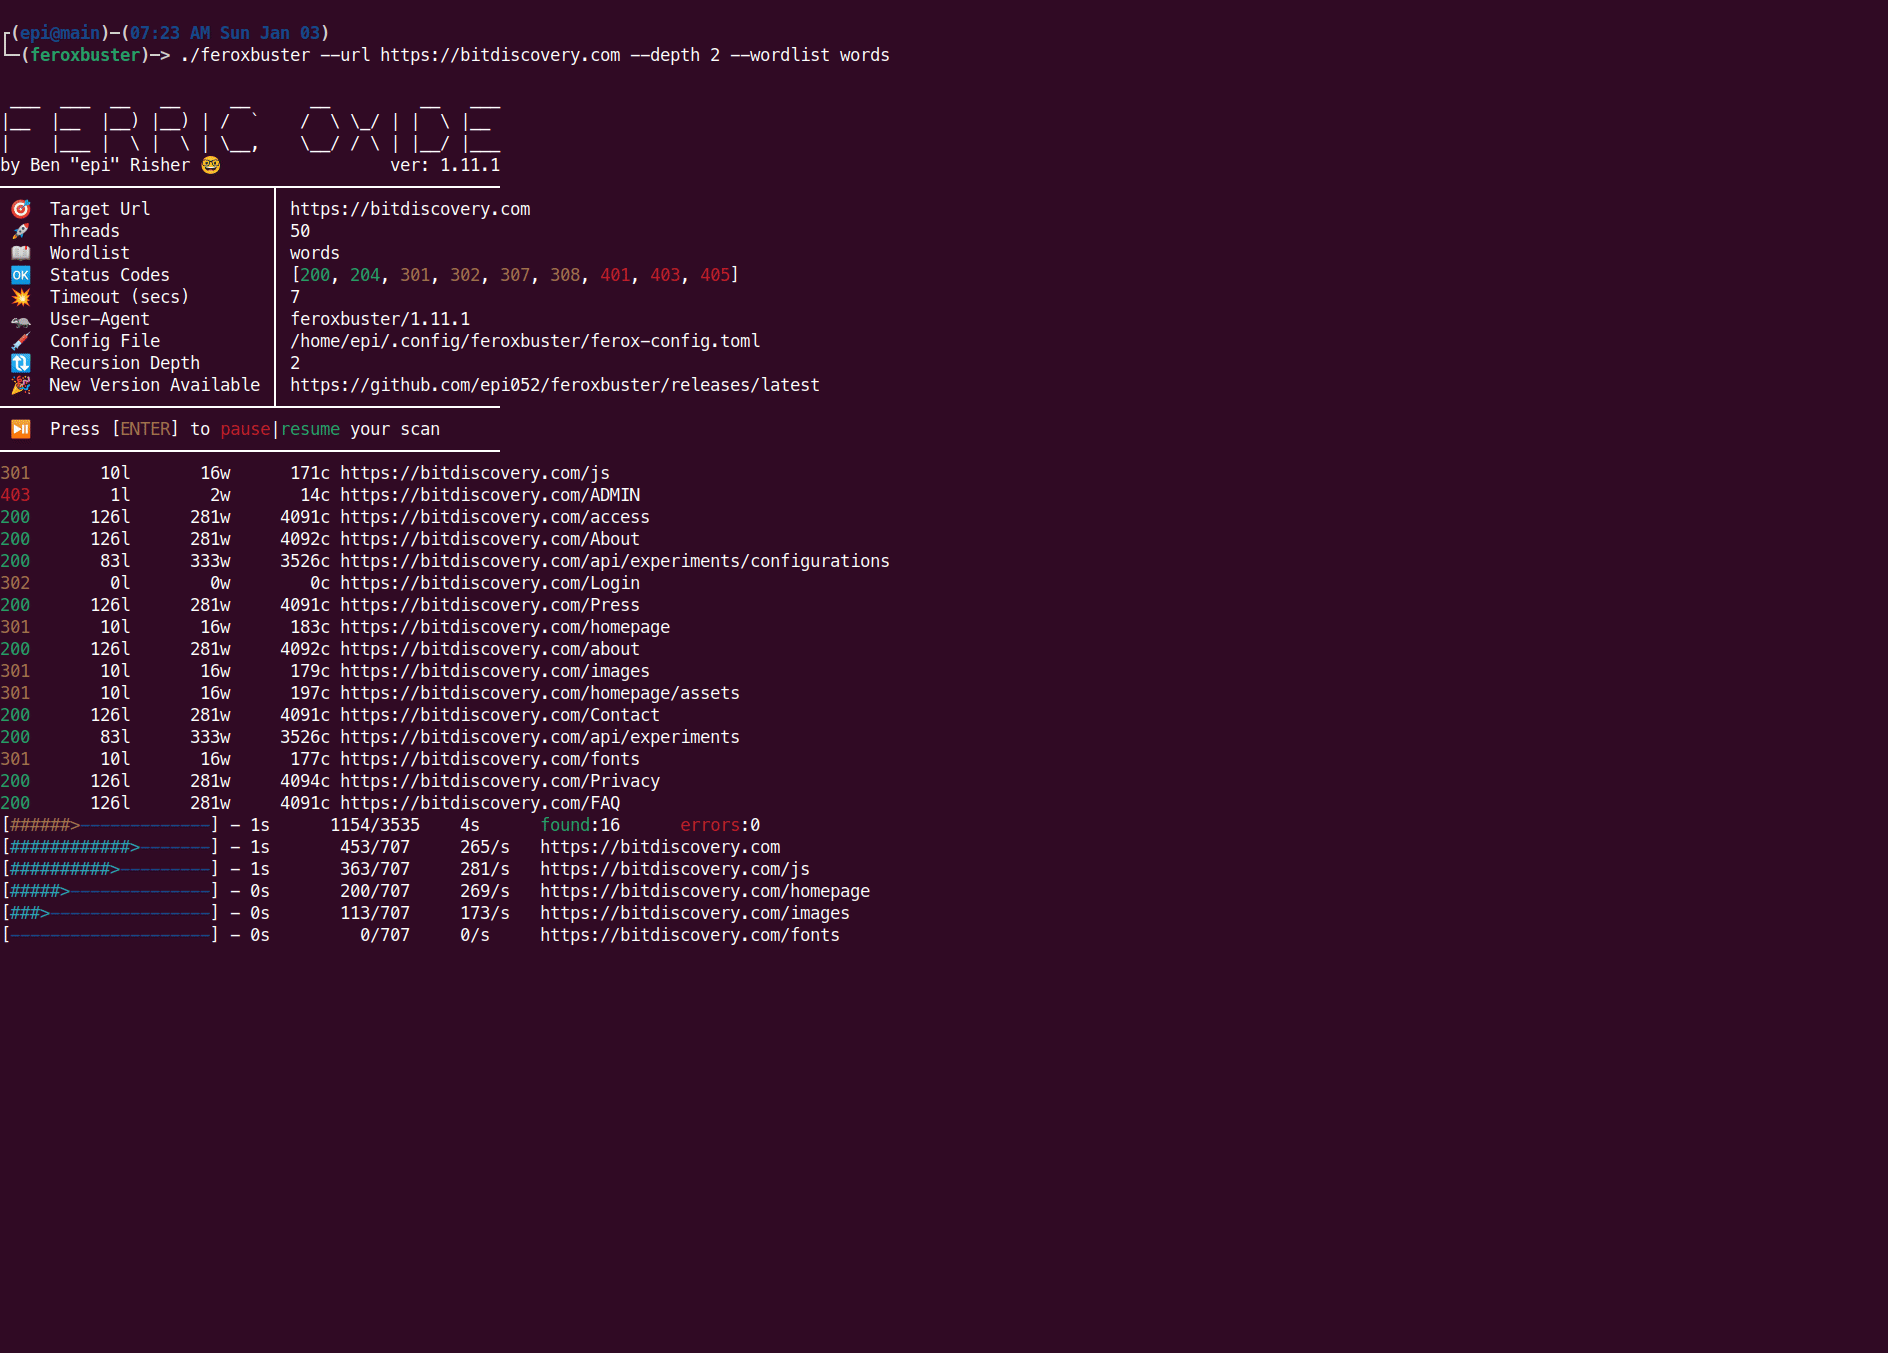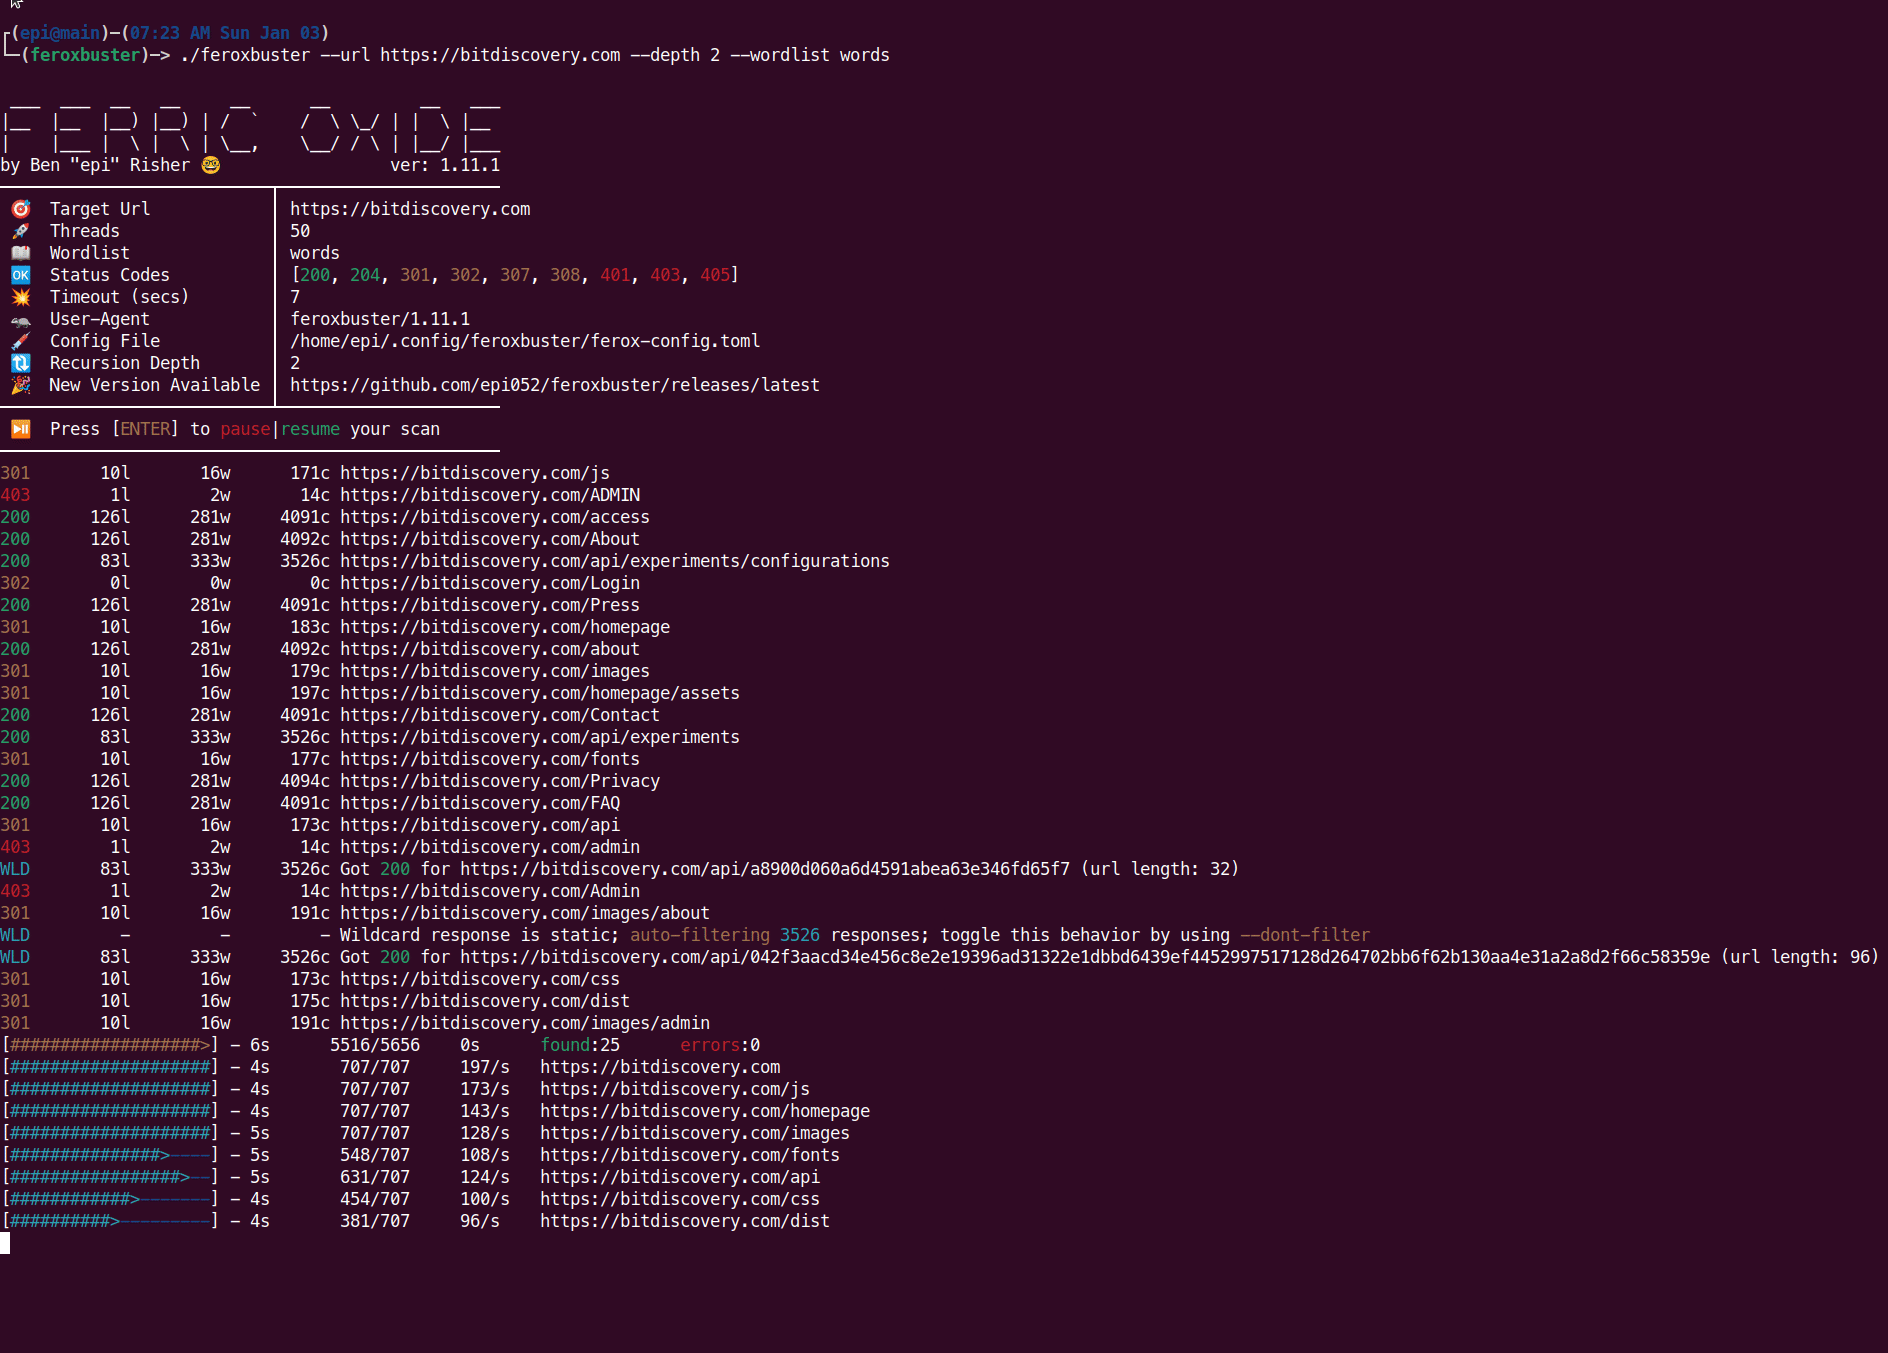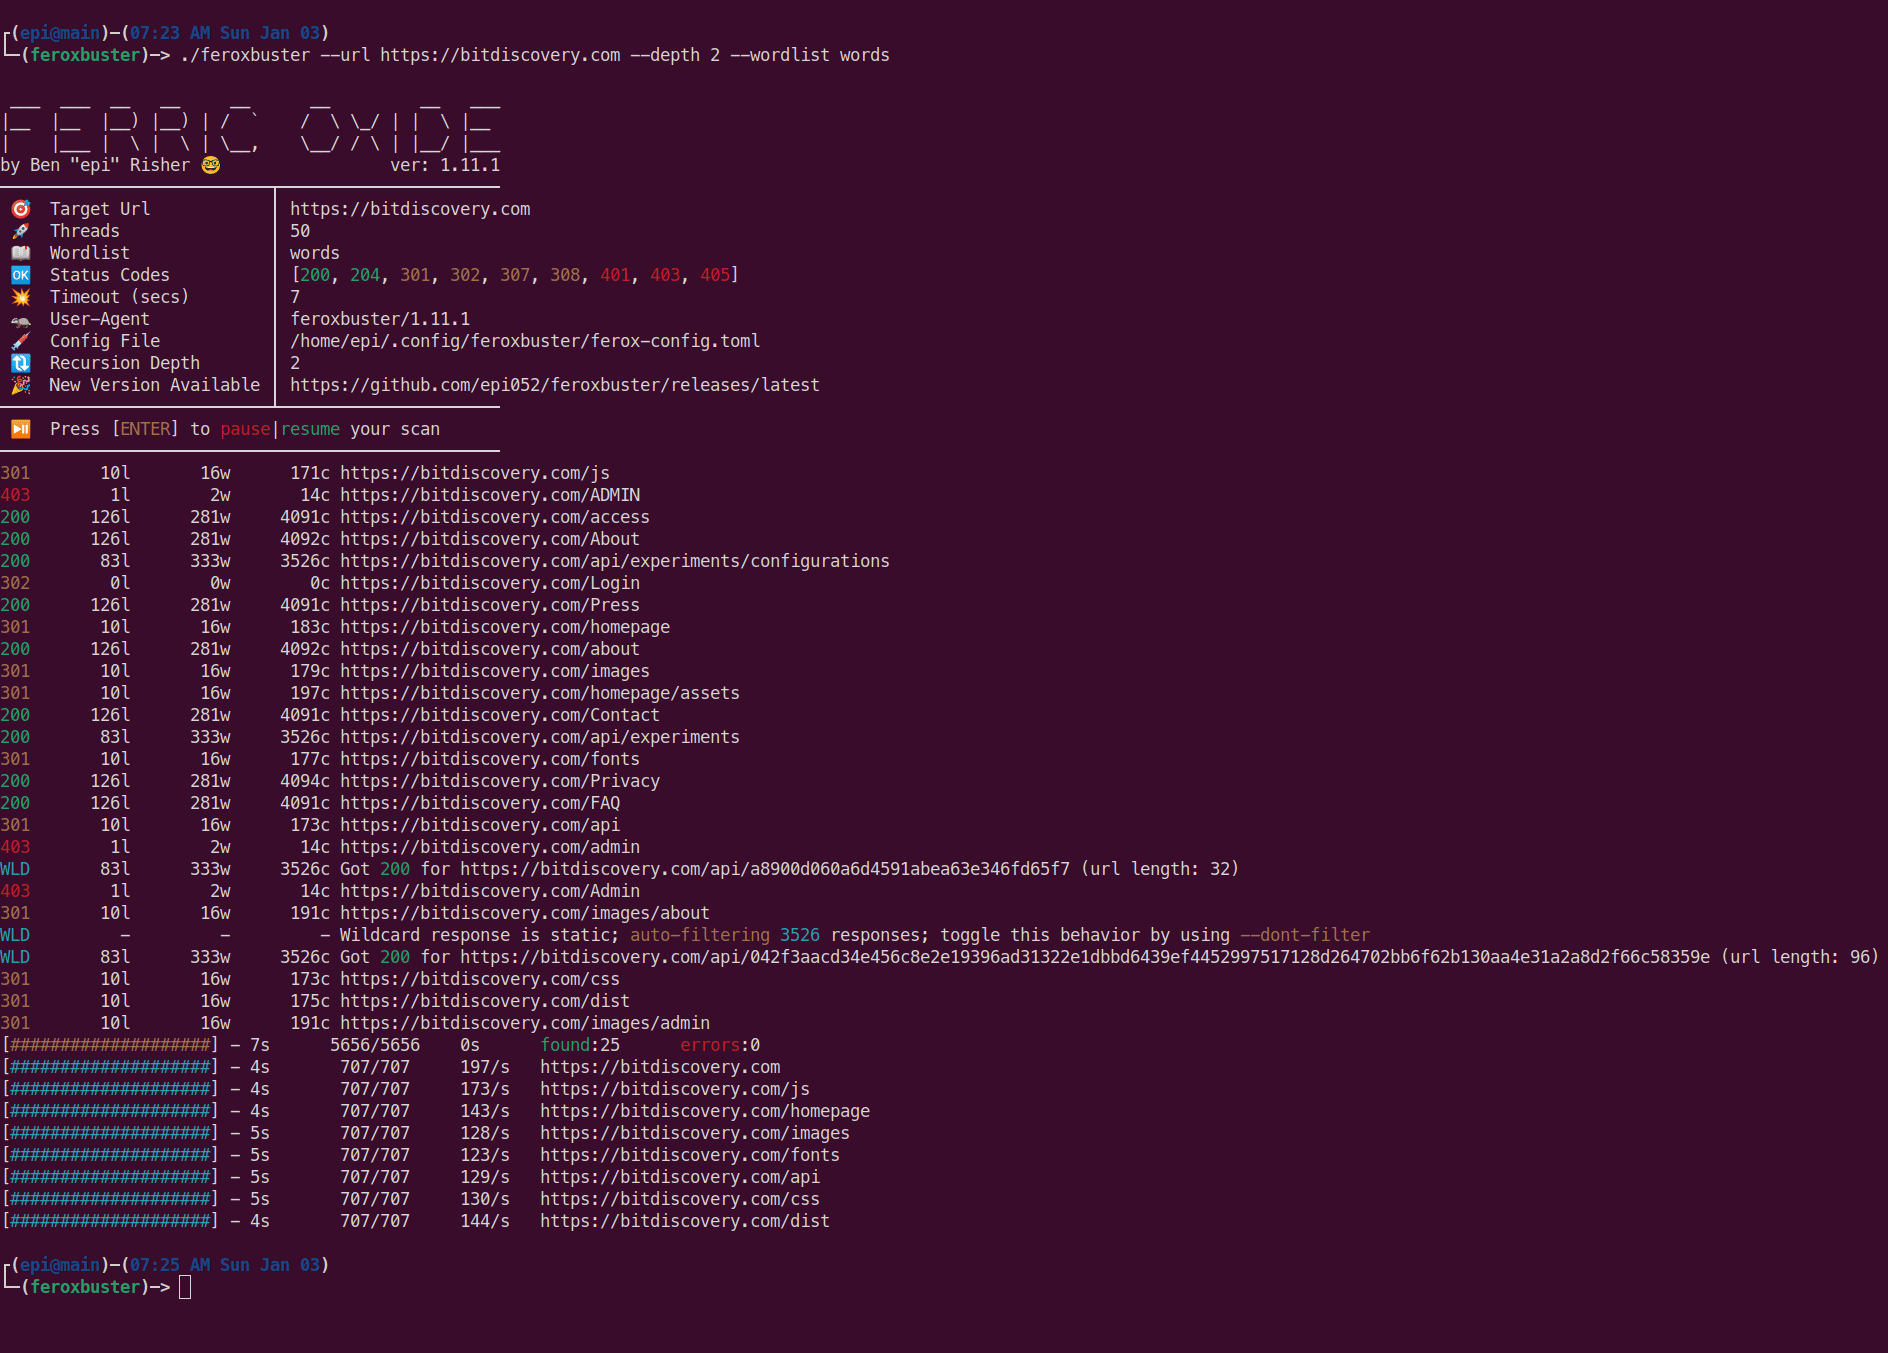
feroxbuster
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
api-securityapi-security-testingcrawler+8
epi052/feroxbusterA fast, simple, recursive content discovery tool written in Rust.
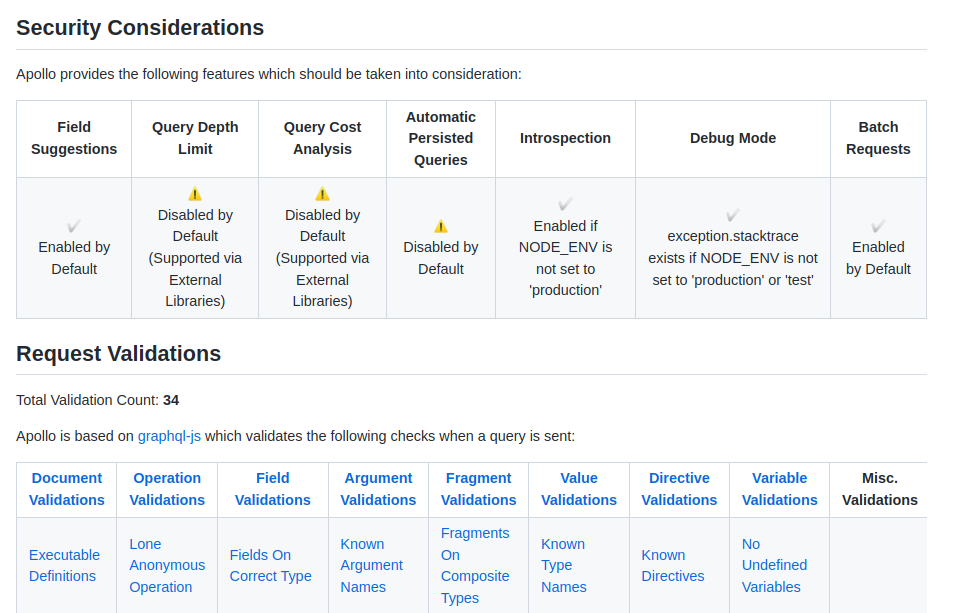 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 alufers/mitmproxy2swagger
Automagically reverse-engineer REST APIs via capturing traffic
 liodeus/swaggerhole
A python3 script searching for secret on swaggerhub
 censys/censys-python
An easy-to-use and lightweight API wrapper for Censys APIs.
 randomrobbiebf/super-secret-finder
Burp Plugin for Secret Matching
 undeadsec/swaggerspy
Automated OSINT tool that scans SwaggerHub API documentation to discover exposed secrets, credentials, and sensitive information using regex-based…
 momenbasel/keyfinder
Passive API key and secret discovery browser extension for Chrome and Firefox. 80+ detection patterns, zero config.
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
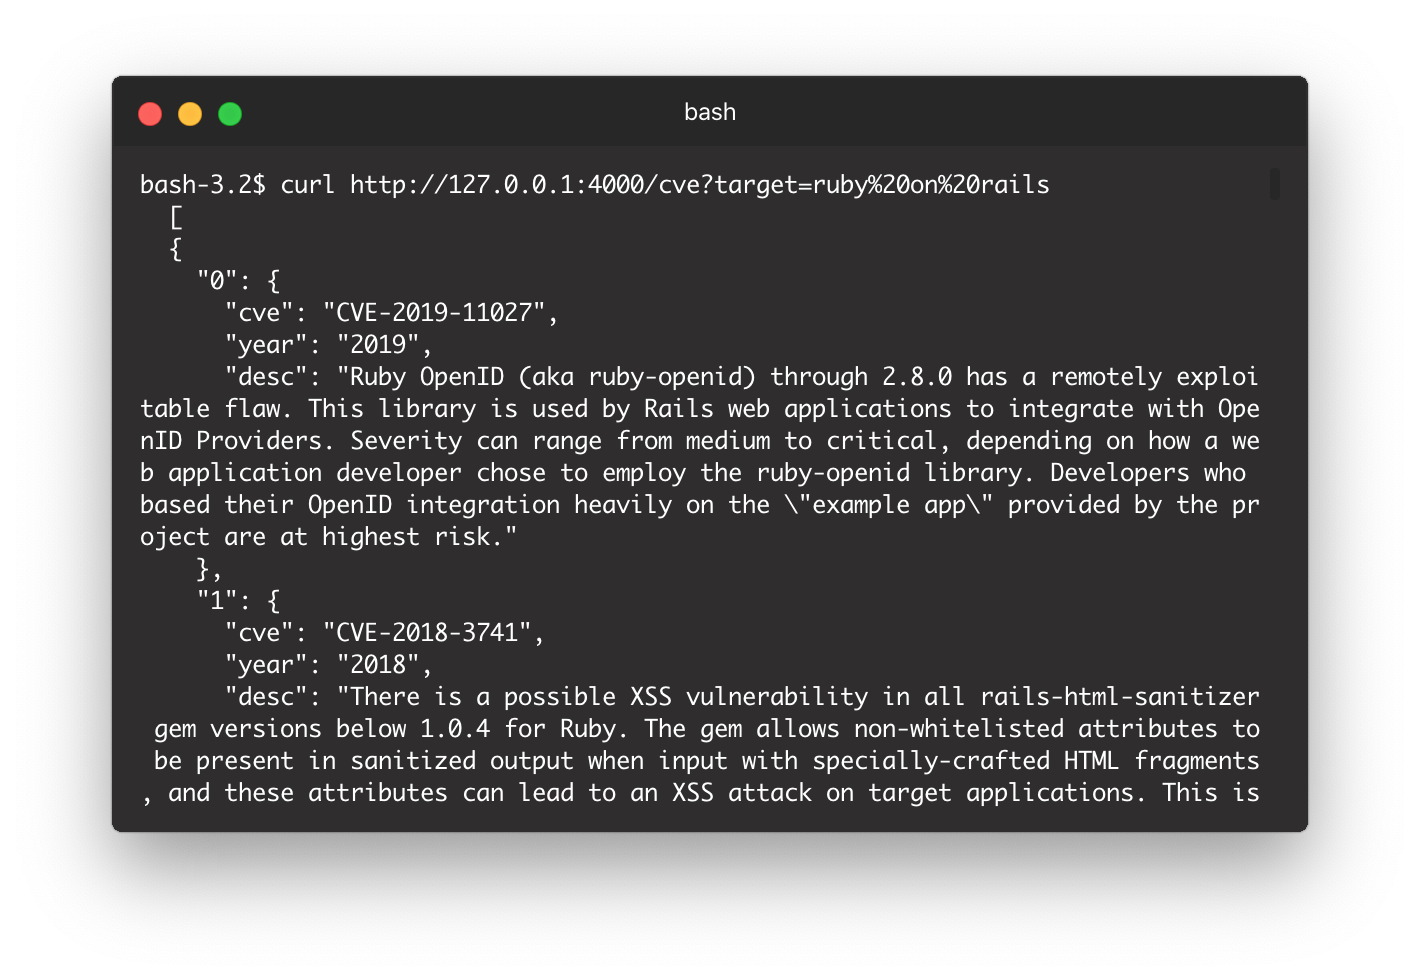 beyarz/cve-api
Unofficial api for cve.mitre.org
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
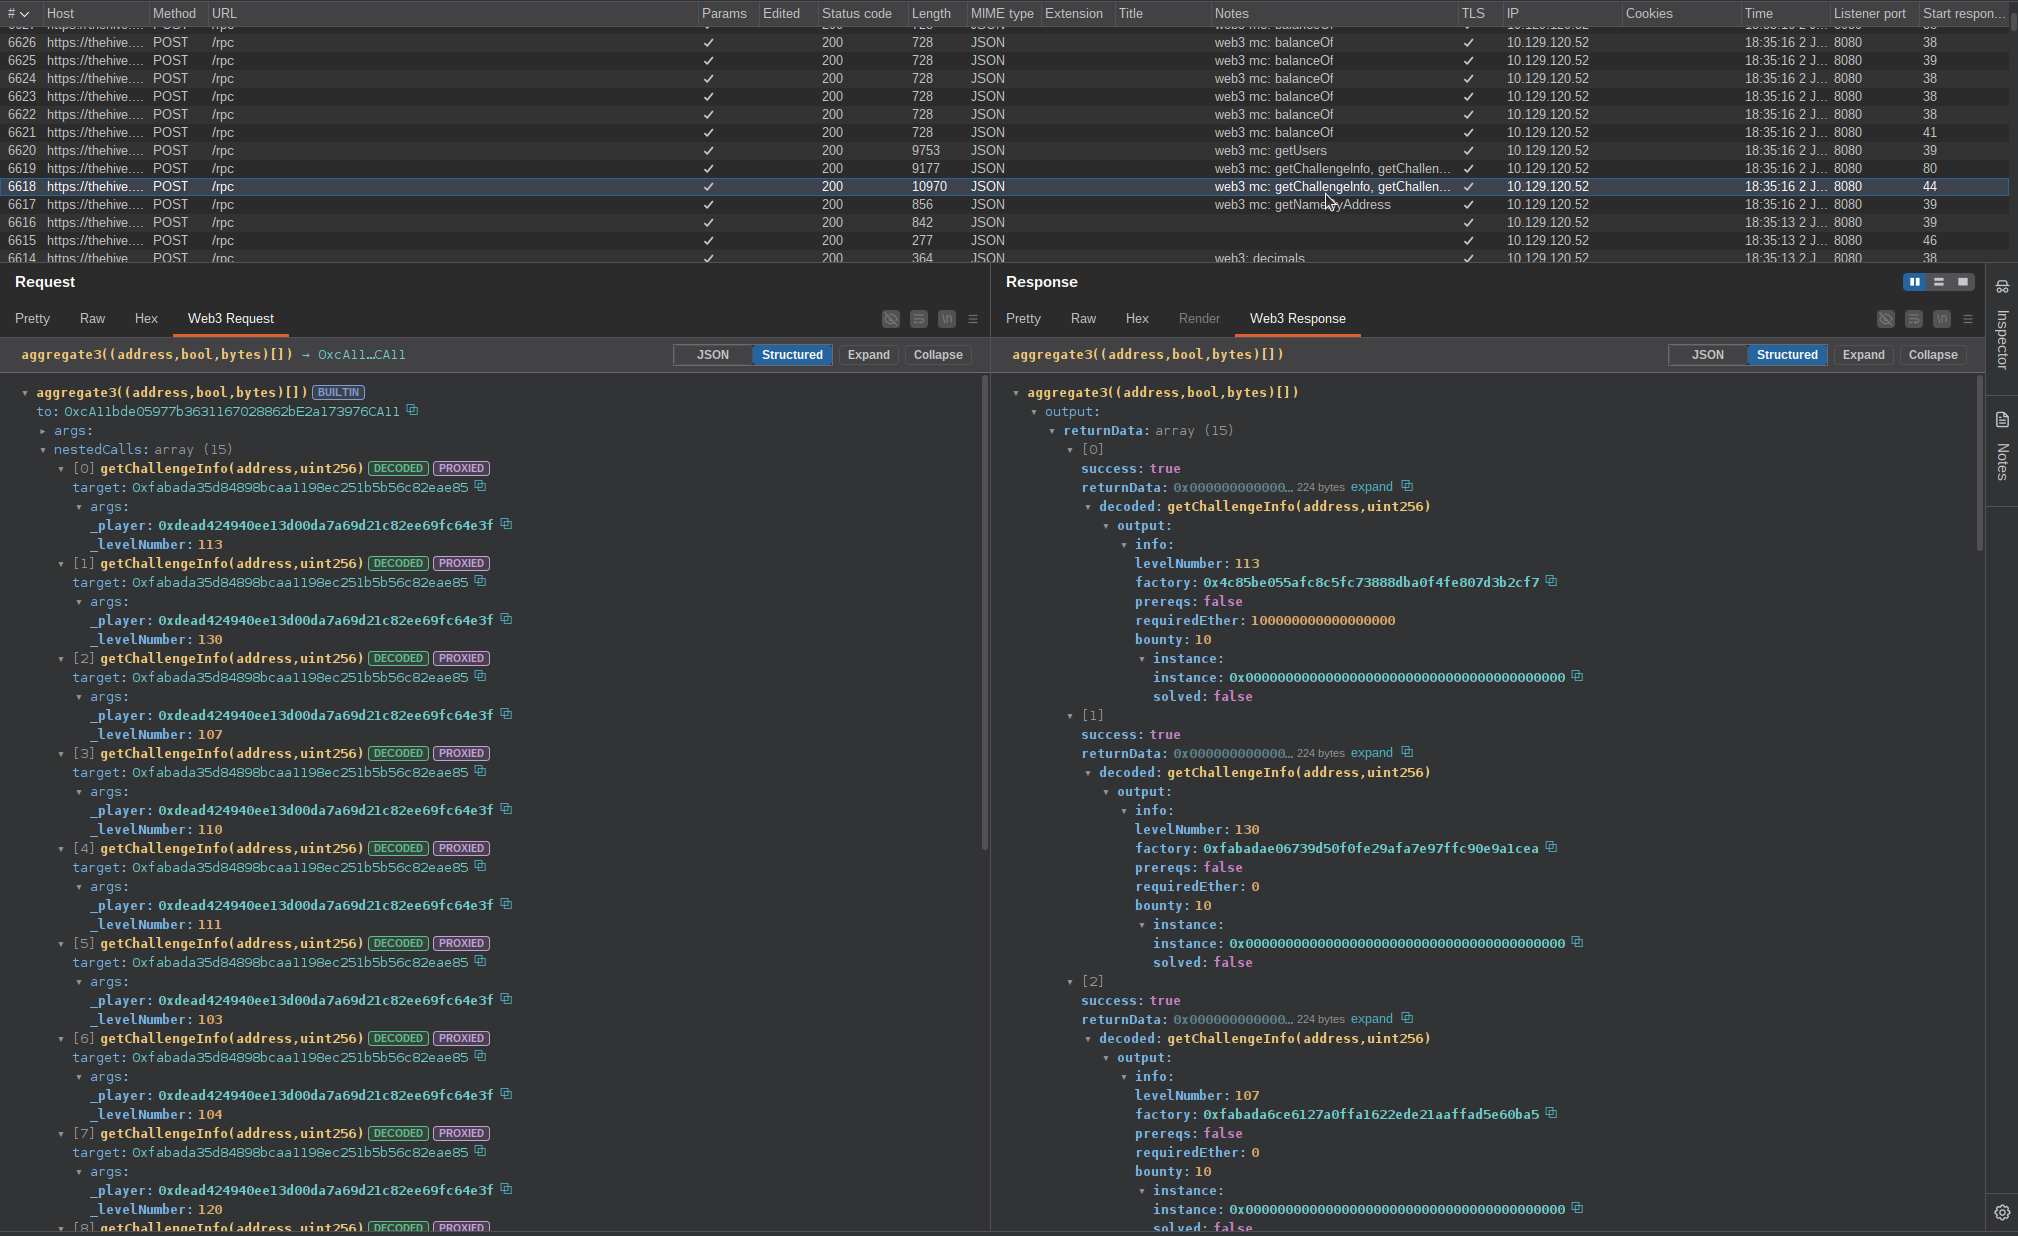 nccgroup/web3-decoder
Burp Suite extension for decoding Web3 JSON-RPC traffic, including smart contract function calls, responses, and ABI resolution with proxy-aware and…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 ex-cal1bur/cve-2026-44595
# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API
 aman-parmar/cve-2025-54554
CVE-2025-54554 – Unauthenticated Access in tiaudit REST API leading to Sensitive Information Disclosure
 secsys-fdu/cve-2025-51869
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Liner's chat component, allowing attackers to tamper with other users'…
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…