
KProcTerminator
 gmh5225/kprocterminator
Windows kernel driver designed for terminating specific processes on a system
anti-botdefensive-toolsmalware-analysis+3
gmh5225/kprocterminatorWindows kernel driver designed for terminating specific processes on a system
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
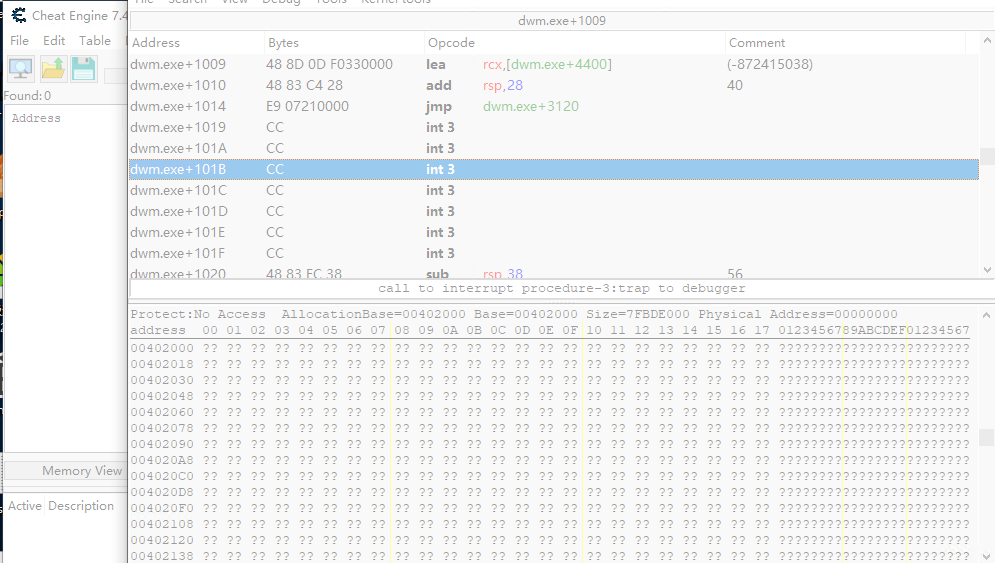 gmh5225/fakeenclave
Proof-of-concept that abuses Windows Enclave to implement anti-tamper and anti-cheat evasion techniques at the driver level.
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 alphadelta/secure-desktop
Anti-keylogger/anti-rat application for Windows
 ak3zaidan/trust-decision-security
Reverse Engineer of Trust Decision Chinese Security
 phpmussel/phpmussel
PHP-based anti-virus anti-trojan anti-malware solution.
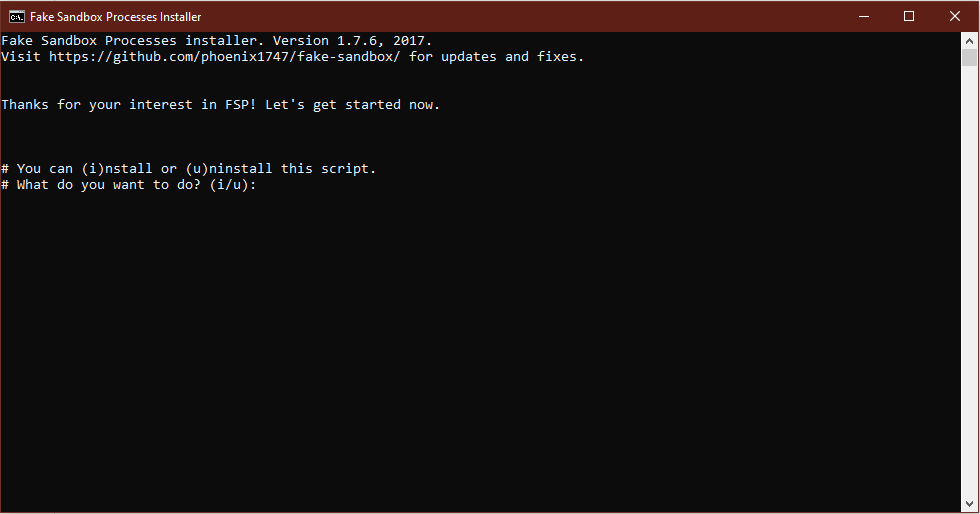 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 theevilbit/shield
An app to protect against process injection and suspicious file links on macOS
 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…