
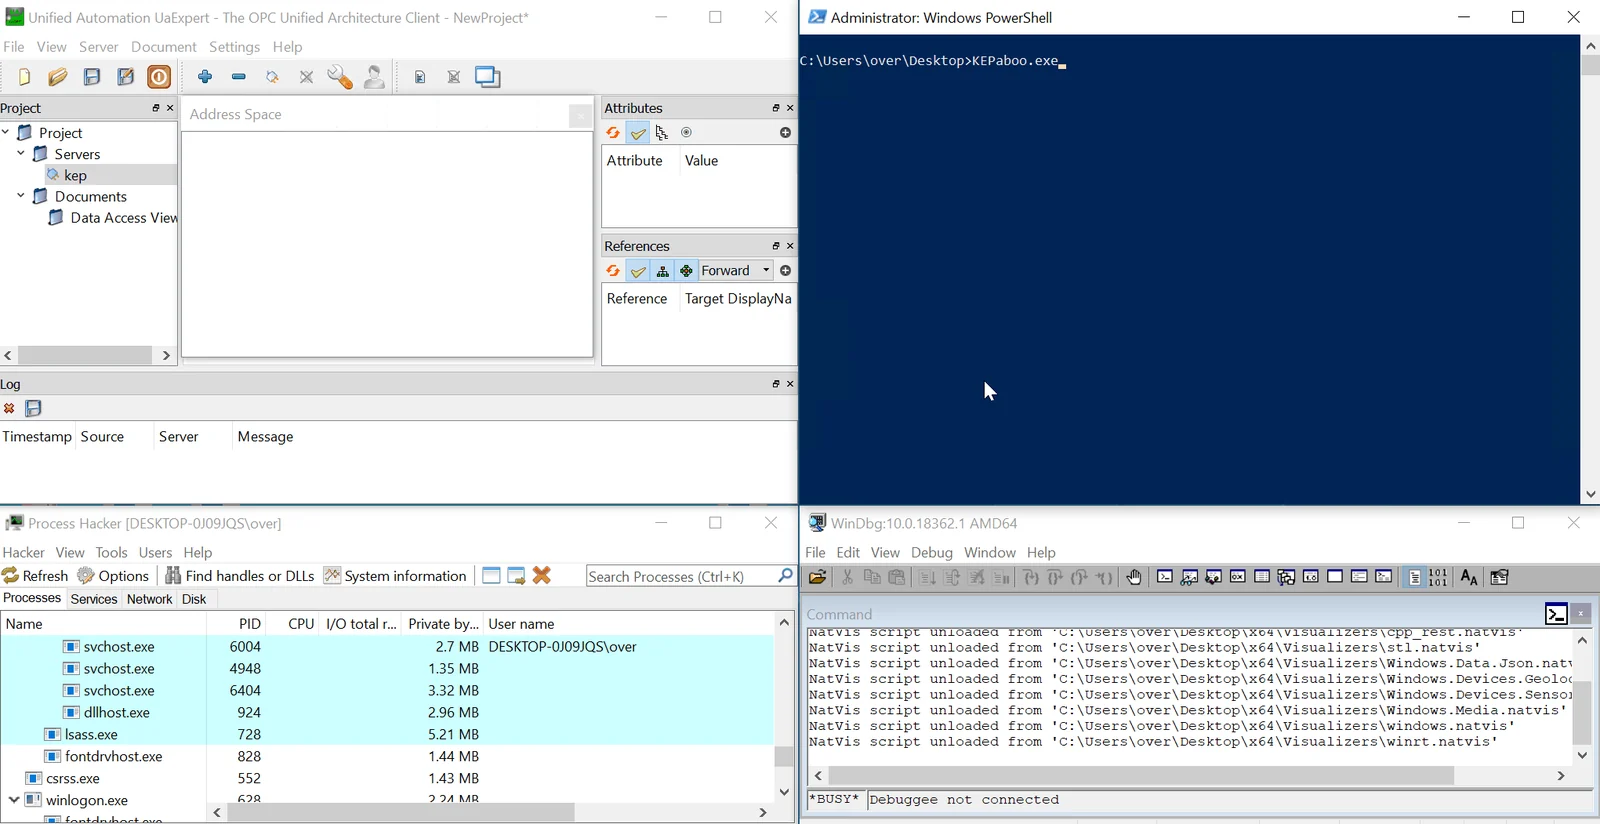
KEPaboo
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
anti-botbinary-analysisbinary-exploitation+5
0vercl0k/kepabooNeutralize KEPServerEX anti-debugging techniques
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 xkiian/vercel-botid
Vercel BotID Solver "X-Is-Human" using 100% golang
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
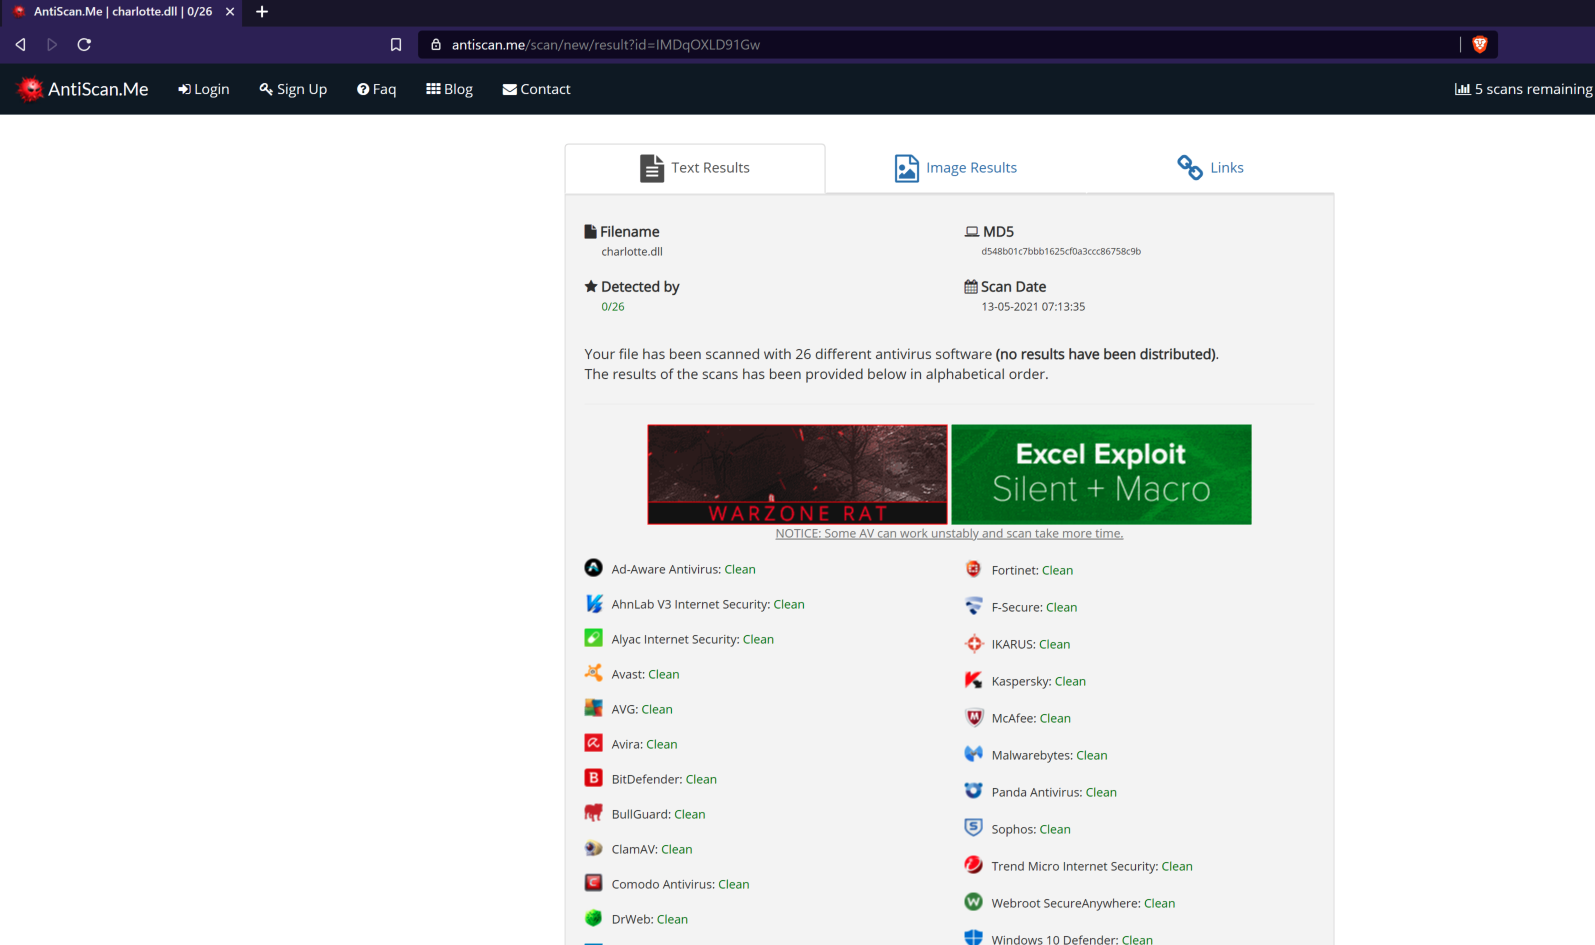 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way