
AiSOC
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
ai-securityanomaly-detectiondefensive-tools+5
2.4k
beenuar/aisocSelf-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 al0ne/cloud-audit
Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…
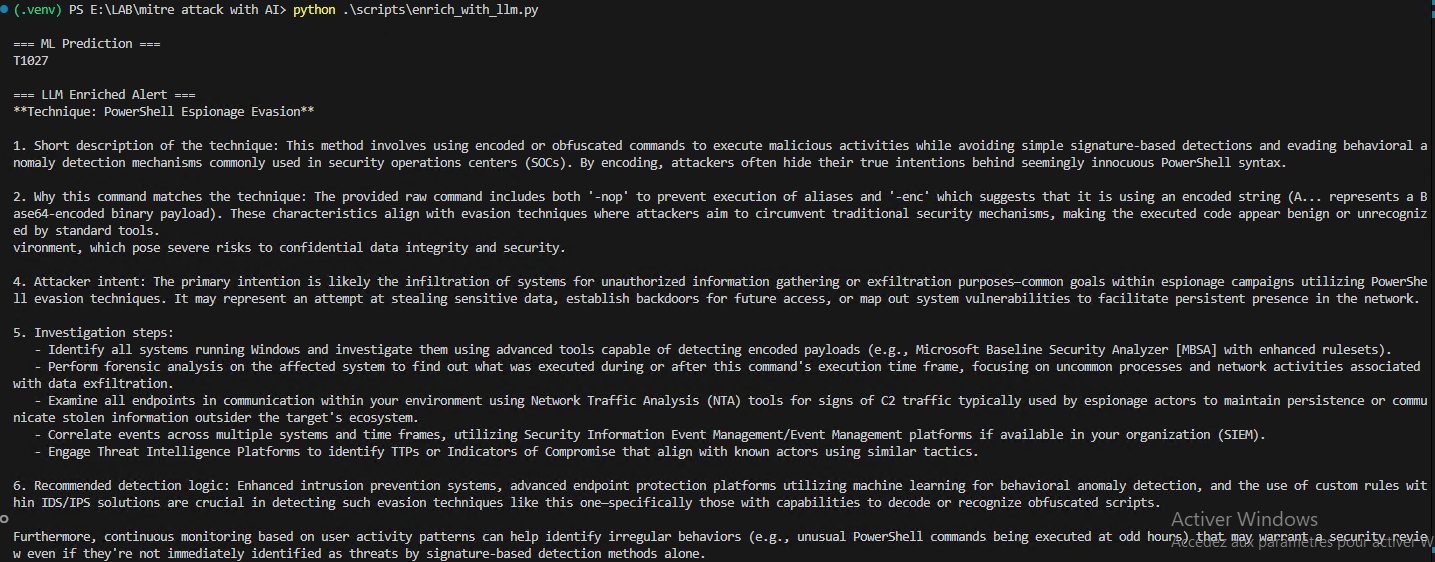 mouna23/ai-driven-mitre-attack
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.
 lightless-labs/third-thoughts
Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…

 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
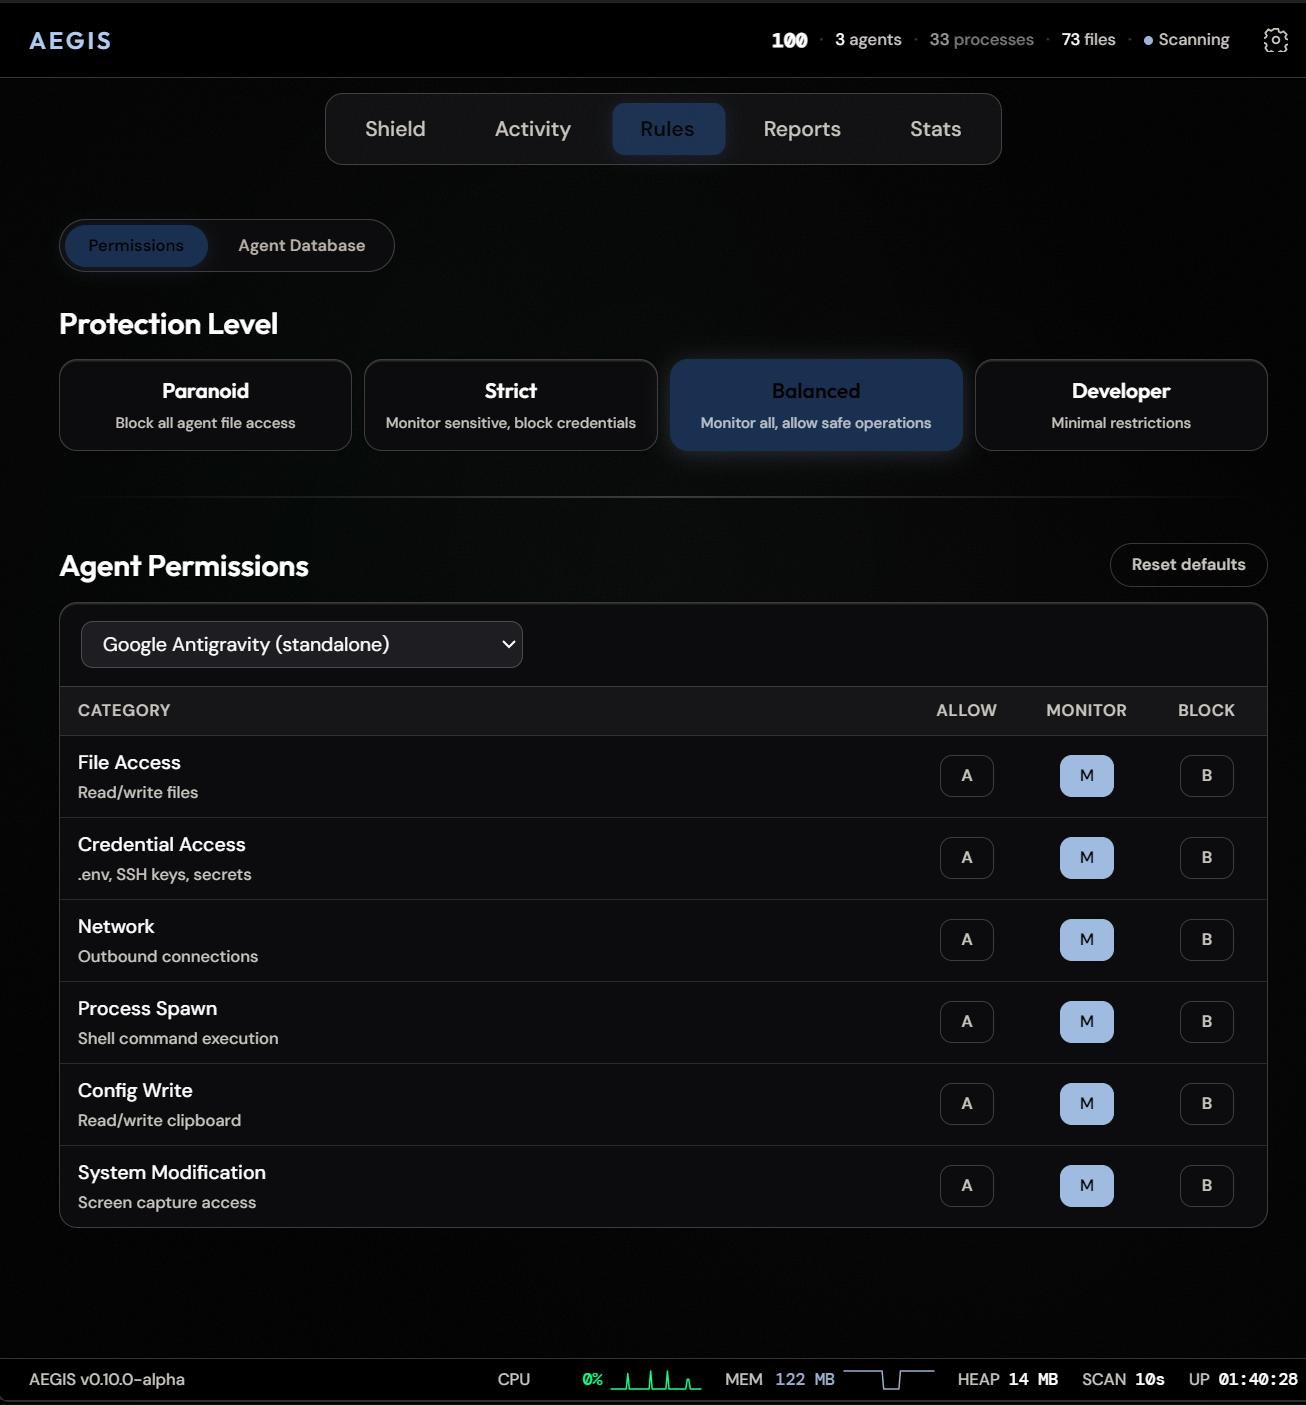 antropos17/aegis
Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
 corelight/zeek-long-connections
Zeek package for tracking long connections to report them before they have completed.
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.