
DetectWindowsCopyOnWriteForAPI
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
anomaly-detectiondefensive-toolsforensics+3
200
nccgroup/detectwindowscopyonwriteforapiEnumerate various traits from Windows processes as an aid to threat hunting
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
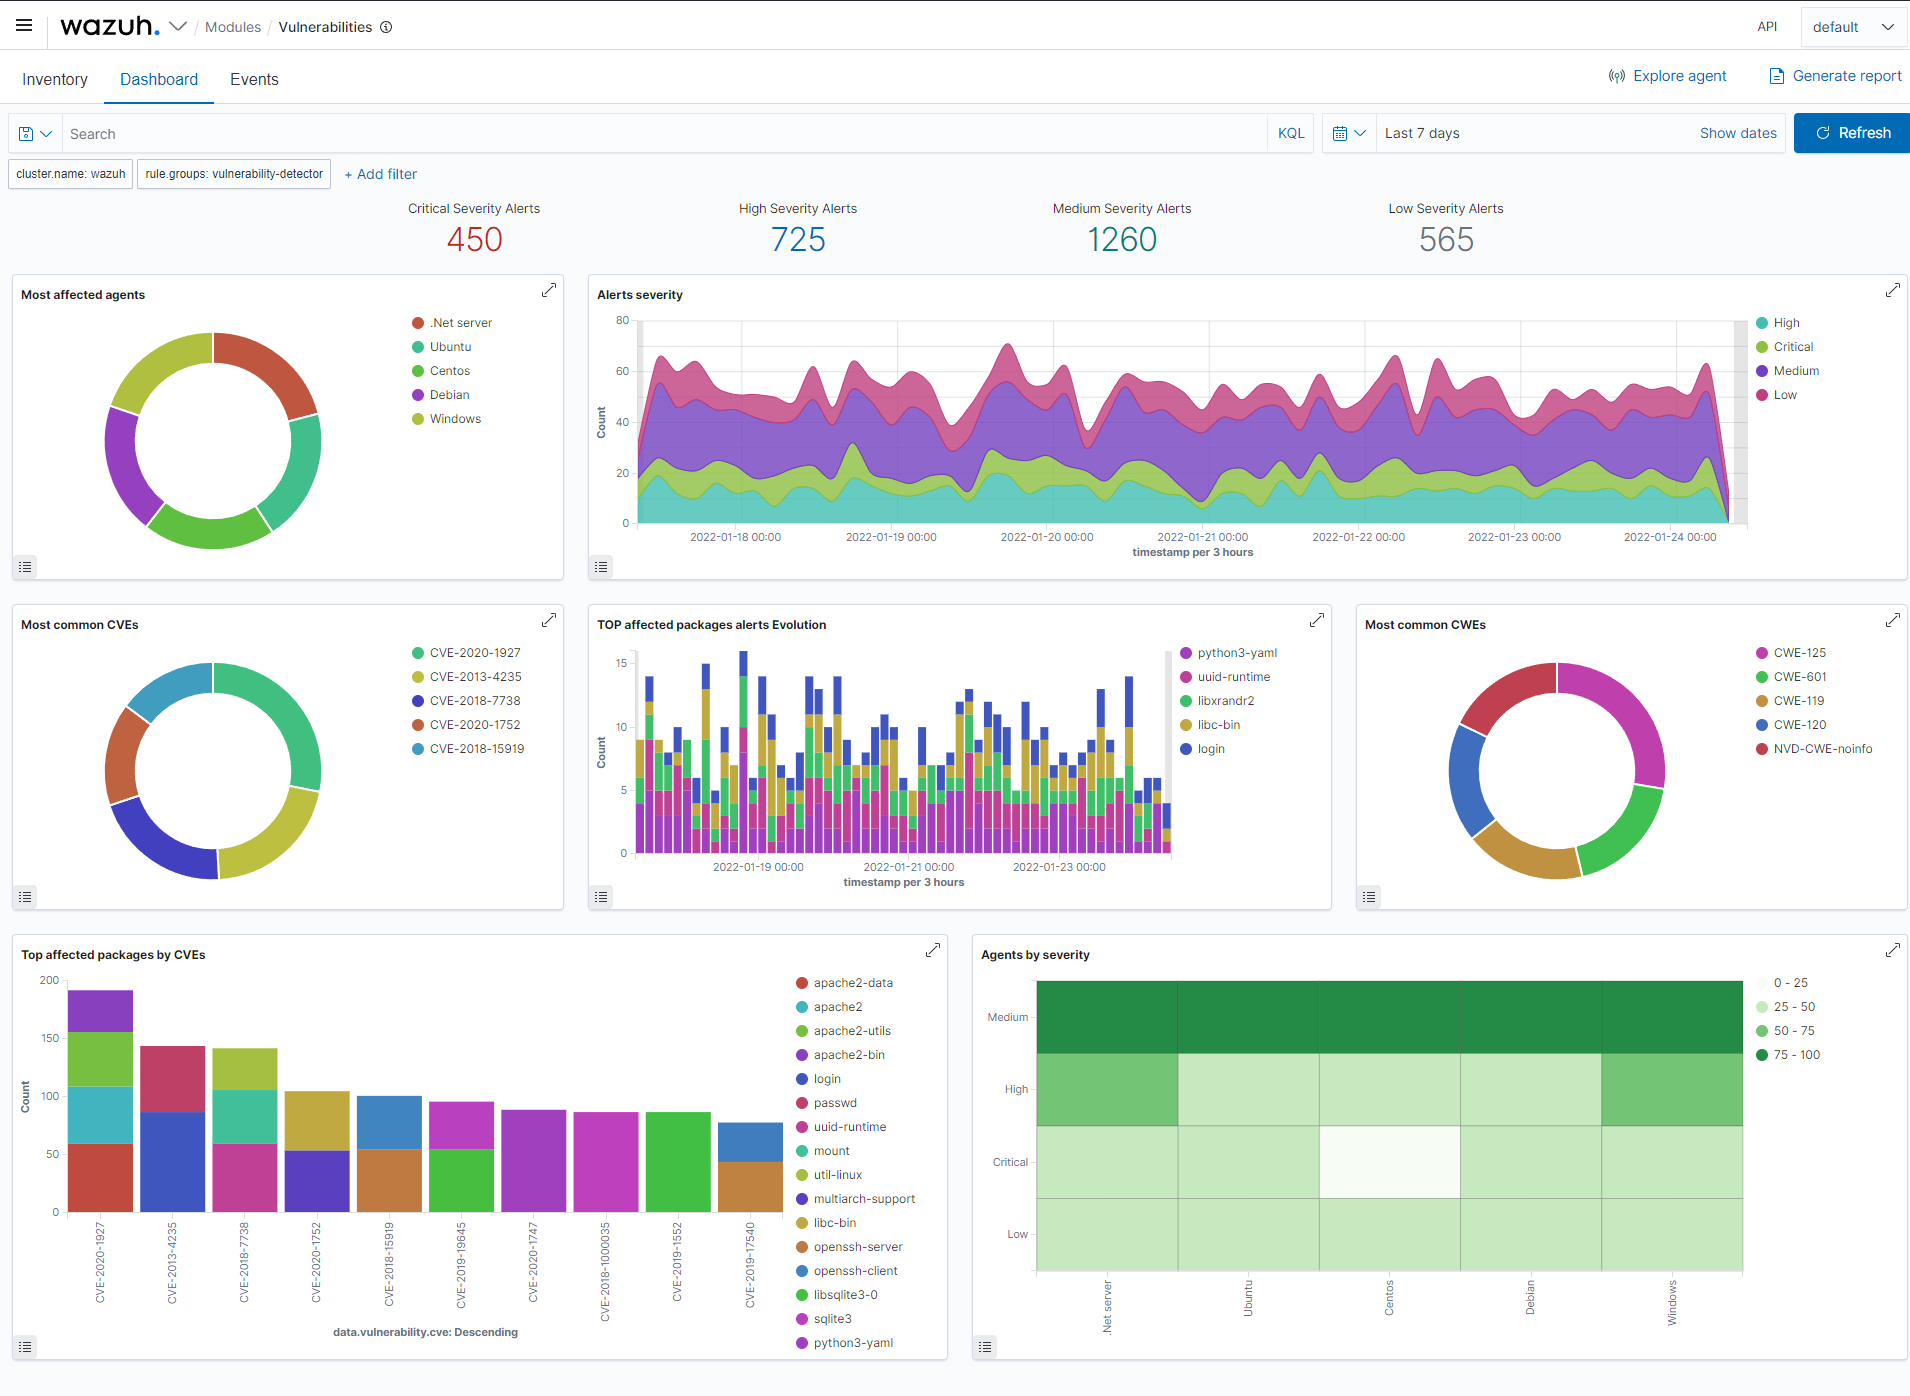 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 zoneminder/zoneminder
ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.
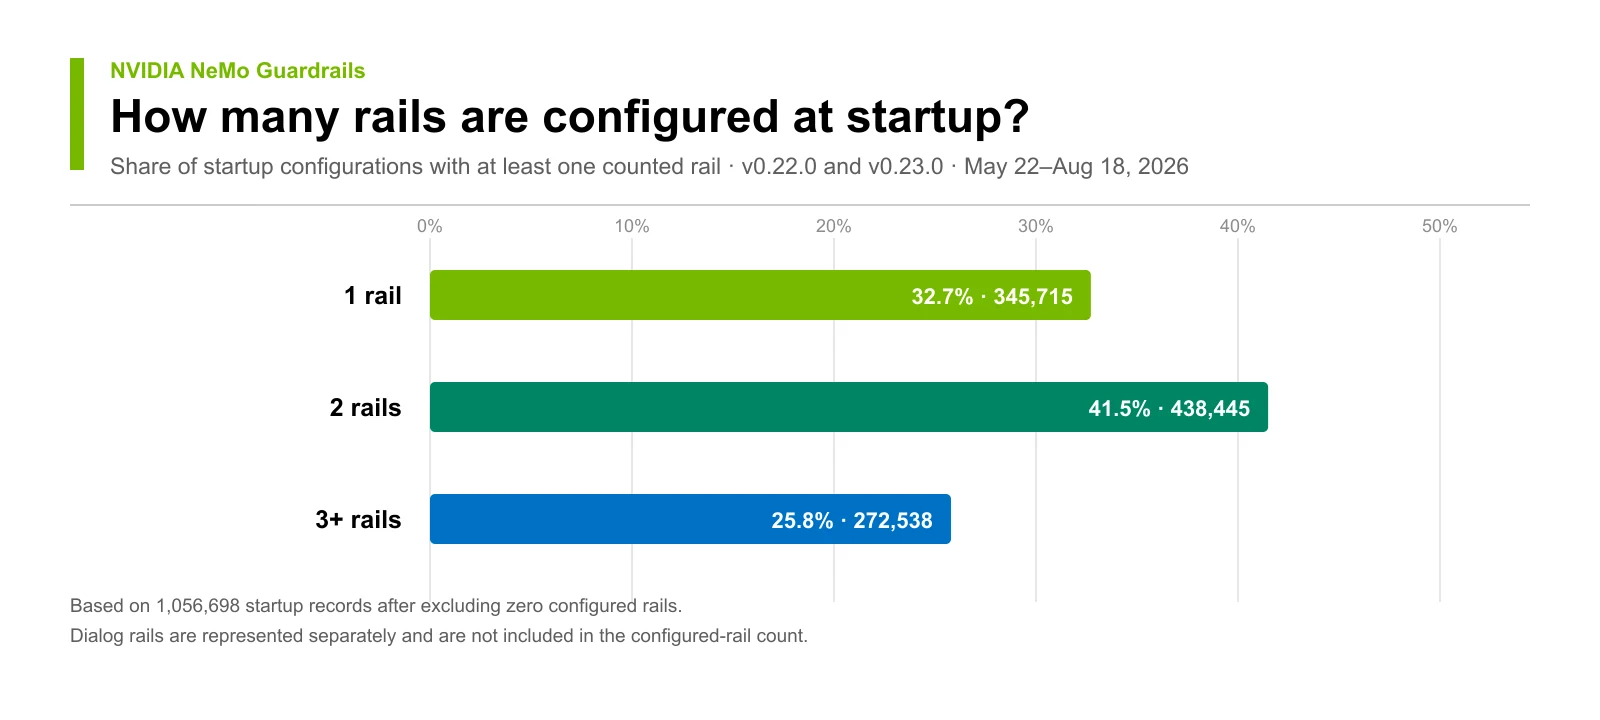 nvidia-nemo/guardrails
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 echowei/deeptraffic
Deep Learning models for network traffic classification
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 chainguard-dev/osquery-defense-kit
Production-ready detection & response queries for osquery
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
 travisbgreen/hunting-rules
Suricata rules for network anomaly detection
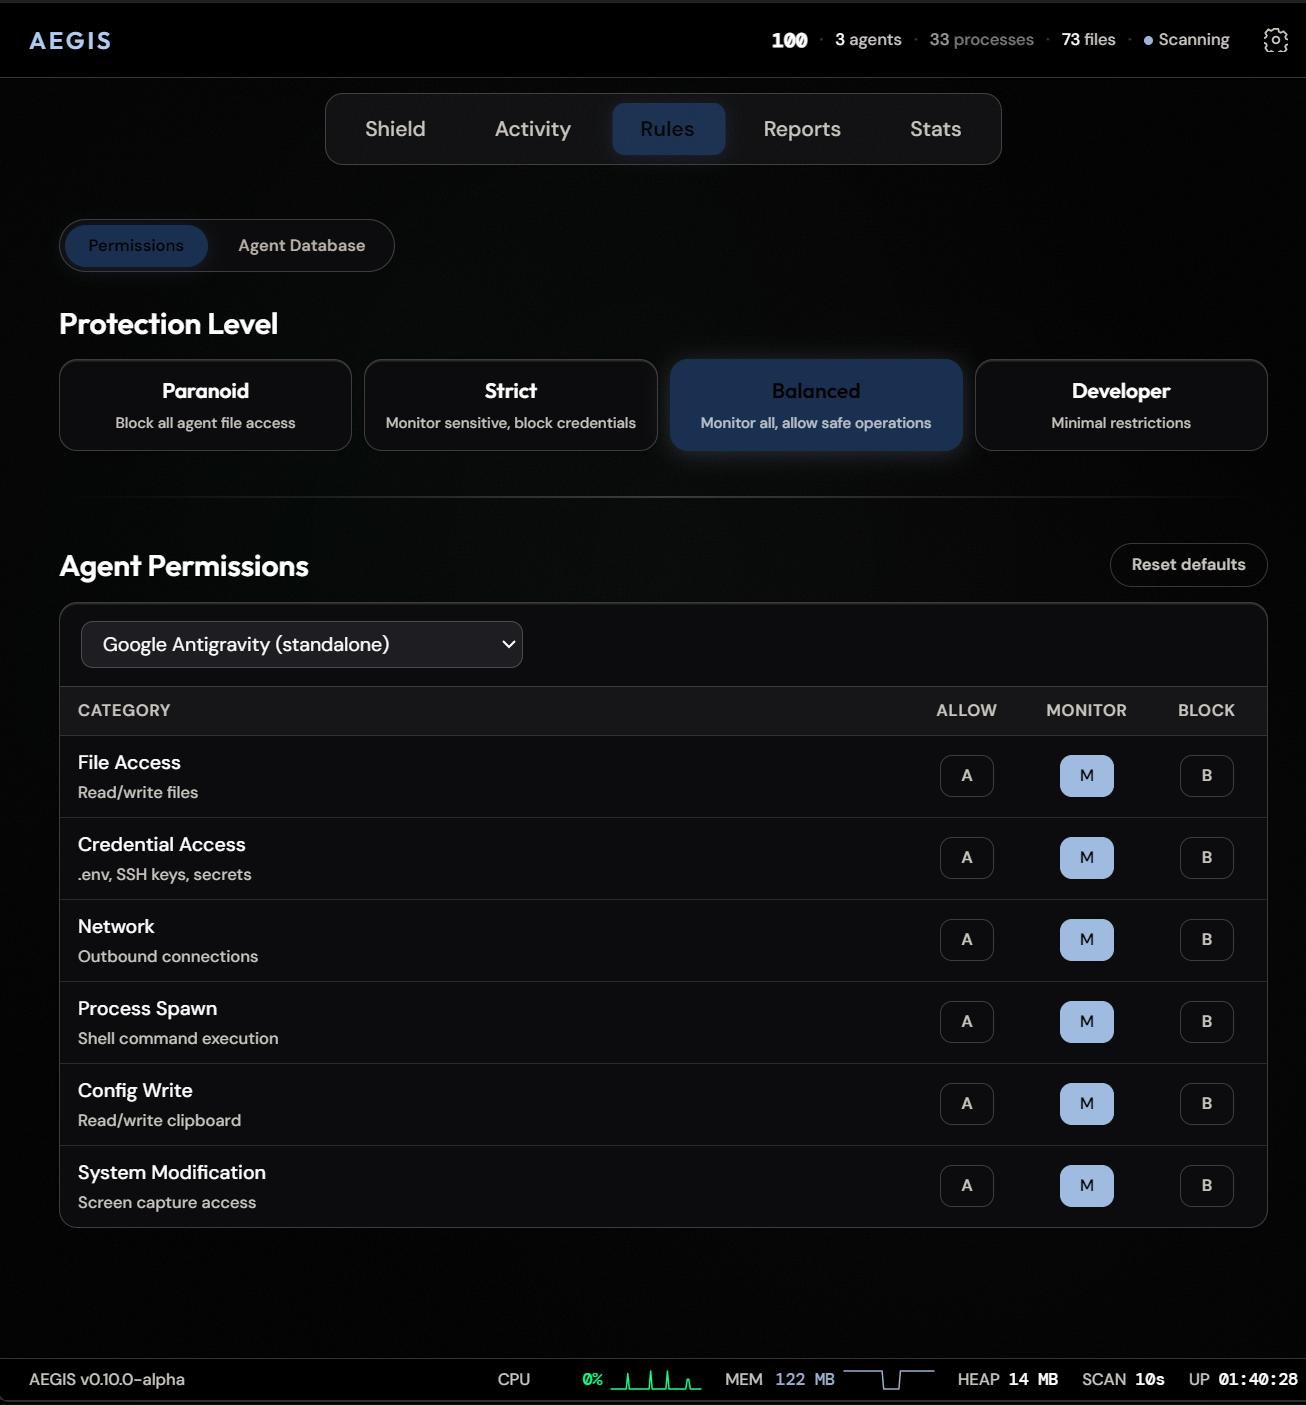 antropos17/aegis
Local, monitor-first observability for AI agents: processes, file activity, TCP endpoints and attribution evidence. Windows primary; macOS/Linux…