
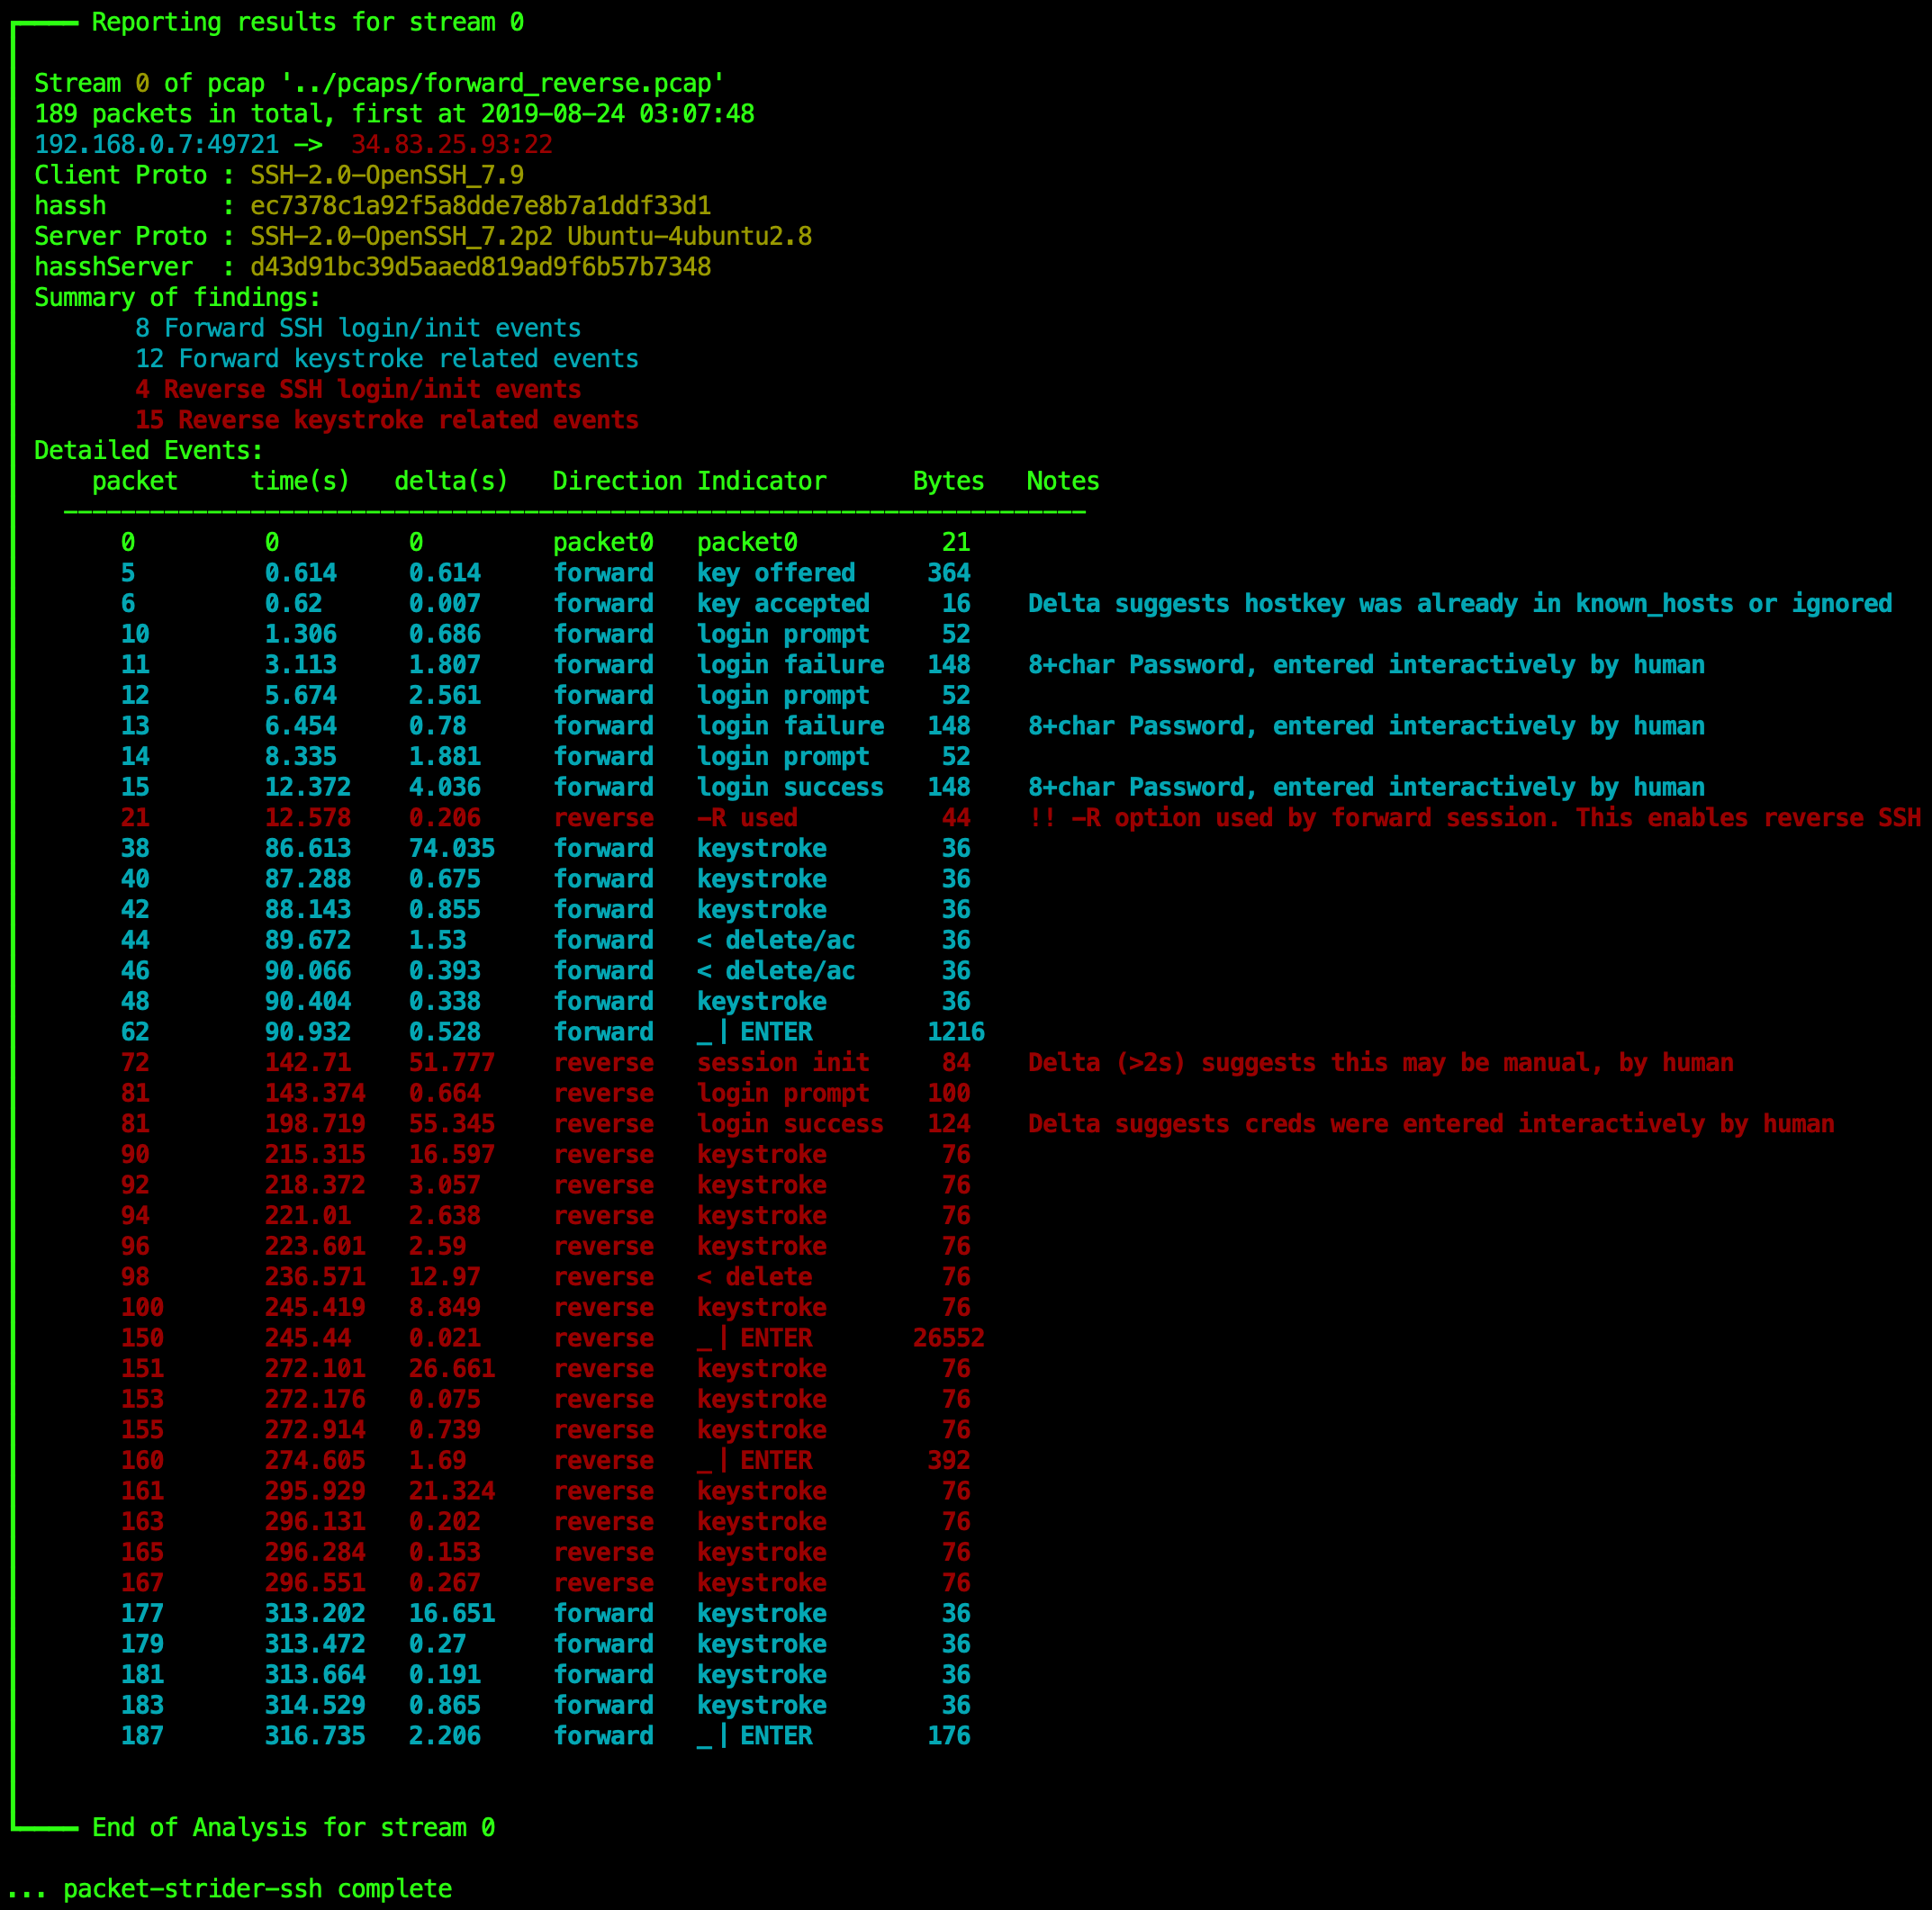
packetStrider
 benjeems/packetstrider
A network packet forensics tool for SSH
anomaly-detectionforensicsintrusion-detection+5
255
benjeems/packetstriderA network packet forensics tool for SSH
 sage-s11/sigcorr
SigCorr is the first open-source tool to detect cross-protocol attack chains spanning SS7/MAP, Diameter S6a, and GTPv2-C through unified subscriber…
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 arthastang/iot-home-guard
A tool for malicious behavior detection in IoT devices
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
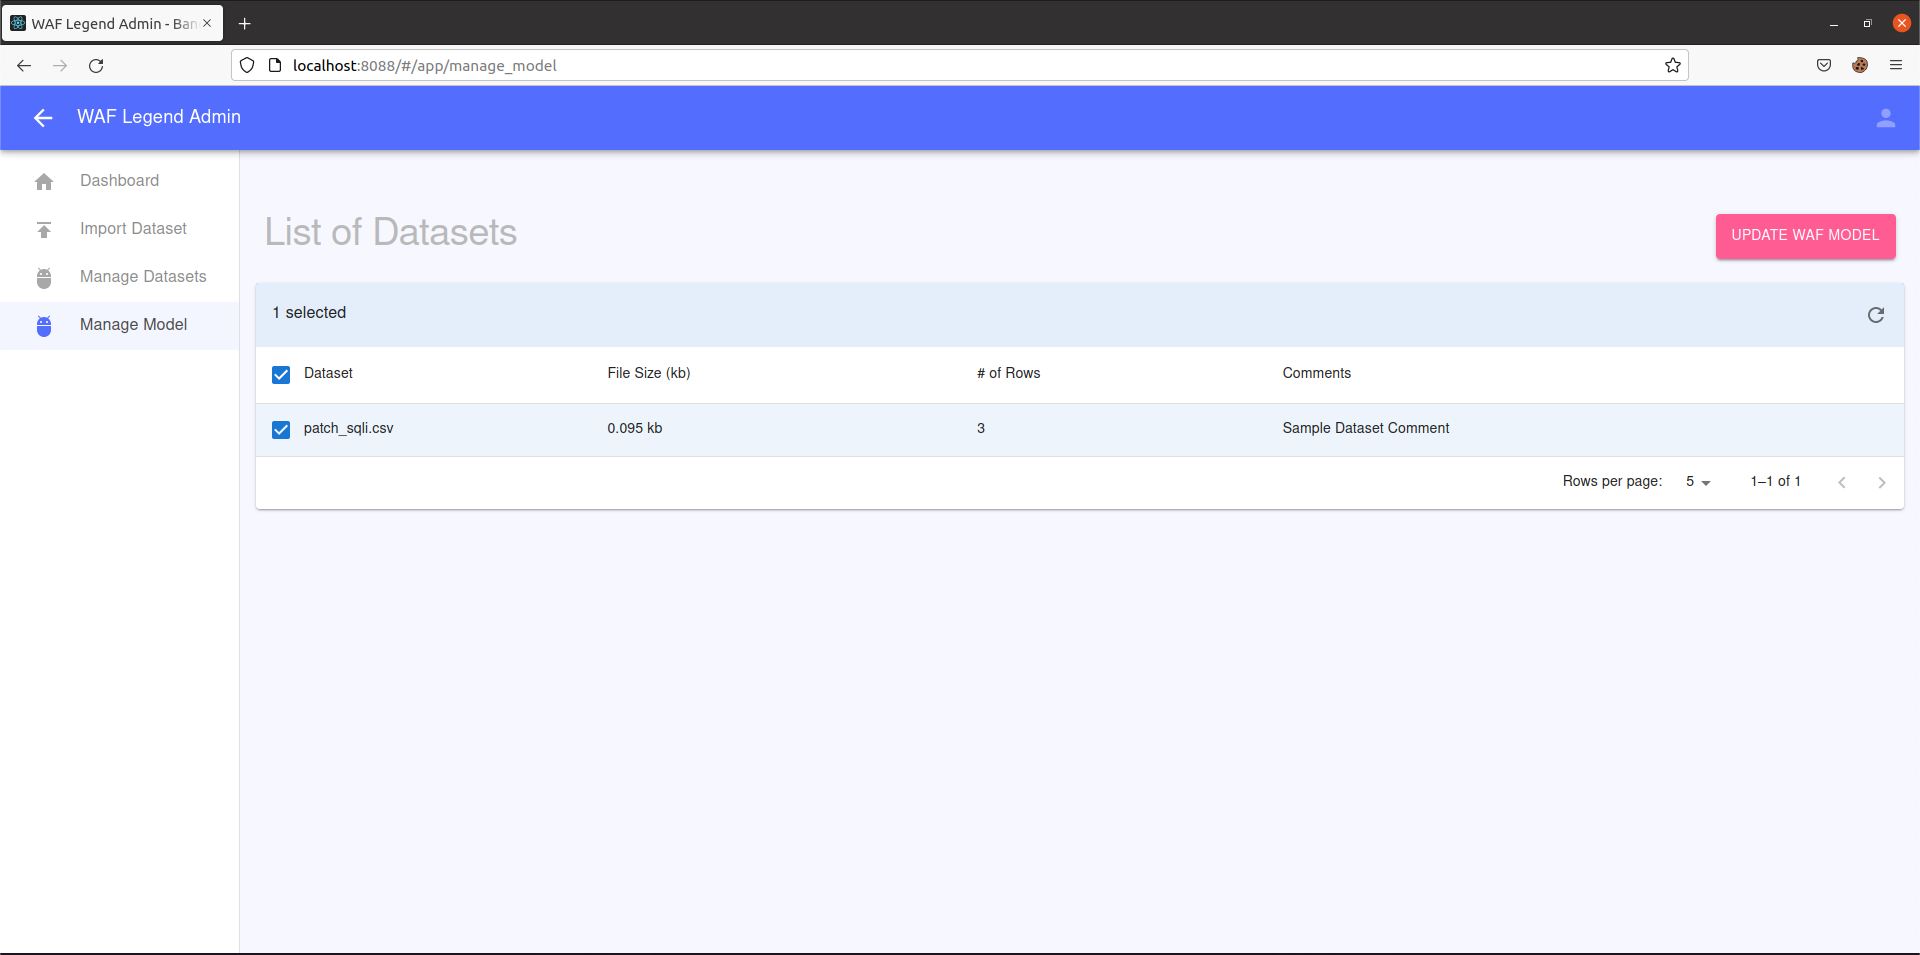 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
 c0oki3s/veilgate
Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…
 thingsboard/thingsboard
Open-source IoT Platform - Device management, data collection, processing and visualization.
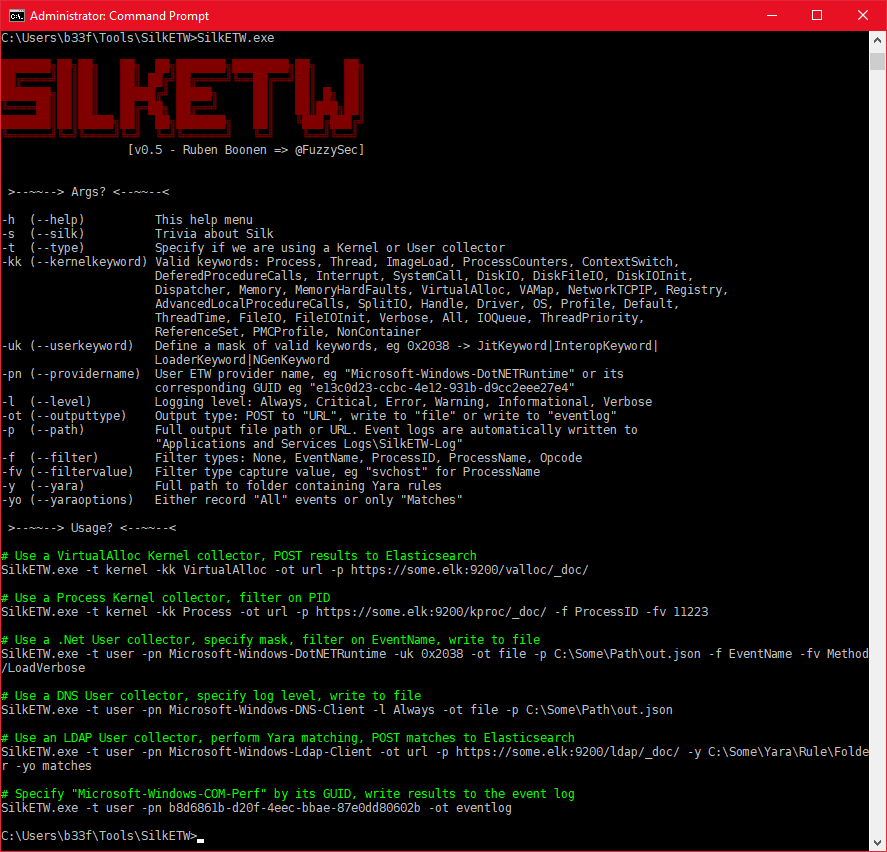 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
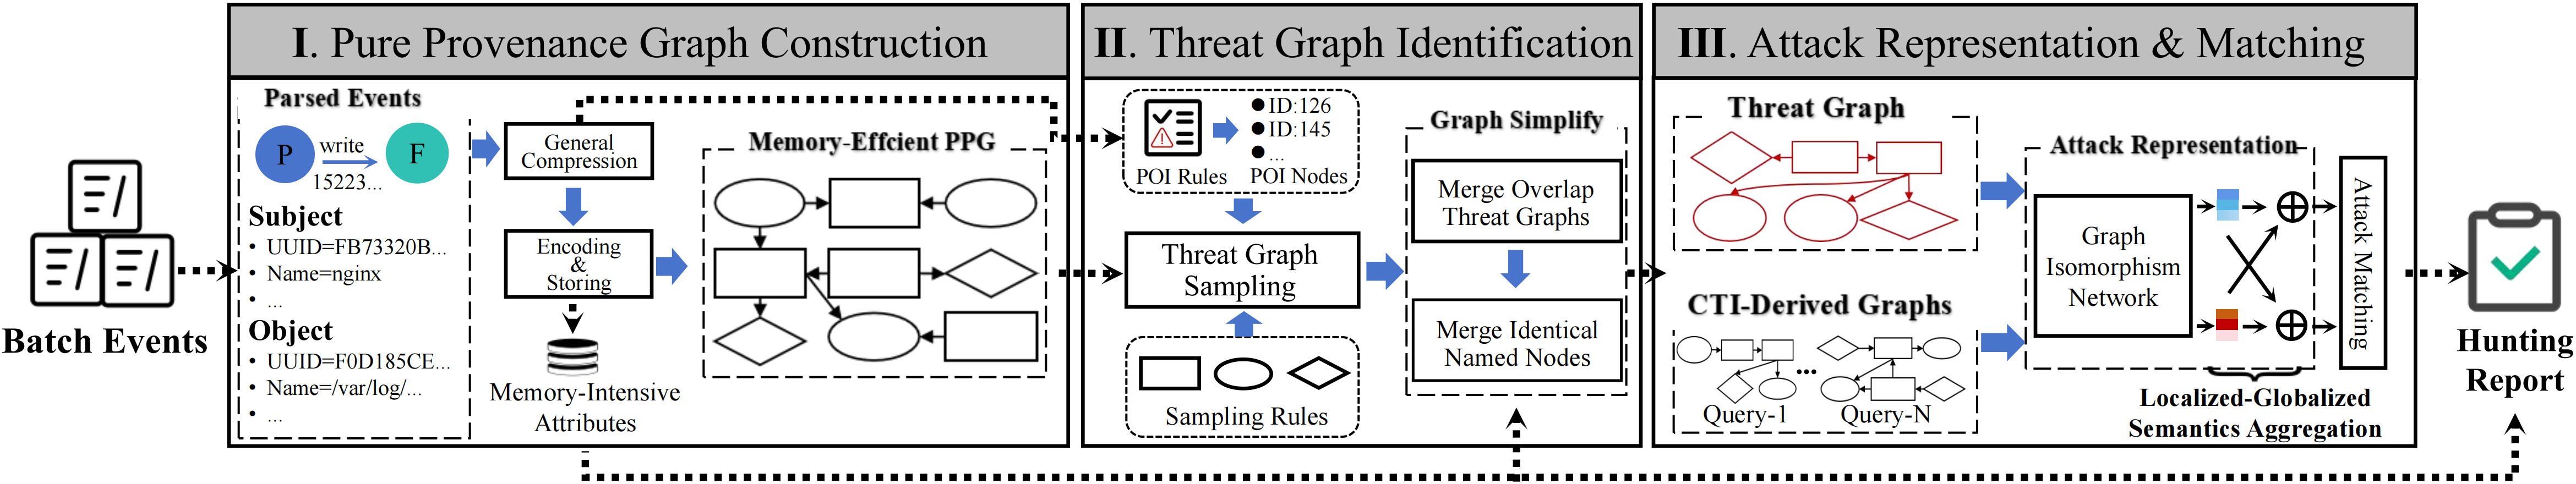 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 skac44/cve-2024-38063
Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
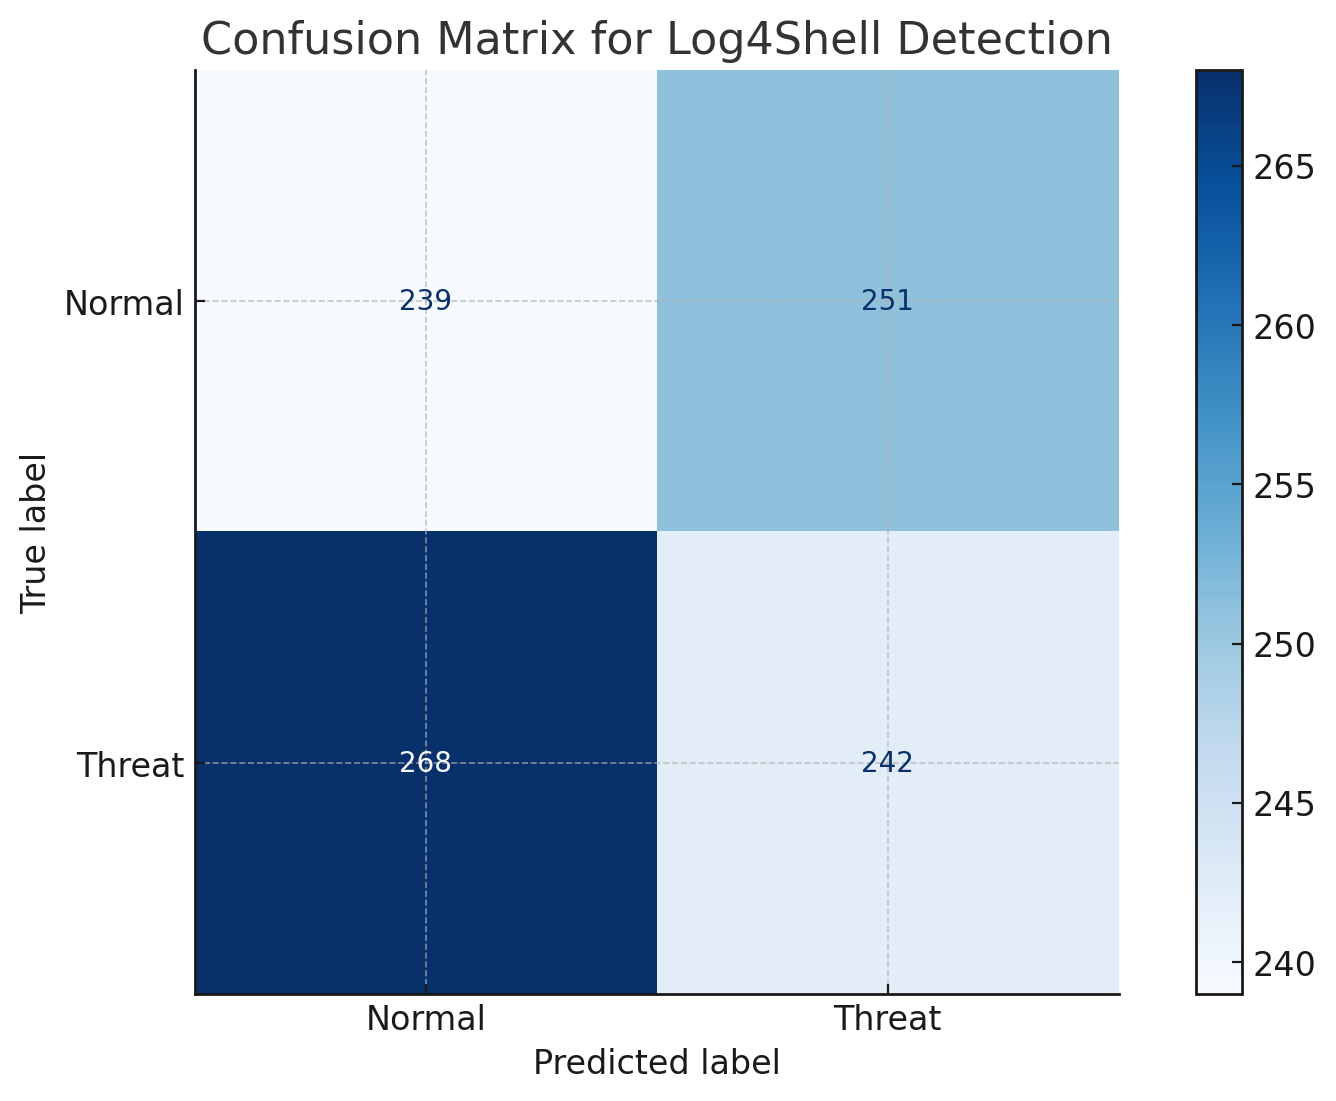 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
 corelight/zeek-long-connections
Zeek package for tracking long connections to report them before they have completed.
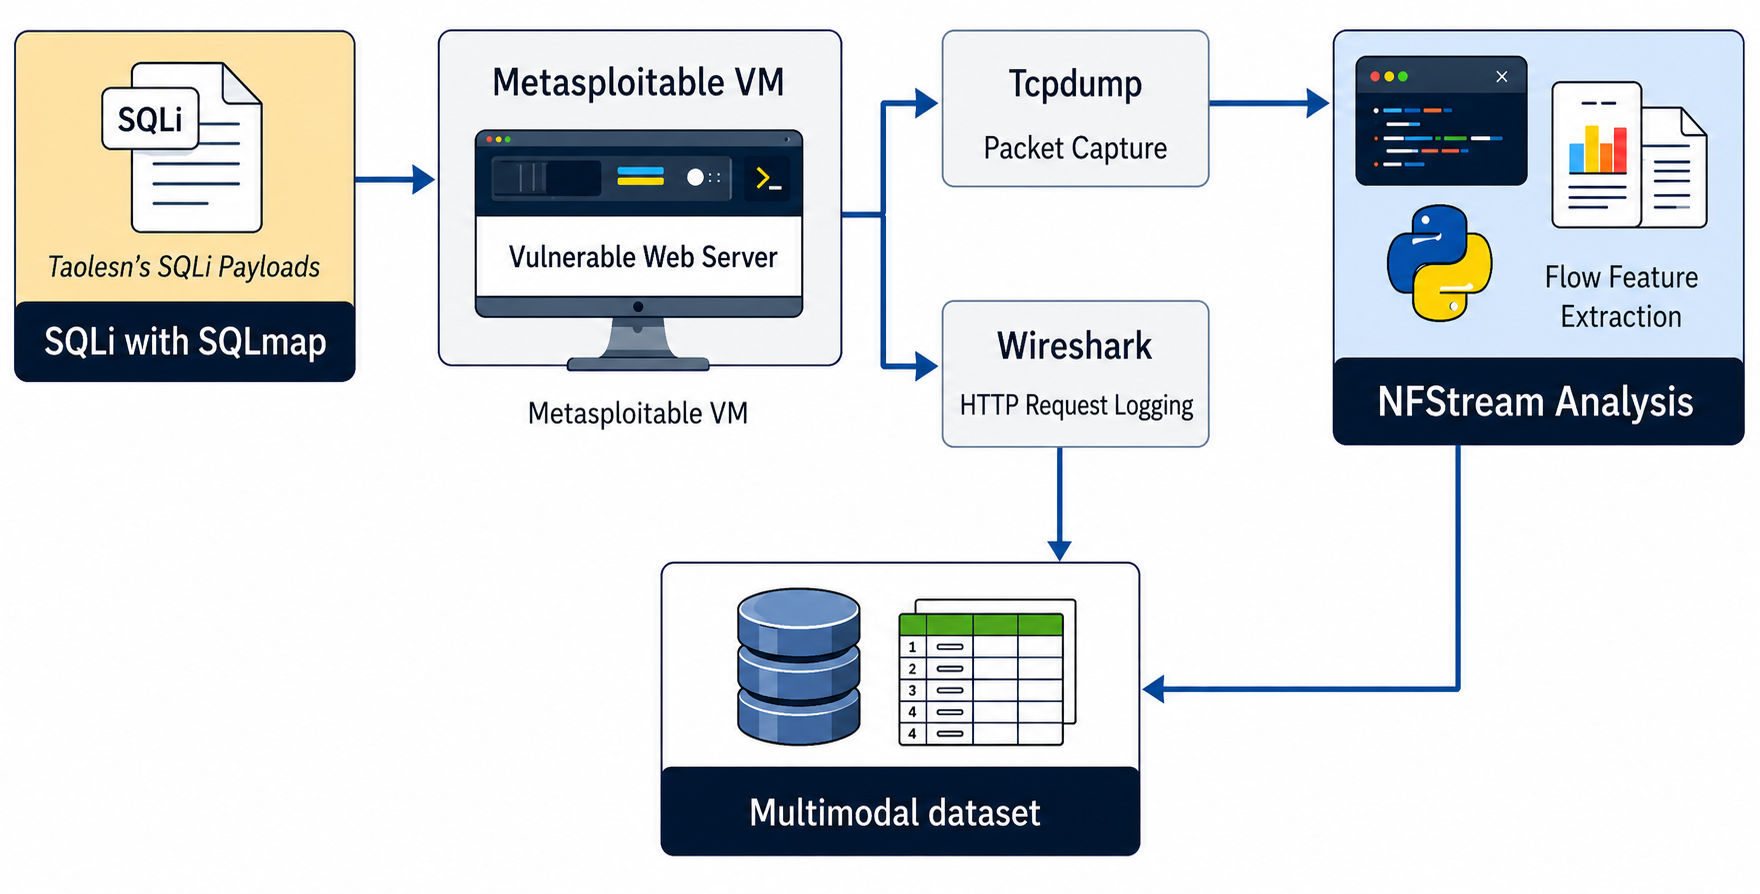 paul12345-cyber/multimodal-web-attack-dataset
This repository hosts a multimodal web attack dataset (MWAD) to advance AI-driven threat detection research.