logdata-anomaly-miner

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

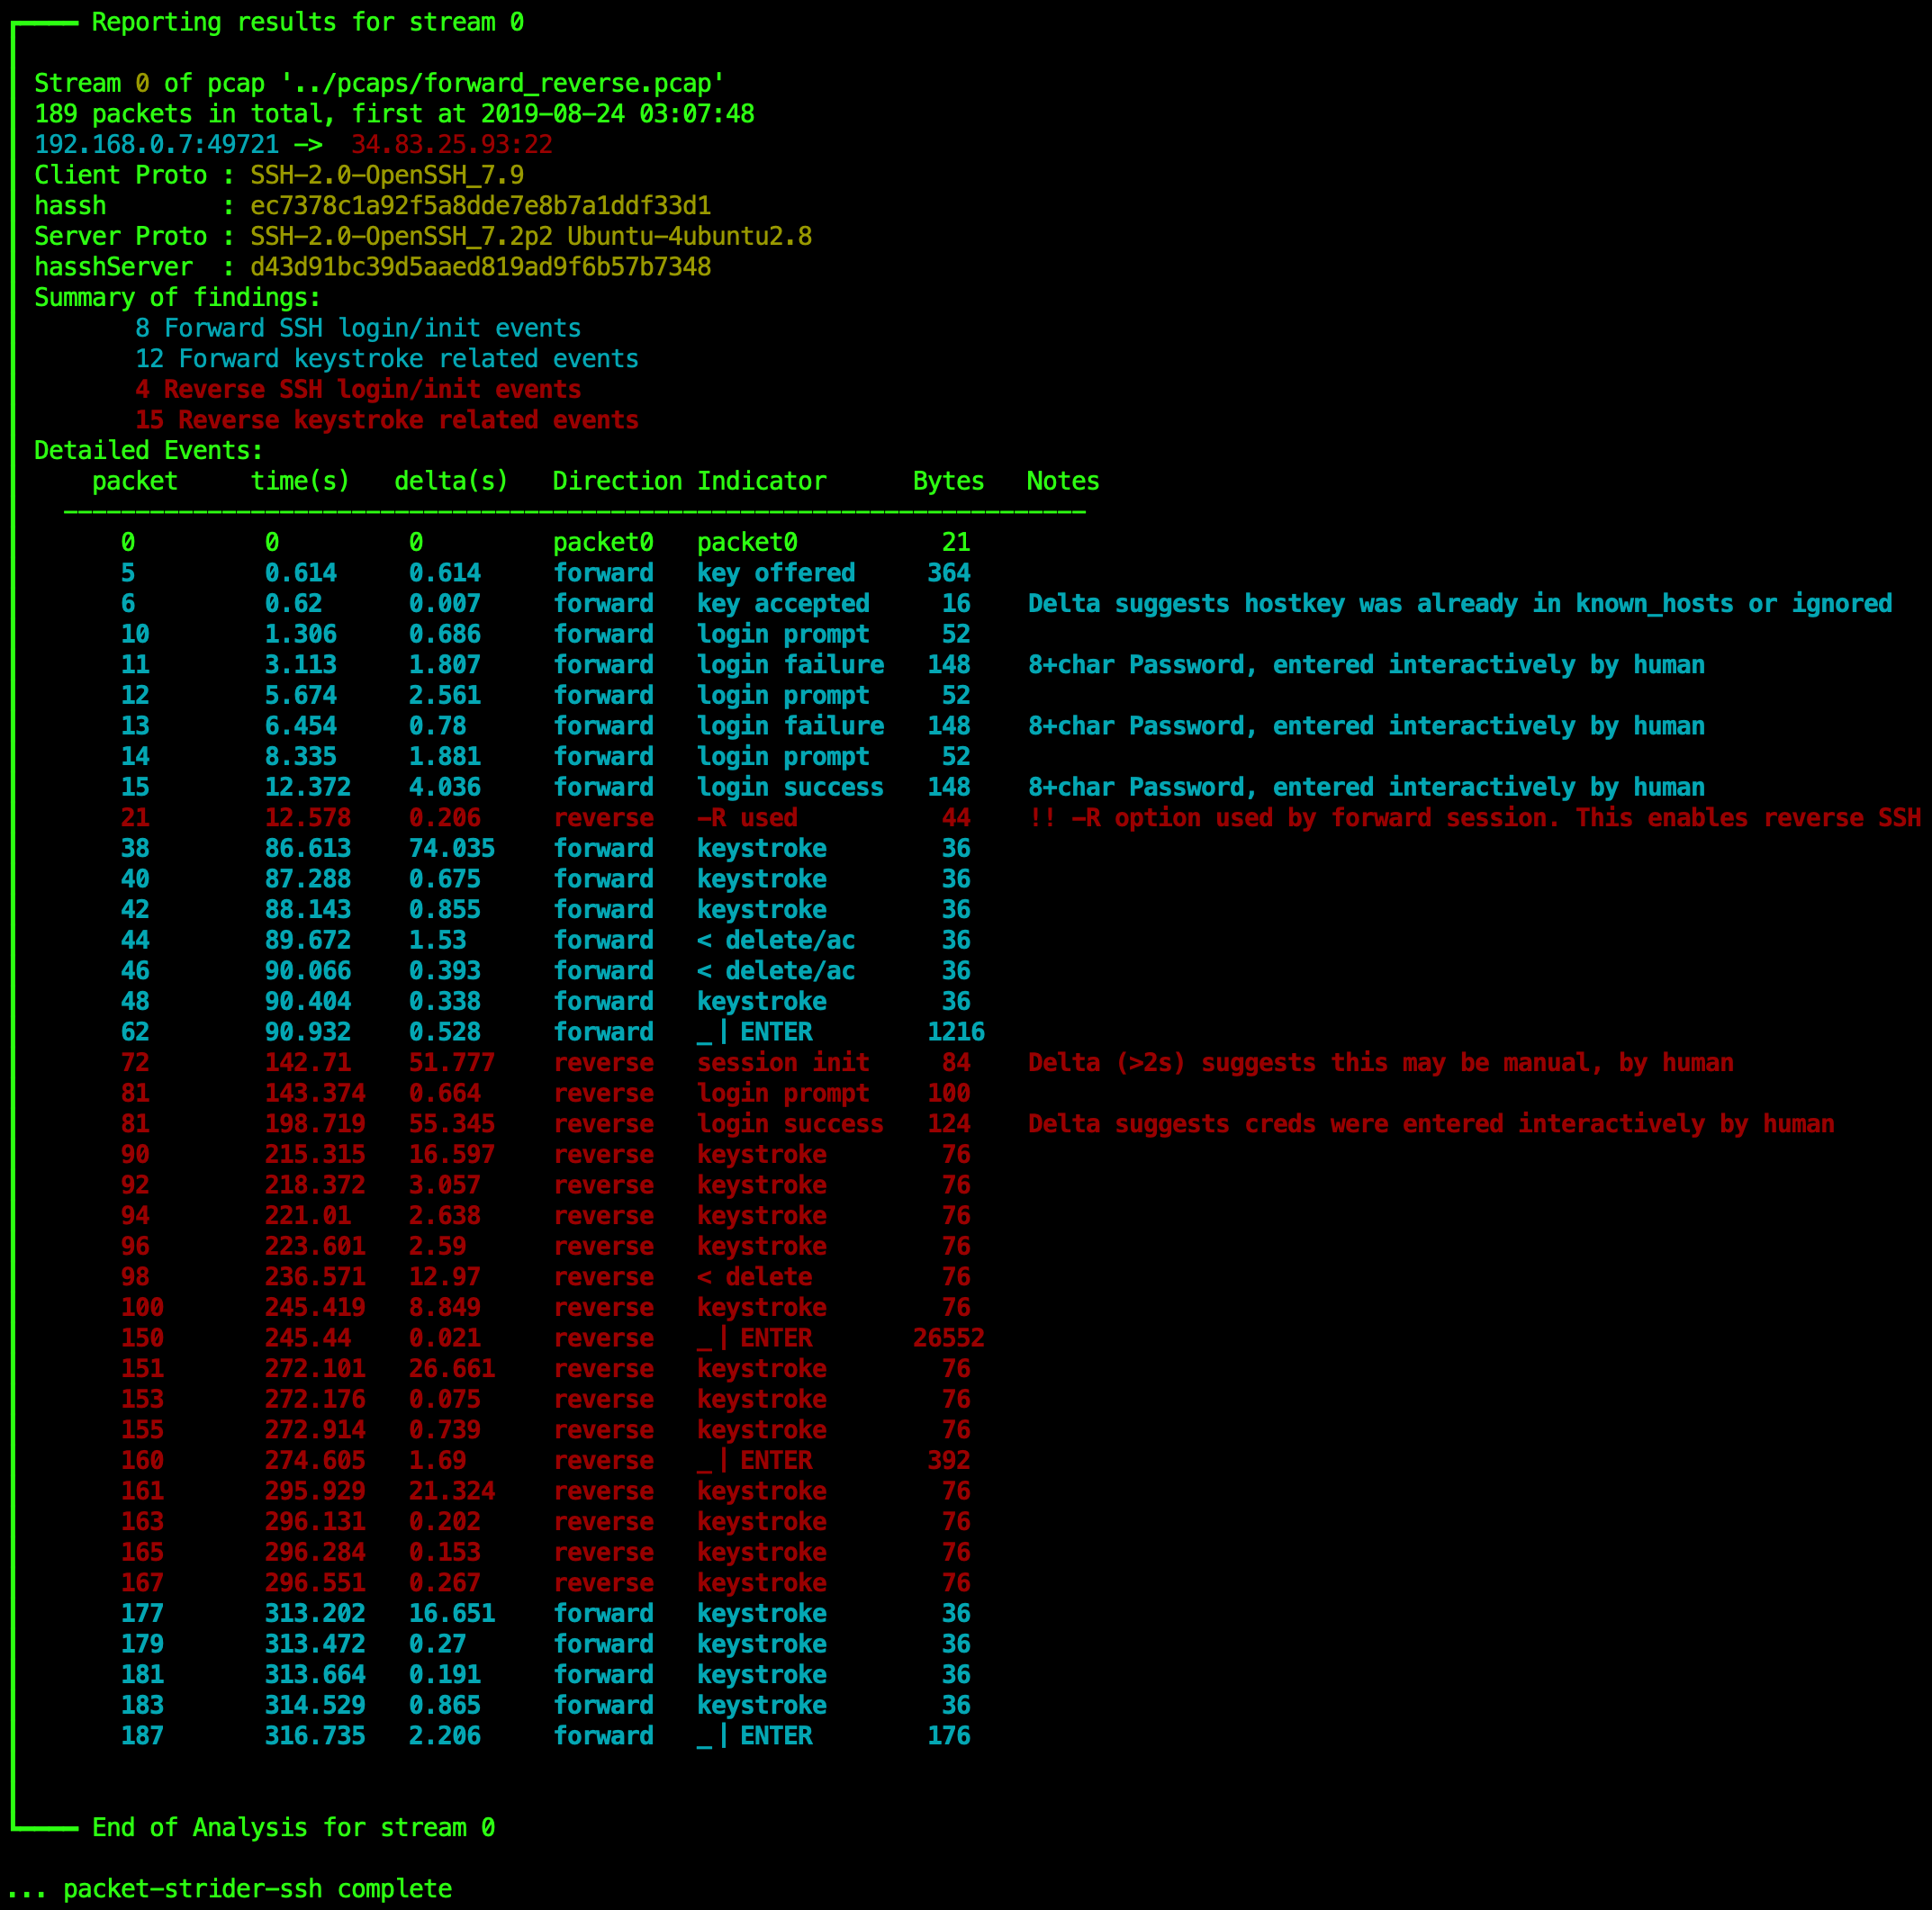
A network packet forensics tool for SSH

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

Small tool to play with IOCs caused by Imageload events

Basic log analysis tool to detect impossible travel via IP address geographic information

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

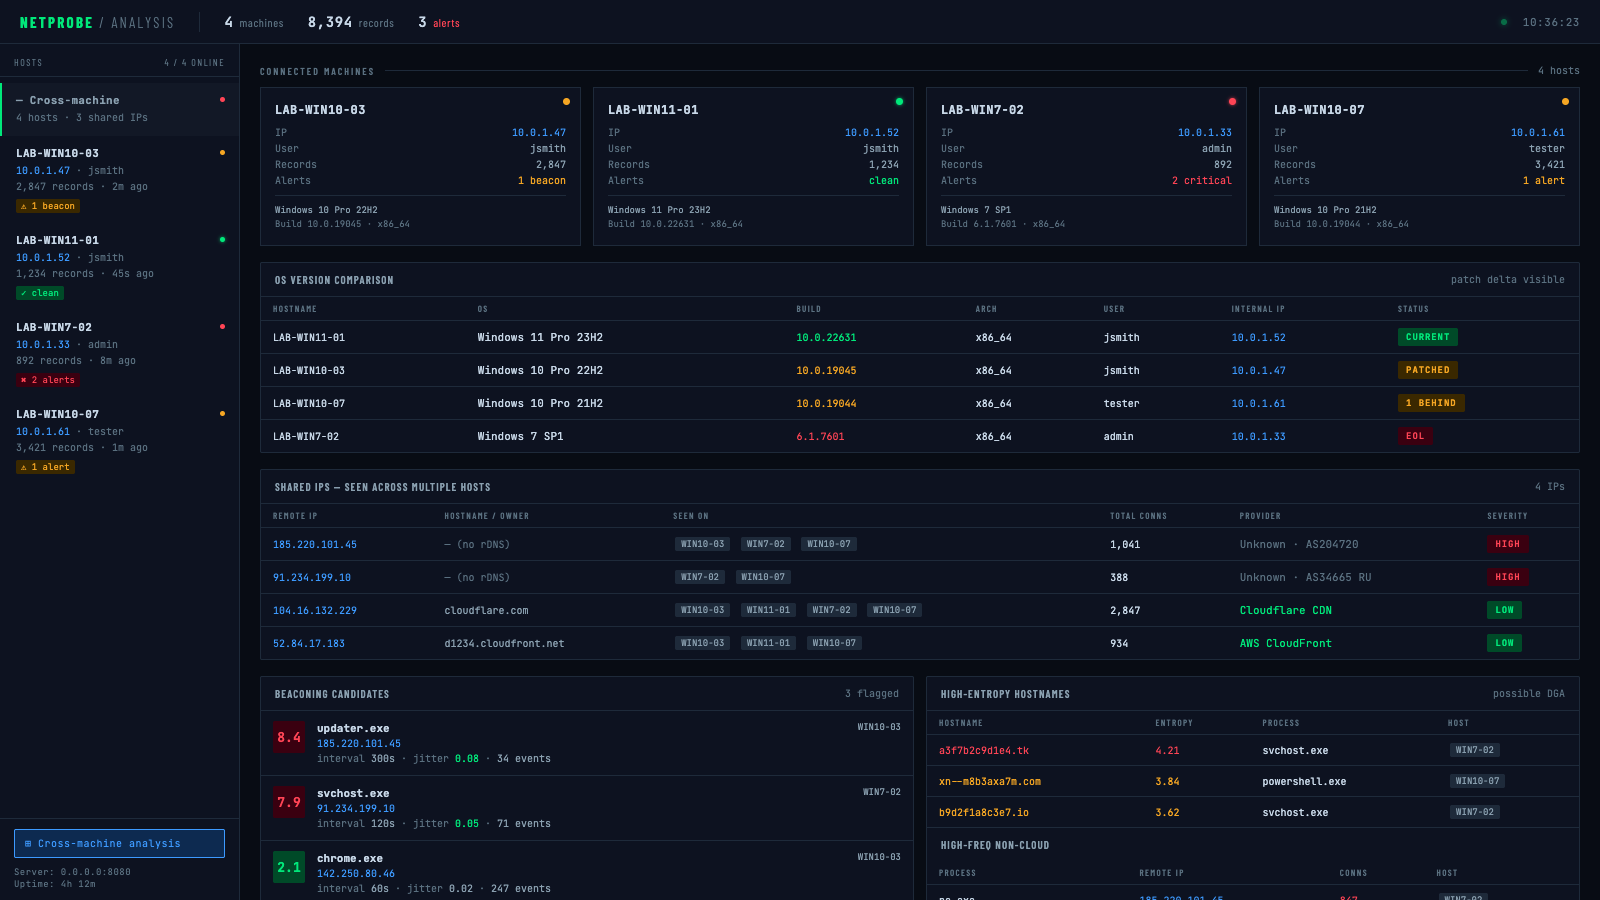
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity

A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.

Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.

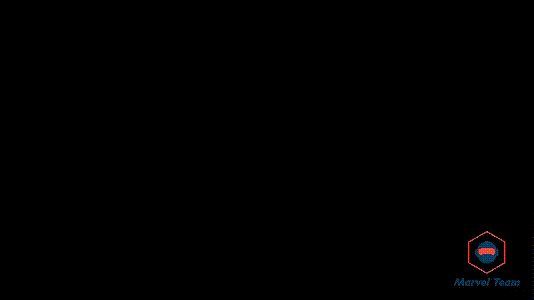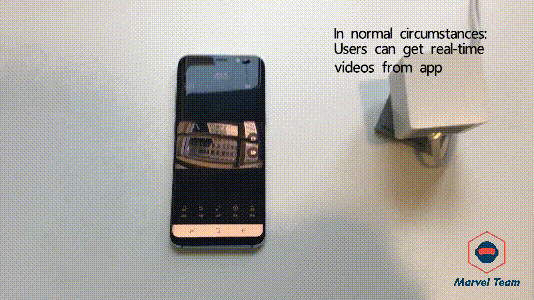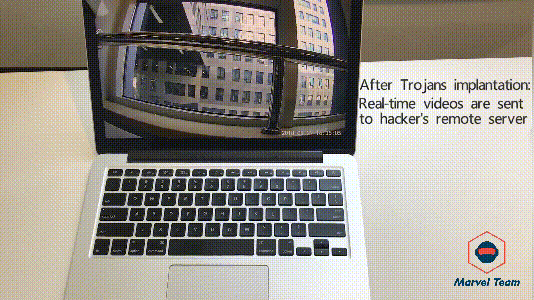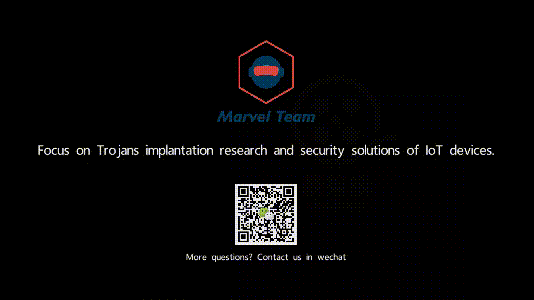
A tool for malicious behavior detection in IoT devices

Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).

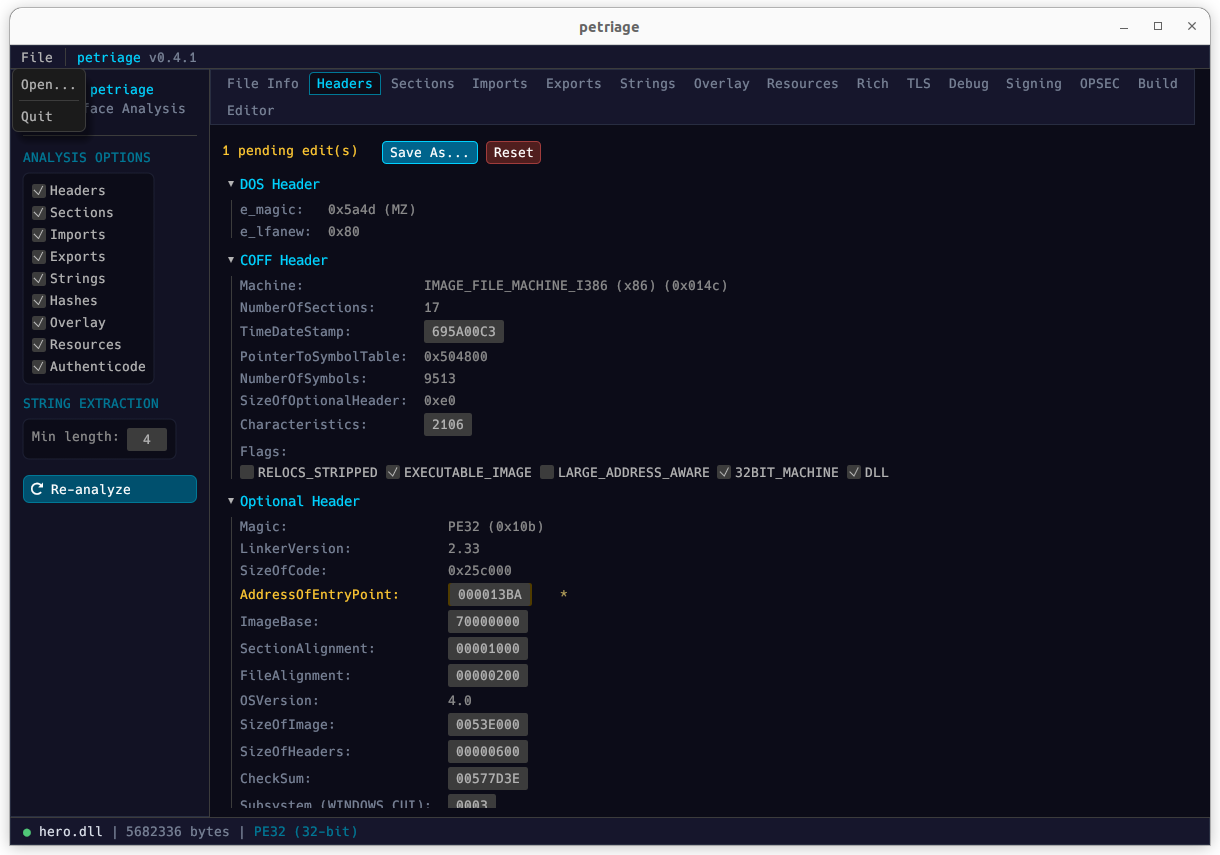
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.

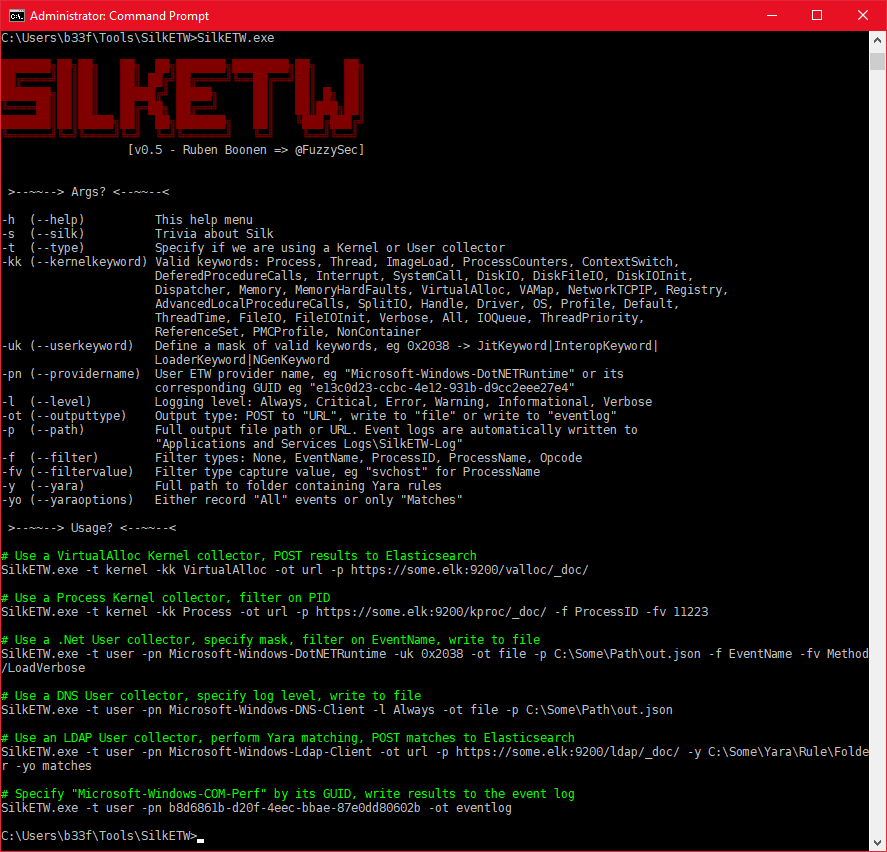
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

ETW based POC to identify direct and indirect syscalls

Detect HTTP stalling attacks like slowloris with Bro

Zeek detection for CVE-2020-16898-"Bad Neighbor"

Real-time anomaly detection system for Apache Struts CVE-2017-5638 exploit using streaming analytics, 3-gram byte analysis, and Count-Min Sketch.…