MemProcFS-Analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…

Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.

Enumerate various traits from Windows processes as an aid to threat hunting

A canary designed to minimize the impact from certain Ransomware actors

Host IDS for desktop users

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection

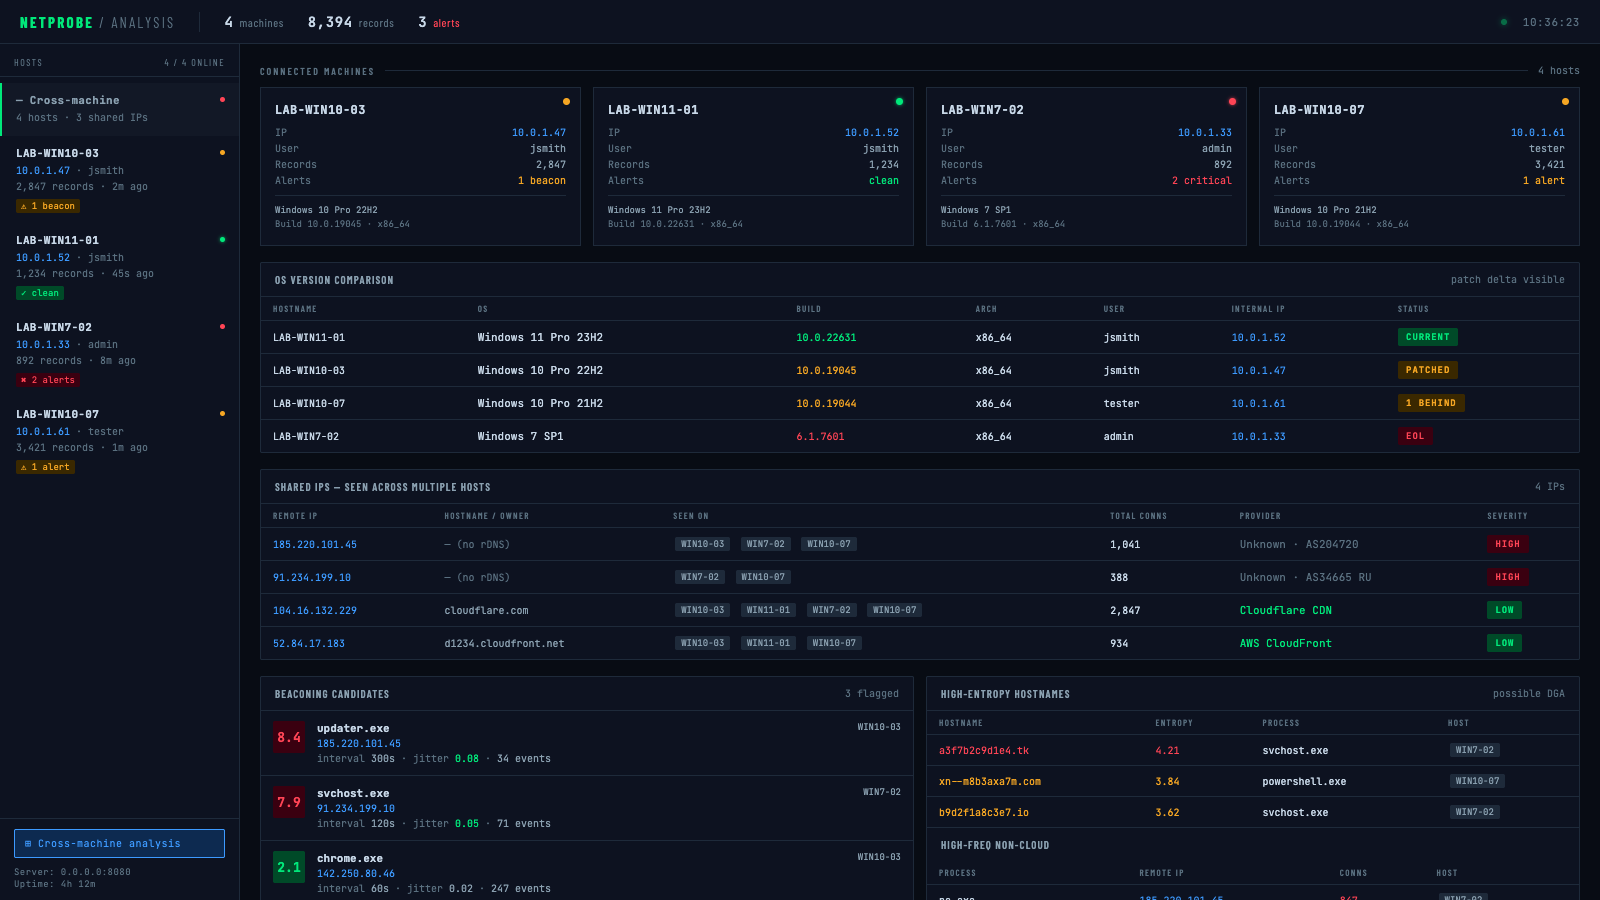
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity