
PortDog
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
anomaly-detectiondefensive-toolsintrusion-detection+3
134
puniaze/portdogNetwork anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
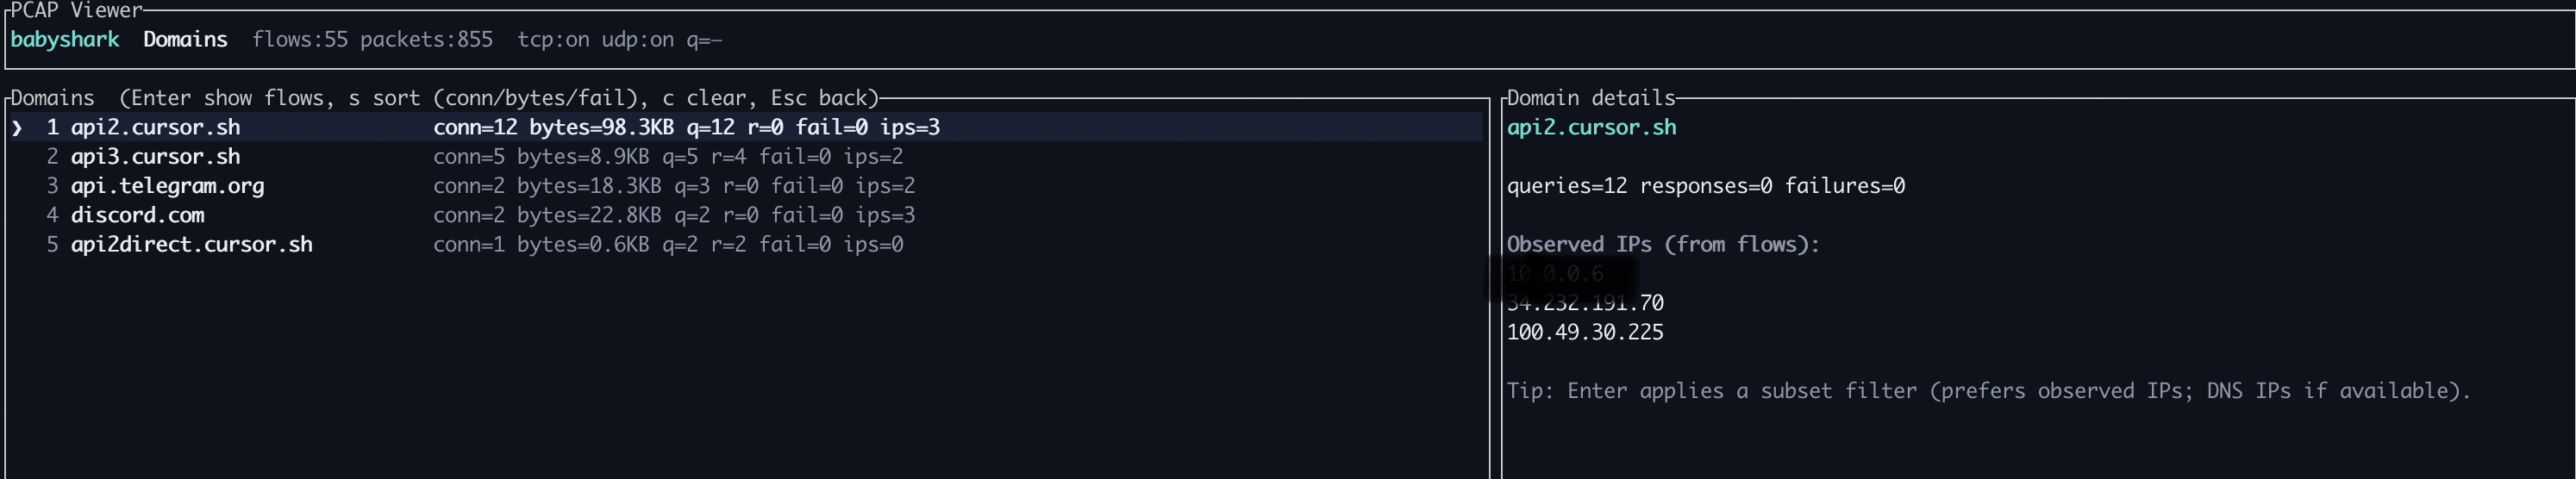 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 jamalrfordii-arch/vanguard-map
3D multi-domain tactical intelligence map — live ships, flights, satellites, cables & space weather in the browser. Time scrubbing, scenario replay,…
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
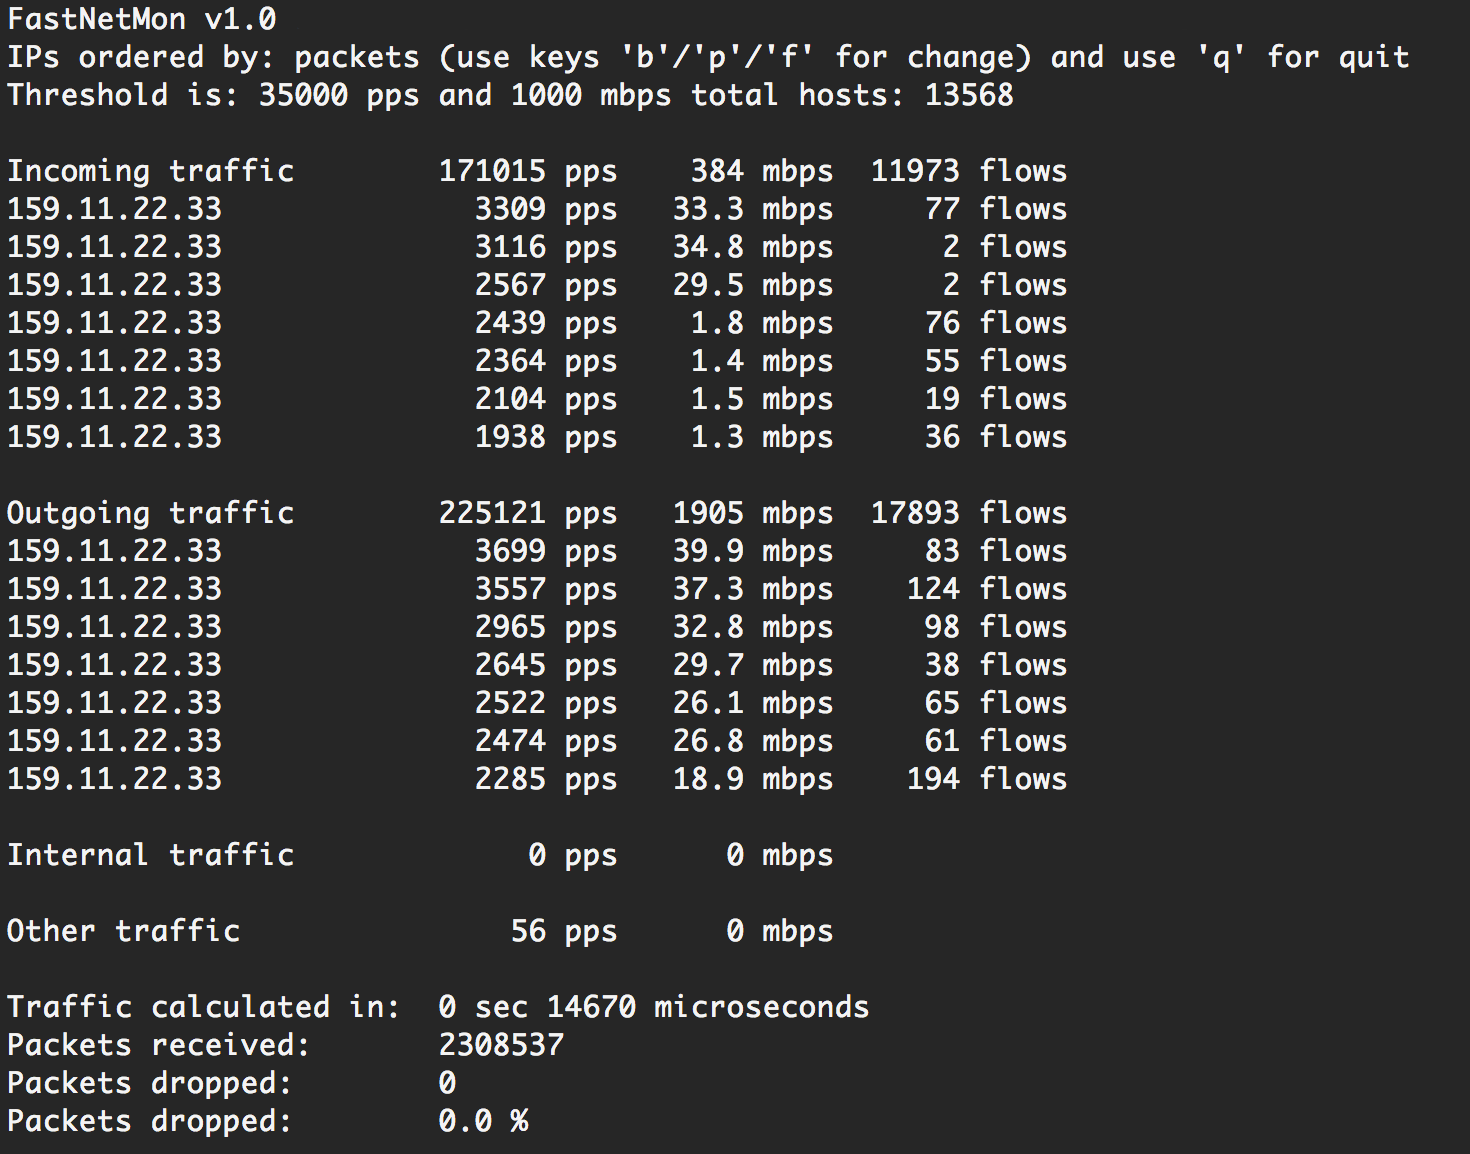 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
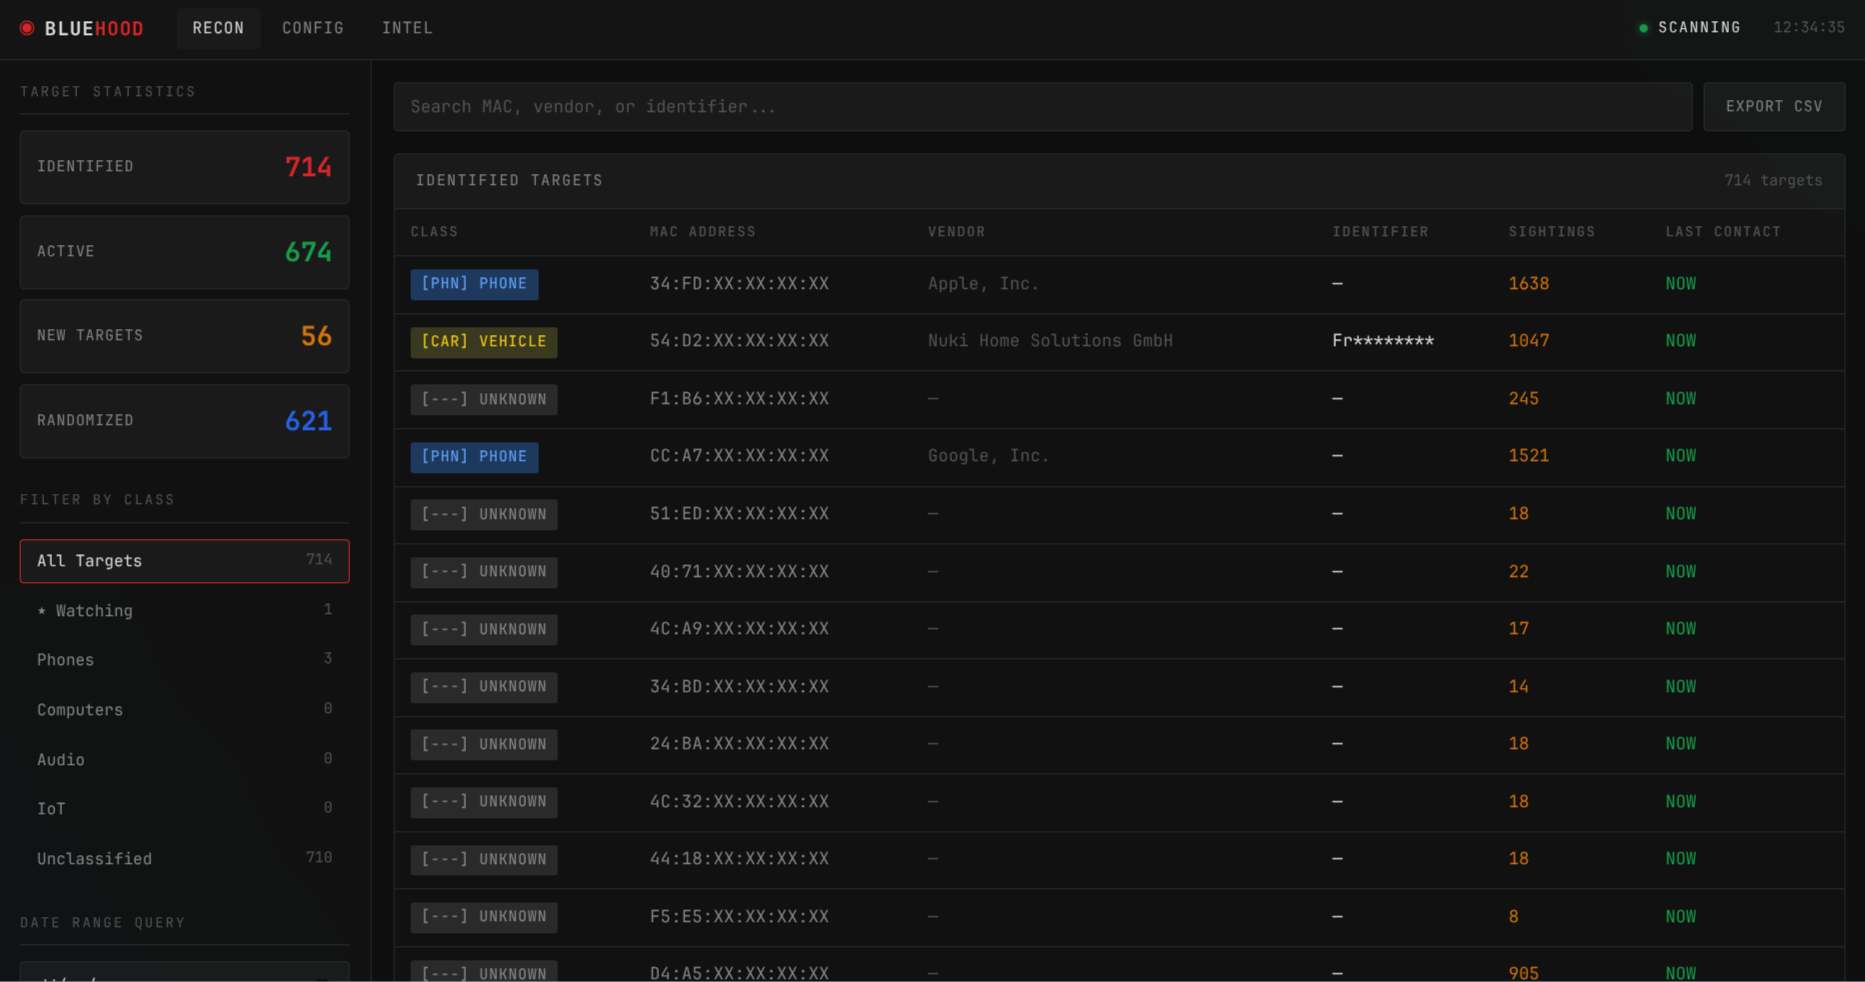 dannymcc/bluehood
Monitor your local neighbourhood's bluetooth activity

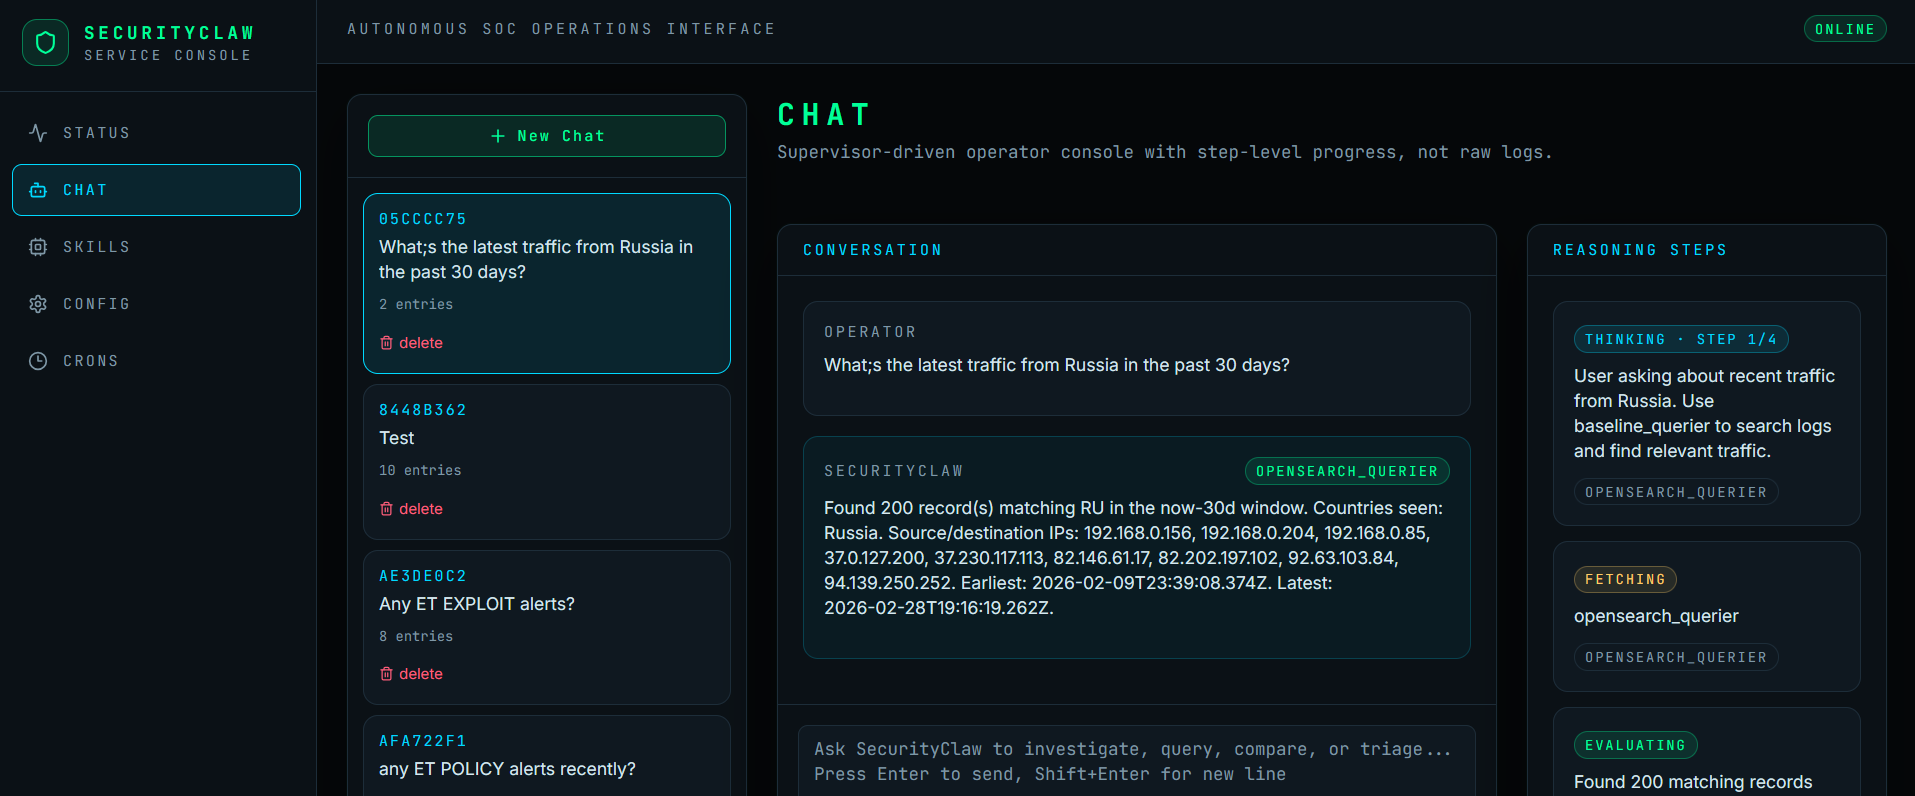 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 delvelabs/batea
AI-based, context-driven network device ranking