

NetScope
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
3
spectralzero/netscopeOffline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
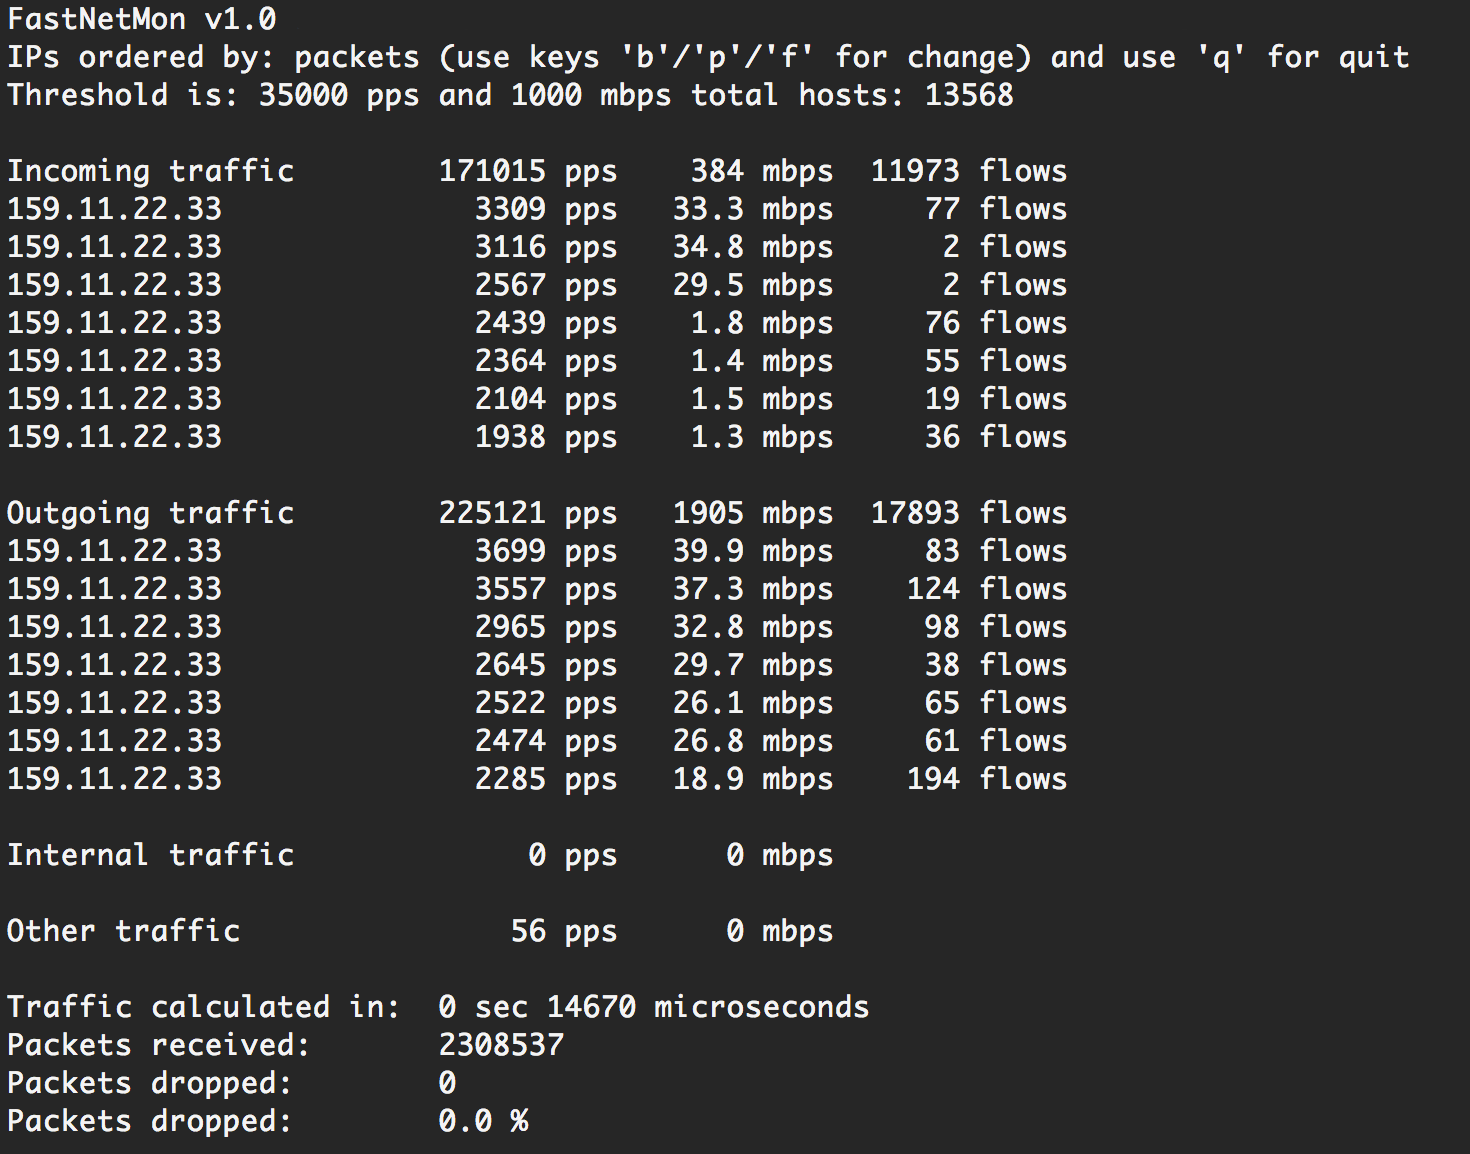 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
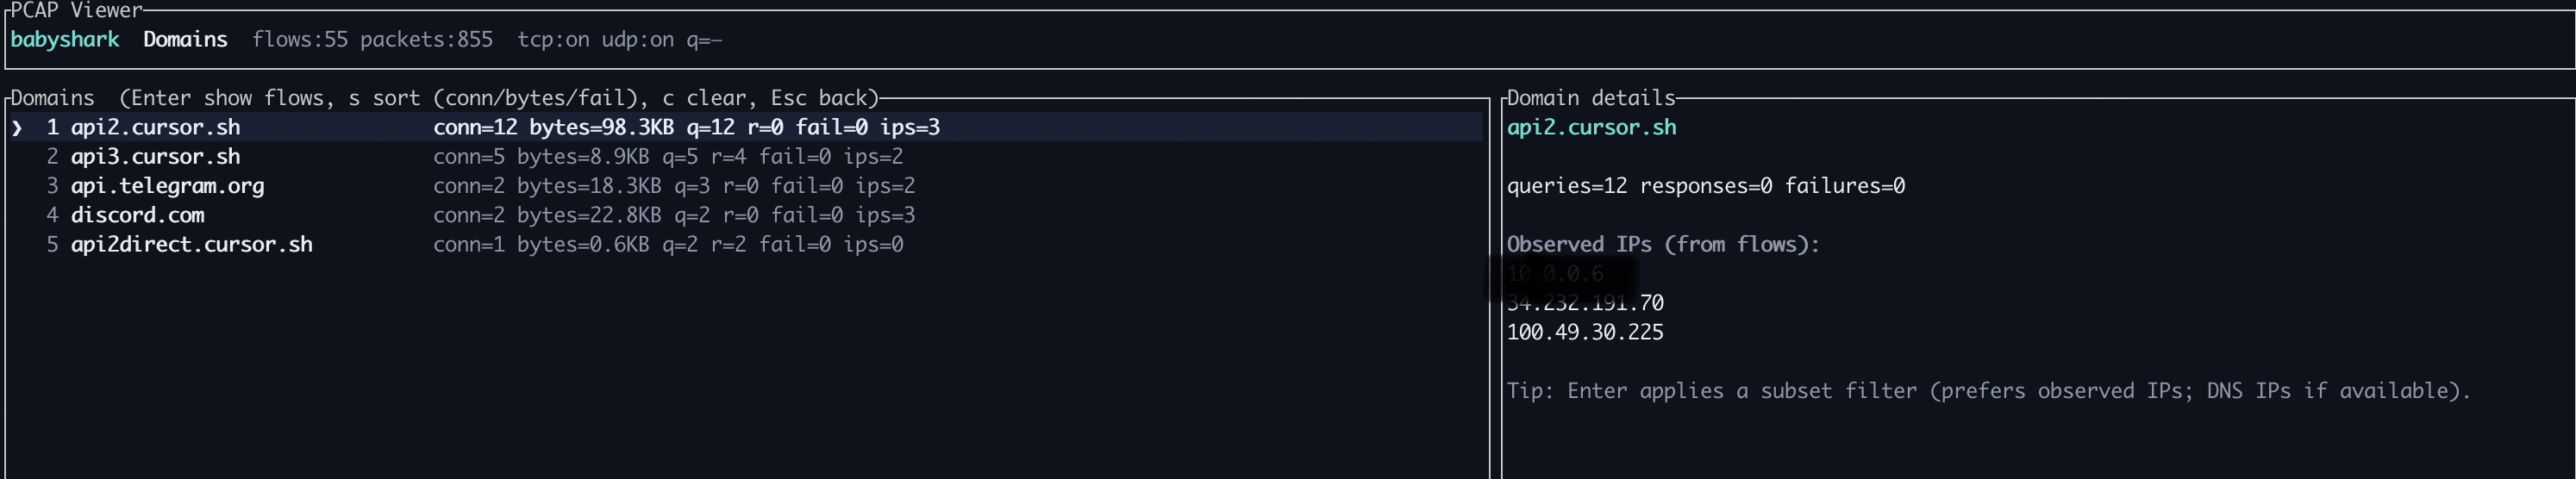 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
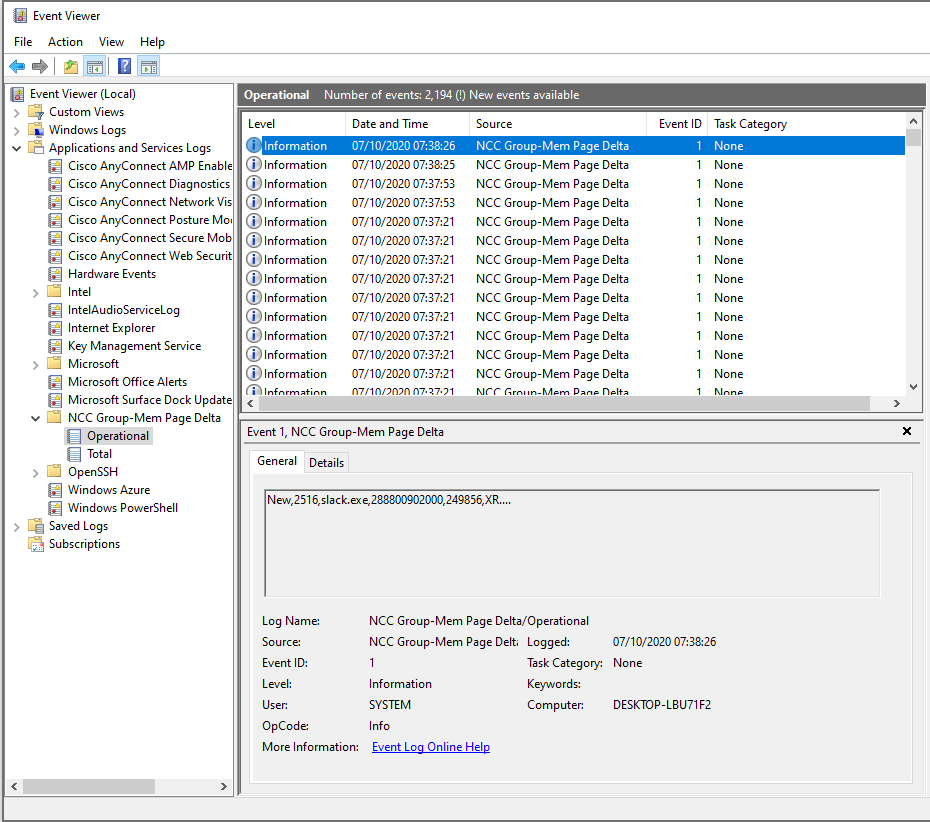 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 corelight/conn-burst
A Bro package to identify connections that are bursting (lots of data and transferring quickly).
 corelight/zeek-endpoint-enrichment-conn
Enrich the conn.log with EDR data
 shoucheng3/graylog2__graylog2-server_cve-2023-41044_5-1-2
Open source log management platform for centralized log aggregation, real-time analysis, and security event monitoring with customizable dashboards…
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…