
SyntheticSun
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
anomaly-detectioncloud-securityincident-response+3
82
jonrau1/syntheticsunServerless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
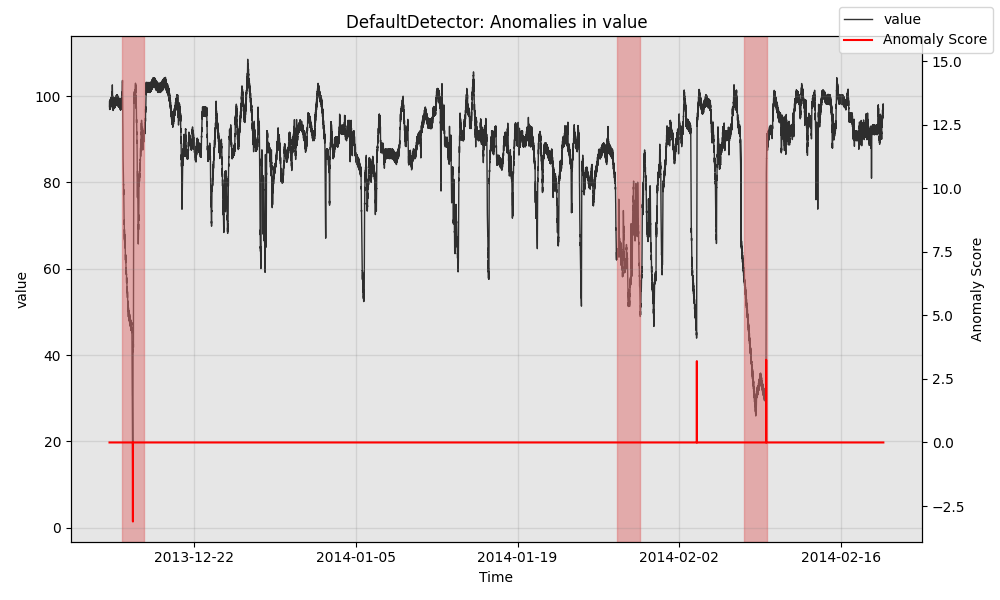 salesforce/merlion
End-to-end Python framework for time series intelligence, offering anomaly detection, forecasting, change point detection, AutoML, ensembles, and…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 gmh5225/maldec-edr
Unix endpoint detection and response solution using kernel-level mechanisms to detect anomalies and malware attacks in real time.
 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
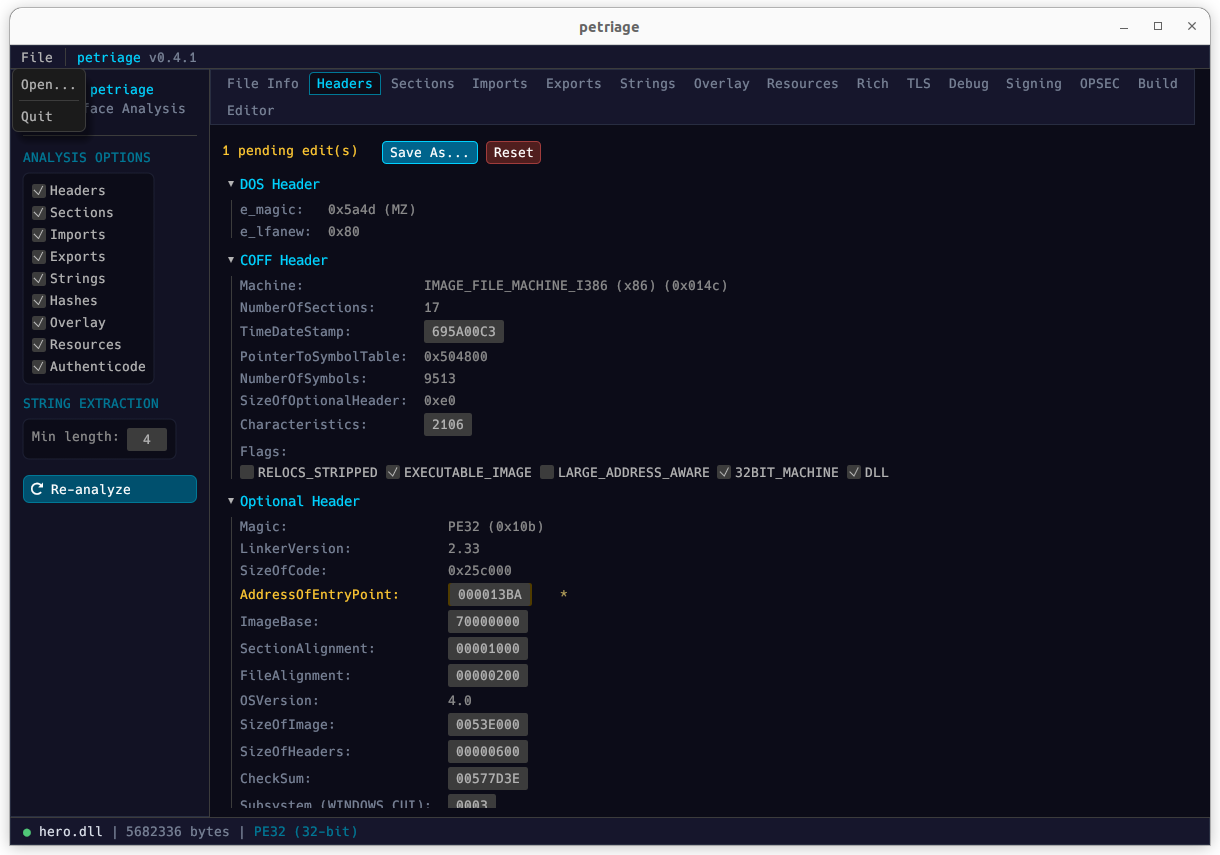 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat
 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…