
columbo
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
anomaly-detectionbinary-analysisdigital-forensics+3
61
visma-prodsec/columboML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
 salesforce/hassh
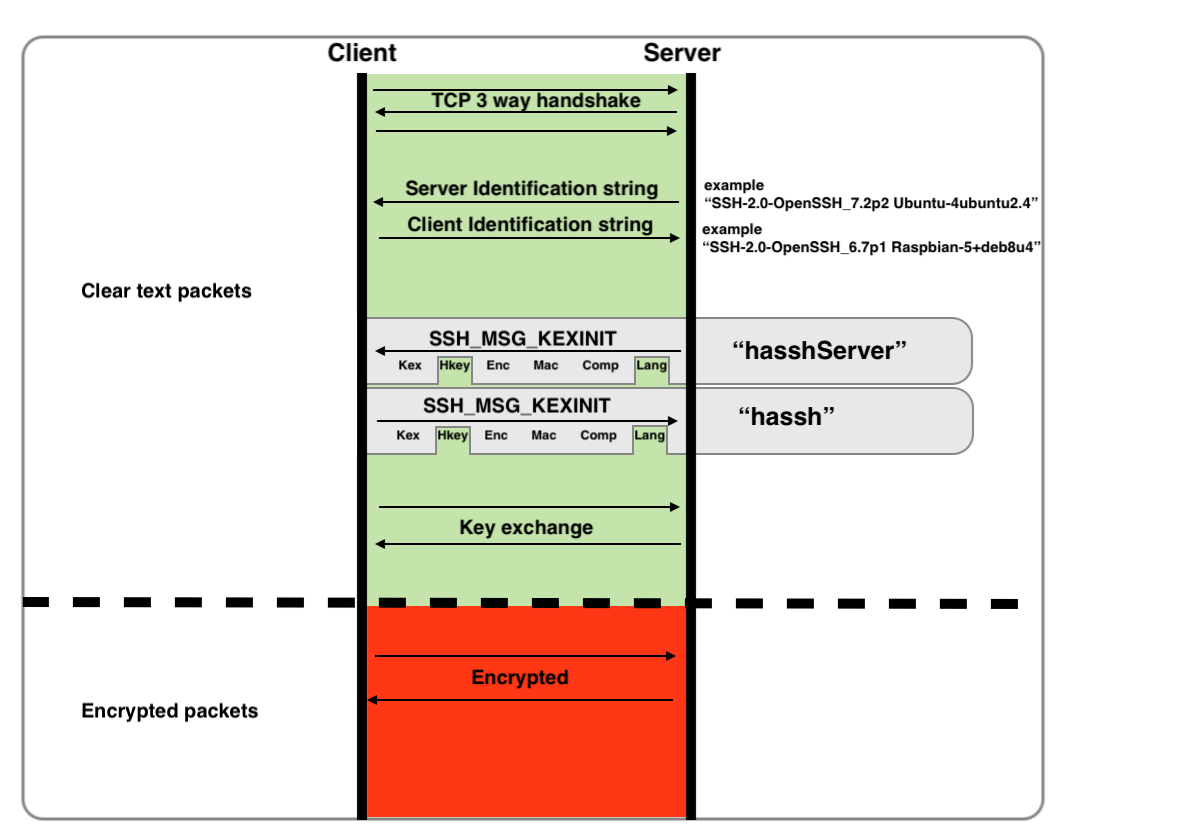
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
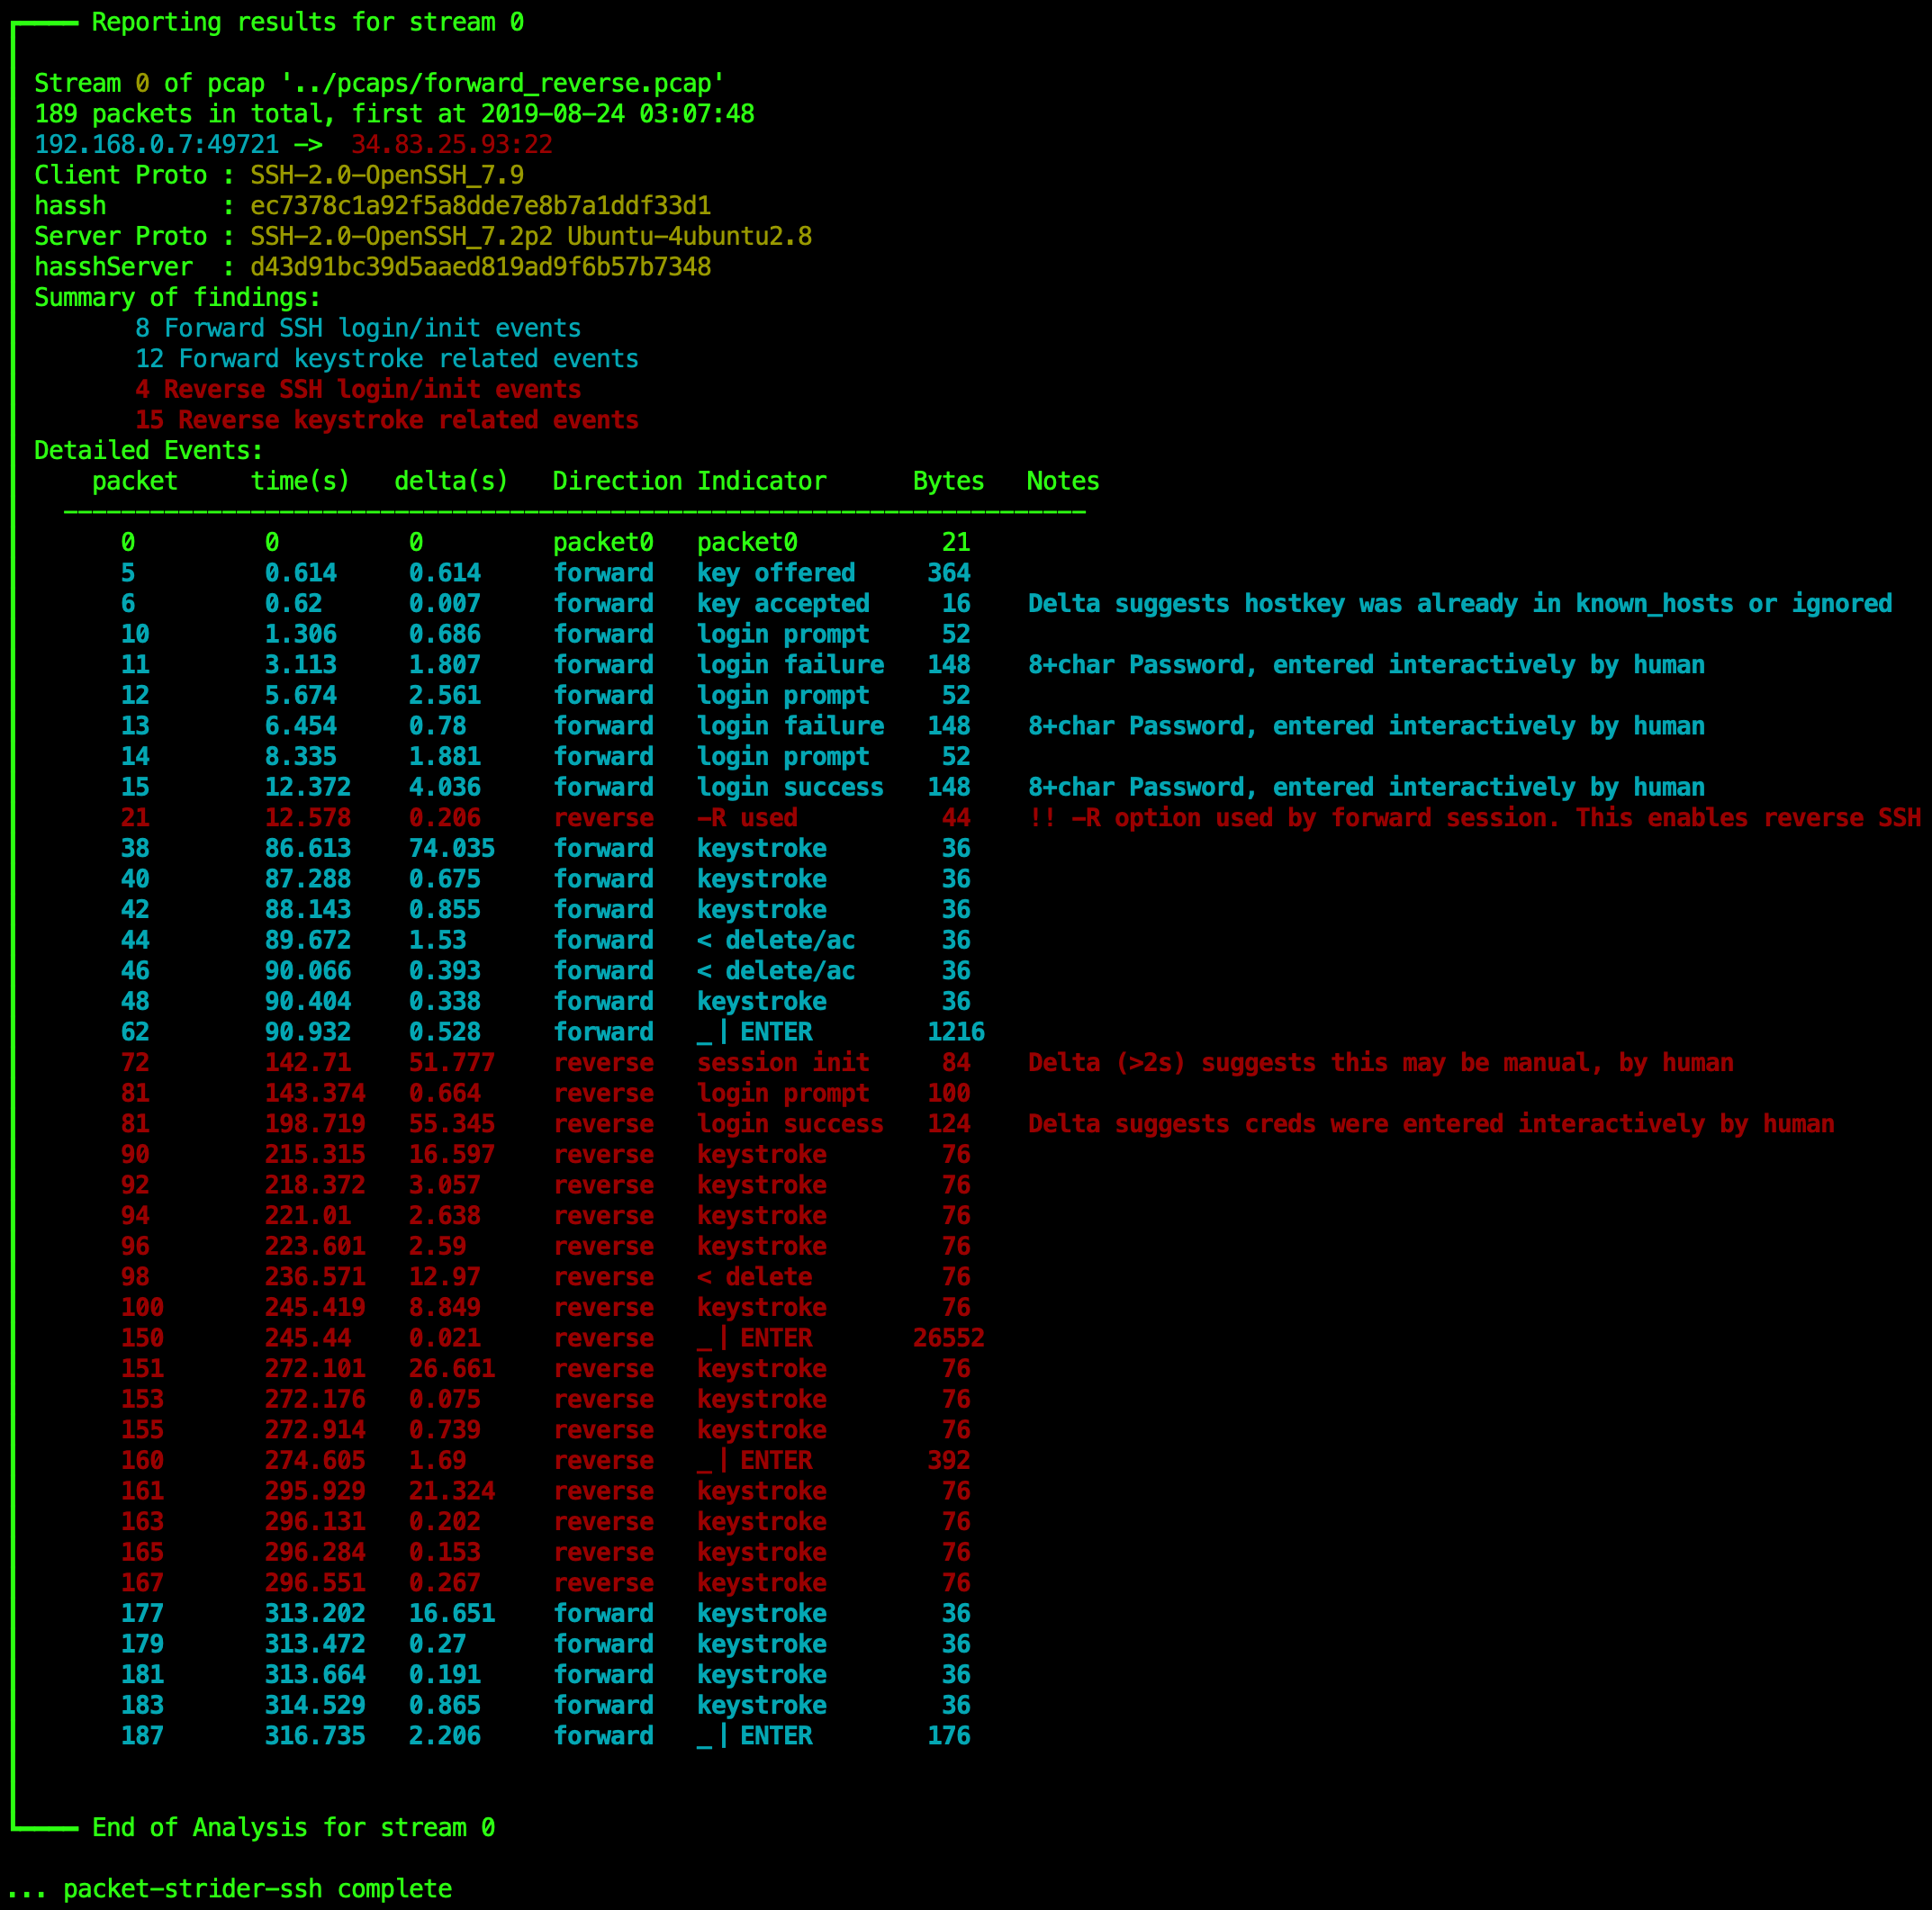 benjeems/packetstrider
A network packet forensics tool for SSH
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 corelight/zeek-xor-exe-plugin
Zeek plugin to detect and decrypt XOR-encrypted EXEs
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
 liuz233/harde
Research code for HARDE, an agent harness that probes and adaptively optimizes components for runtime risk detection and execution control across…
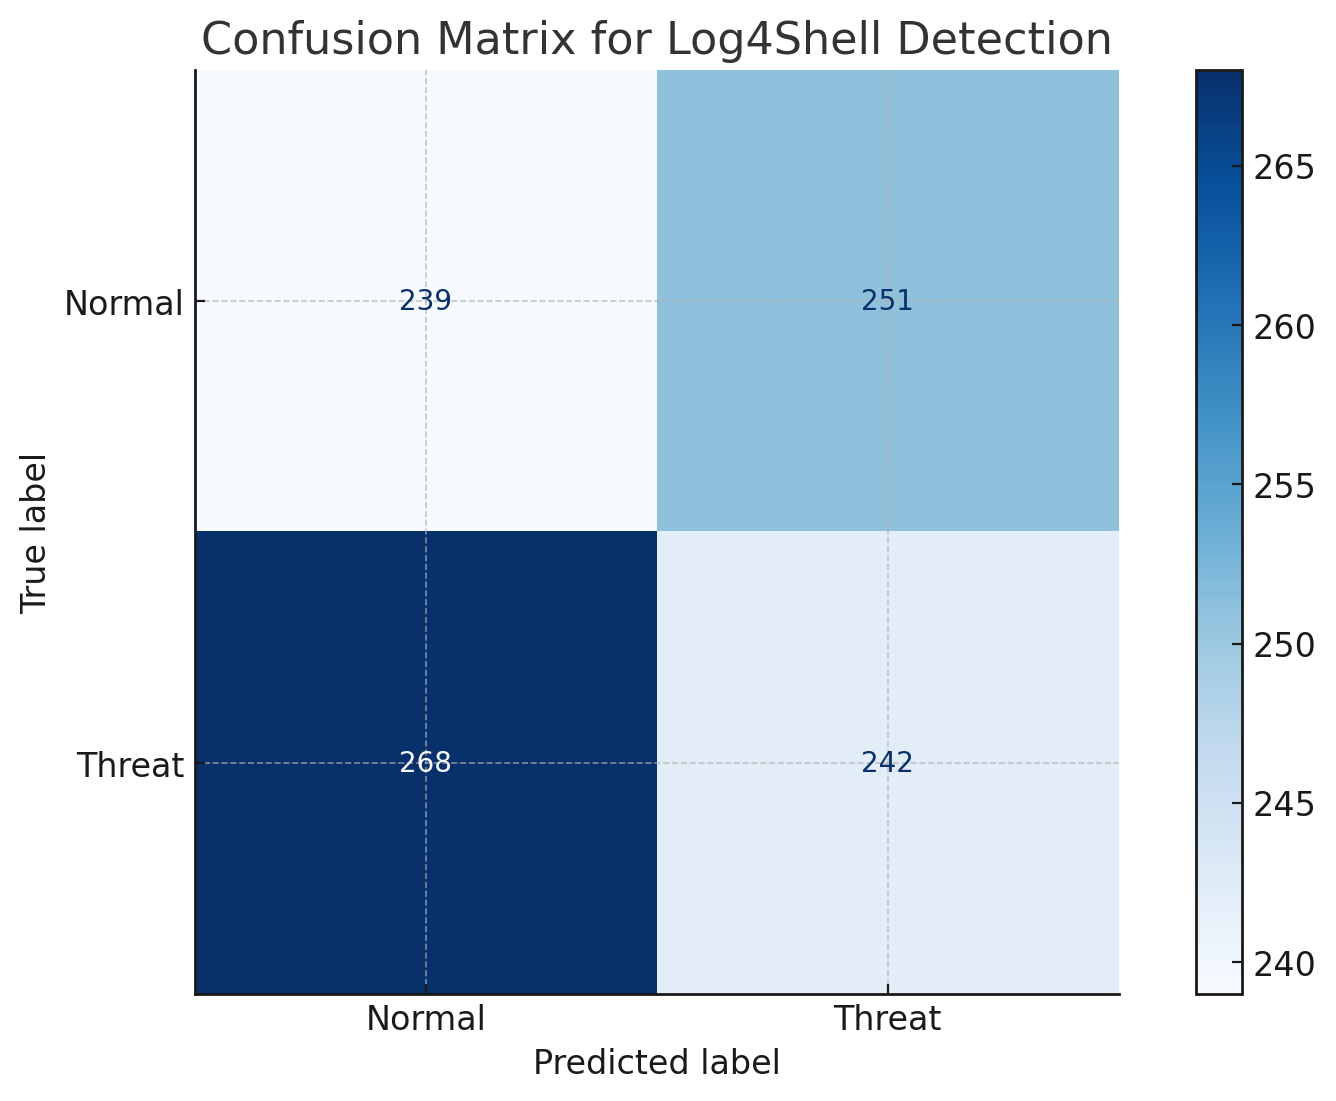 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…

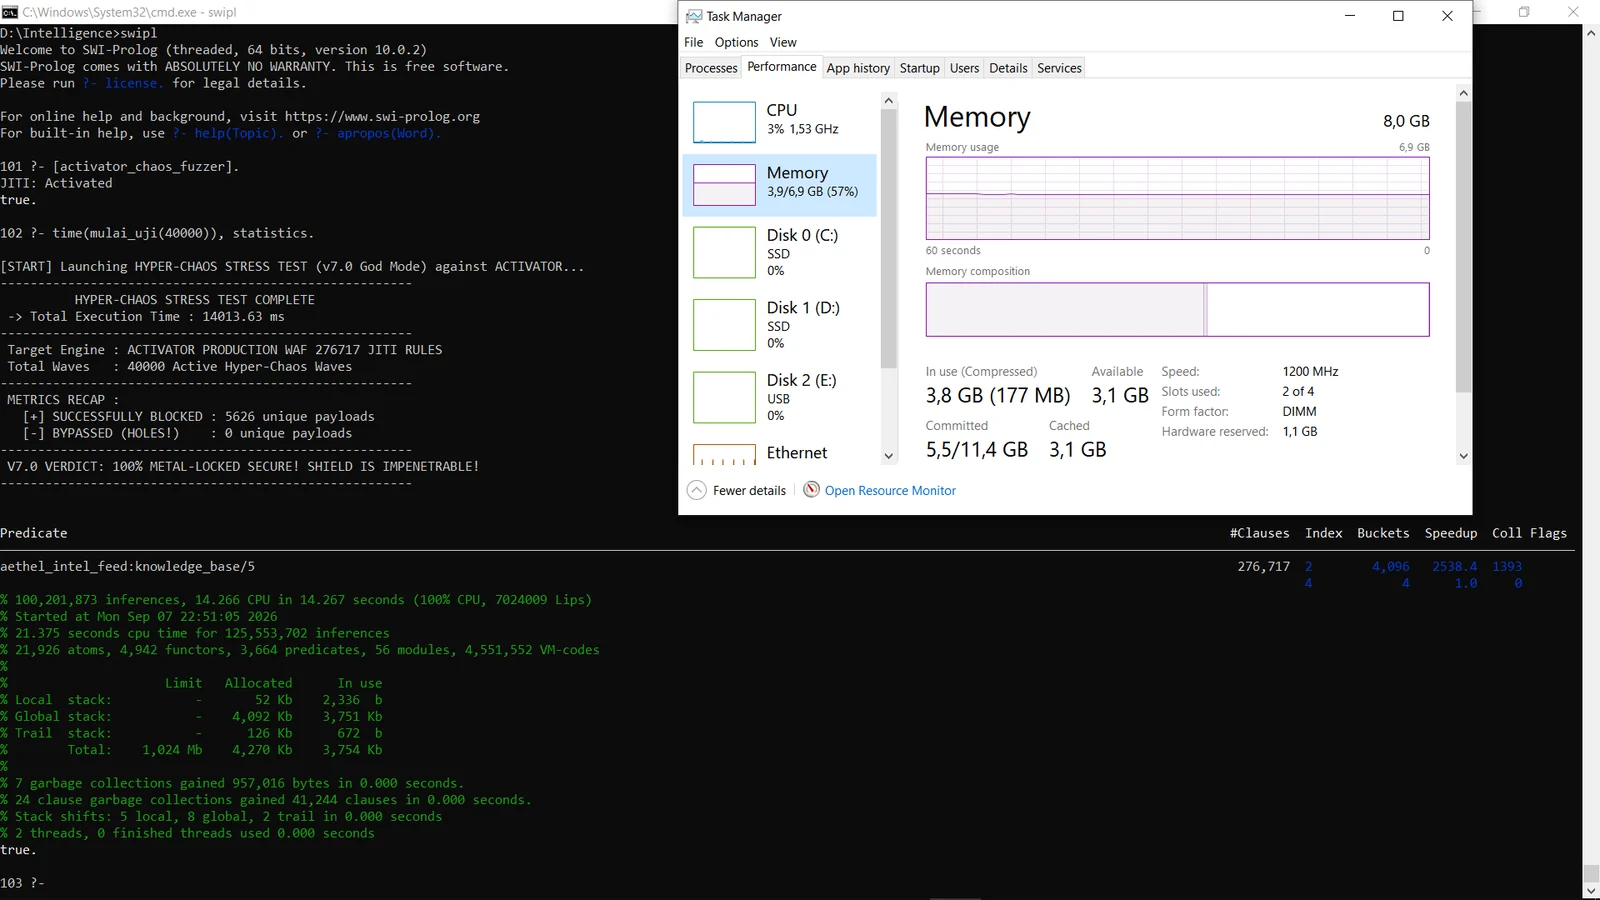 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 arthastang/iot-home-guard
A tool for malicious behavior detection in IoT devices
 thegamestopsnow/power-tracks-research
Research related to the Power Tracks discovered in market microstructure.
 shuangliangx/learning-to-detect
Detects unknown jailbreak attacks in large vision-language models using hidden state analysis and autoencoders, with training and evaluation…