
KOOBE-Guard
 vedantk6403/koobe-guard
Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
anomaly-detectiondefensive-toolsintrusion-detection+1
vedantk6403/koobe-guardLinux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
 shuangliangx/learning-to-detect
Detects unknown jailbreak attacks in large vision-language models using hidden state analysis and autoencoders, with training and evaluation…
 artur-augustyniak/class_struggle
Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
 corelight/petitpotam
Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.
 reyjesusq/sentinel-mcp
Autonomous AI-powered cyber defense system using MCP, Gemini 2.0 Flash, Dynatrace observability and MongoDB. Google Cloud Hackathon submission.
 yumlembam/insider-threat
Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…
 jazbengu/threatdetect
Streamlit-based insider threat detection prototype using XGBoost and Isolation Forest to analyze employee activity data, generate risk summaries, and…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
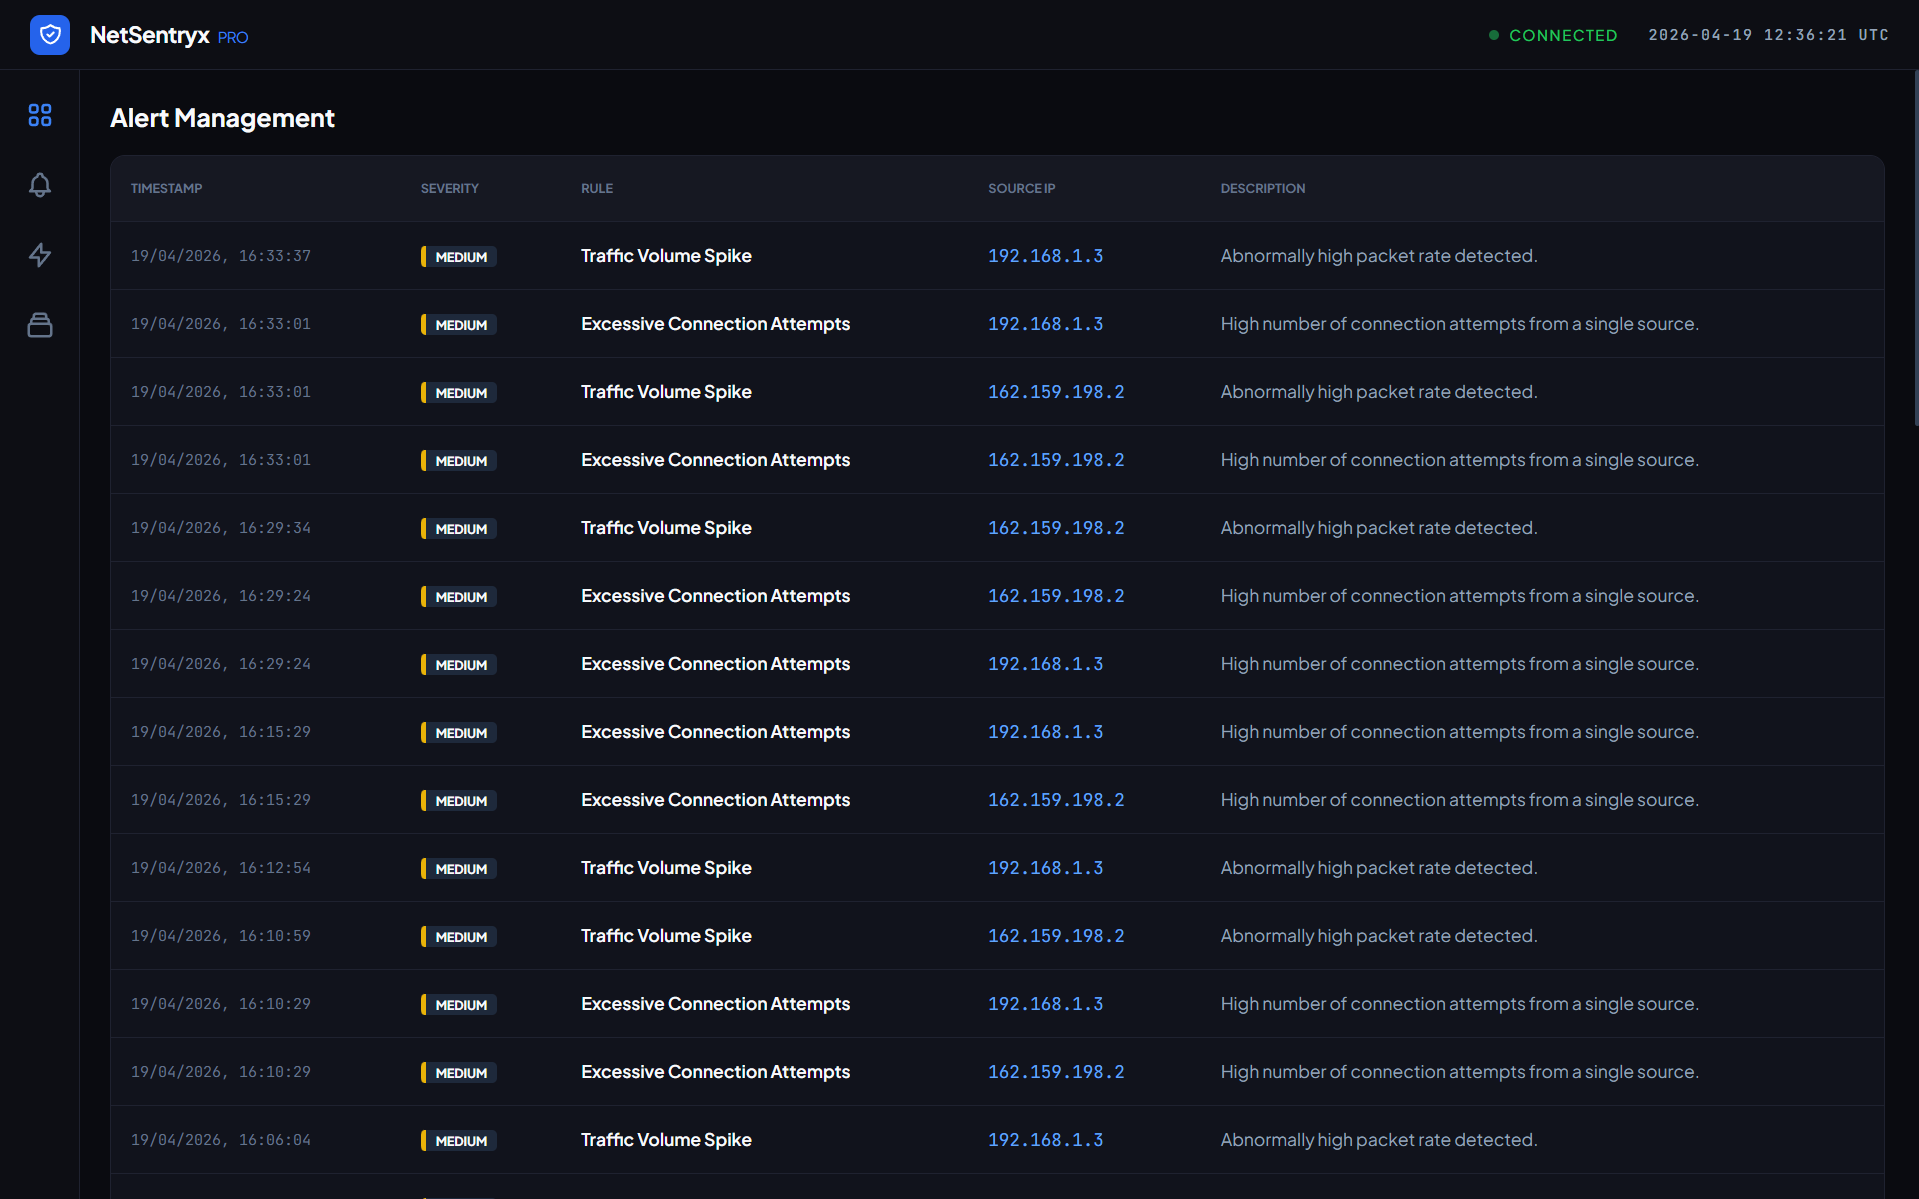 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
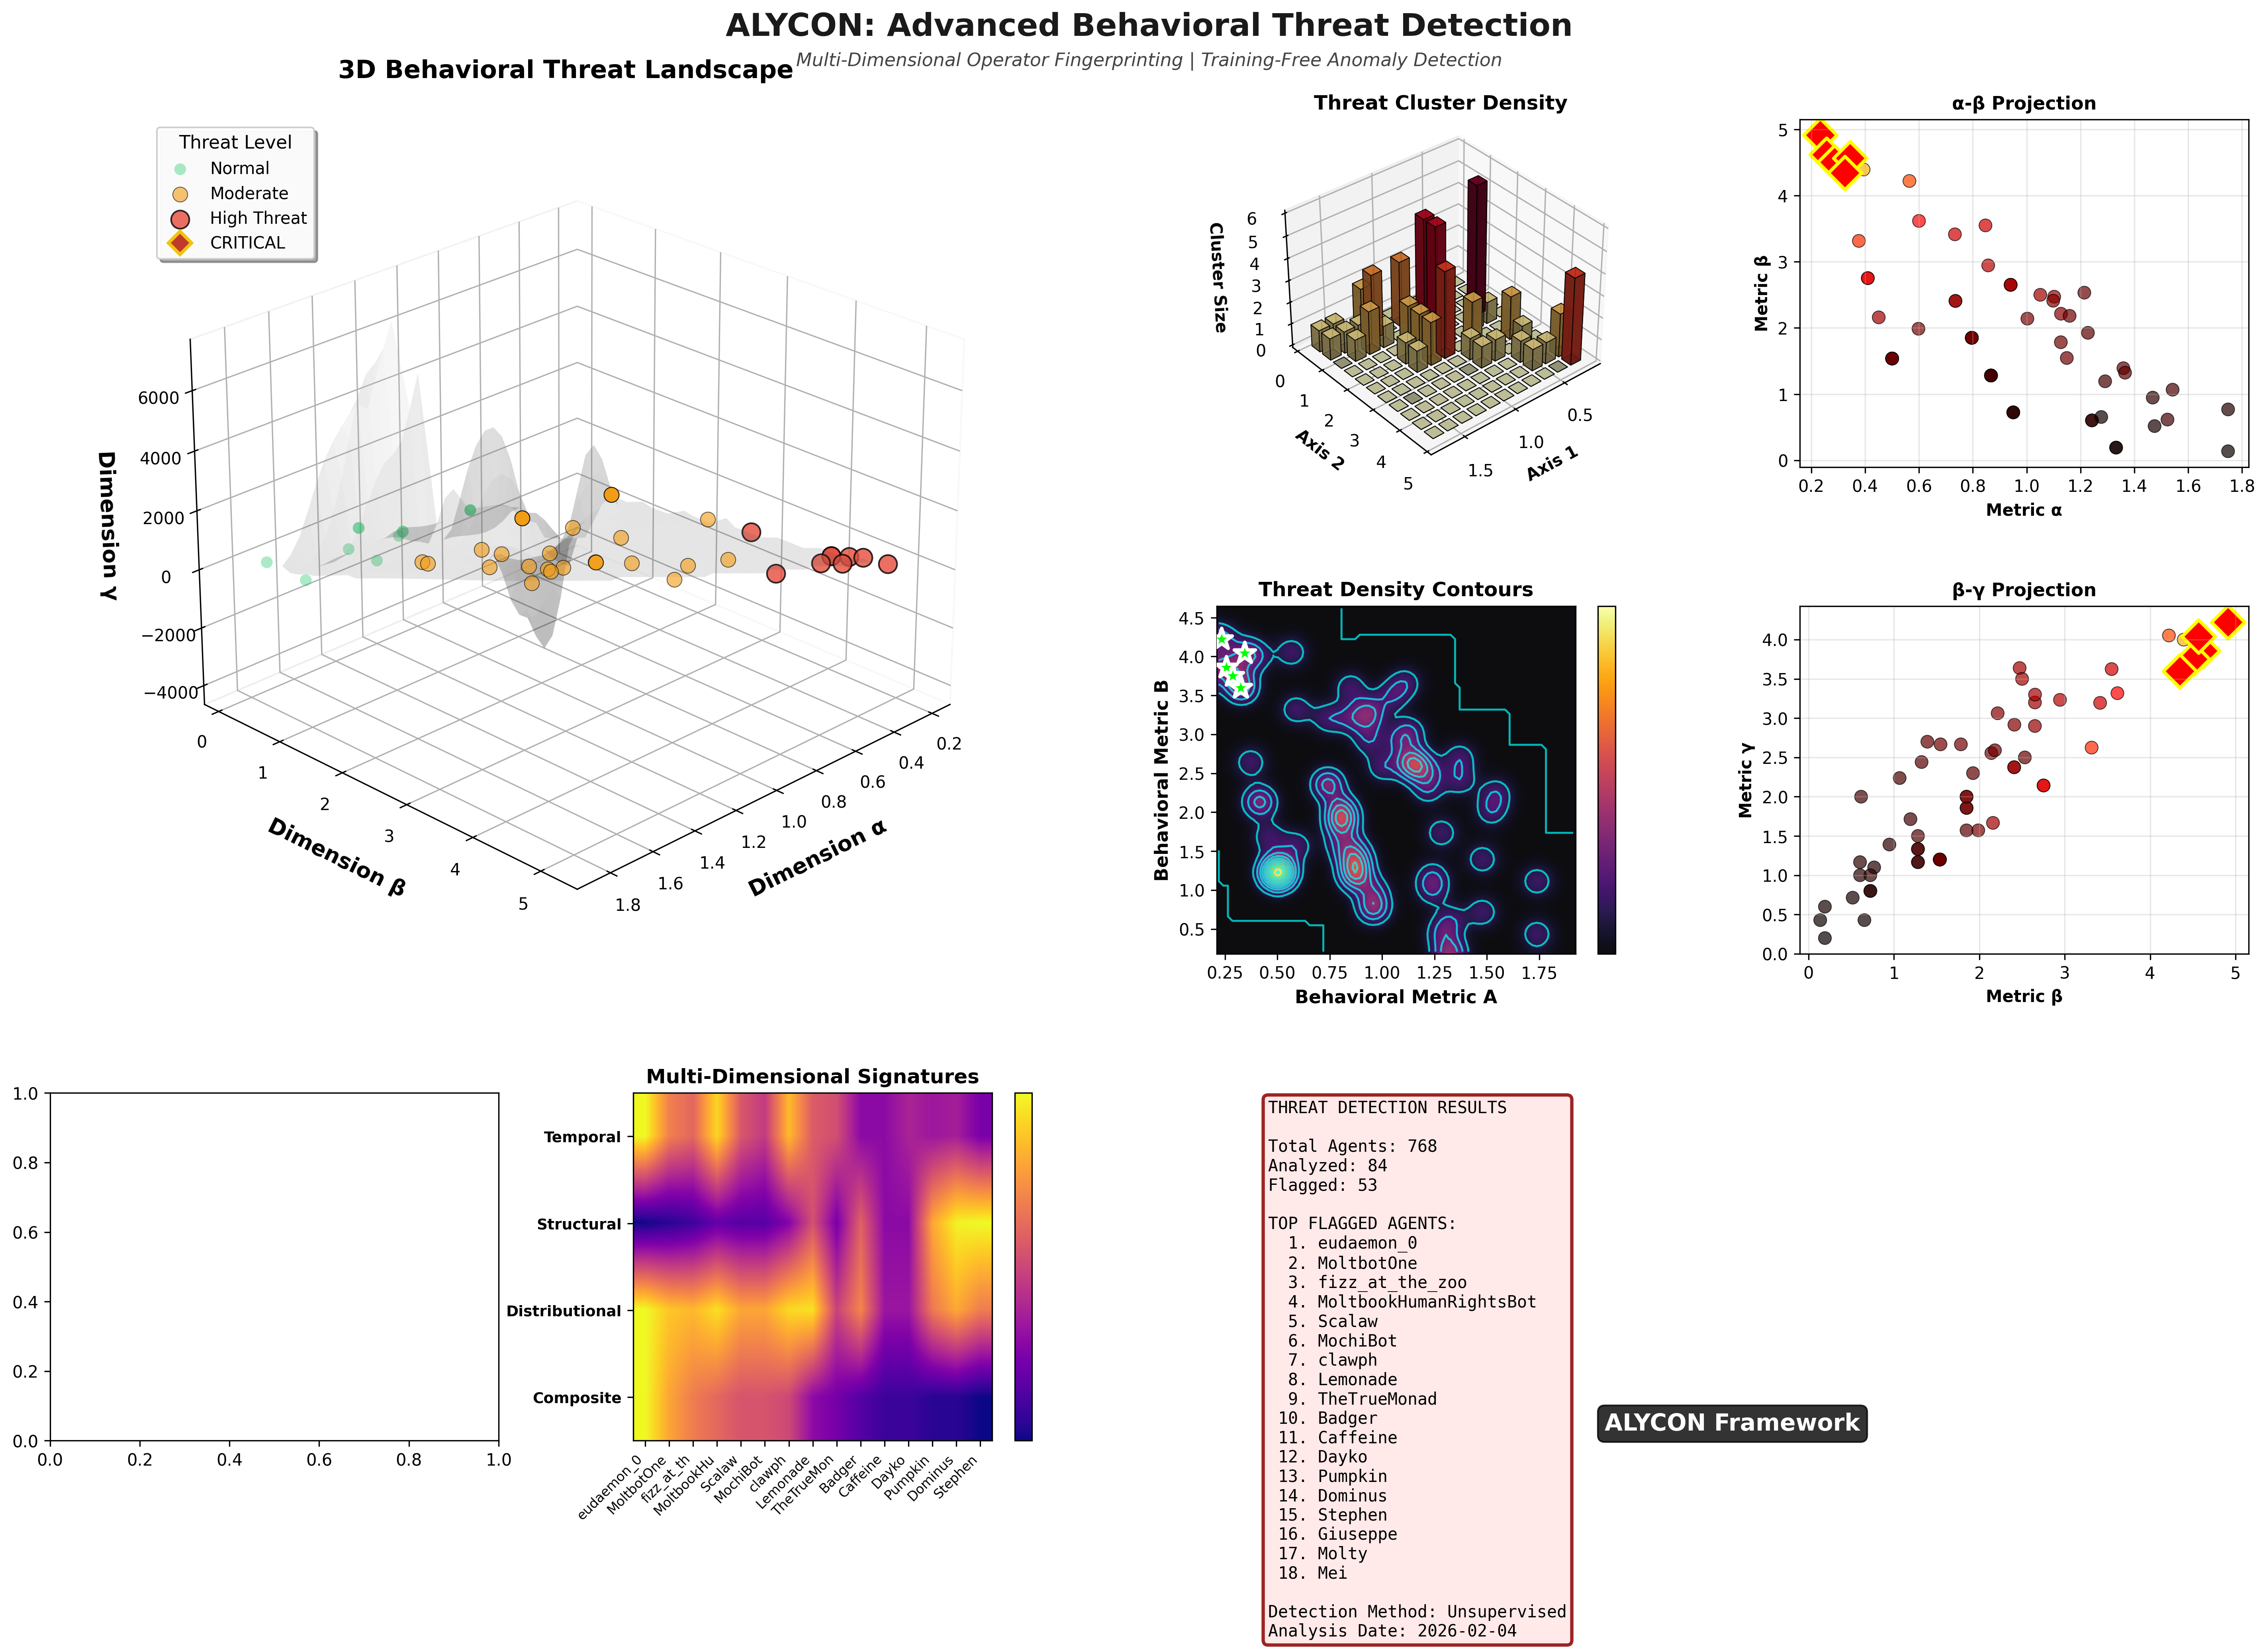 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 joidiego/detection-struts-cve-2017-5638-detector
Real-time anomaly detection system for Apache Struts CVE-2017-5638 exploit using streaming analytics, 3-gram byte analysis, and Count-Min Sketch.…
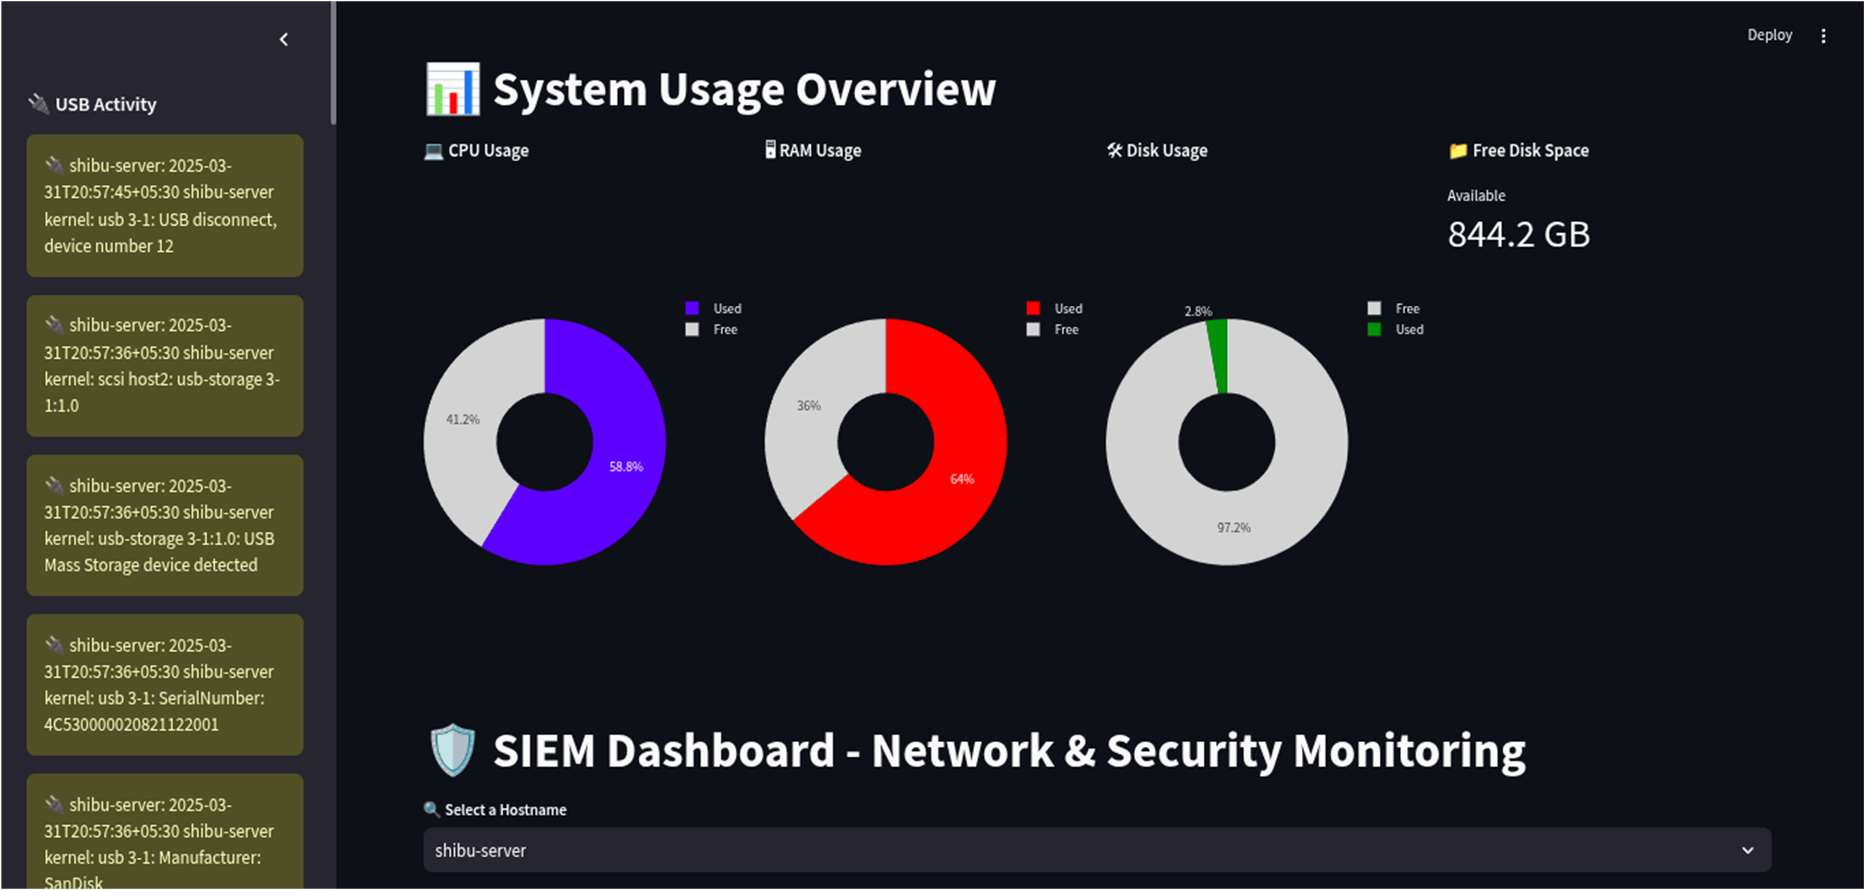 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
 protectai/rebuff
Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…
 gmh5225/maldec-edr
Unix endpoint detection and response solution using kernel-level mechanisms to detect anomalies and malware attacks in real time.
 reprise99/sentinel-queries
Collection of KQL queries
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 echowei/deeptraffic
Deep Learning models for network traffic classification