
Argos
 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
anomaly-detectiondigital-forensicsinformation-gathering+3
1
functori/argos/argosAnalysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 thingsboard/thingsboard
All-in-one IoT Platform - Device management, data collection, processing and visualization.
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 francescopace/espectre
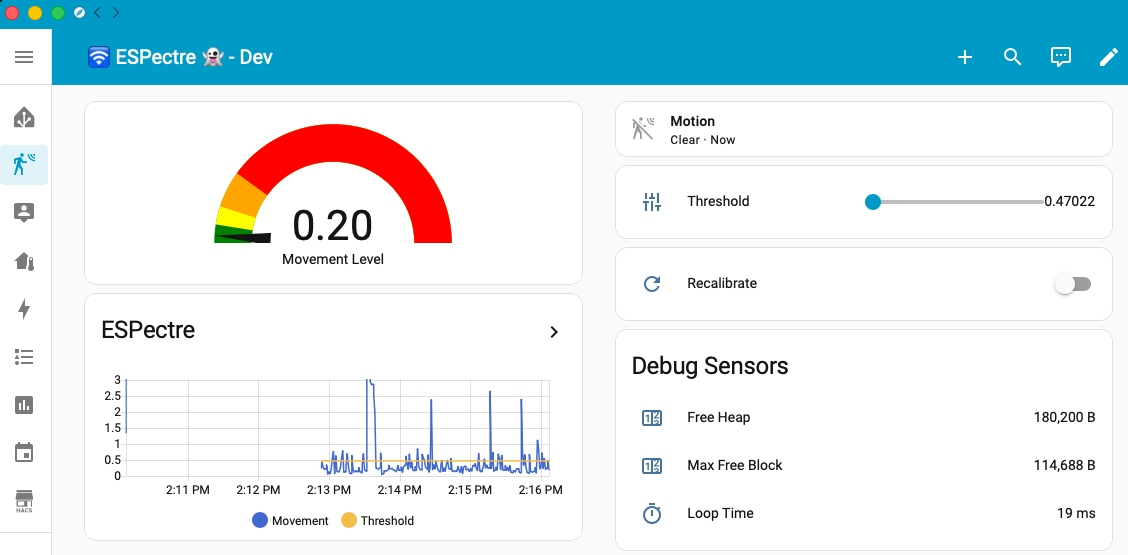
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 edoardottt/offensive-onos
My experiments in weaponizing ONOS applications (https://github.com/opennetworkinglab/onos)
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 kreotic/sentrygrid
ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
 ait-aecid/rootkit-detection-ebpf-time-trace
Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
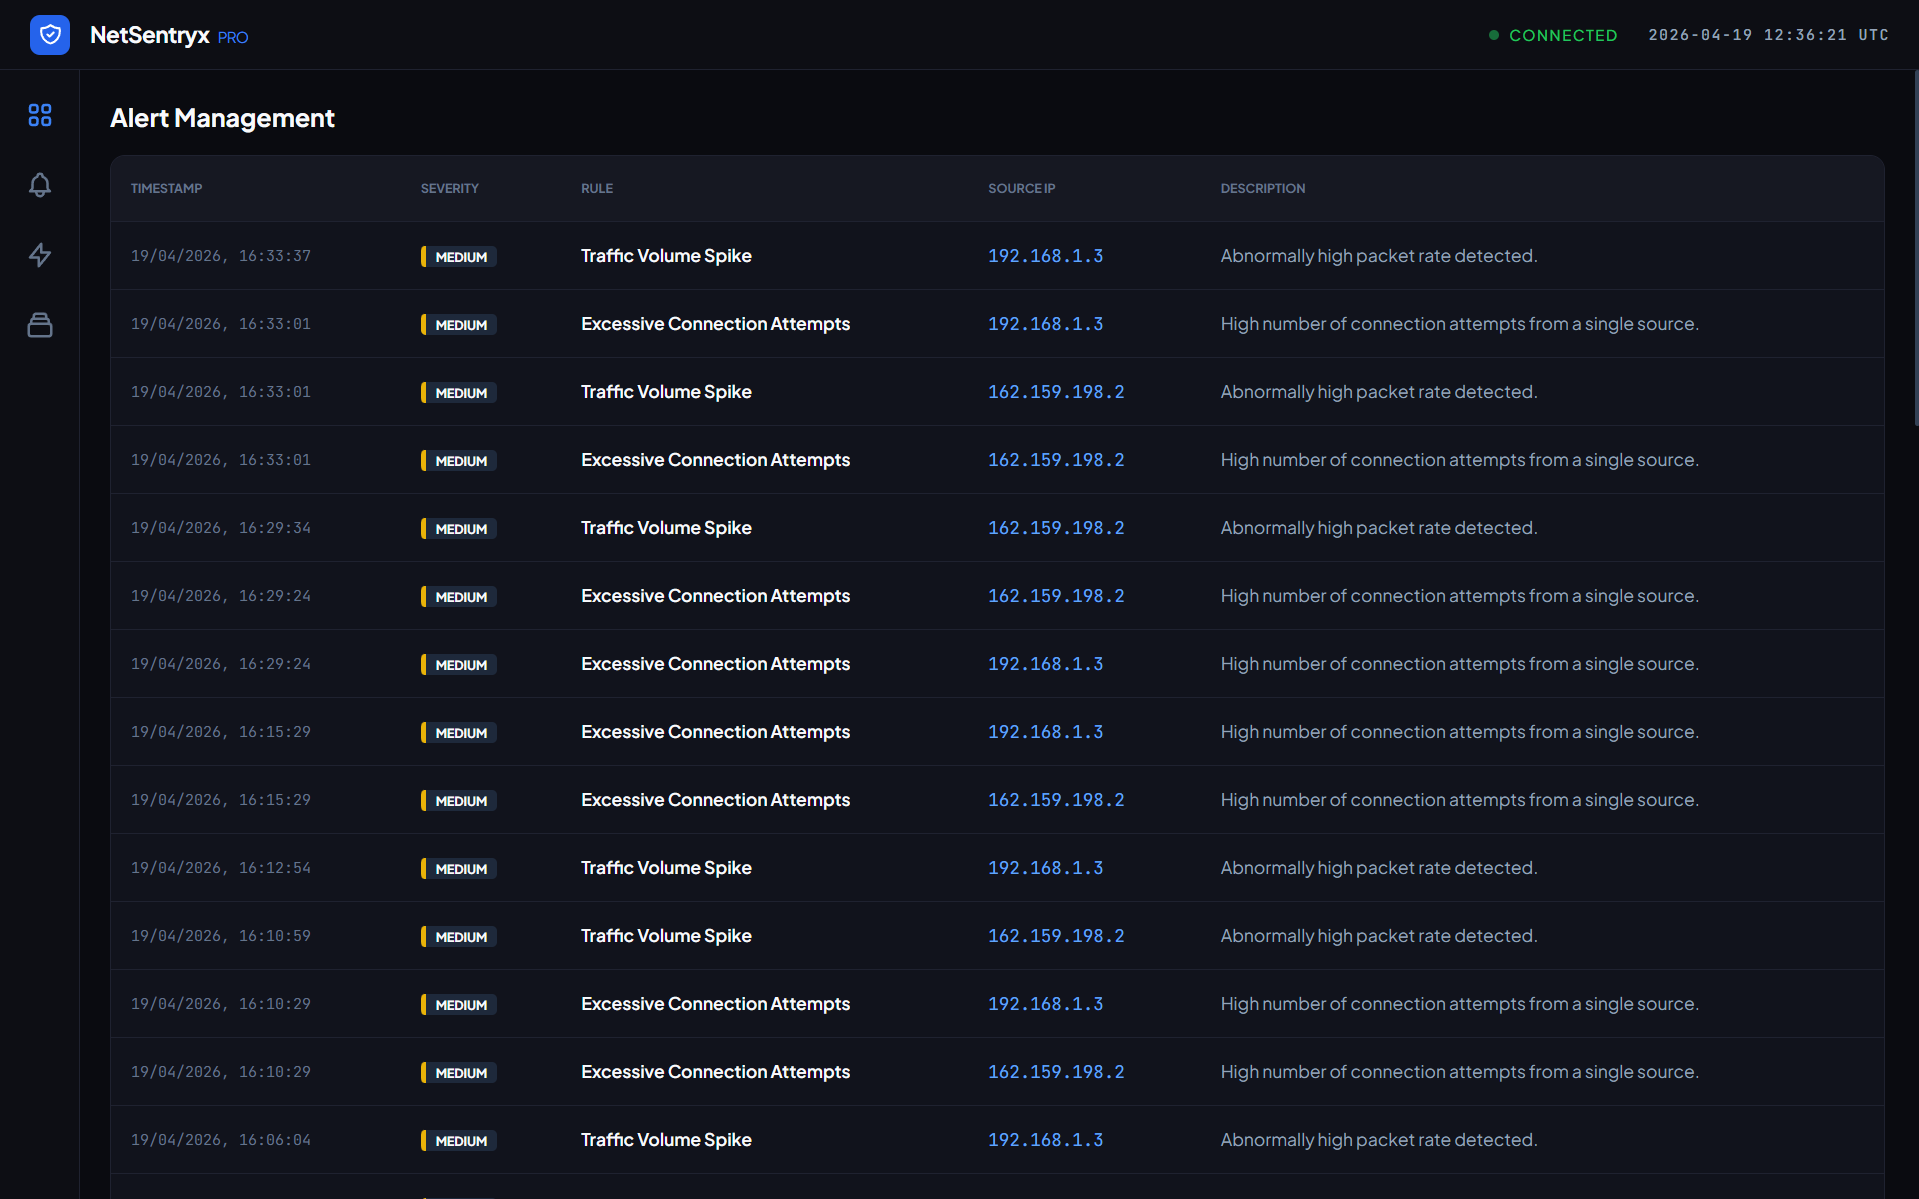 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
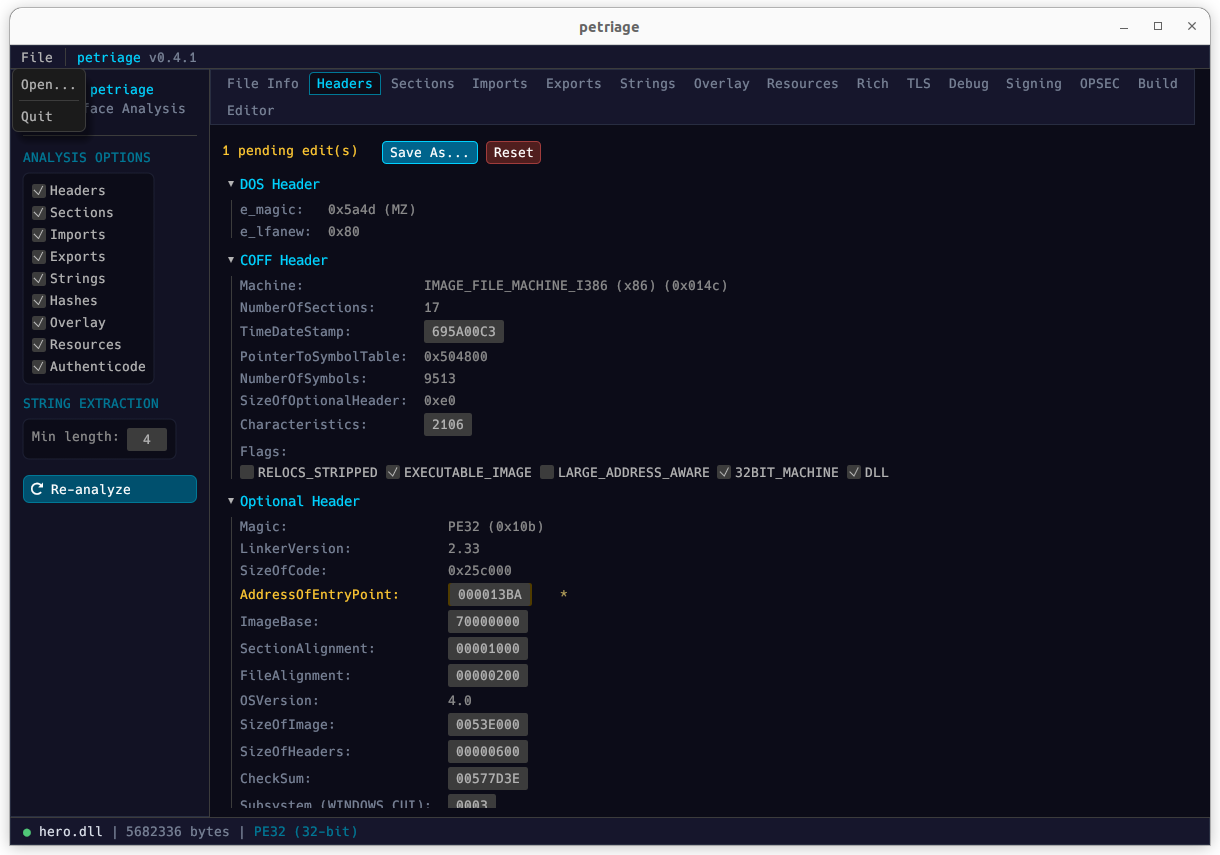 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 roxanne_ardary/nexora
AI-driven endpoint governance platform that monitors software usage, applies deterministic policy-based risk classification, and generates structured…
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…