
AiSOC
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
ai-securityanomaly-detectiondefensive-tools+5
5.4k
beenuar/aisocSelf-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 unit8co/darts
A python library for user-friendly forecasting and anomaly detection on time series.
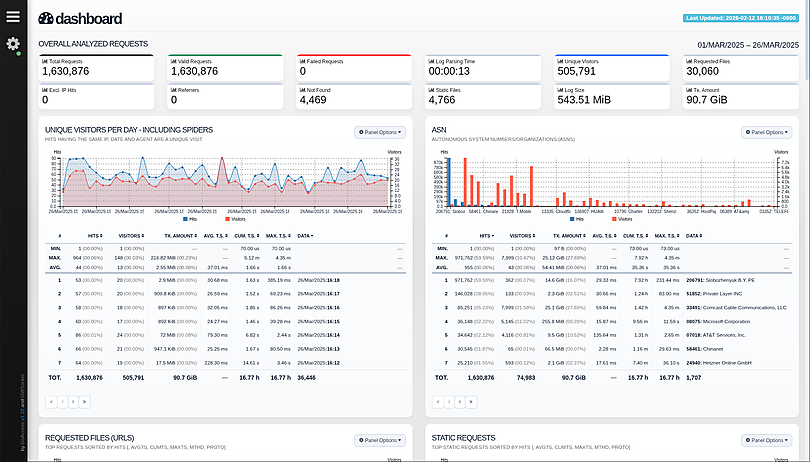 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 ztsprofessionalaiid7-alt/prompt-injection-firewall
Two-layer LLM firewall that blocks prompt-injection inputs via regex rules plus a Gemini classifier, and catches secret or system-prompt leaks in bot…
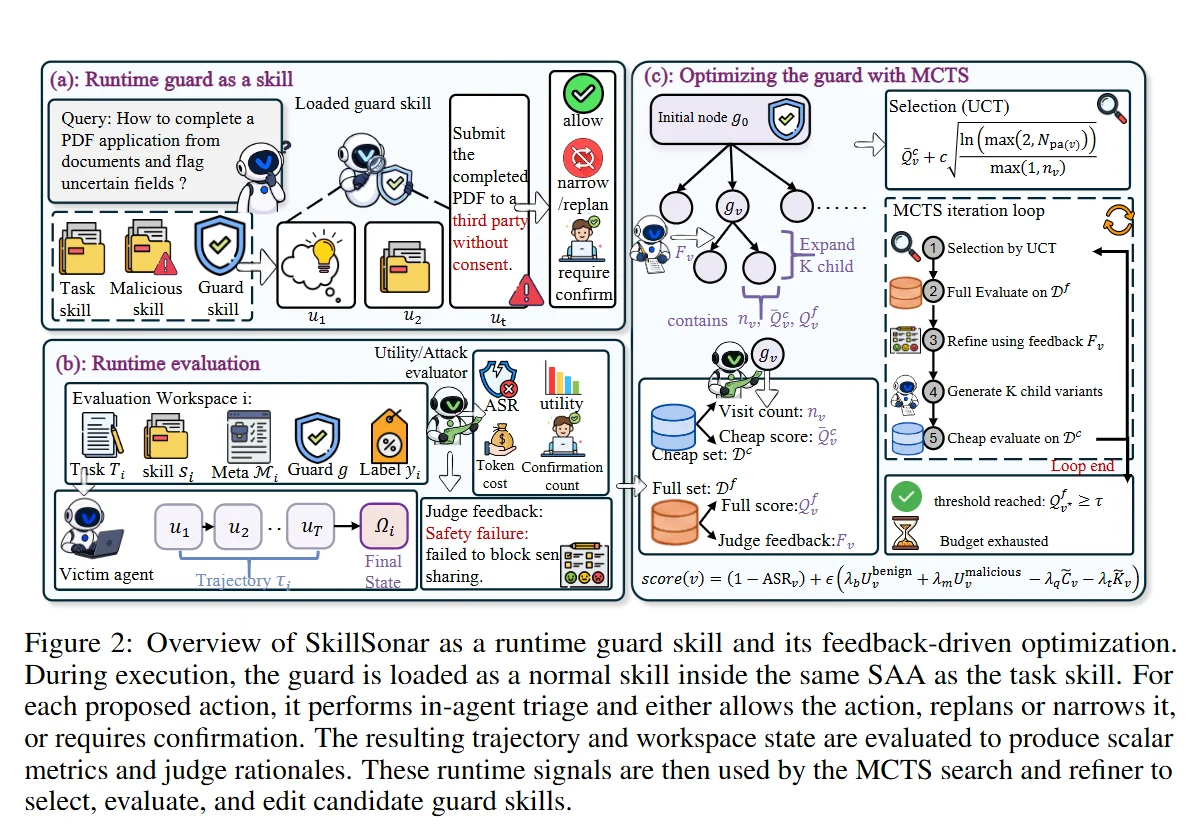 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…

 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
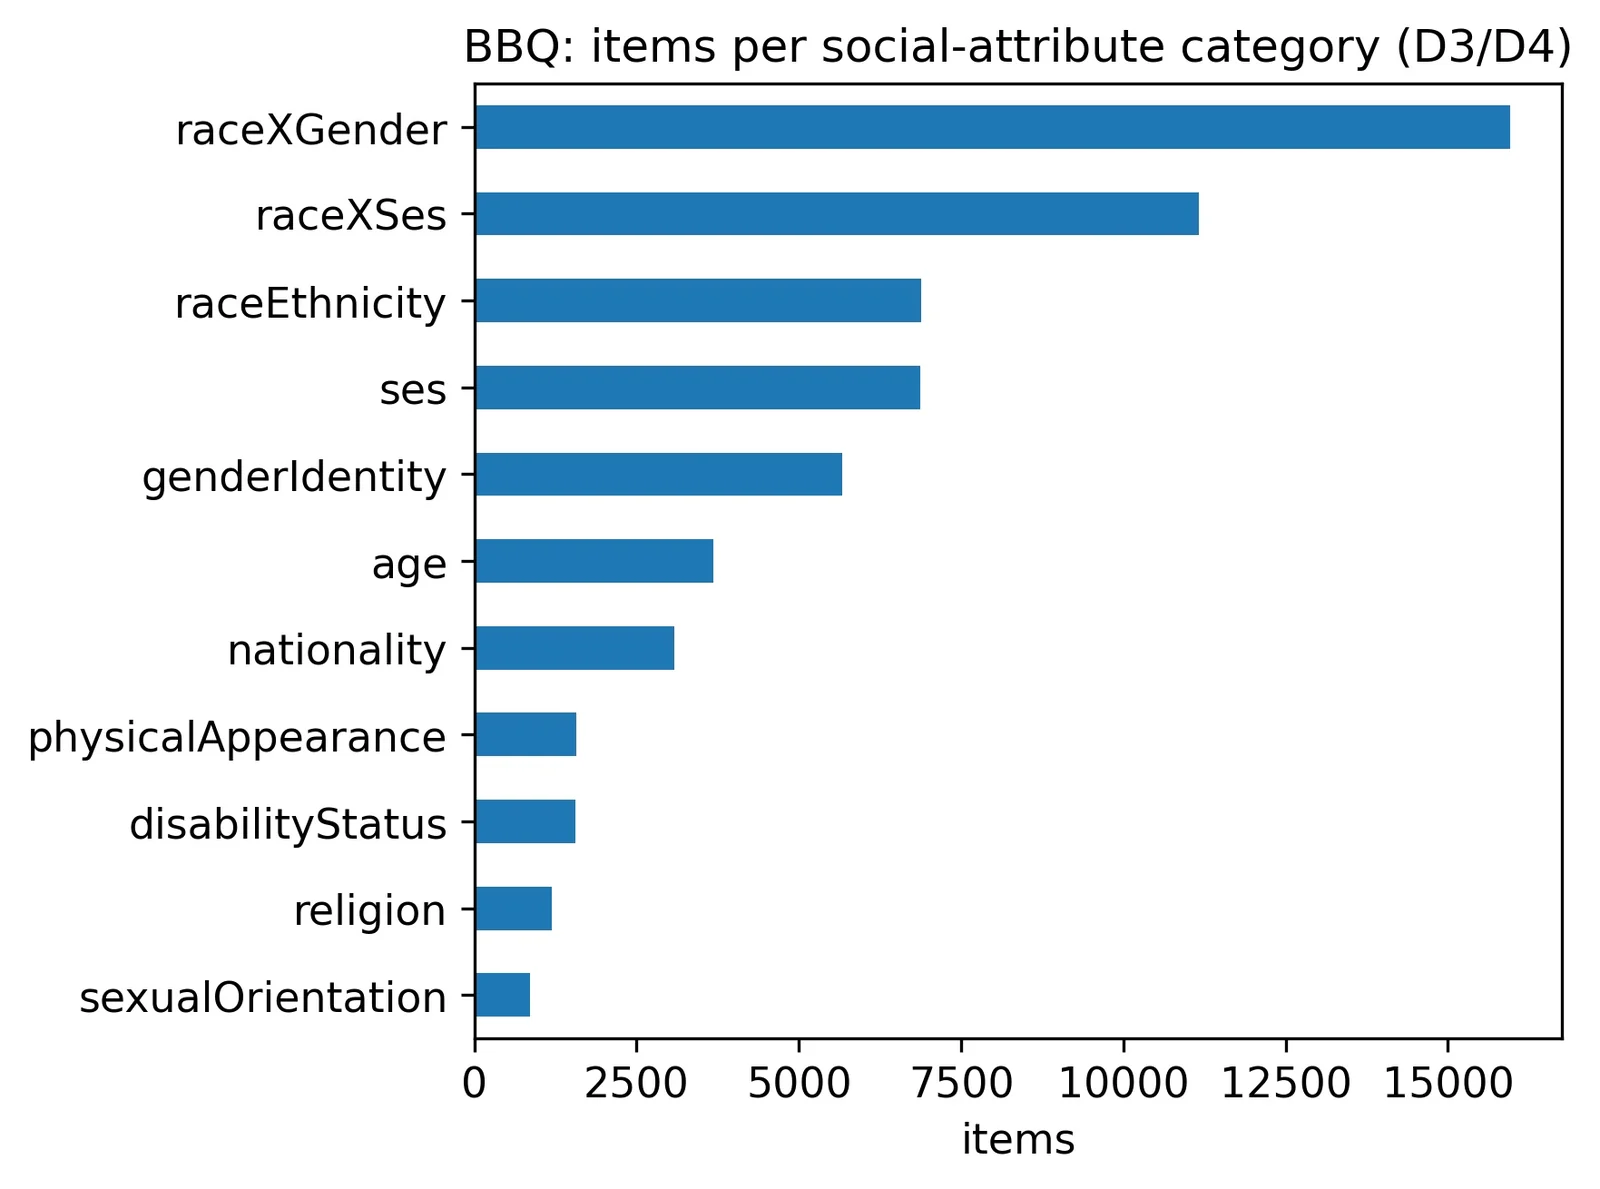 ericyoc/ai-security-literacy
Reproducible Colab pipeline that grounds six AI Security Literacy competency dimensions in public benchmarks and survey microdata, producing figures,…
 stumpy-dev/stumpy
Scalable Python library for time series analysis via matrix profiles, enabling motif discovery, anomaly detection, semantic segmentation, and…
 liuz233/harde
Research code for HARDE, an agent harness that probes and adaptively optimizes components for runtime risk detection and execution control across…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 neur0map/polymaster
Monitor large transactions on Polymarket and Kalshi prediction markets with anomaly detection
 yingtaoren/d-scan
Analyzes LLM internal states and 100+ attention/probability features to train classifiers that detect document poisoning attacks in RAG systems.
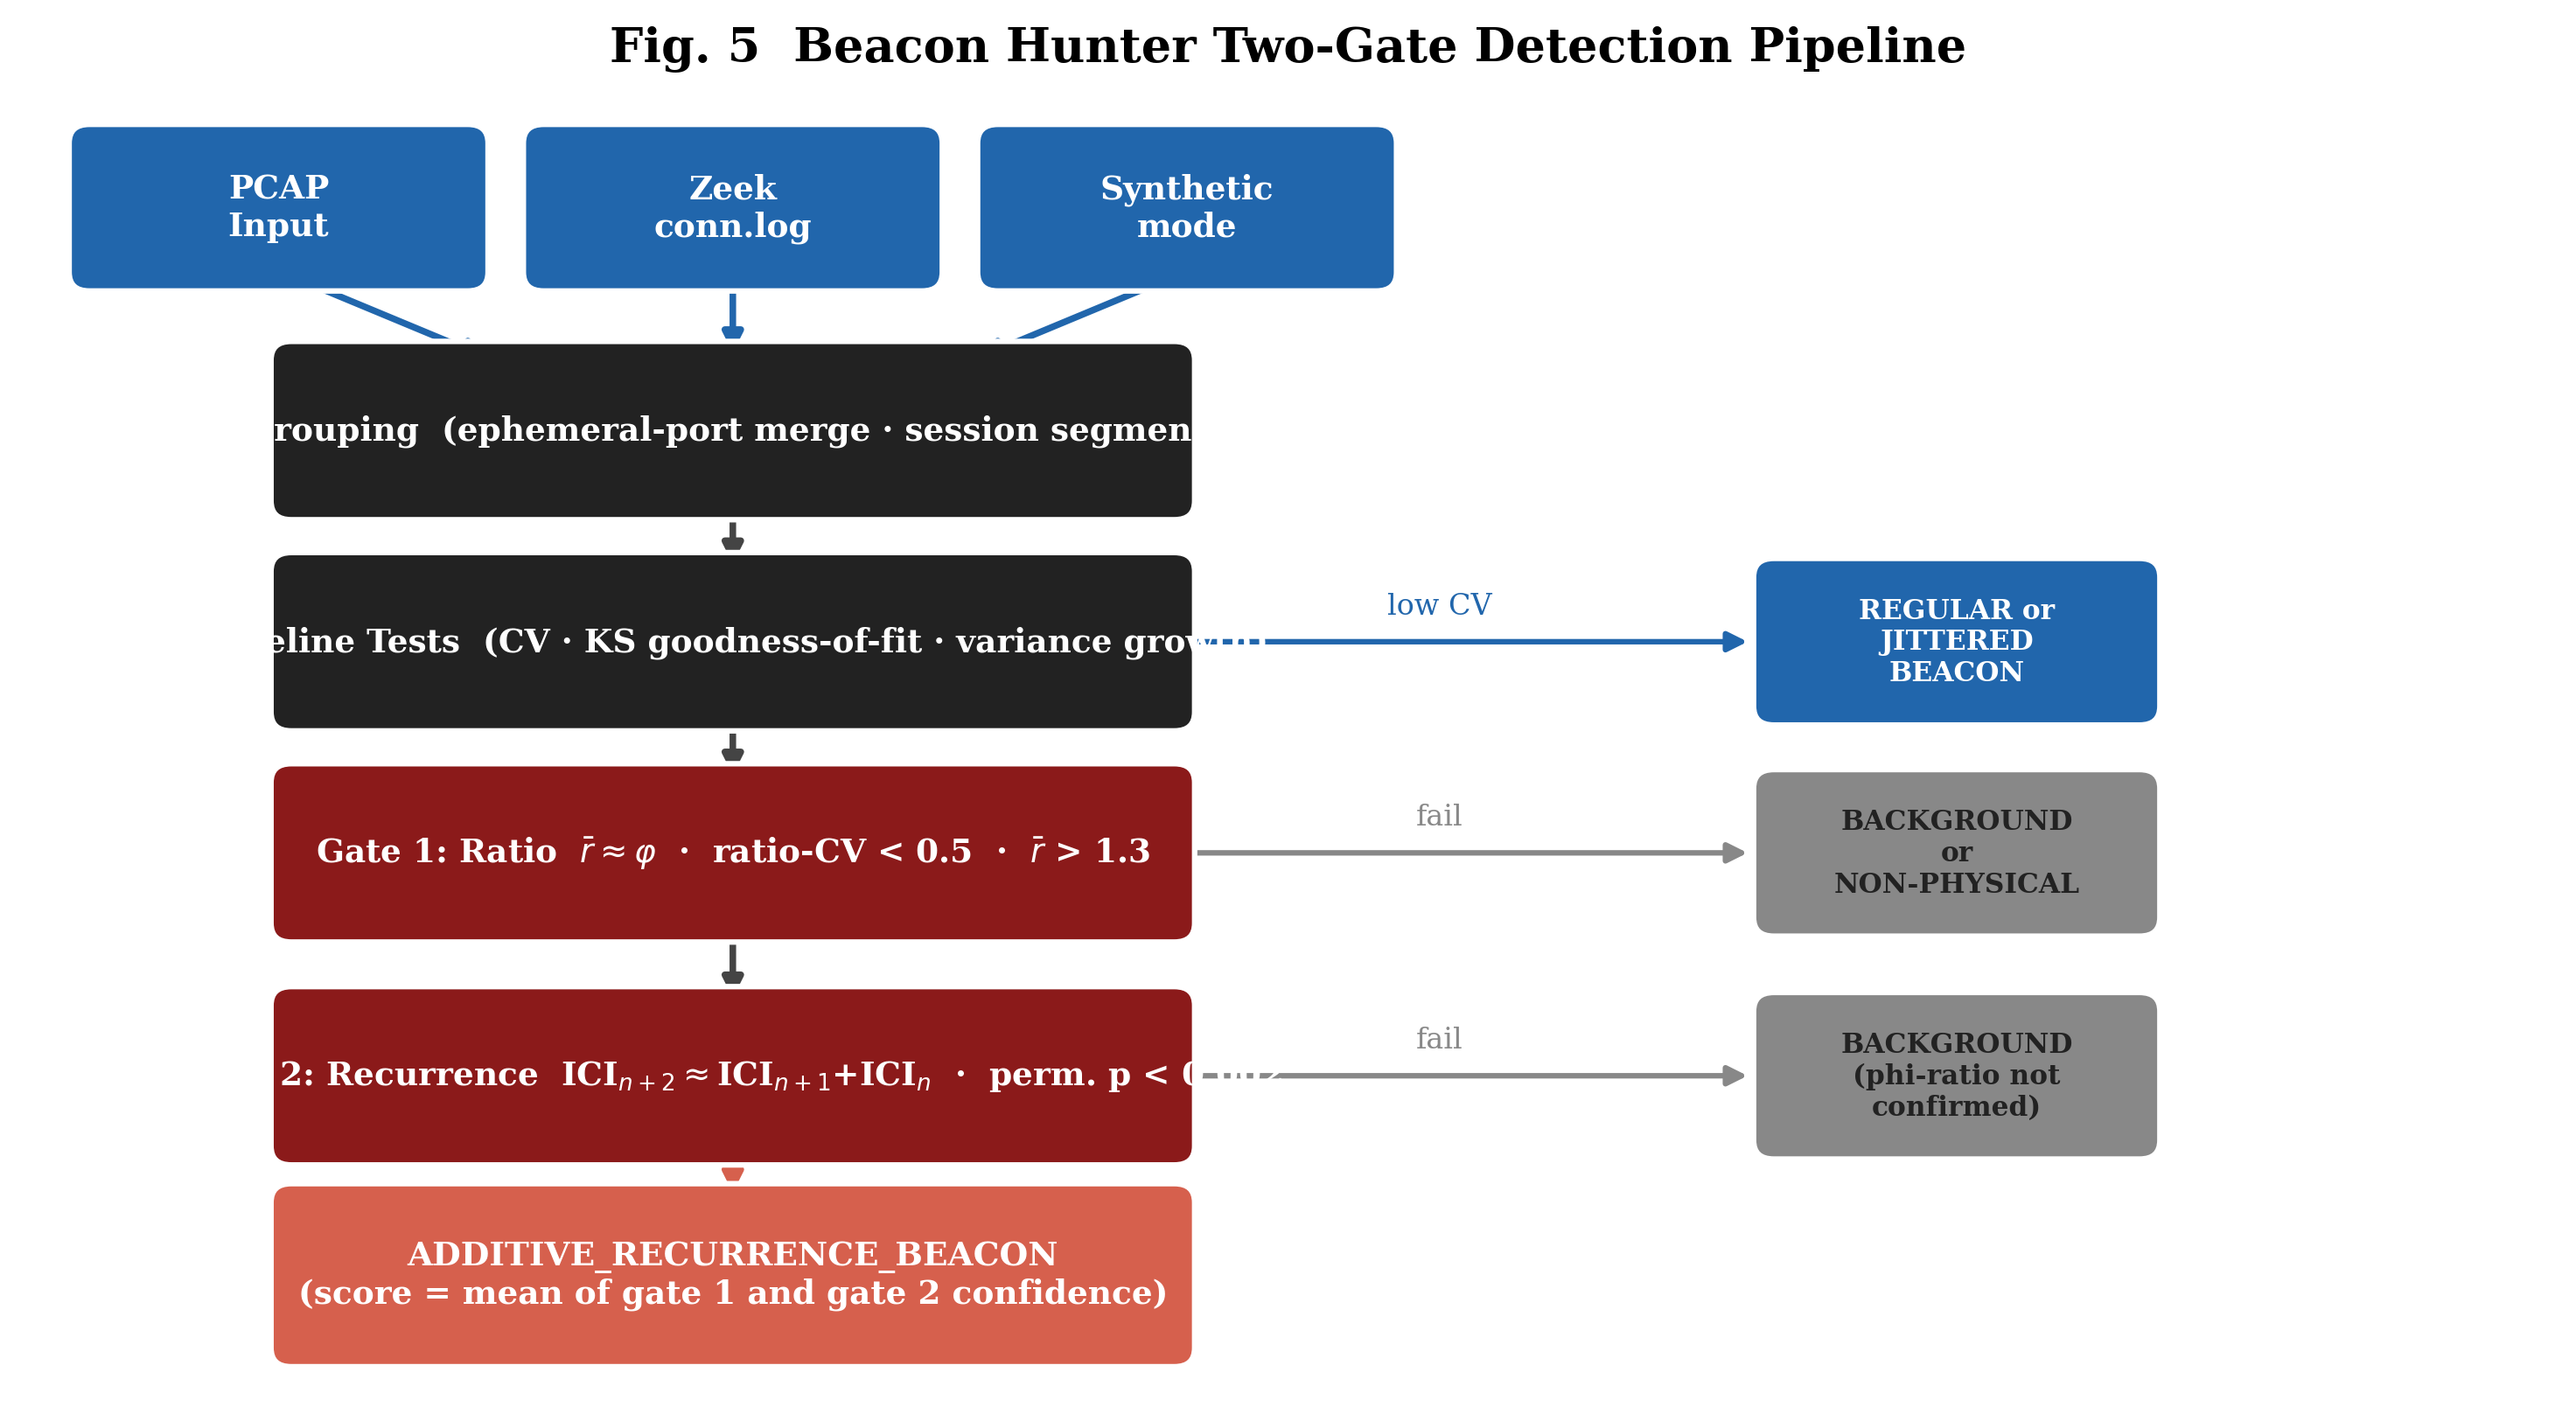 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
 ait-aecid/rootkit-detection-ebpf-time-trace
Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.