

ntopng
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
anomaly-detectiondns-analysisintrusion-detection+6
ntop/ntopngWeb-based Traffic and Cybersecurity Network Traffic Monitoring
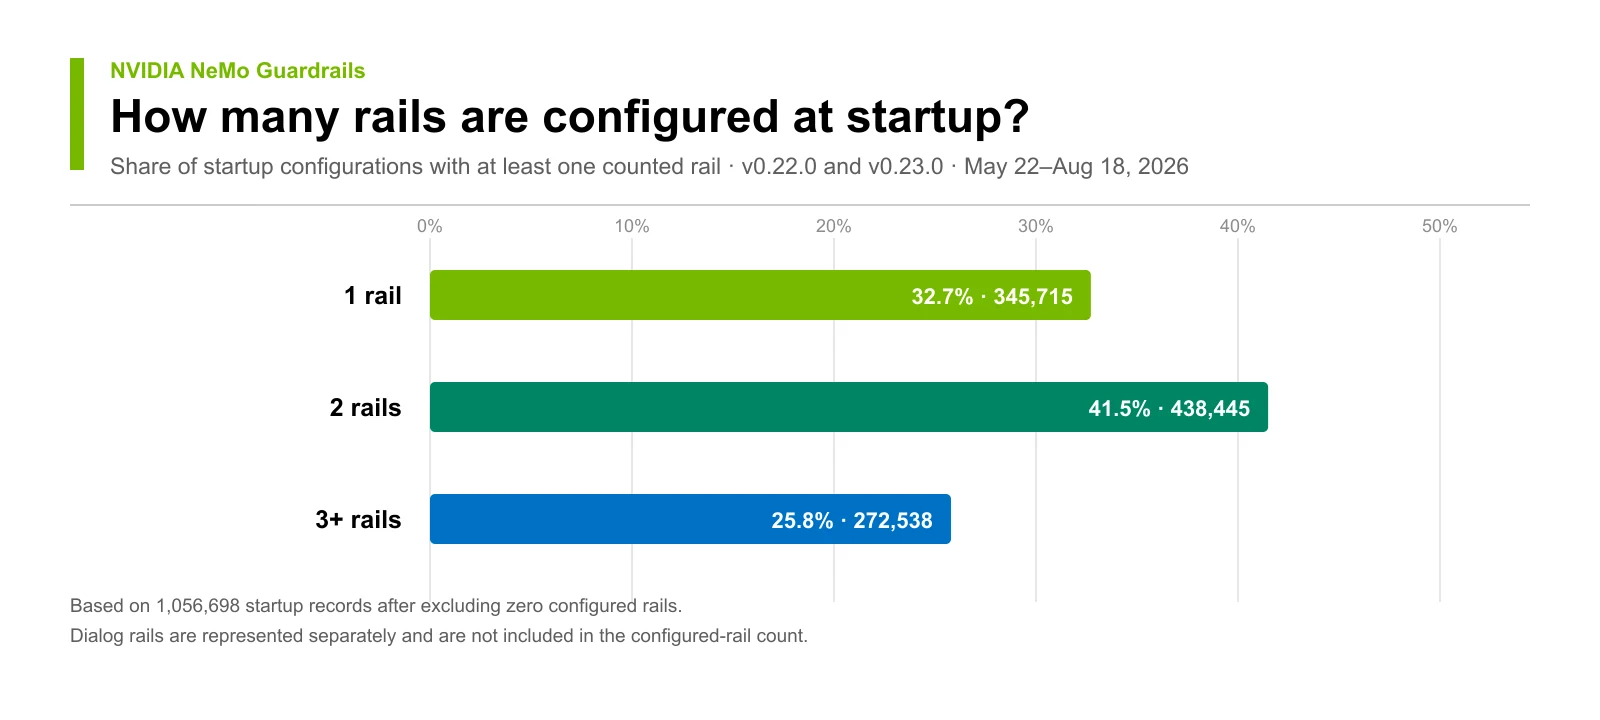 nvidia-nemo/guardrails
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
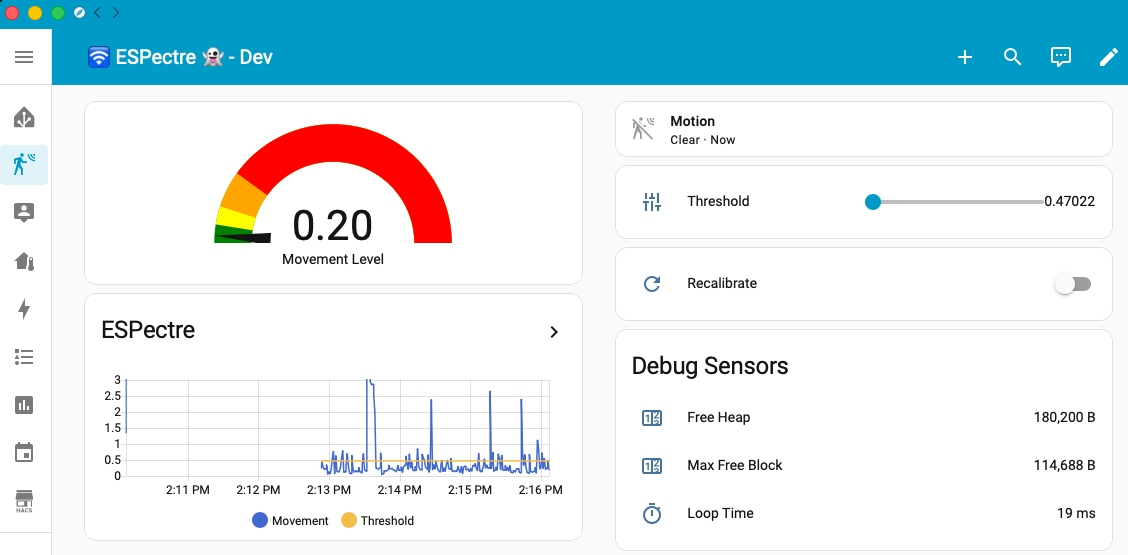 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
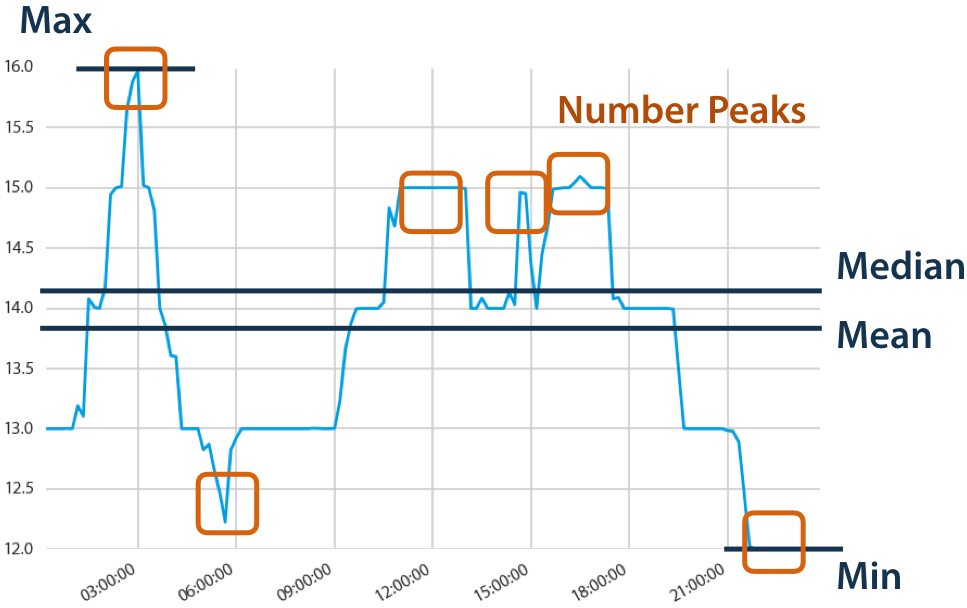 blue-yonder/tsfresh
Automatic extraction of relevant features from time series:
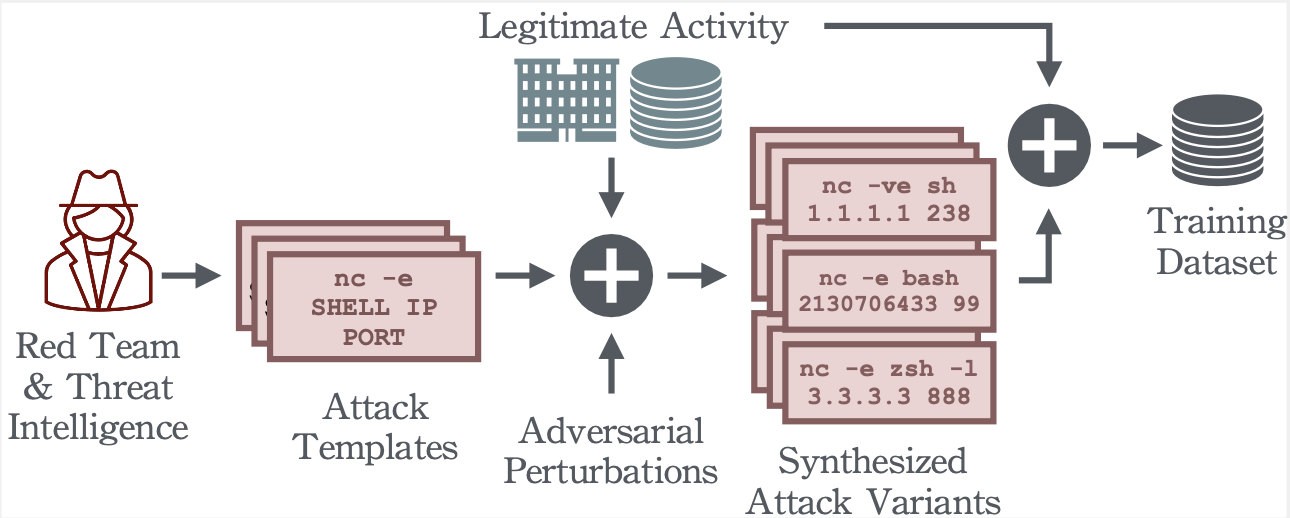 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 jazbengu/threatdetect
Streamlit-based insider threat detection prototype using XGBoost and Isolation Forest to analyze employee activity data, generate risk summaries, and…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 yumlembam/insider-threat
Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
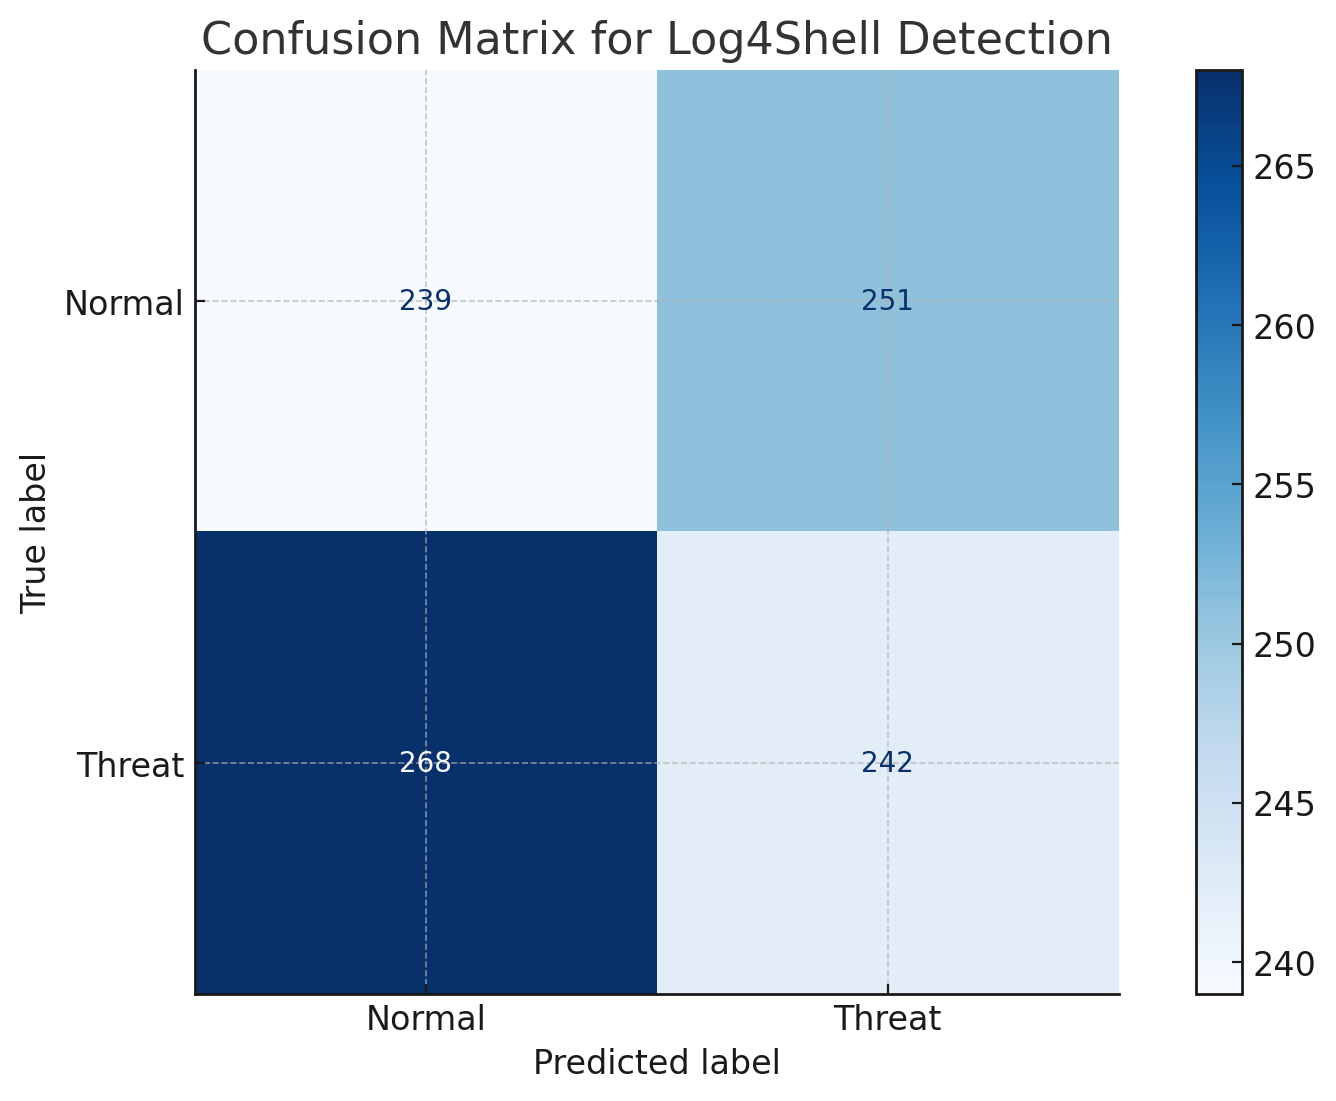 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
 logpai/loglizer
A machine learning toolkit for log-based anomaly detection [ISSRE'16]
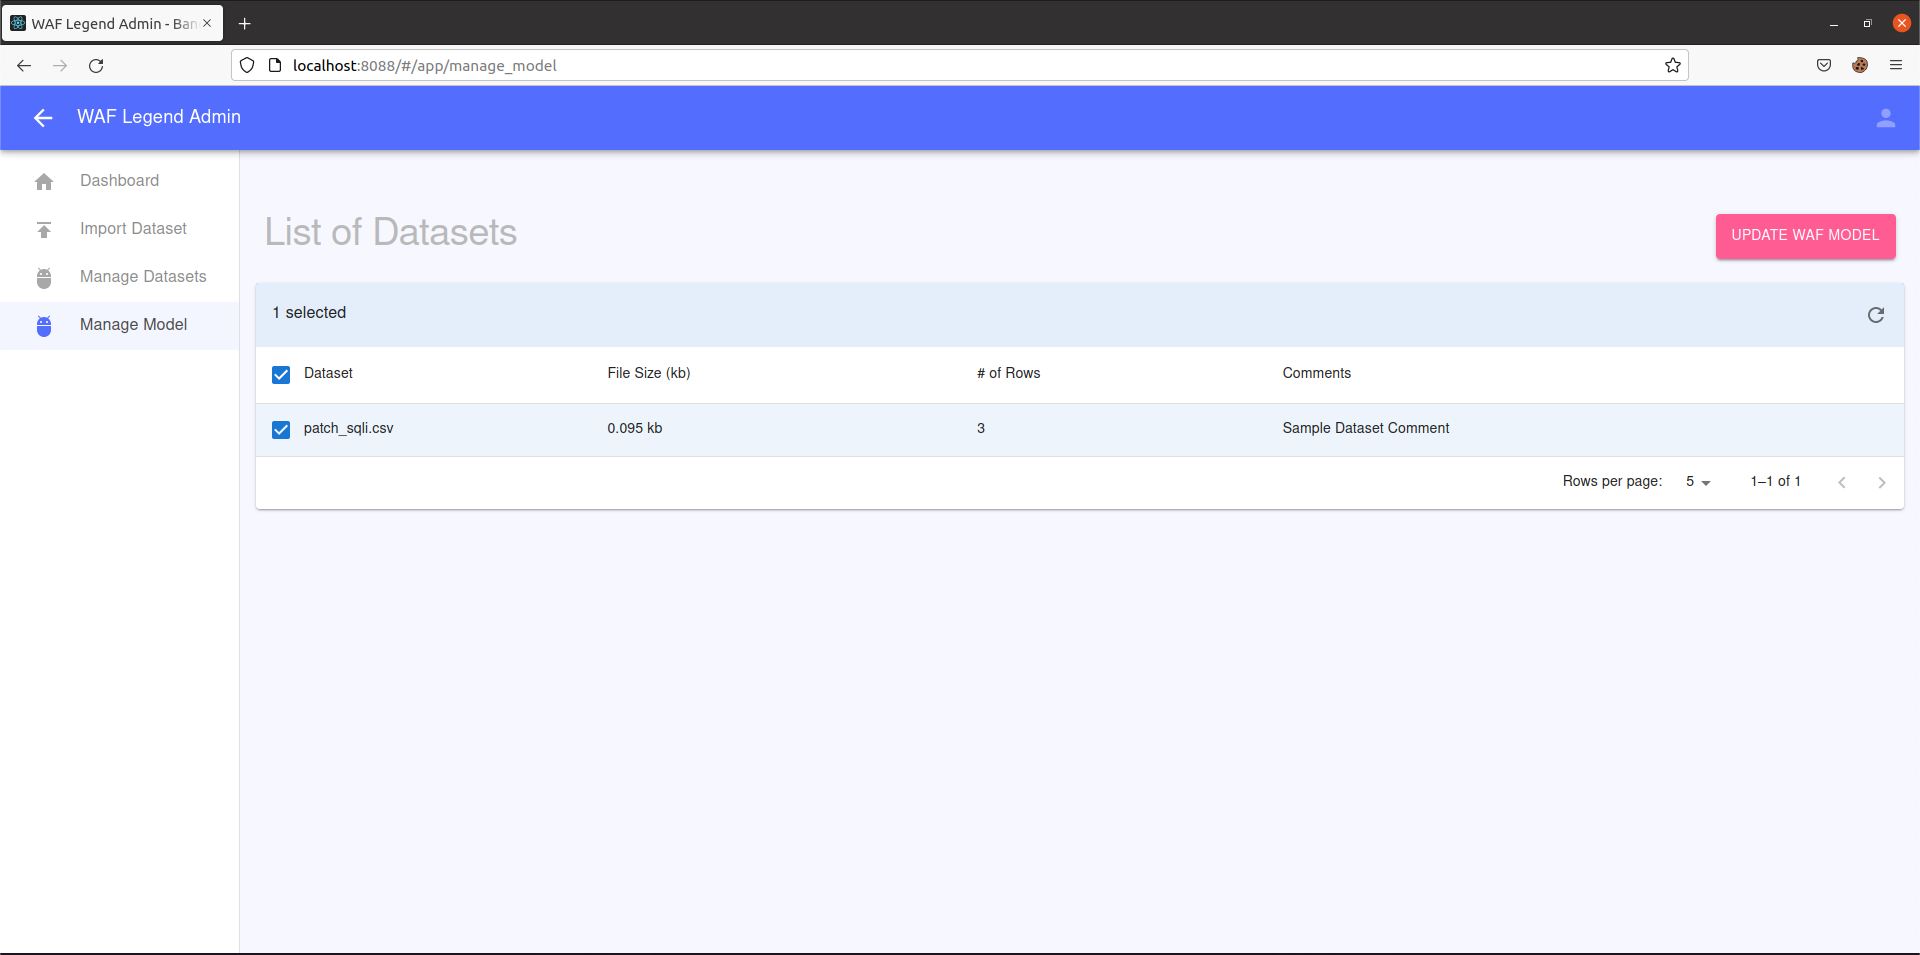 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
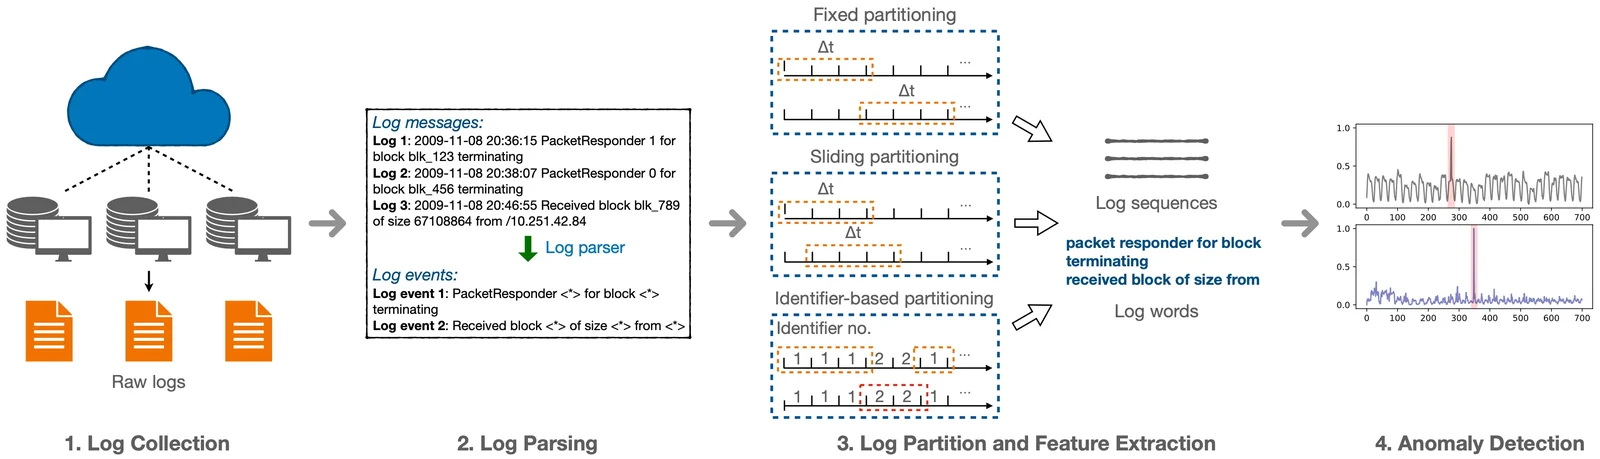 logpai/deep-loglizer
A deep learning toolkit for log-based anomaly detection