
DetectWindowsCopyOnWriteForAPI
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
anomaly-detectiondefensive-toolsforensics+3
200
nccgroup/detectwindowscopyonwriteforapiEnumerate various traits from Windows processes as an aid to threat hunting
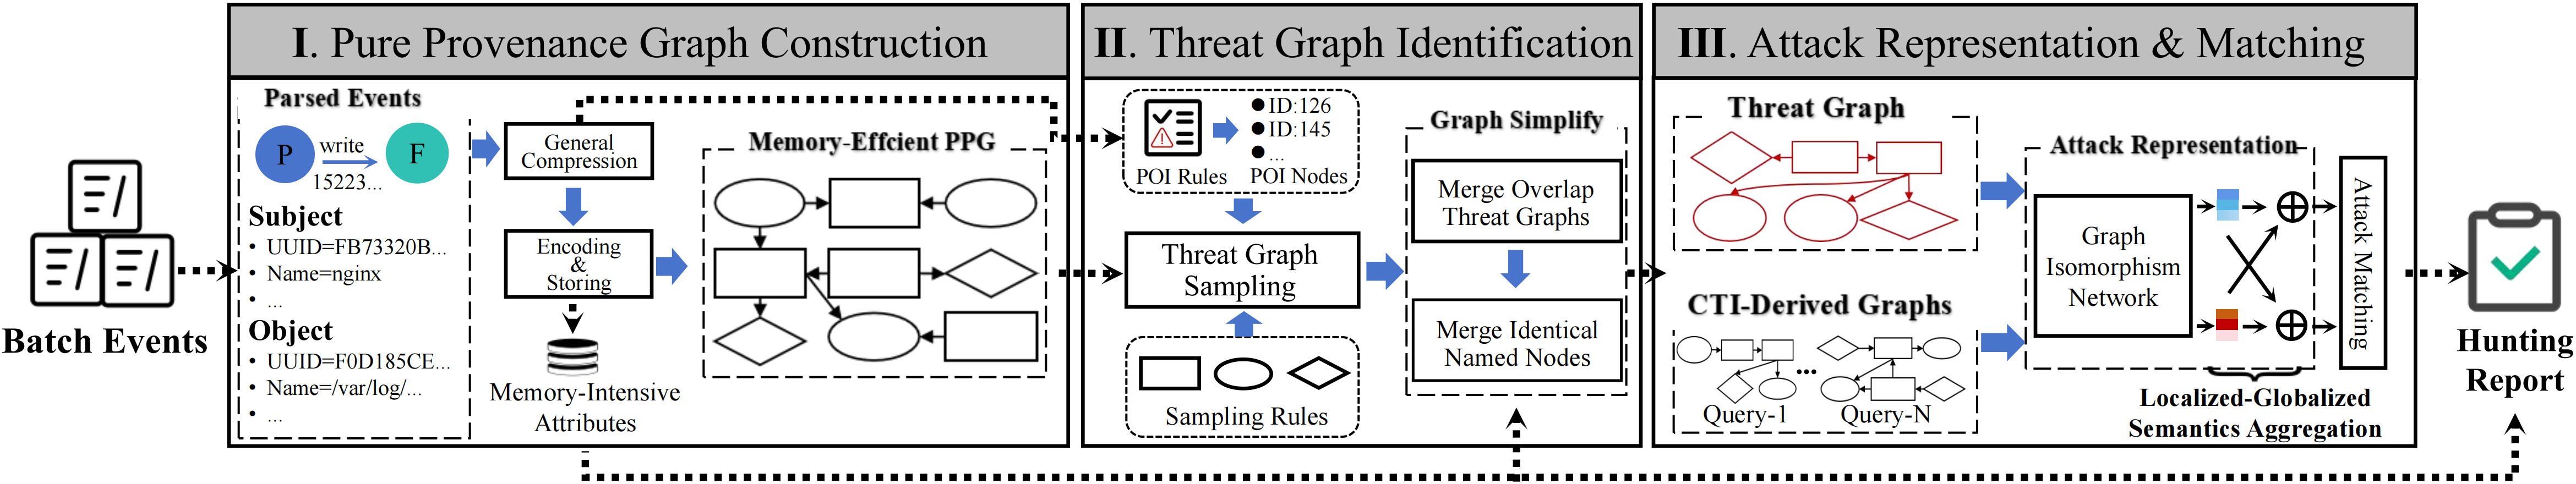 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
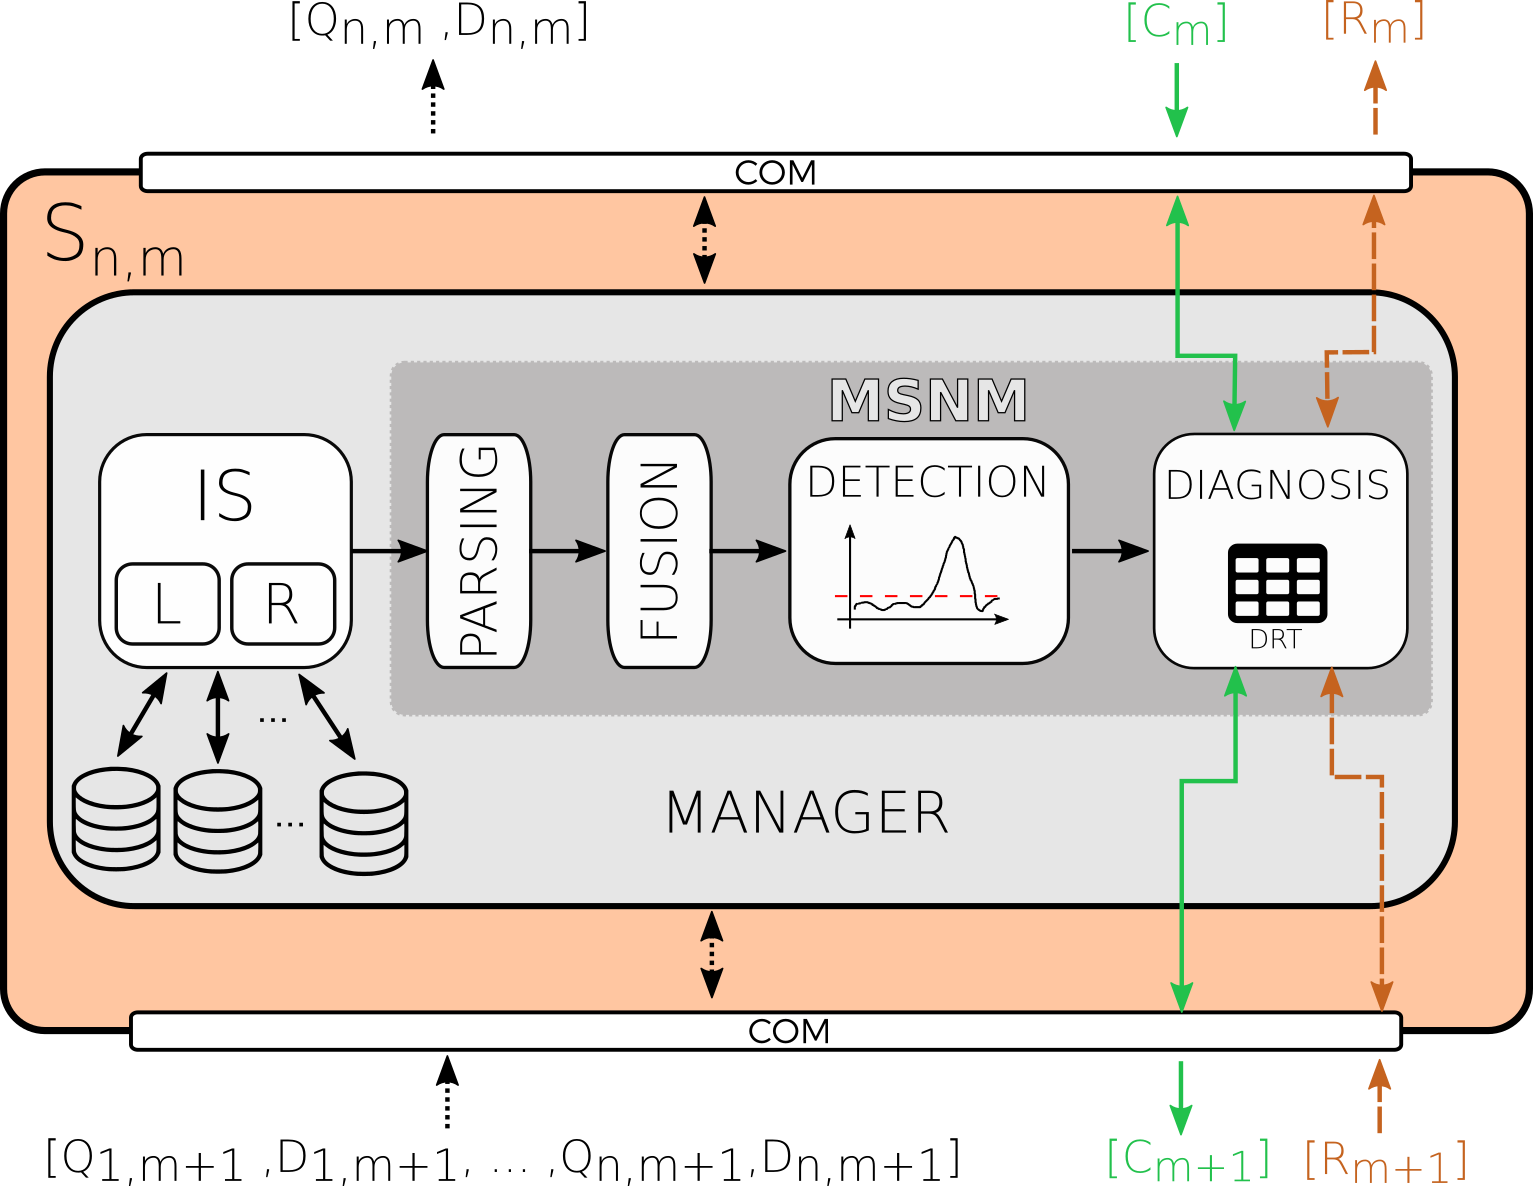 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…

 jamalrfordii-arch/vanguard-map
3D multi-domain tactical intelligence map — live ships, flights, satellites, cables & space weather in the browser. Time scrubbing, scenario replay,…
 delvelabs/batea
AI-based, context-driven network device ranking