
netward-standalone
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
anomaly-detectionanti-botdefensive-tools+6
dragon-lady/netward-standaloneUser-space bot and DDoS deflection for small HTTP services
 check-risk-waf/check-risk-waf
Reverse-proxy web application firewall with WAF, anti-bot and anti-DDoS protection at L3/L4/L7, custom rules, rate limiting, geo/IP filtering and…
 ztsprofessionalaiid7-alt/prompt-injection-firewall
Two-layer LLM firewall that blocks prompt-injection inputs via regex rules plus a Gemini classifier, and catches secret or system-prompt leaks in bot…
 raj3shp/malscore
Maliciousness scoring for Linux commands
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 logpai/logparser
A machine learning toolkit for log parsing [ICSE'19, DSN'16]
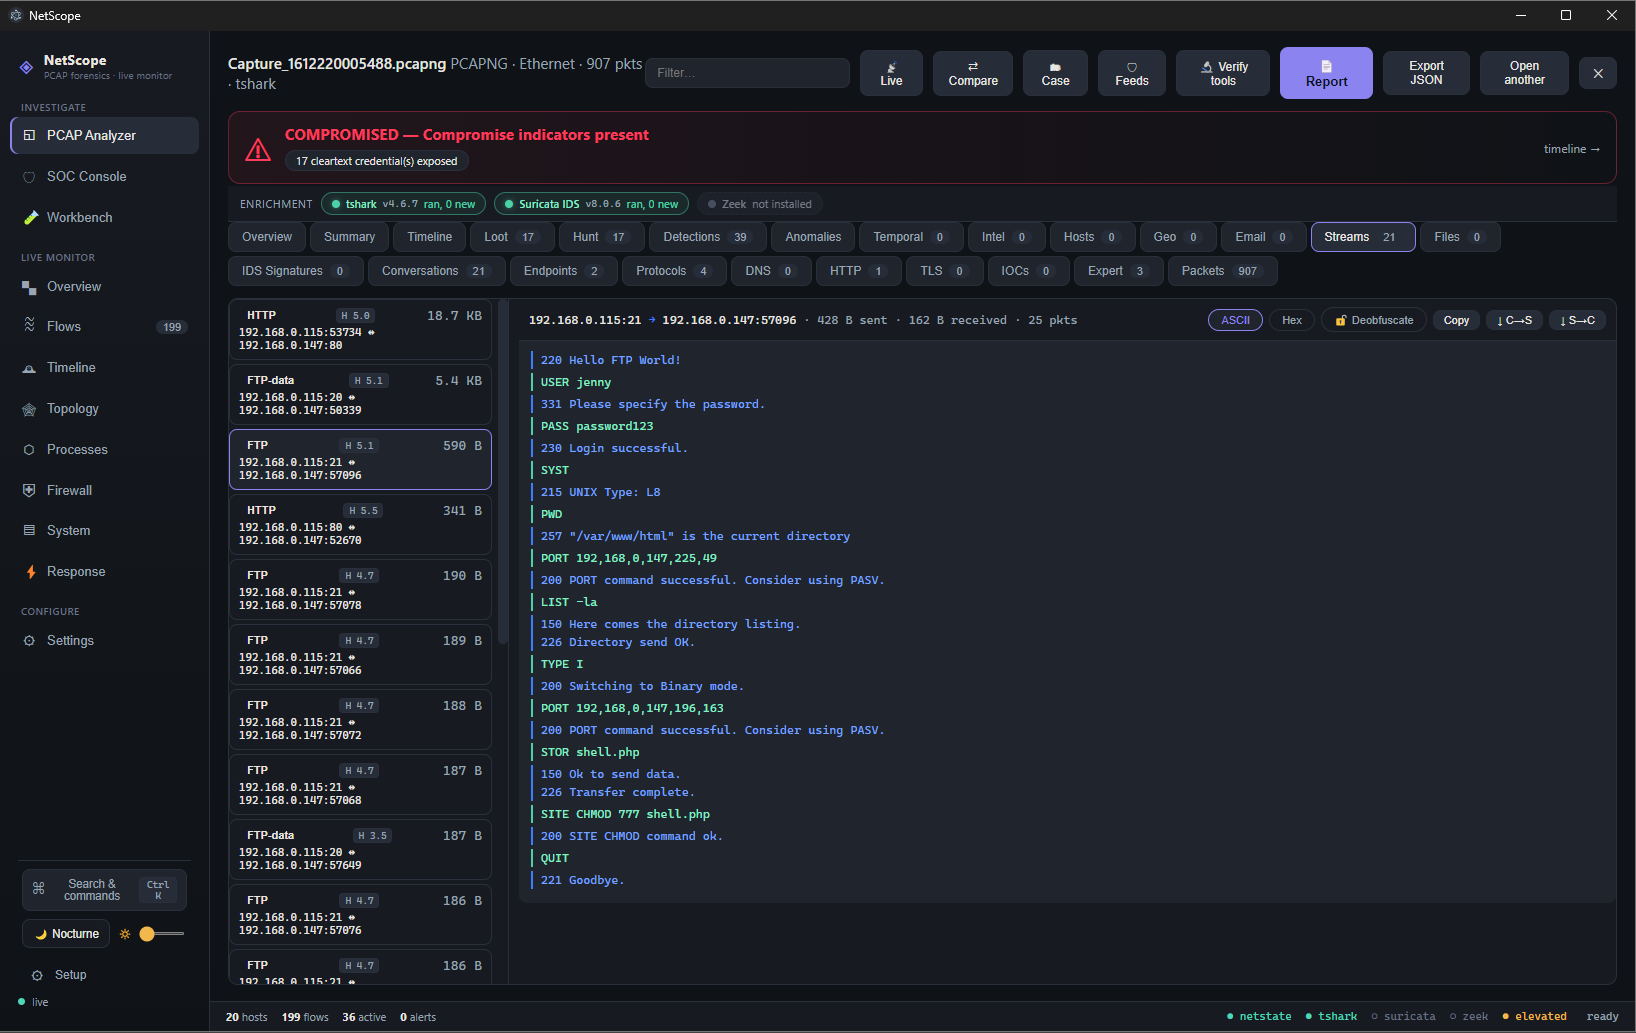 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 connectedlucy/plague
Default Detections for EDR
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 nccgroup/killedprocesscanary
A canary designed to minimize the impact from certain Ransomware actors
 nccgroup/mimikatz-detector-condrv
The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…
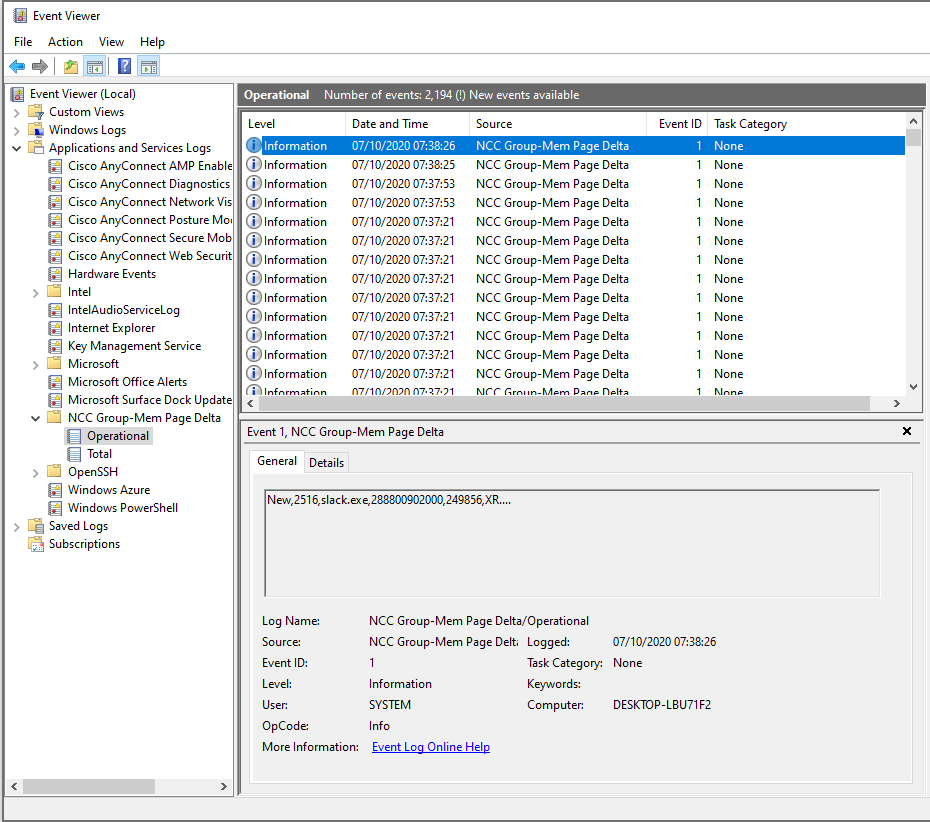 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
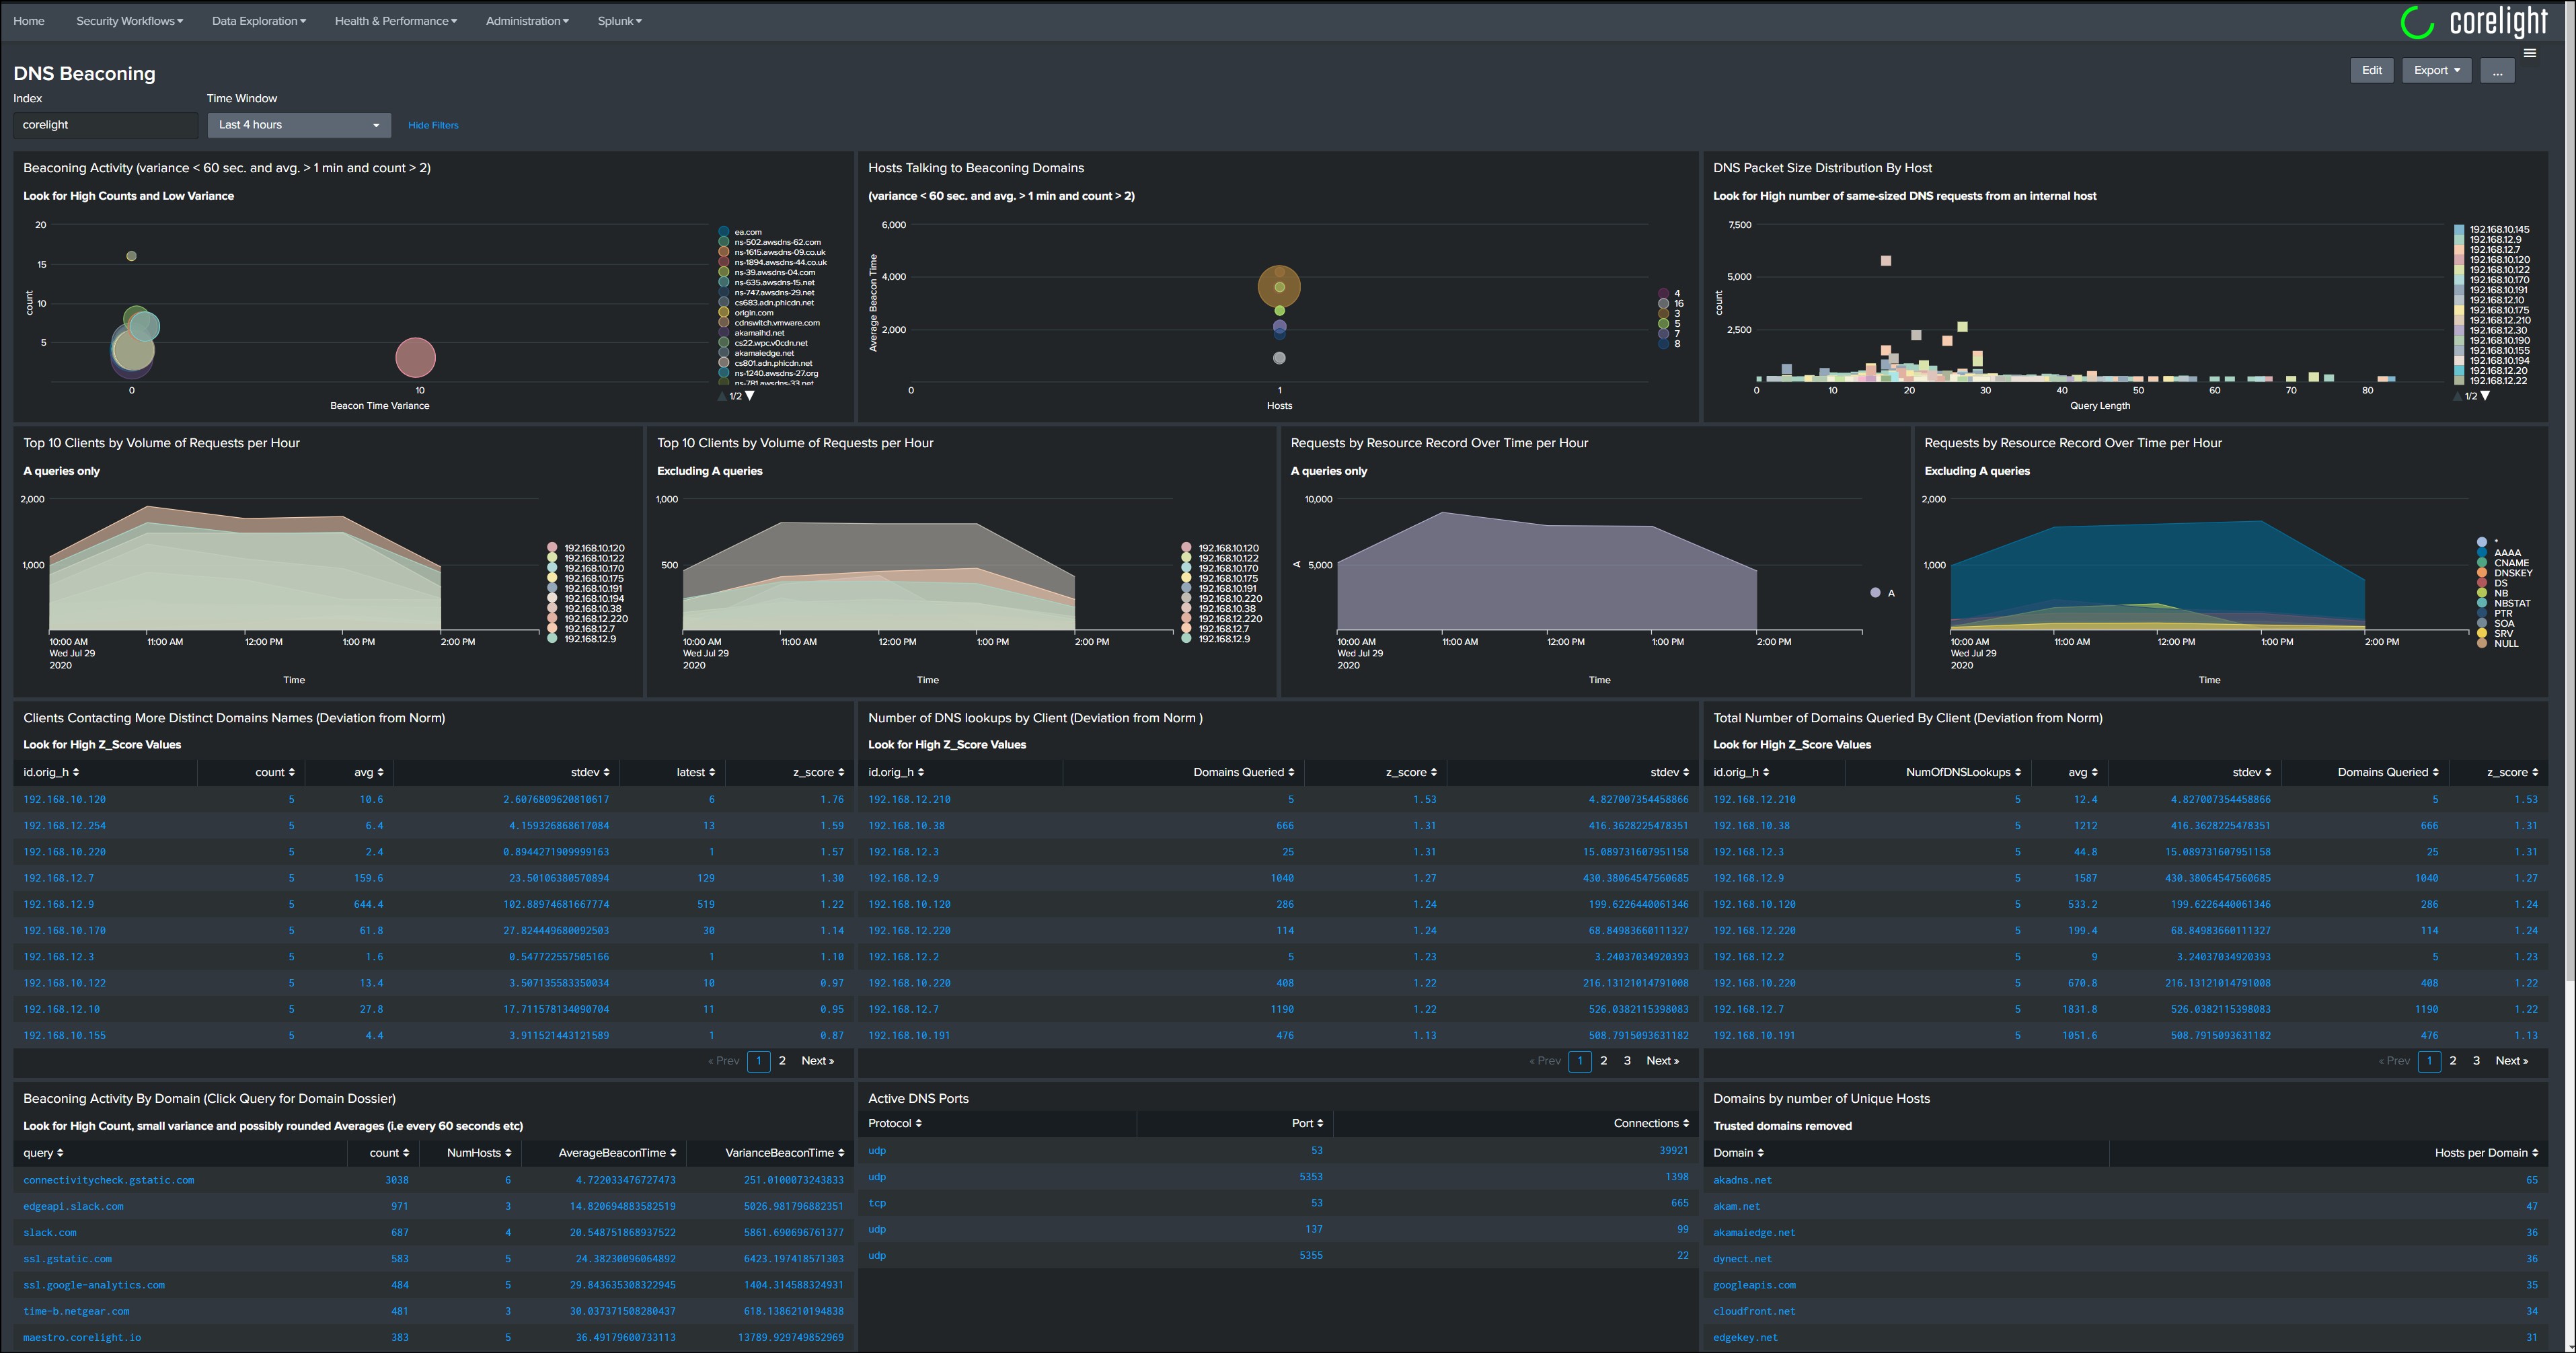 corelight/dashboards-splunk-dns-hunting-beaconing
DNS Dashboard for hunting and identifying beaconing
 corelight/http-stalling-detector
Detect HTTP stalling attacks like slowloris with Bro
 endgameinc/dga_predict
LSTM-based classifier for detecting domain generation algorithm (DGA) domains, with Keras implementations of neural network and bigram models for DNS…

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)