
SysTrace
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
24
tracebyte8/systraceLinux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 blue-yonder/tsfresh
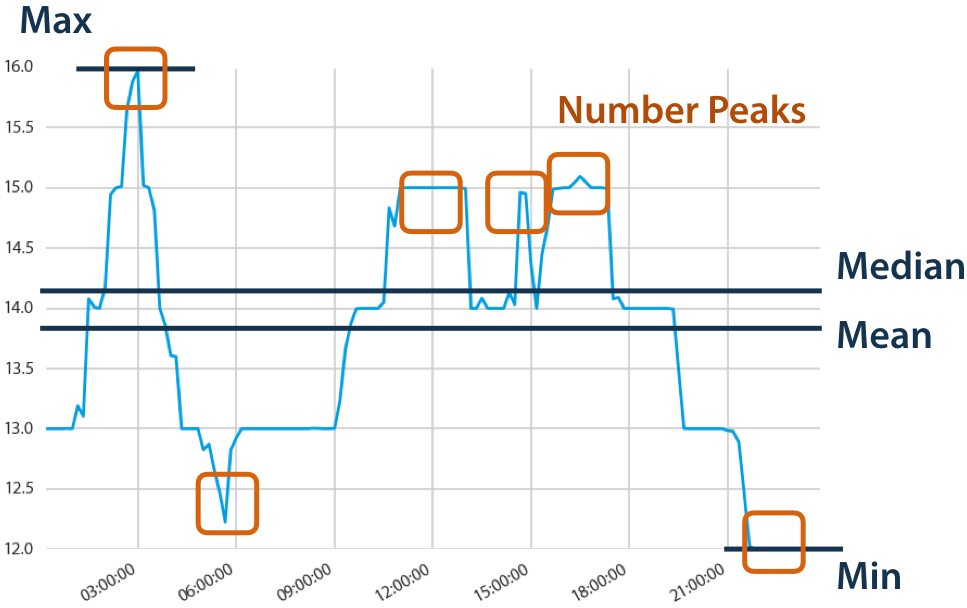
Automatic extraction of relevant features from time series:
 nvidia-nemo/guardrails
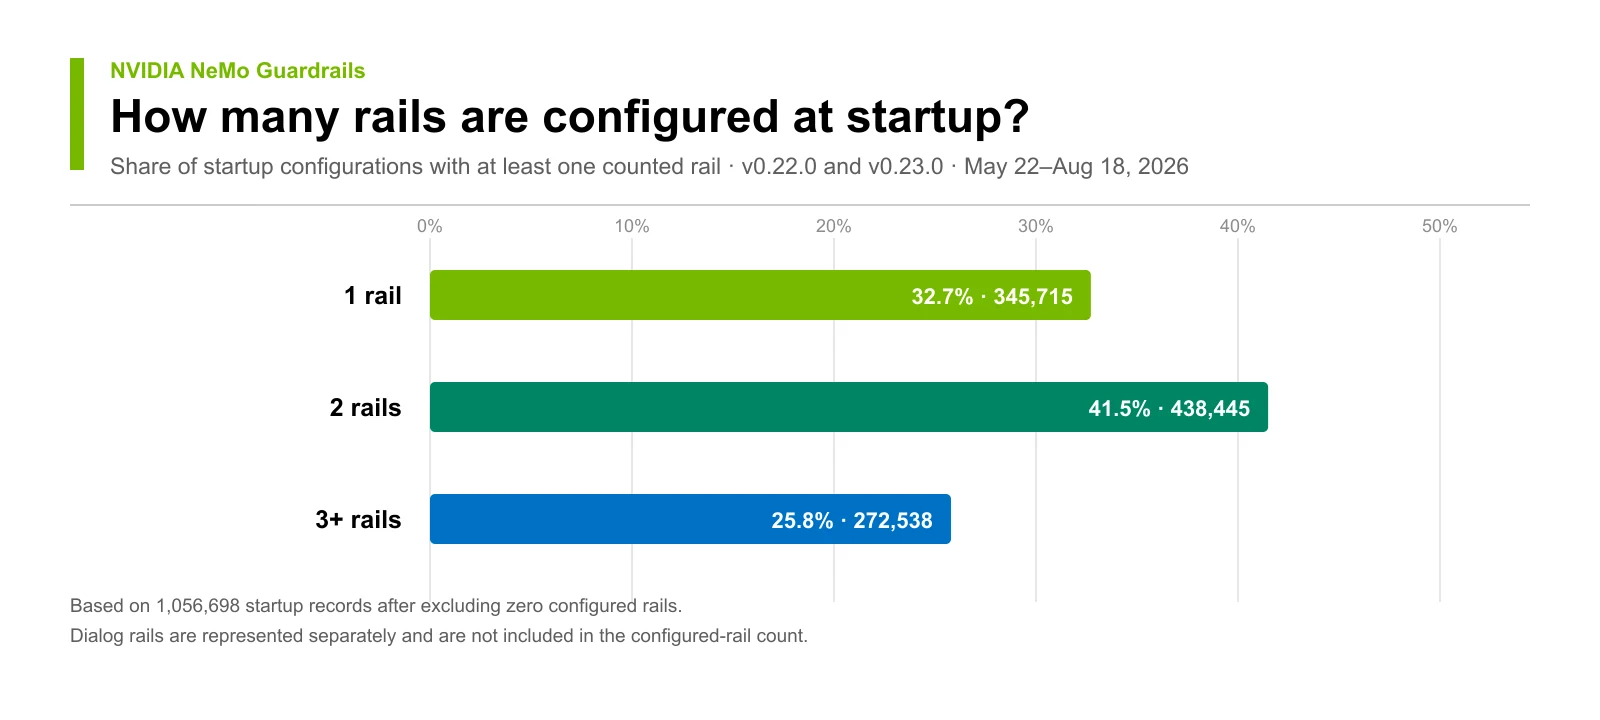
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
 logpai/loglizer
A machine learning toolkit for log-based anomaly detection [ISSRE'16]
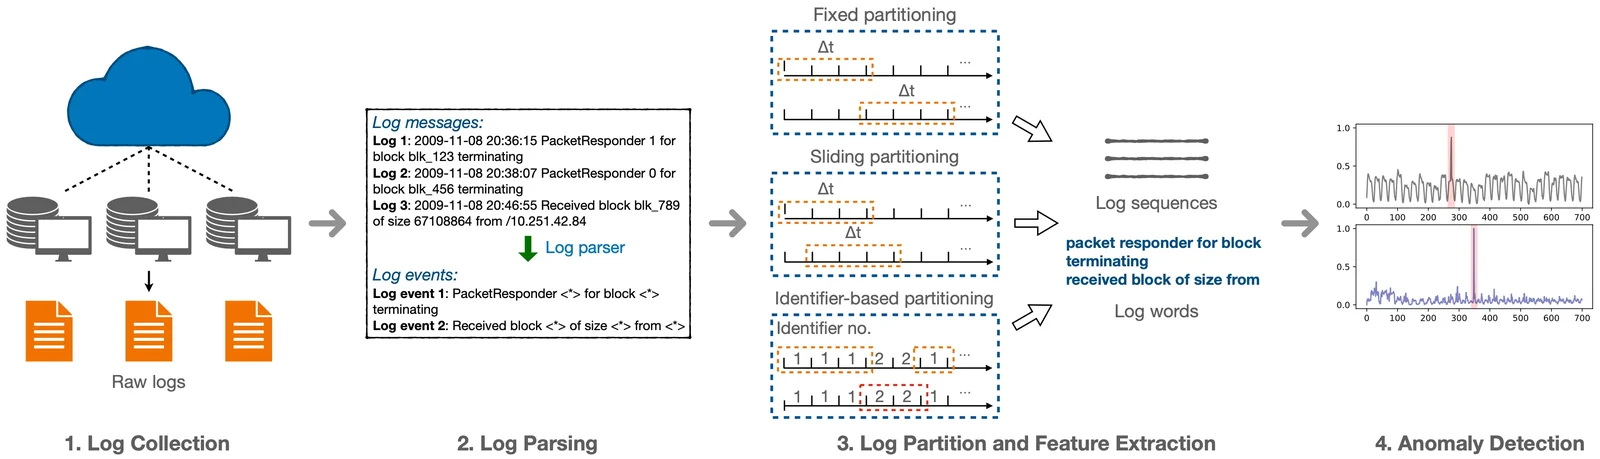 logpai/deep-loglizer
A deep learning toolkit for log-based anomaly detection
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
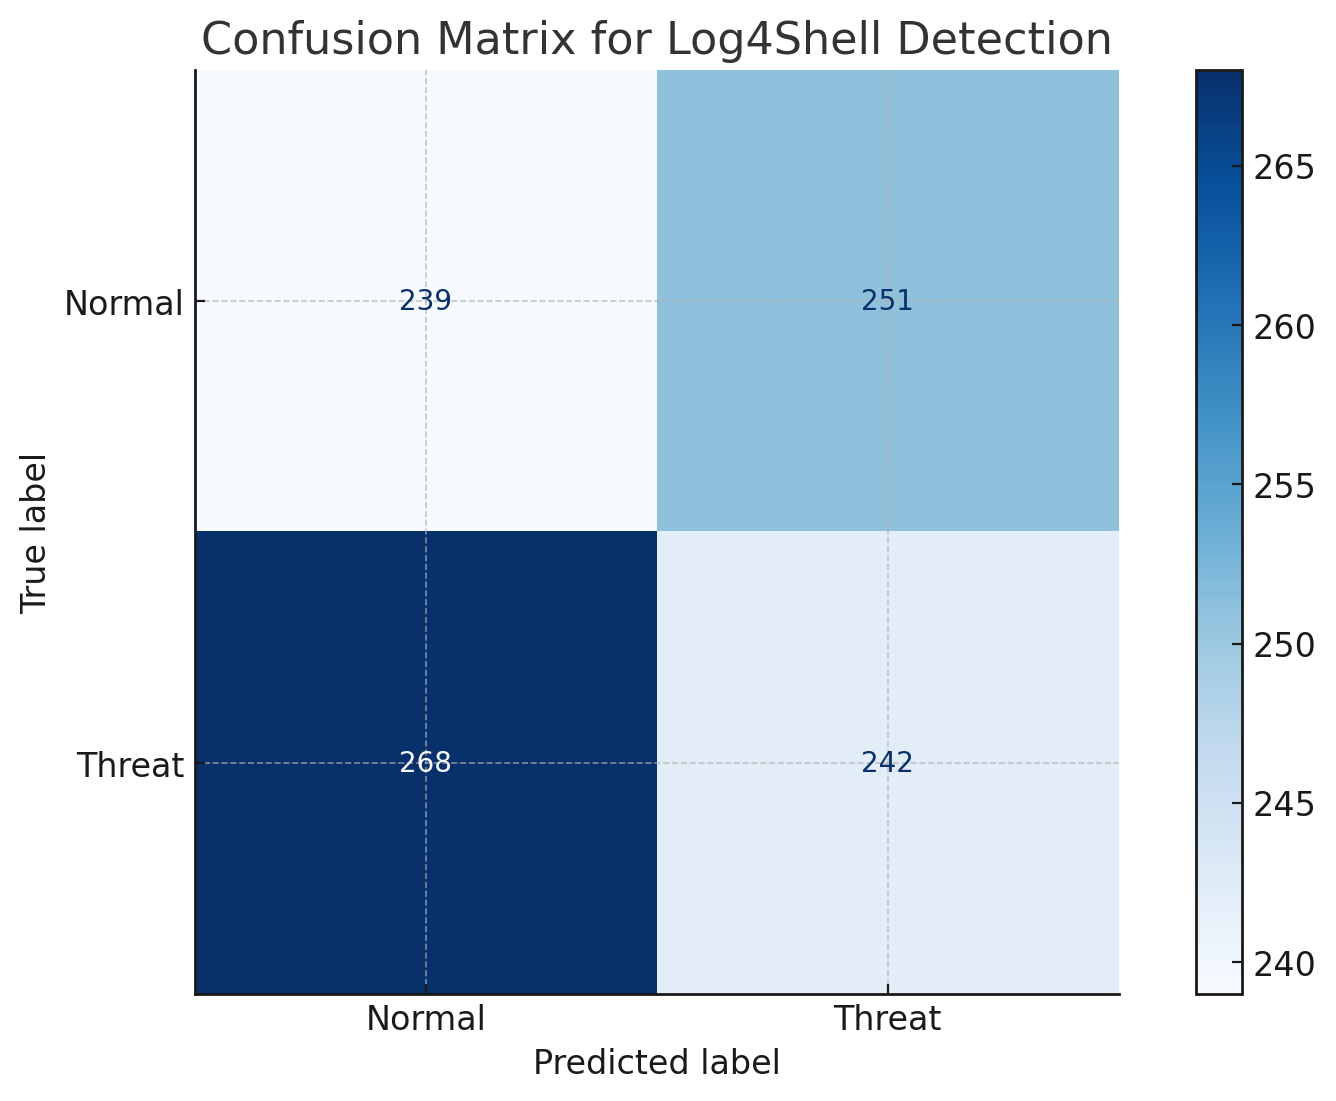 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
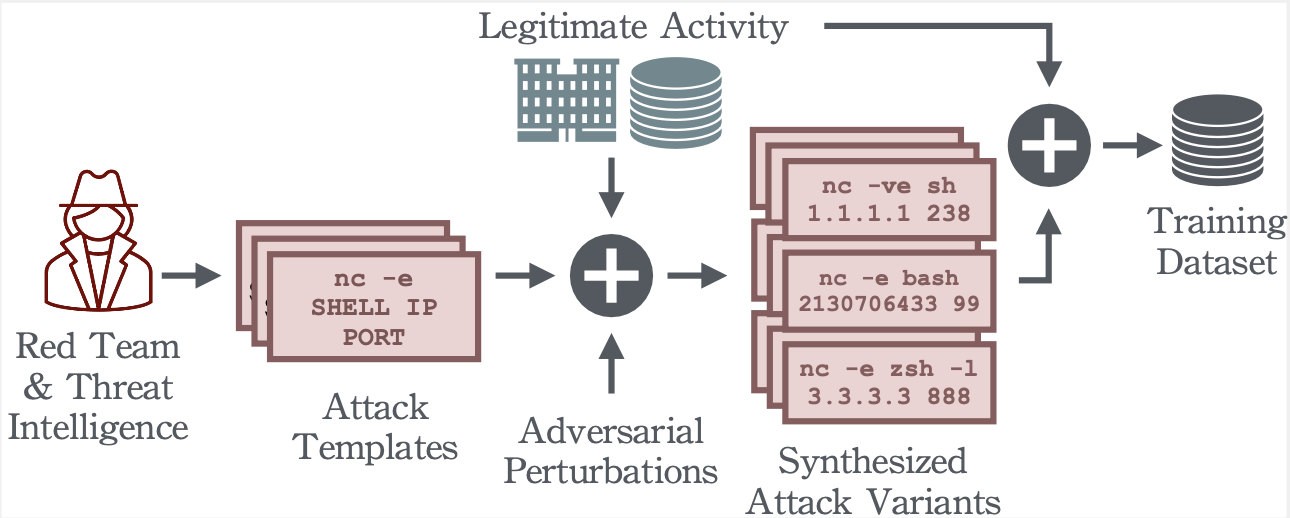 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
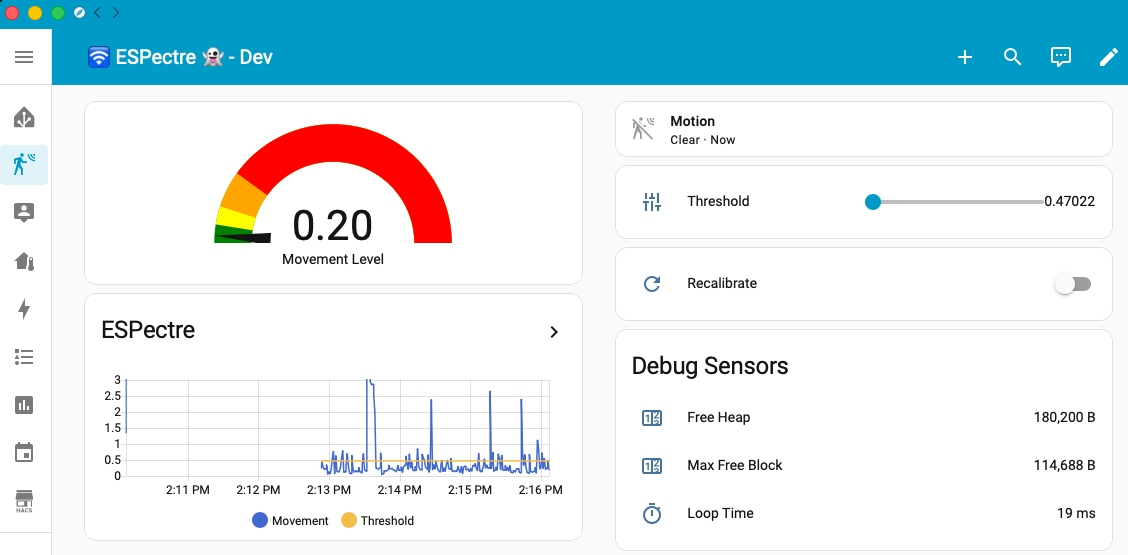 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 yumlembam/insider-threat
Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 nameles-org/nameles
Open source entropy based invalid traffic detection and pre-bid filtering.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring