

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.1k2 days ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
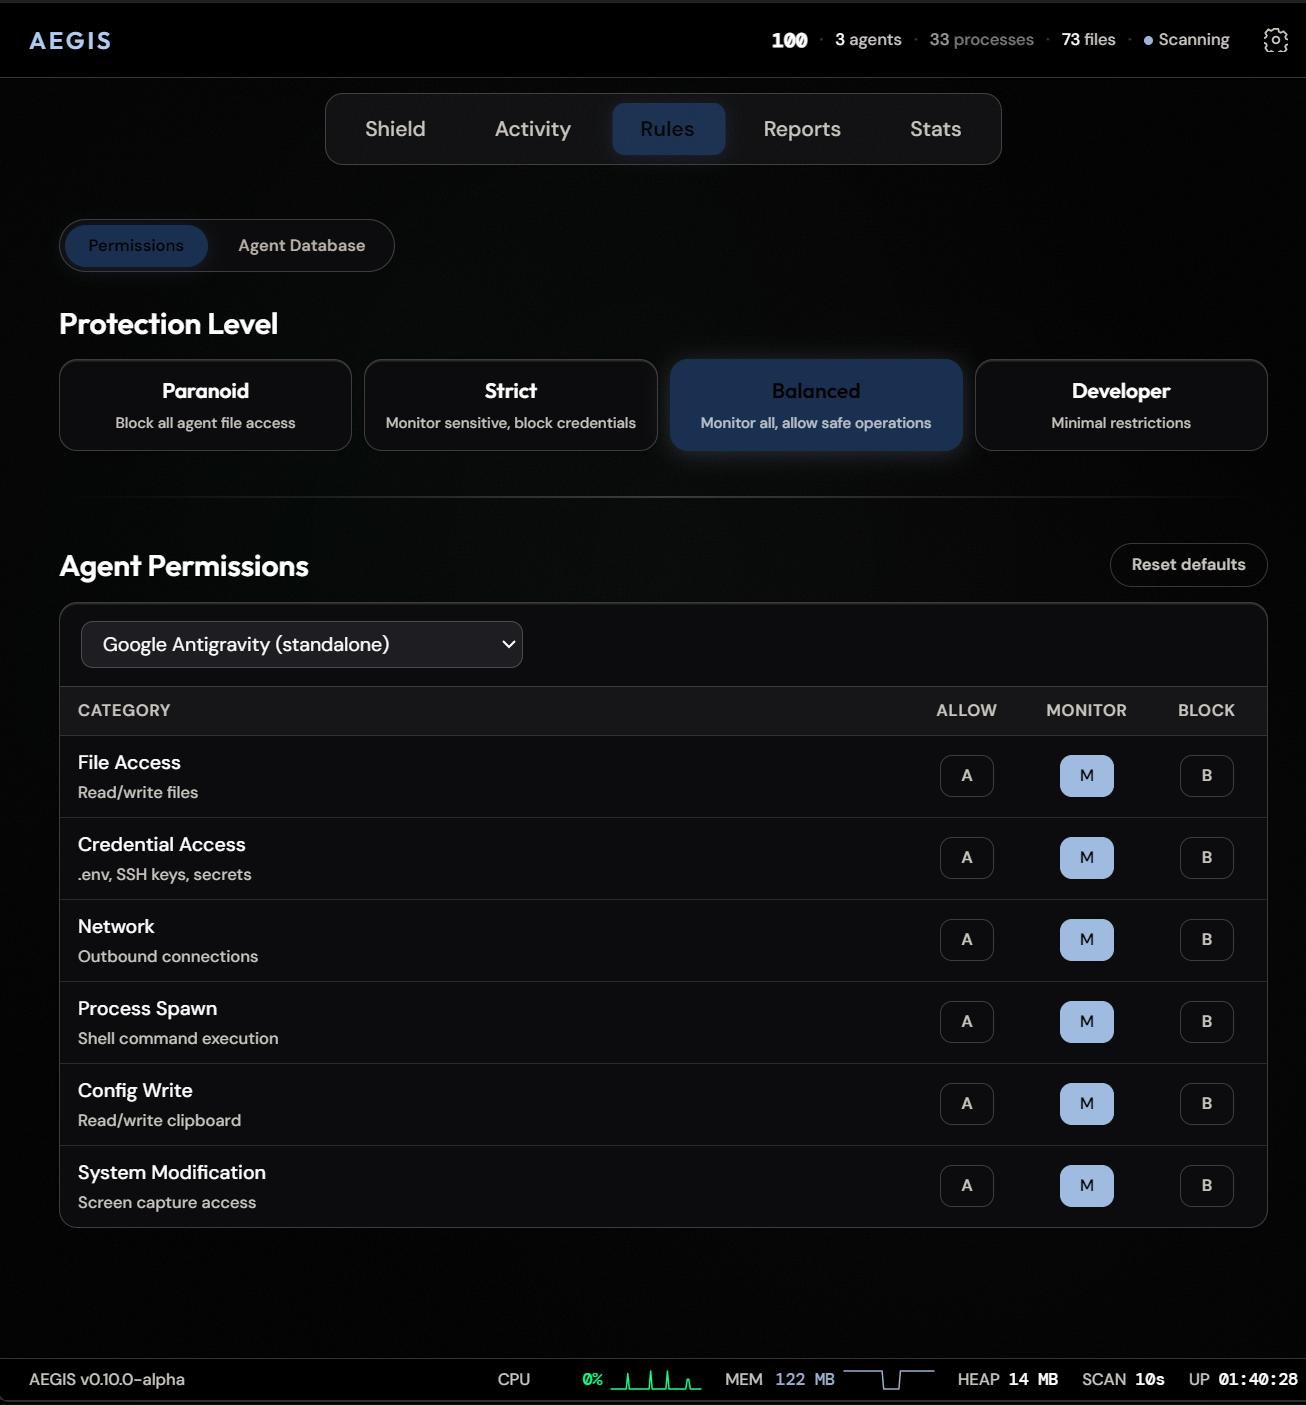 antropos17/aegis
Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
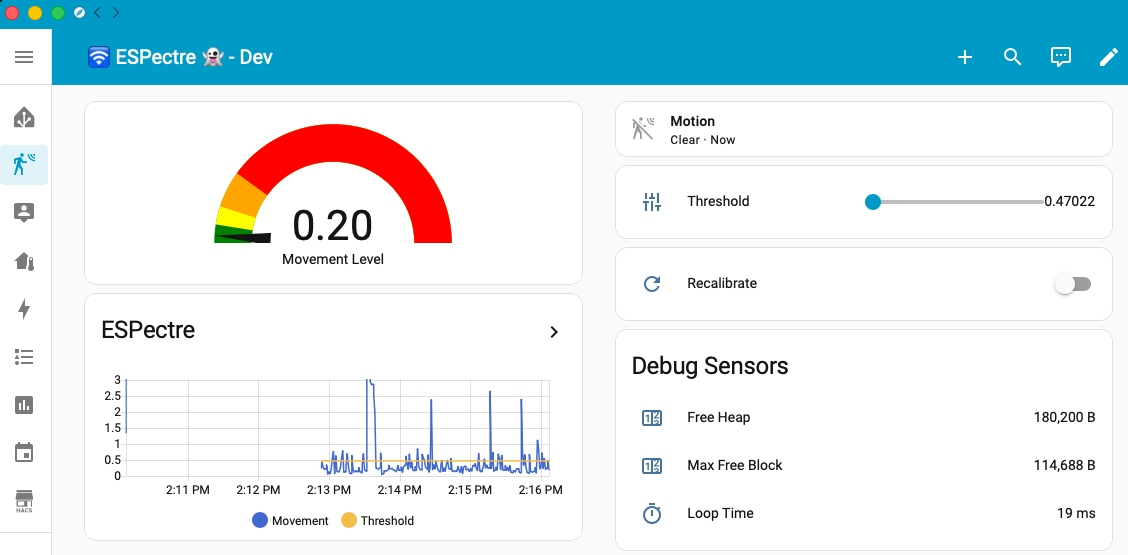 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
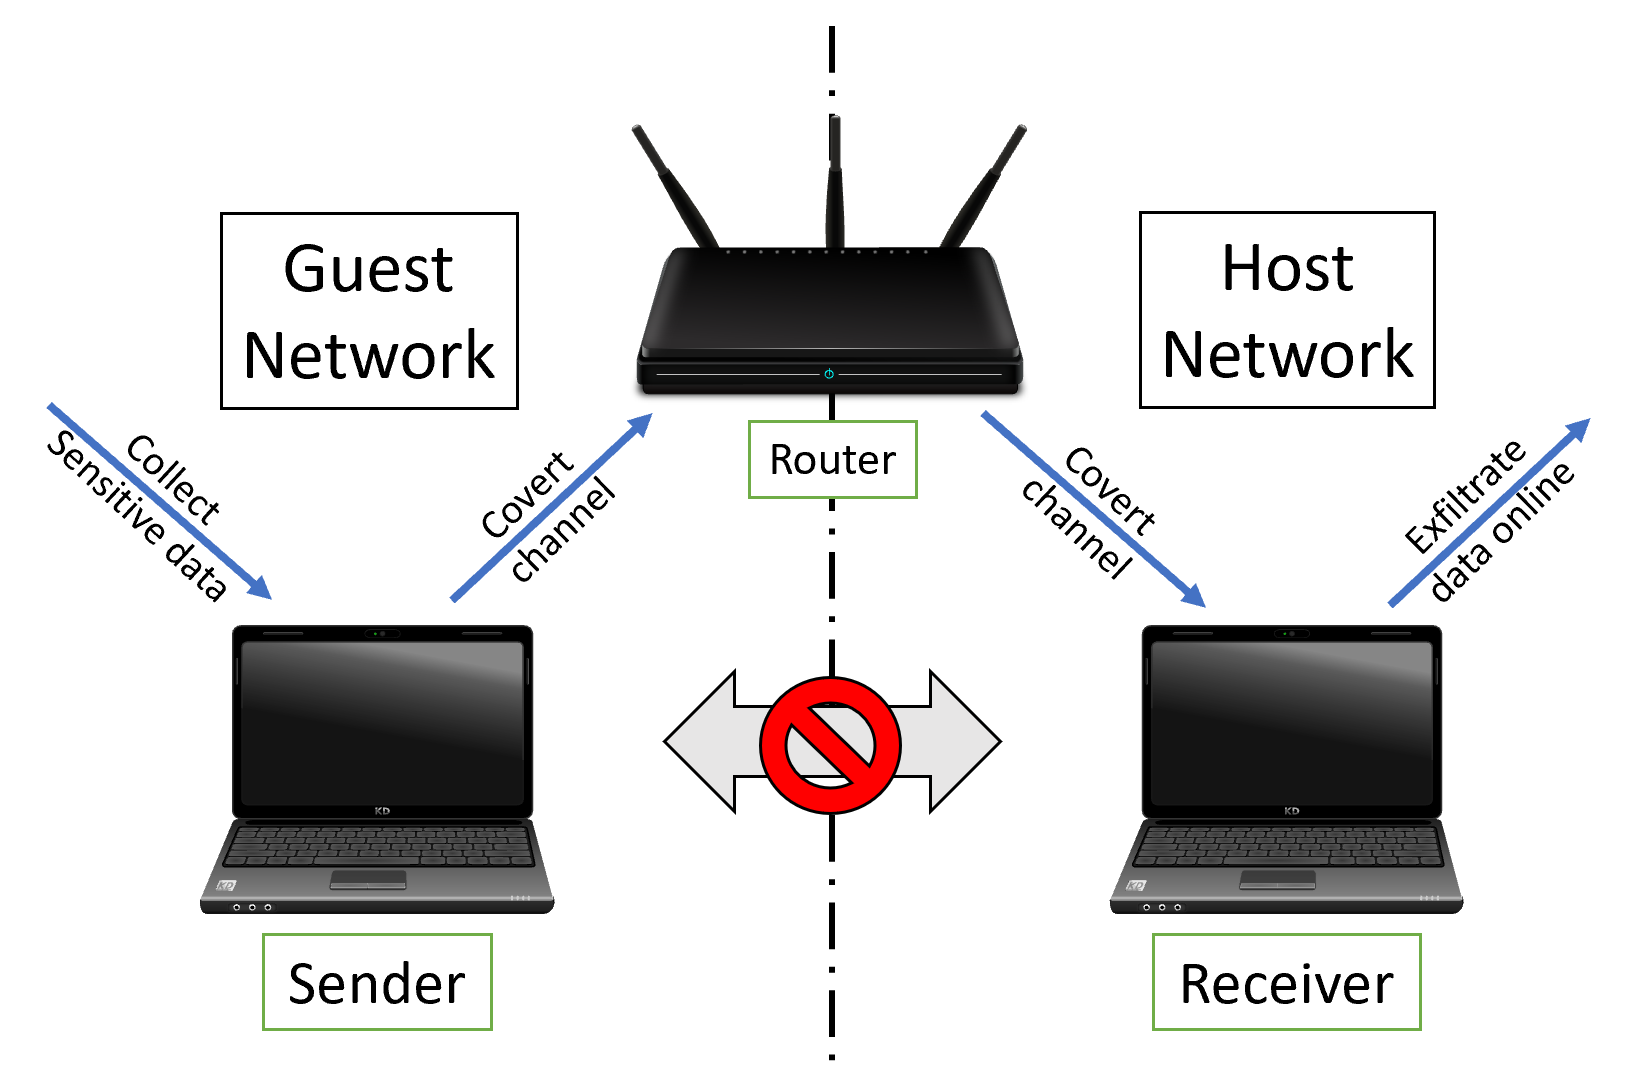 orensv/characterization-and-detection-of-cross-router-covert-channels
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
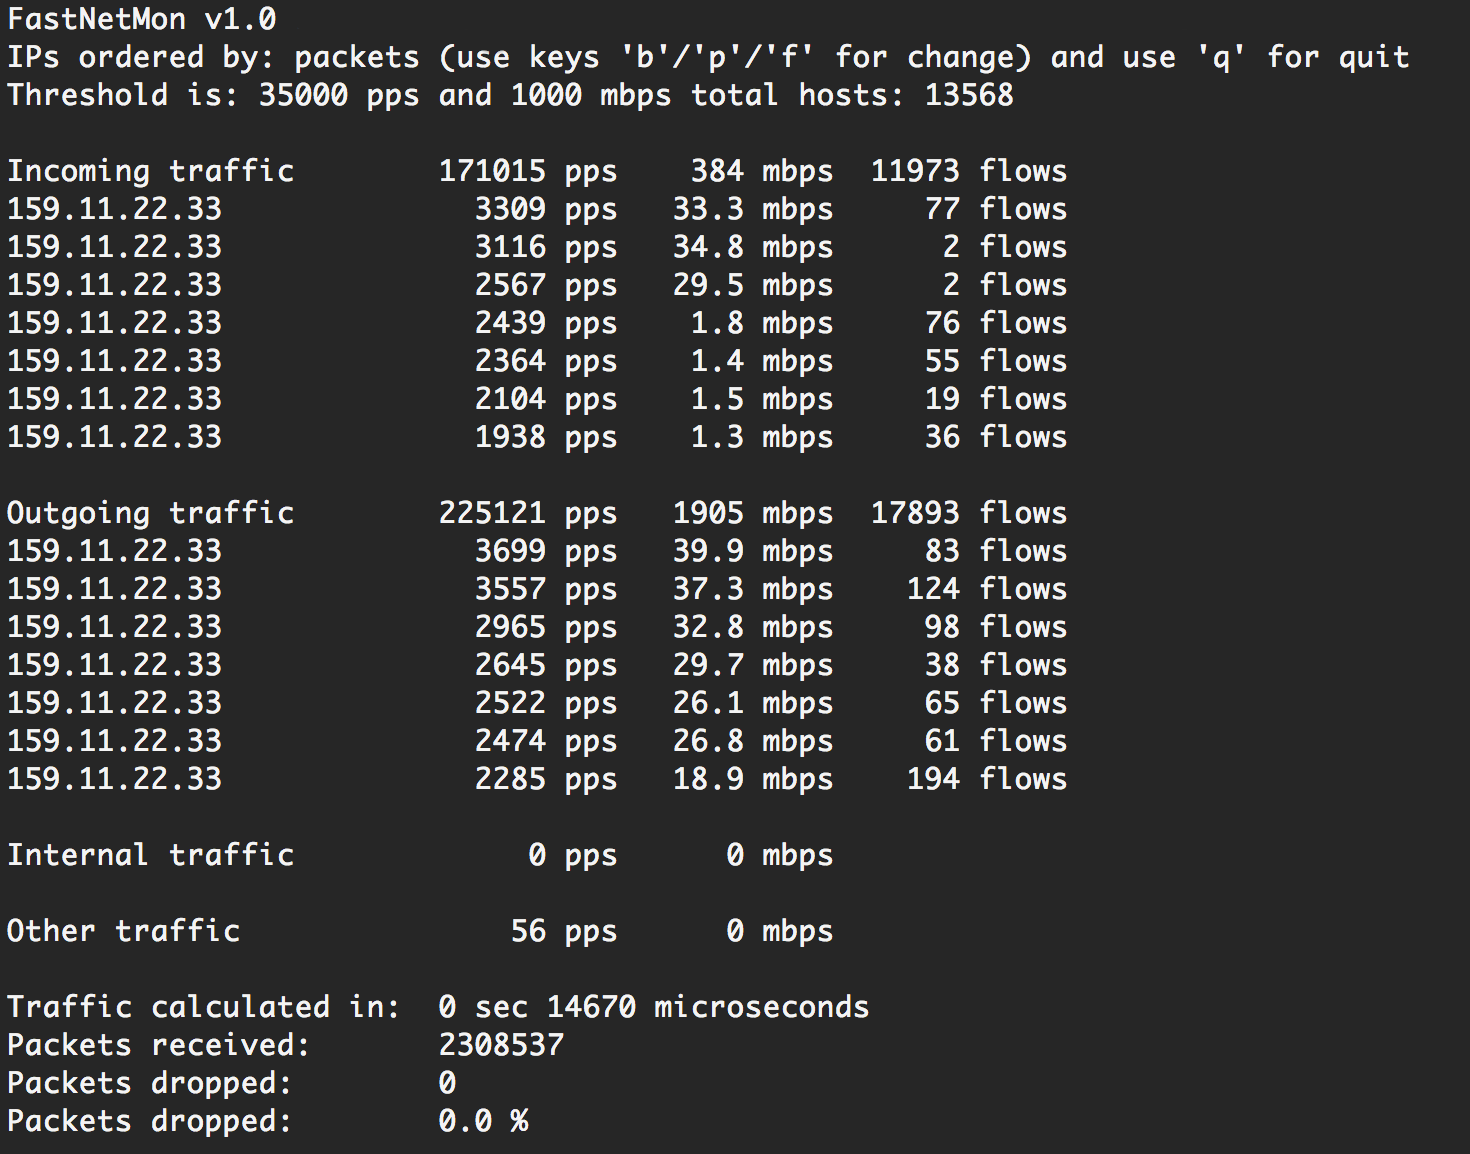 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 nameles-org/nameles
Open source entropy based invalid traffic detection and pre-bid filtering.