
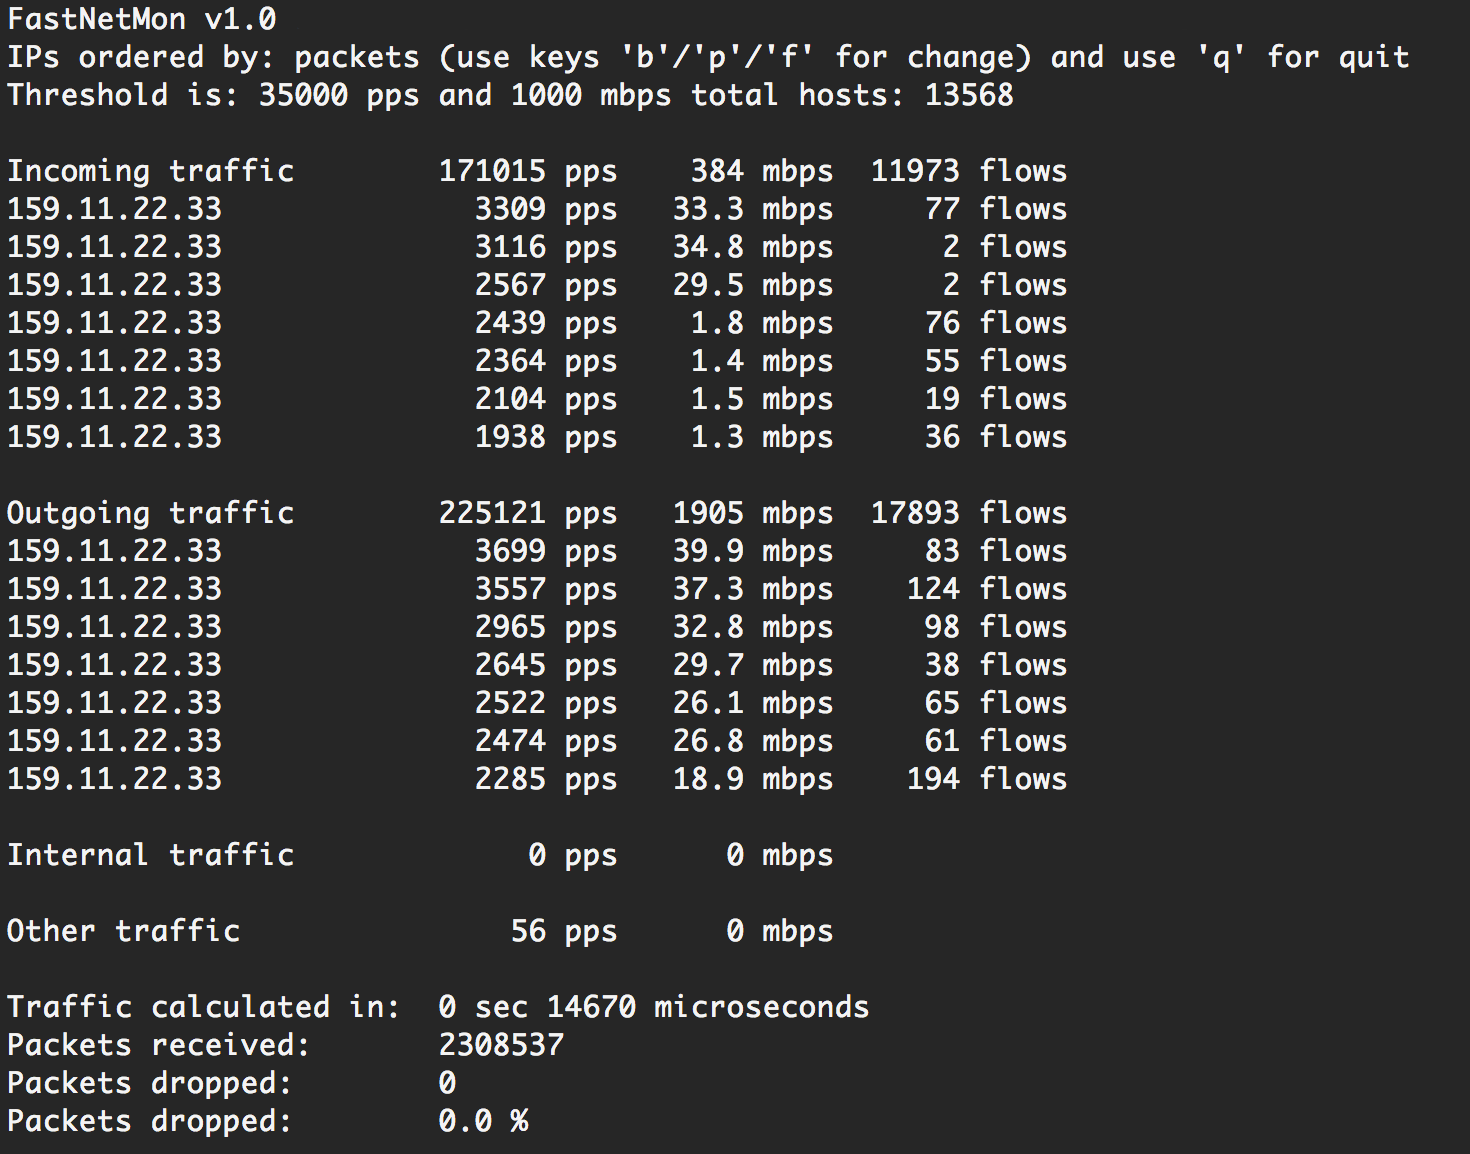
fastnetmon
 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
anomaly-detectionincident-responselog-analysis+5
3.7k1 month ago
pavel-odintsov/fastnetmonVery fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
 corelight/conn-burst
A Bro package to identify connections that are bursting (lots of data and transferring quickly).
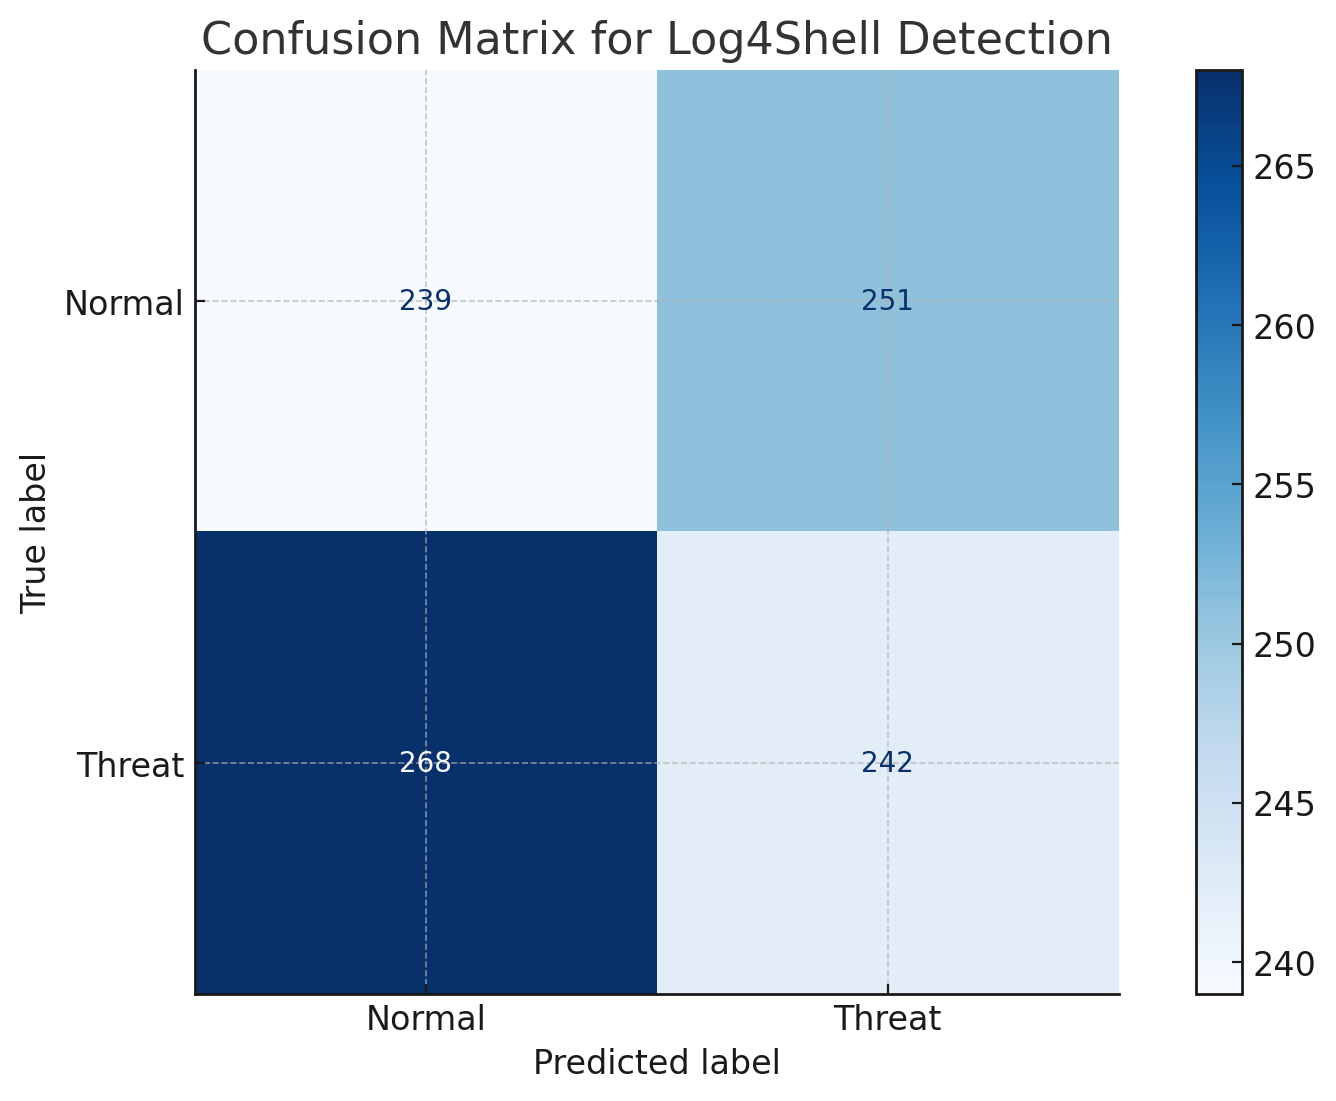 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…