the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…

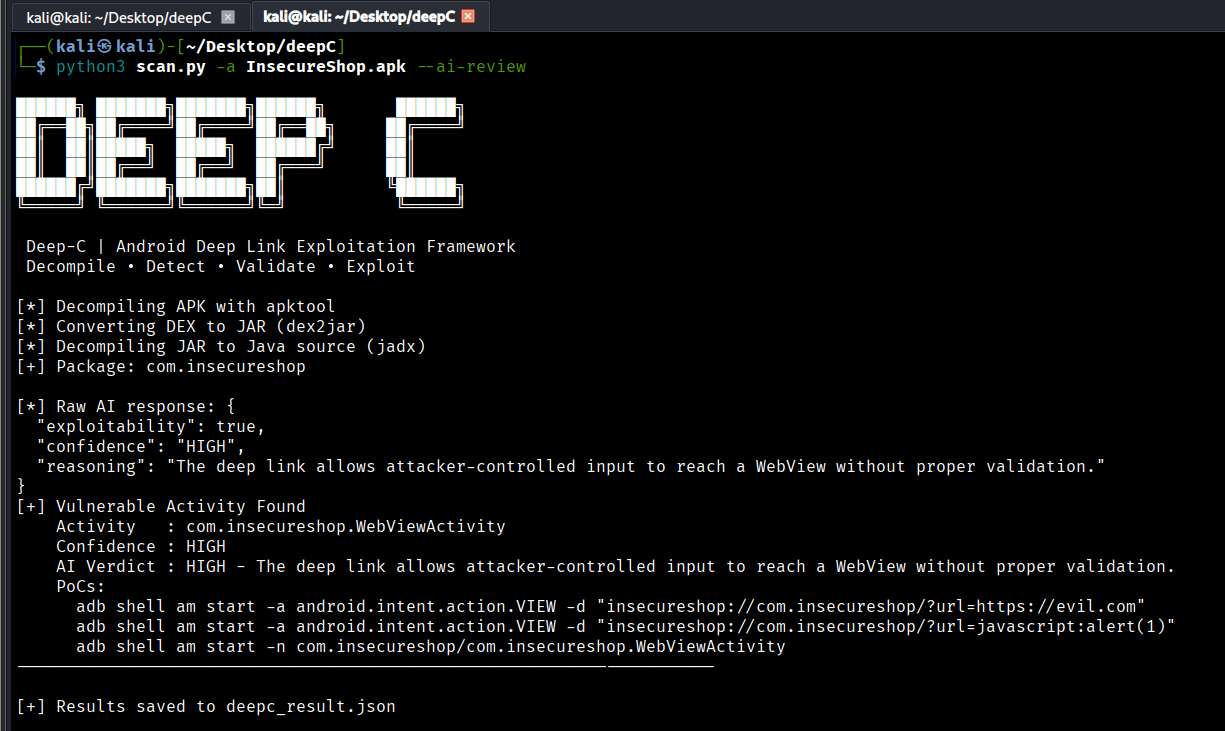
Android deeplink misconfiguration detector and exploitation tool

Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…

Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…


Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…

Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…

ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.

ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.

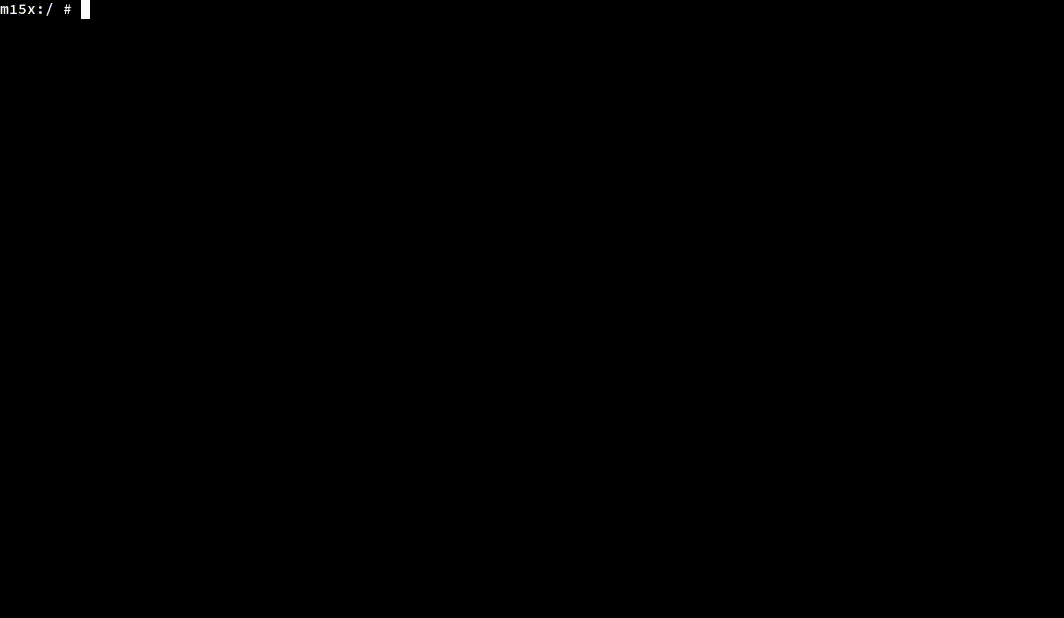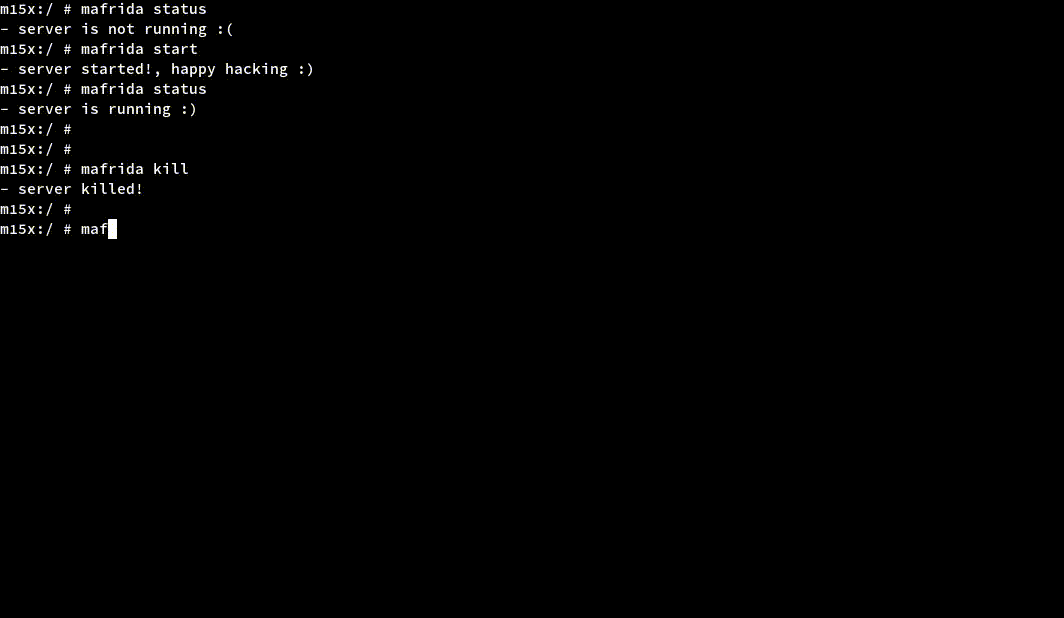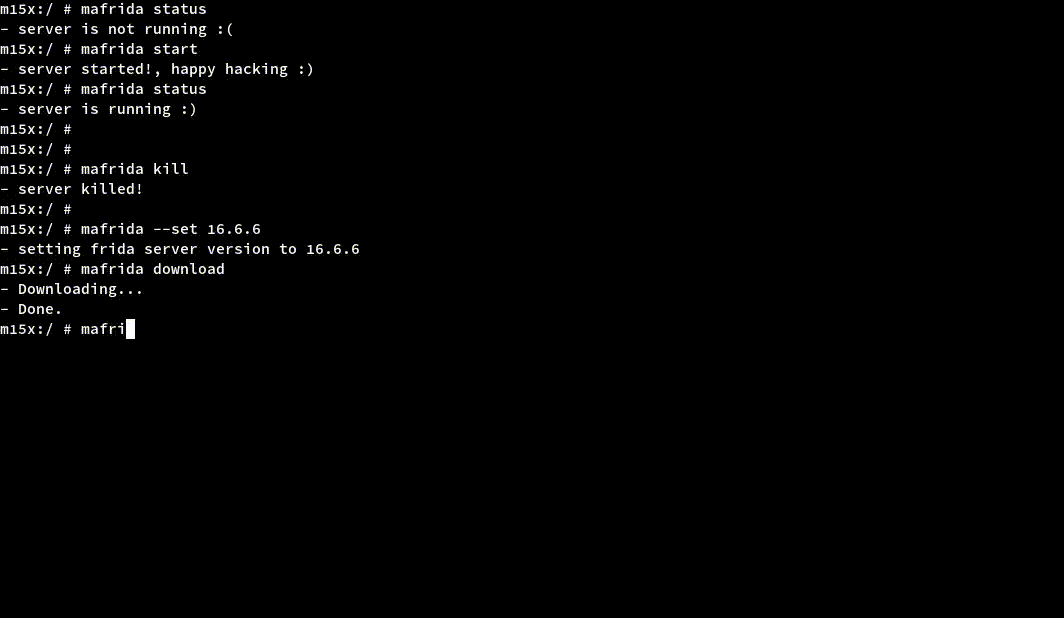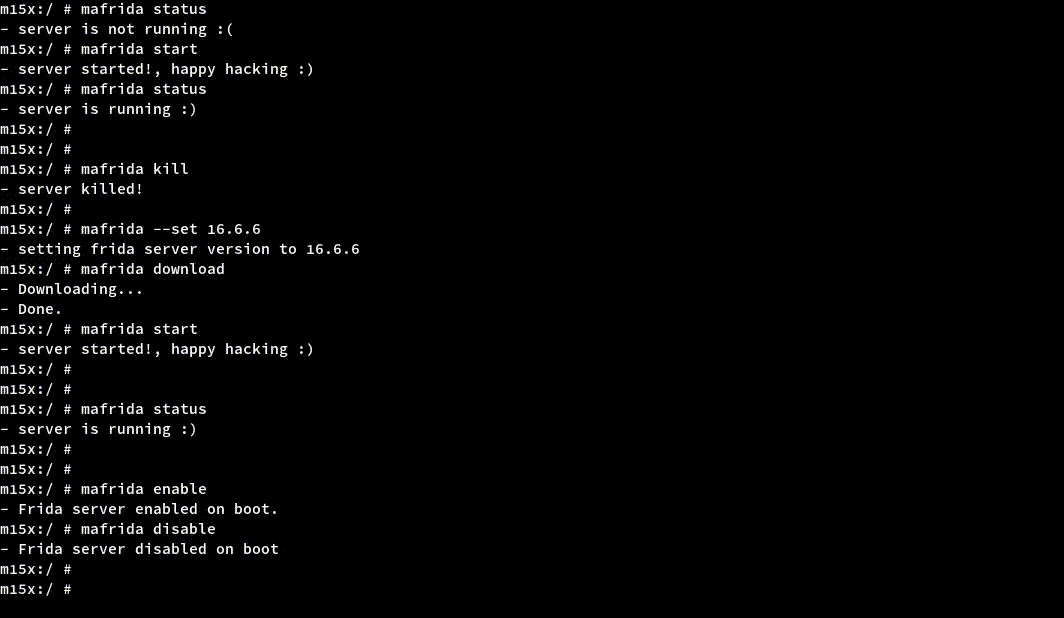
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…

This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…

This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…