
cve-2015-1538-1
 jduck/cve-2015-1538-1
Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
android-securitybinary-exploitationexploitation+3
205
jduck/cve-2015-1538-1Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
 hhj4ck/cve-2016-2067
GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 k0mraid3/k0mraid3s-system-shell-prebuilt
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
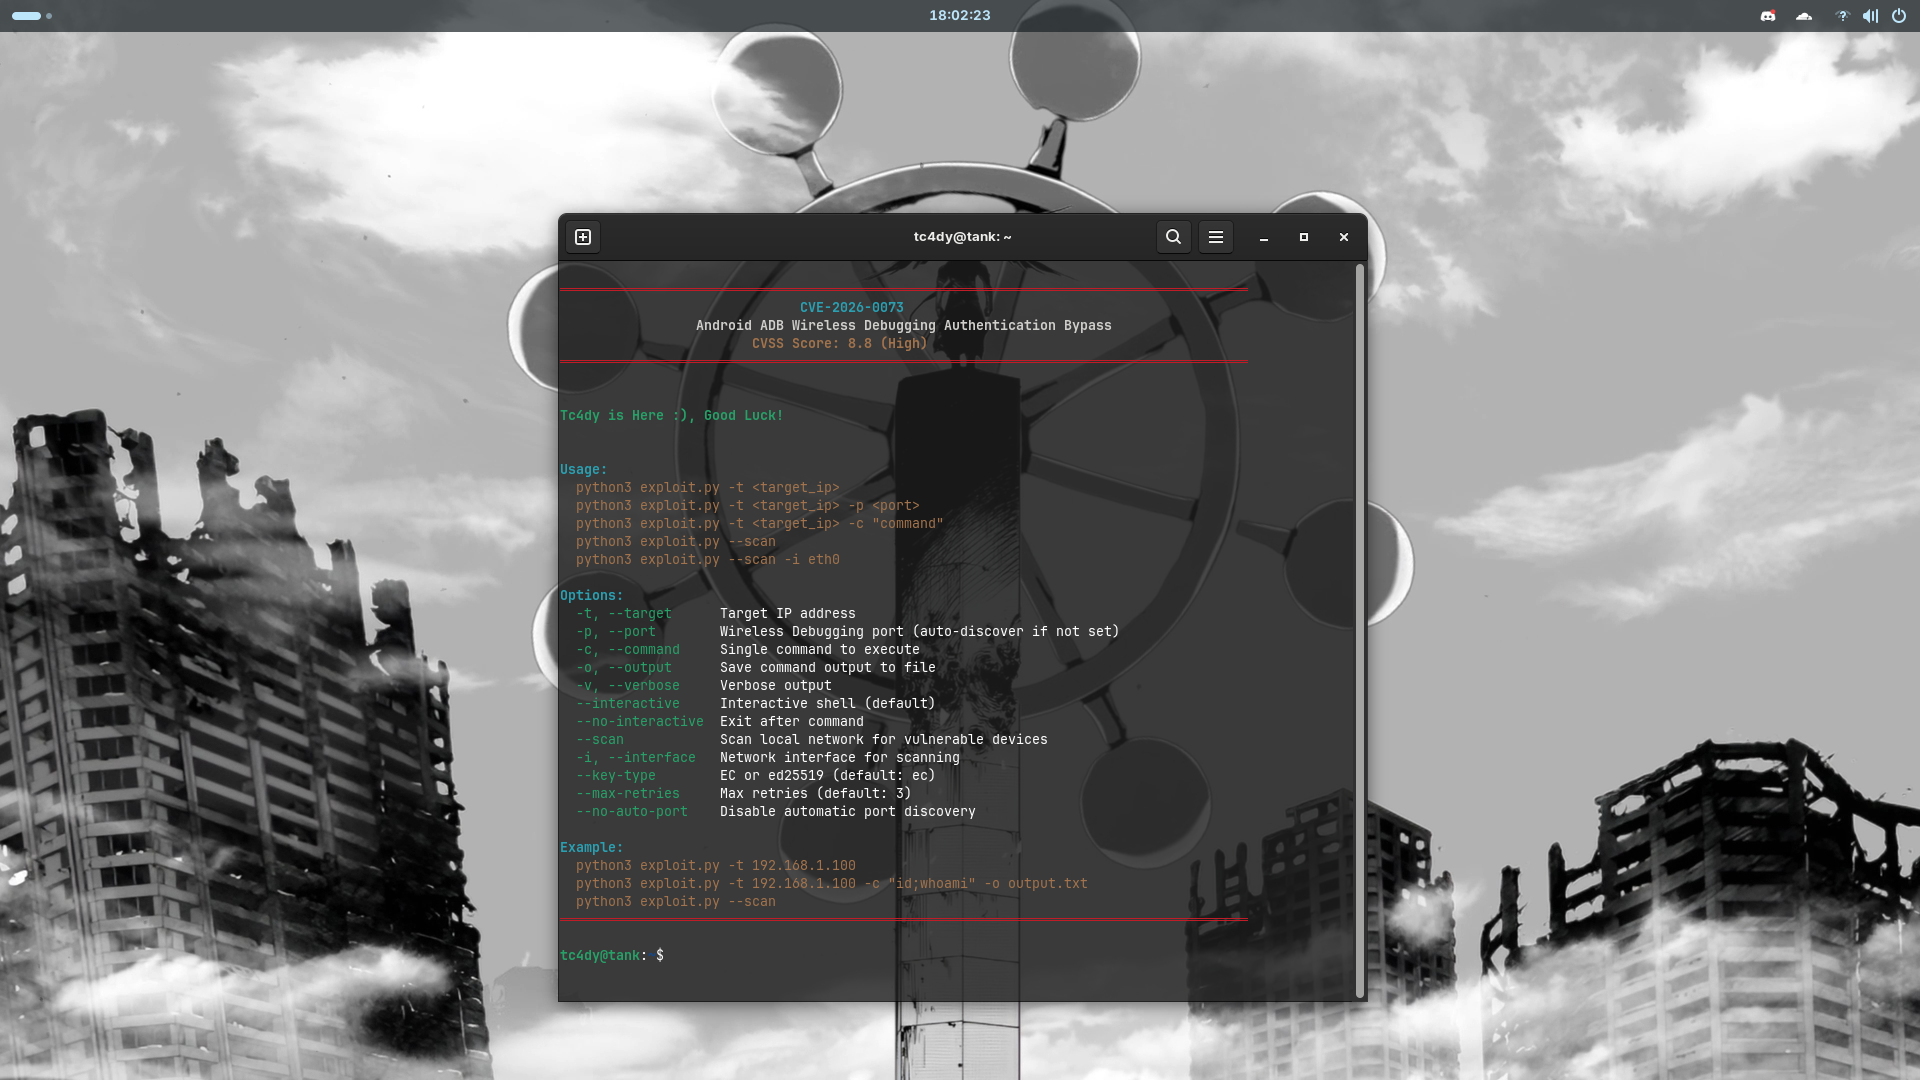 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 jcalabres/root-exploit-pixel3
Local privilege escalation exploit for Pixel 3 (CVE-2020-0041) that disables SELinux and spawns a root shell via kernel memory corruption and offset…
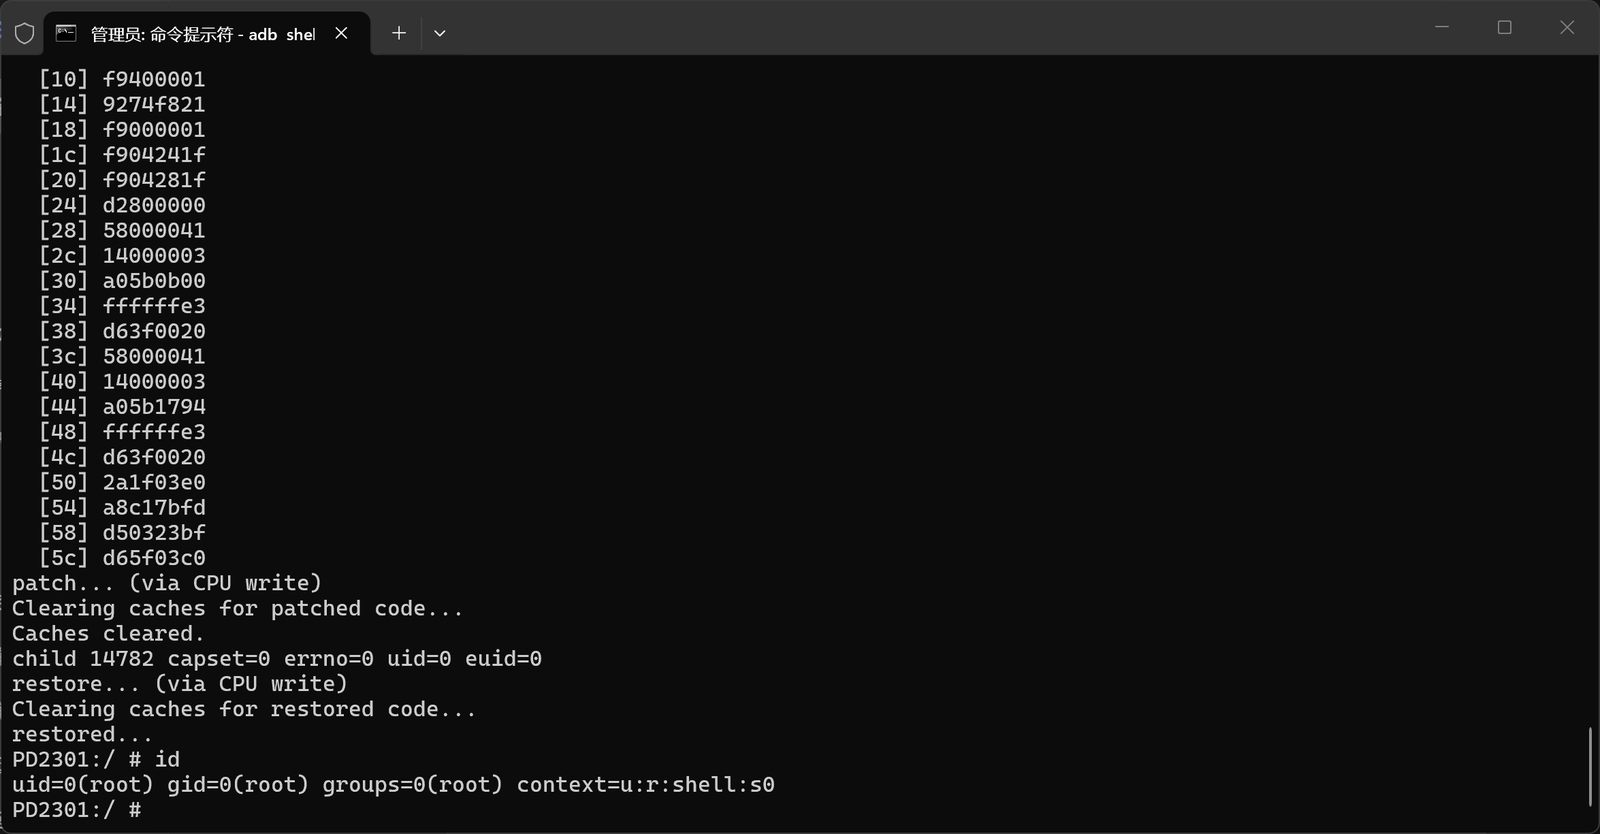 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.