

Archived
android-forensics
 nowsecure/android-forensics
Open source Android Forensics app and framework
android-securitydata-recoverydigital-forensics+2
397
nowsecure/android-forensicsOpen source Android Forensics app and framework
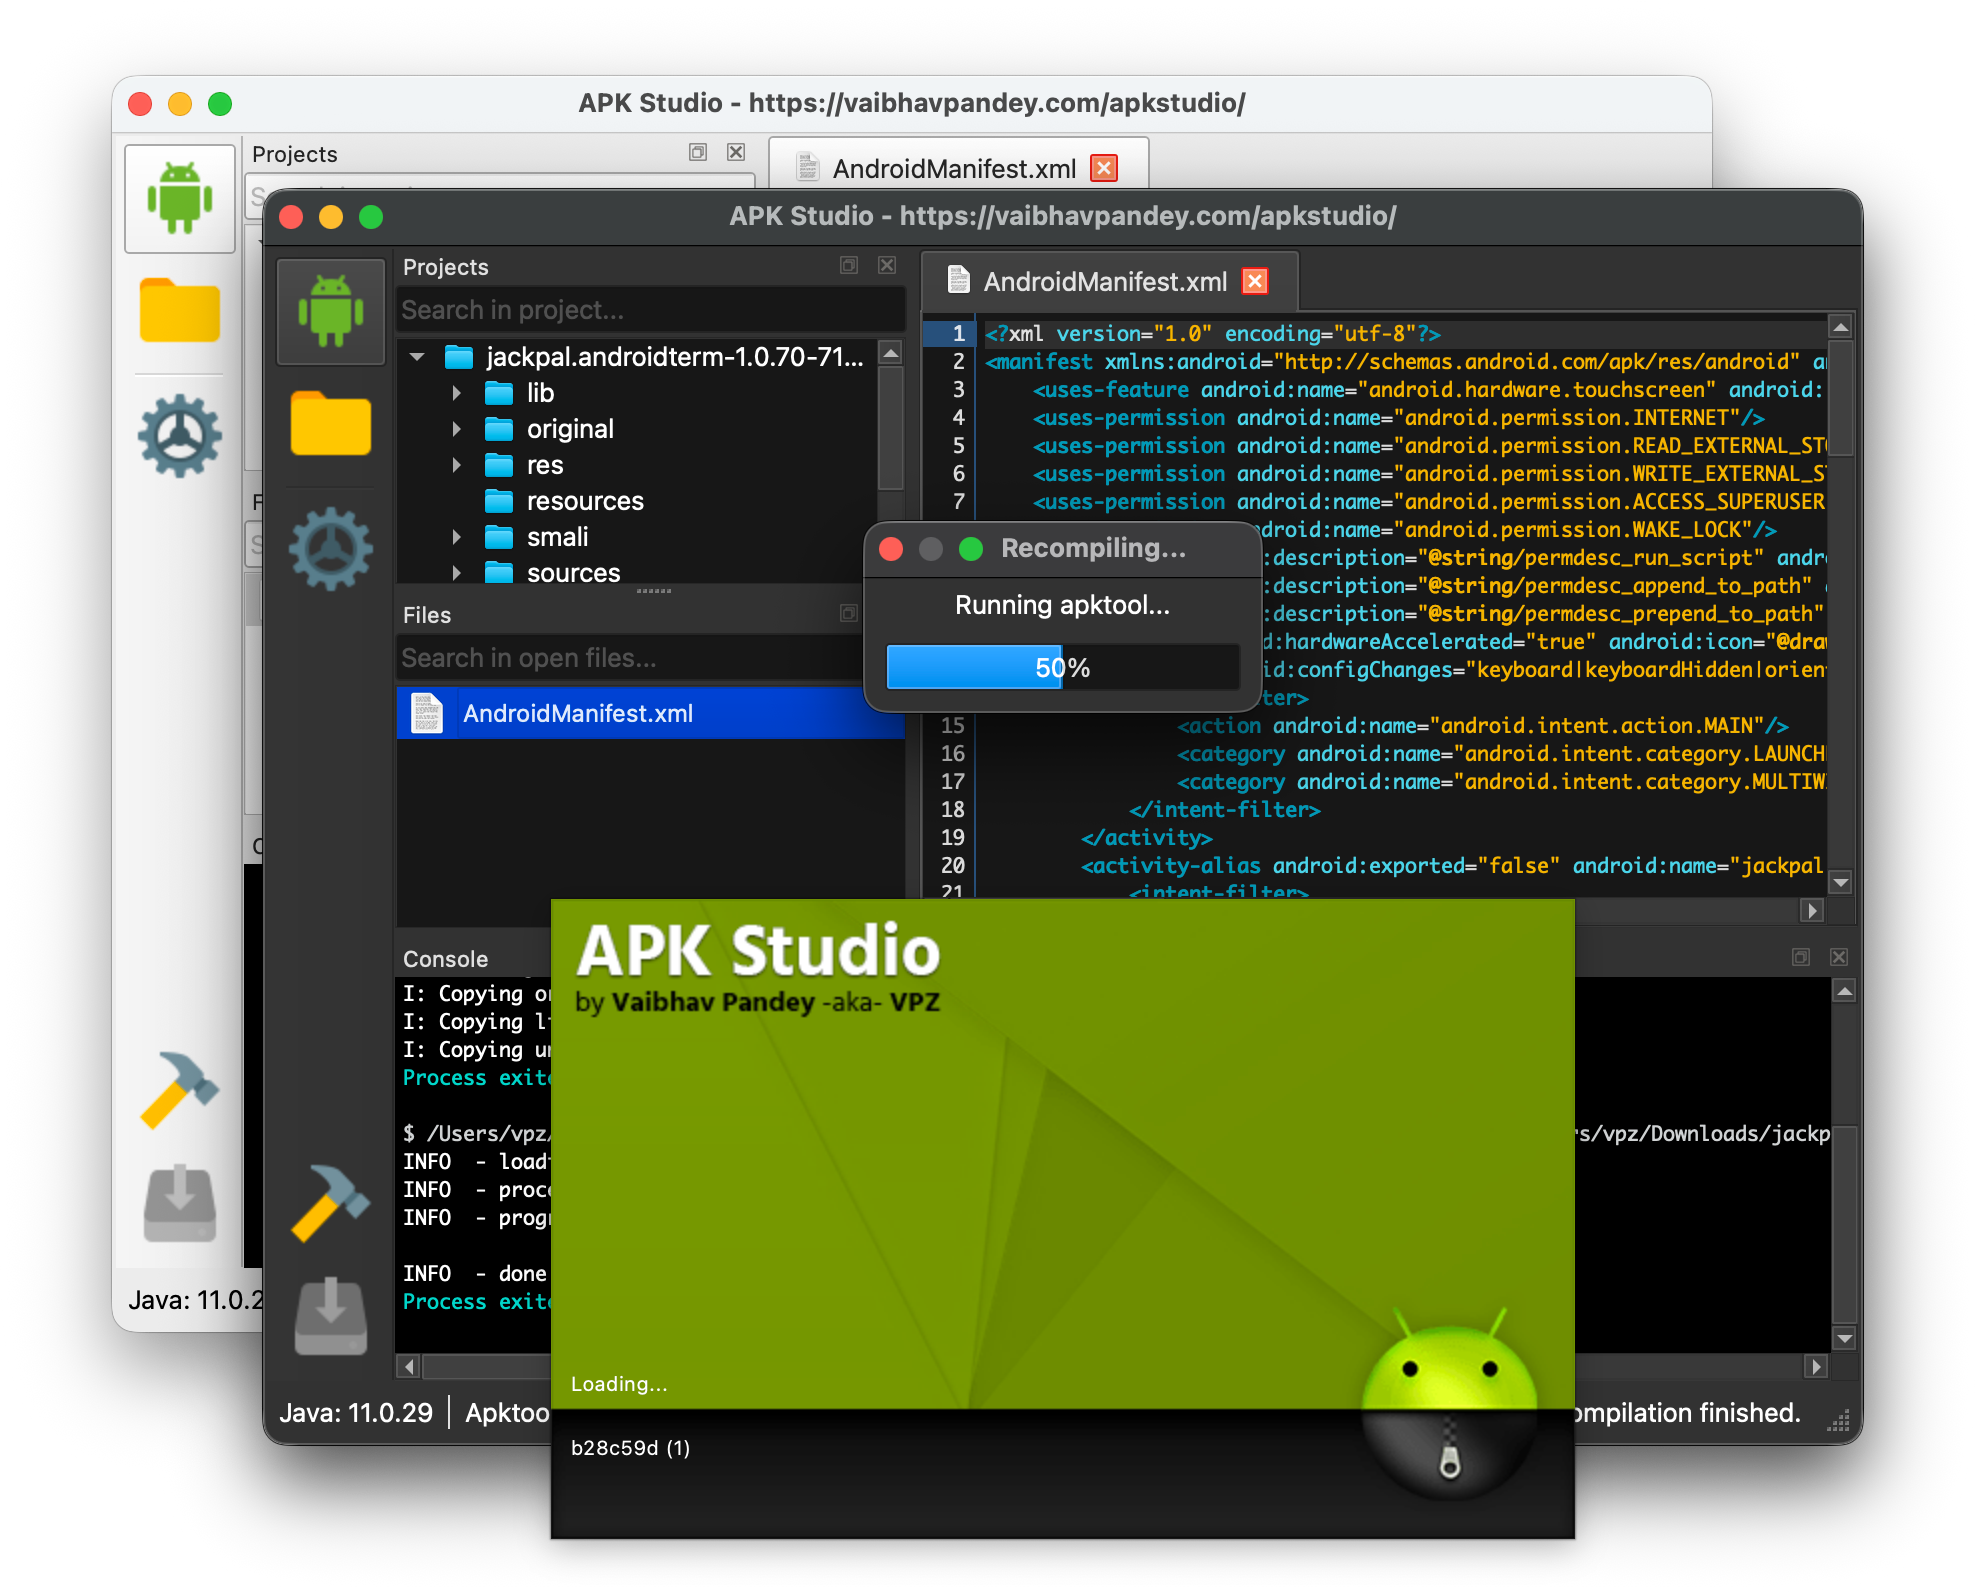 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 donctl/sandy
Release of the sandy framework.
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
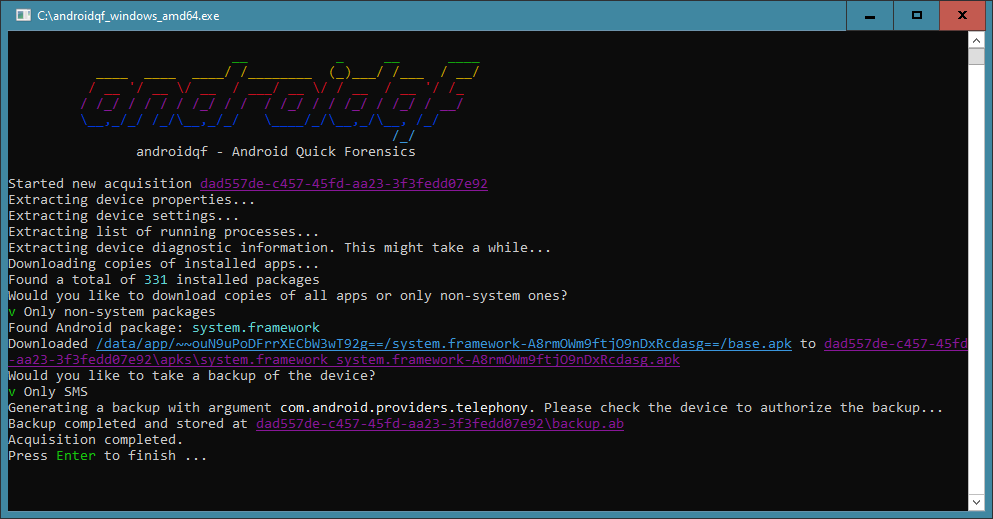 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 kimocoder/android_kernel_oneplus_avicii
OnePlus Nord (avicii) NeverSettle Kernel Source
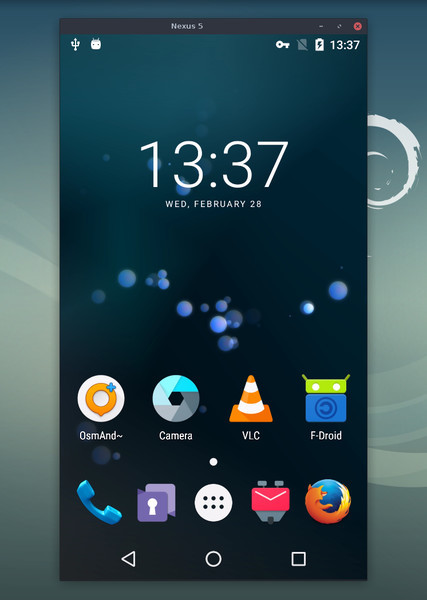 genymobile/scrcpy
Display and control your Android device
 linkedin/qark
Tool to look for several security related Android application vulnerabilities
 petalrain224/cve-2026-43499-redmi-turbo5
Use CVE-2026-43499 on Redmi Turbo 5 to escalate privilege
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
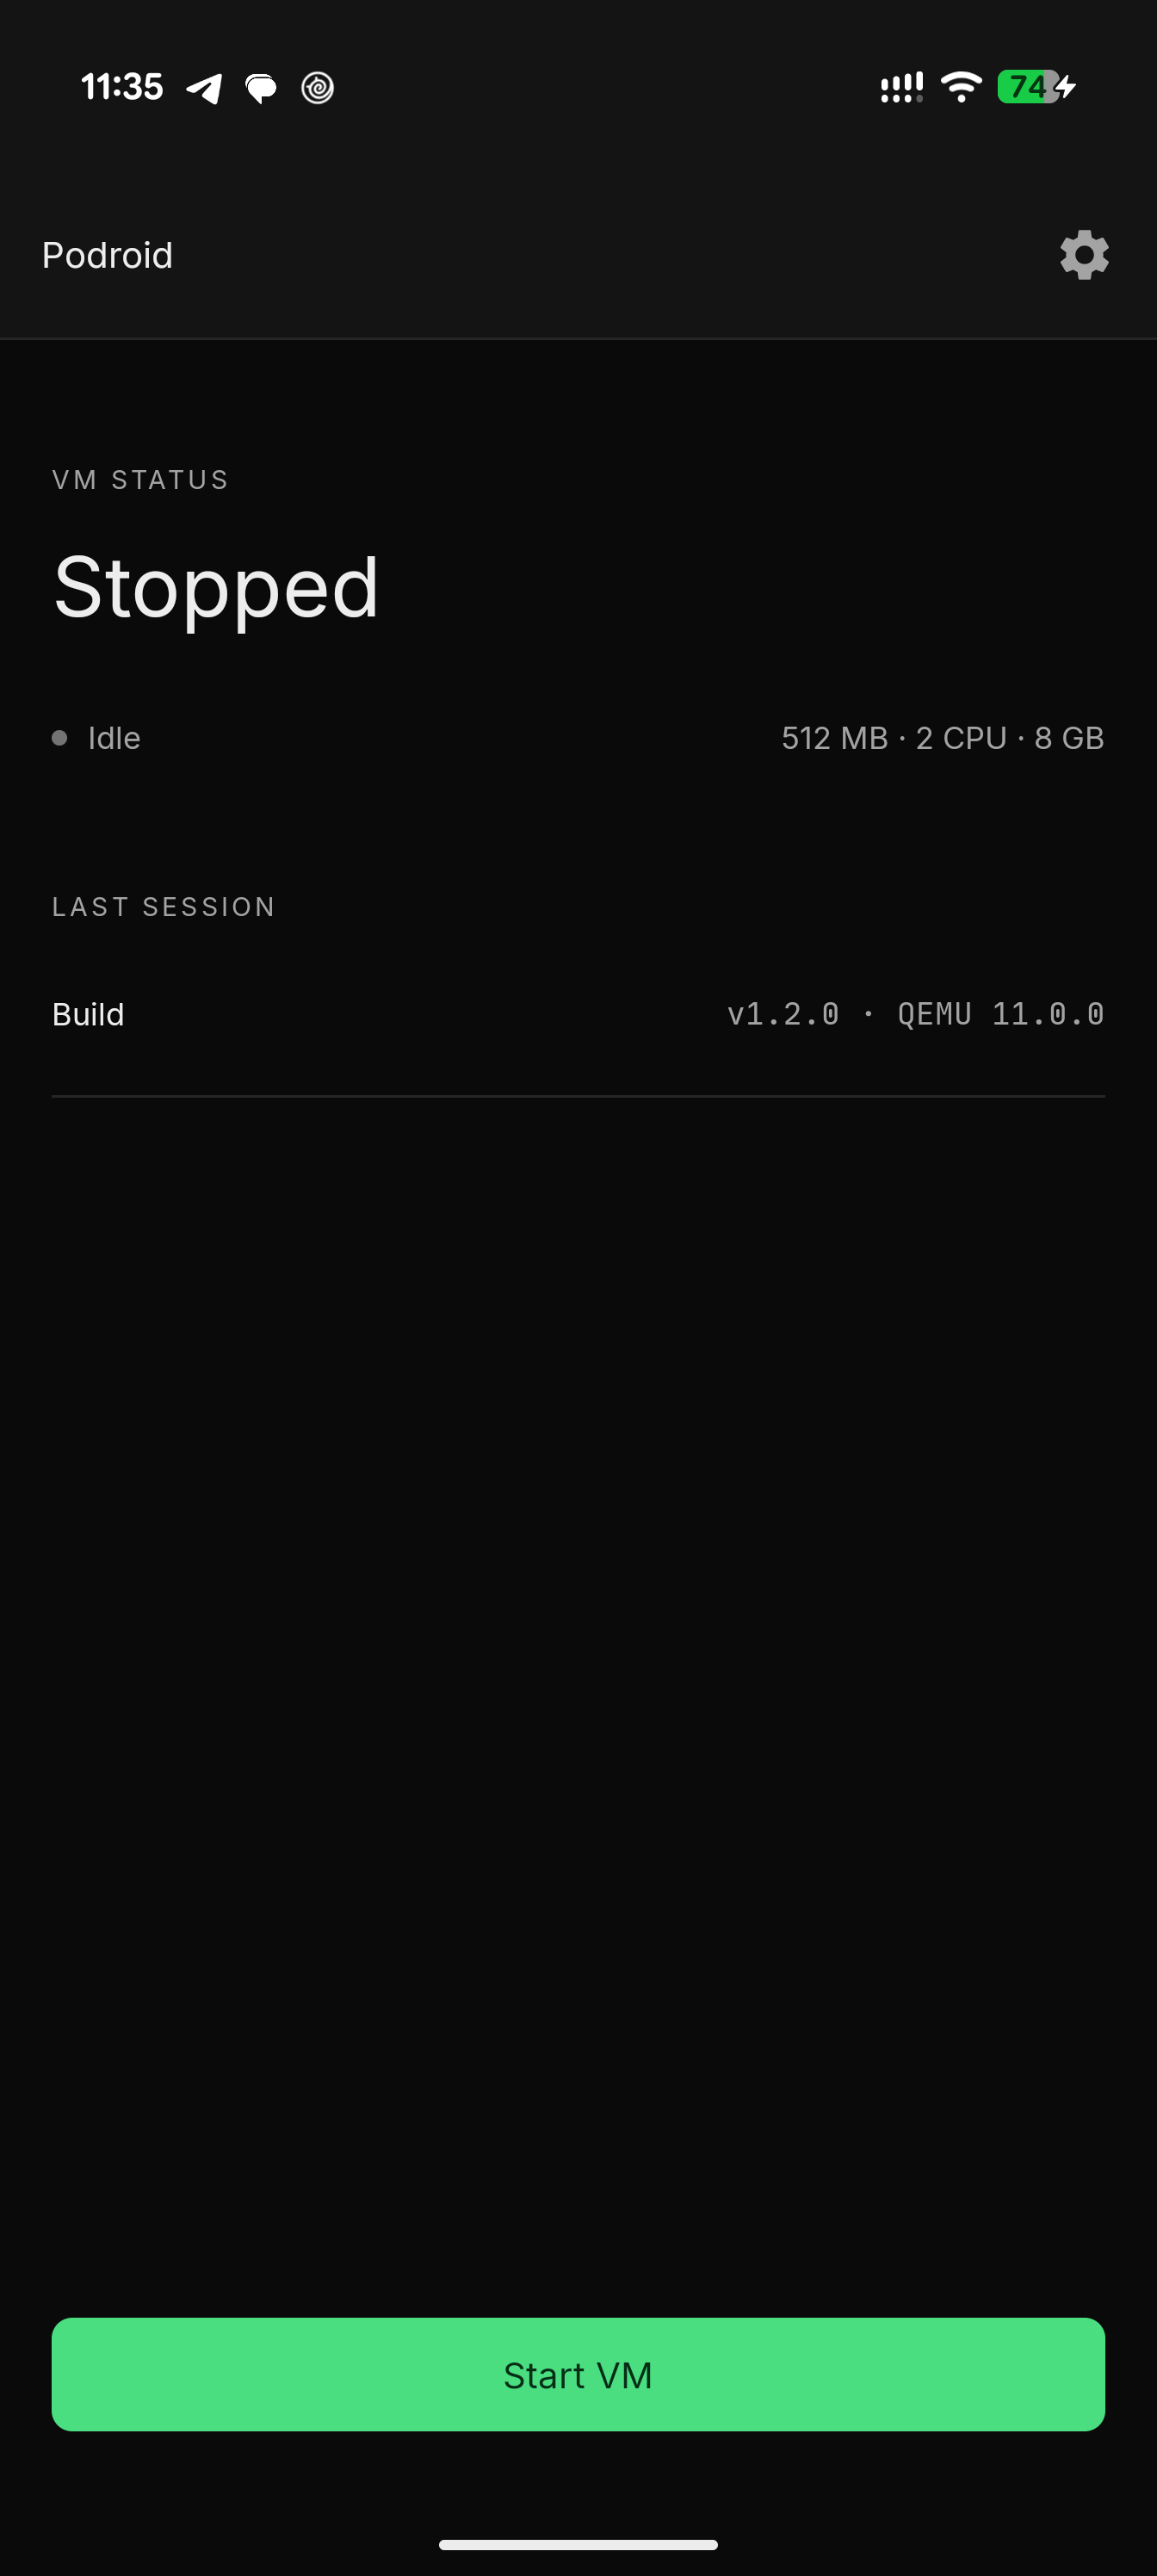 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
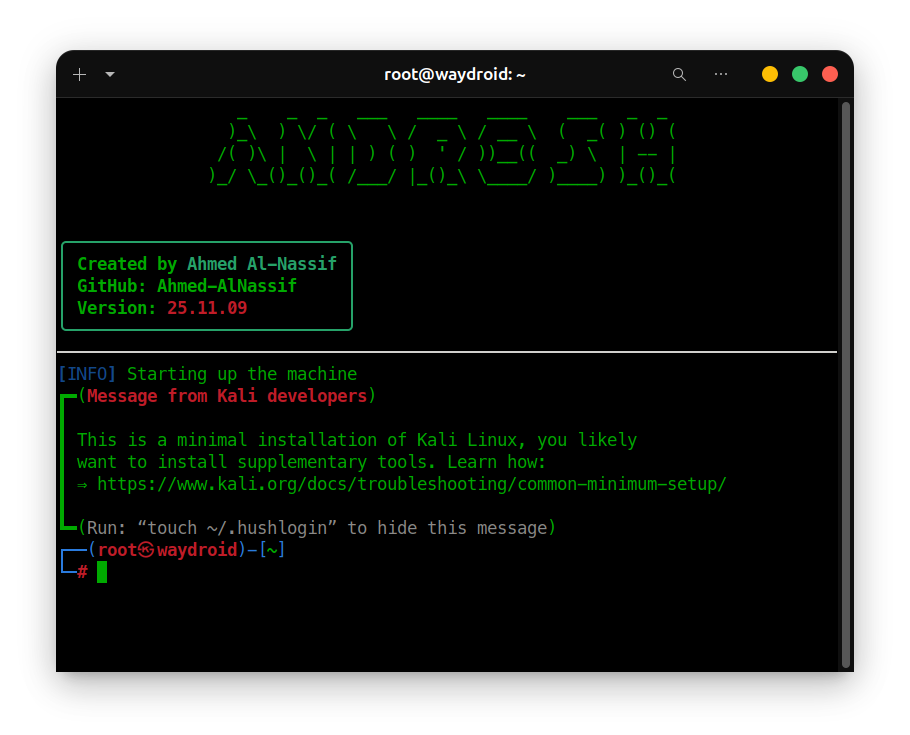 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 thespeedx/tbomb
This is a SMS And Call Bomber For Linux And Termux
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 uazo/cromite
Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.