
ghostlock-aresin
 nothingfumo/ghostlock-aresin
GhostLock (CVE-2026-43499) exploit for POCO F3 GT (aresin) — MediaTek Dimensity 1200, Linux 4.14.186 ARM64 kernel privilege escalation via futex PI…
android-securitybinary-exploitationexploitation+4
12
nothingfumo/ghostlock-aresinGhostLock (CVE-2026-43499) exploit for POCO F3 GT (aresin) — MediaTek Dimensity 1200, Linux 4.14.186 ARM64 kernel privilege escalation via futex PI…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 dangtunguyen/towelroot
Gain root privilege by exploiting CVE-2014-3153 vulnerability
 filipkarc/poc-ubuntutouch-pin-privesc
CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce
 petalrain224/cve-2026-43499-redmi-turbo5
Use CVE-2026-43499 on Redmi Turbo 5 to escalate privilege
 soralis0912/cve-2026-43499-aristotle
Local privilege escalation exploit for Xiaomi XIG04 (Android 12) via CVE-2026-43499 kernel use-after-free. Data-only direct-root technique with MTE…
 mouseos/cve-2019-2215_sh-m08
Proof-of-concept exploit for CVE-2019-2215 targeting Android kernel to achieve root privilege escalation on AQUOS sense 2 (SH-M08). Includes kernel…
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
 woshimaniubi8/cve-2026-43499-root-kernelsu
基于内核漏洞CVE-2026-43499的本地提权适配,集成嵌入式 KernelSU.CVE-2026-43499+KernelSU越狱模式
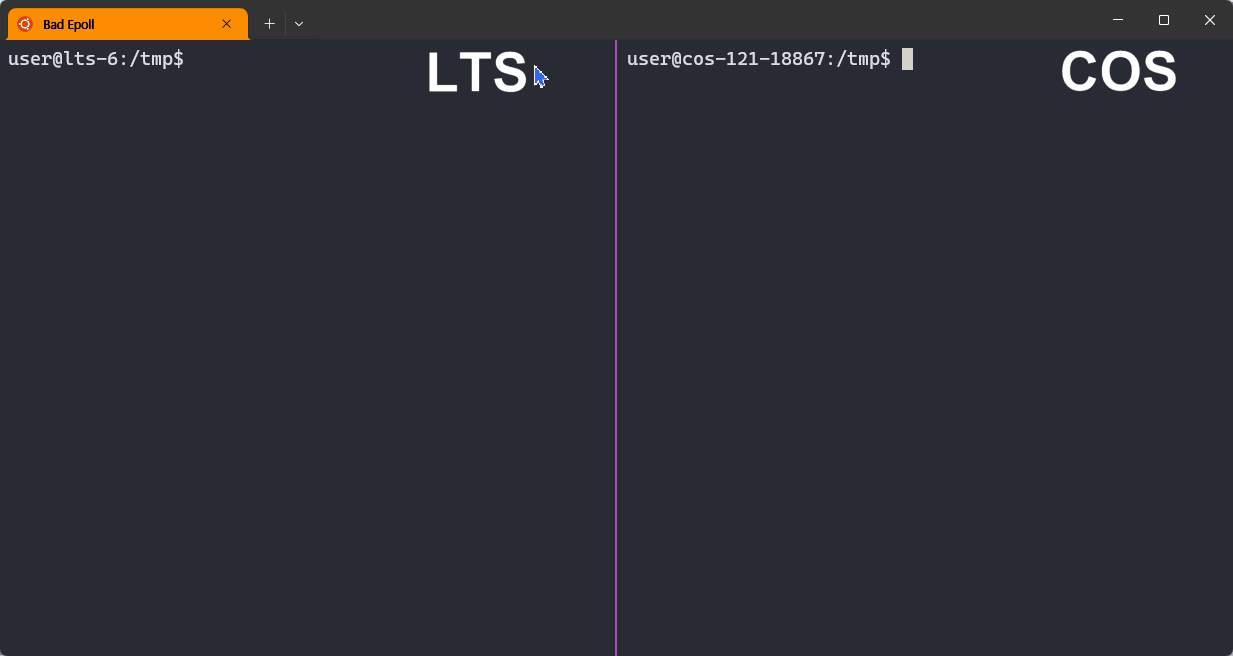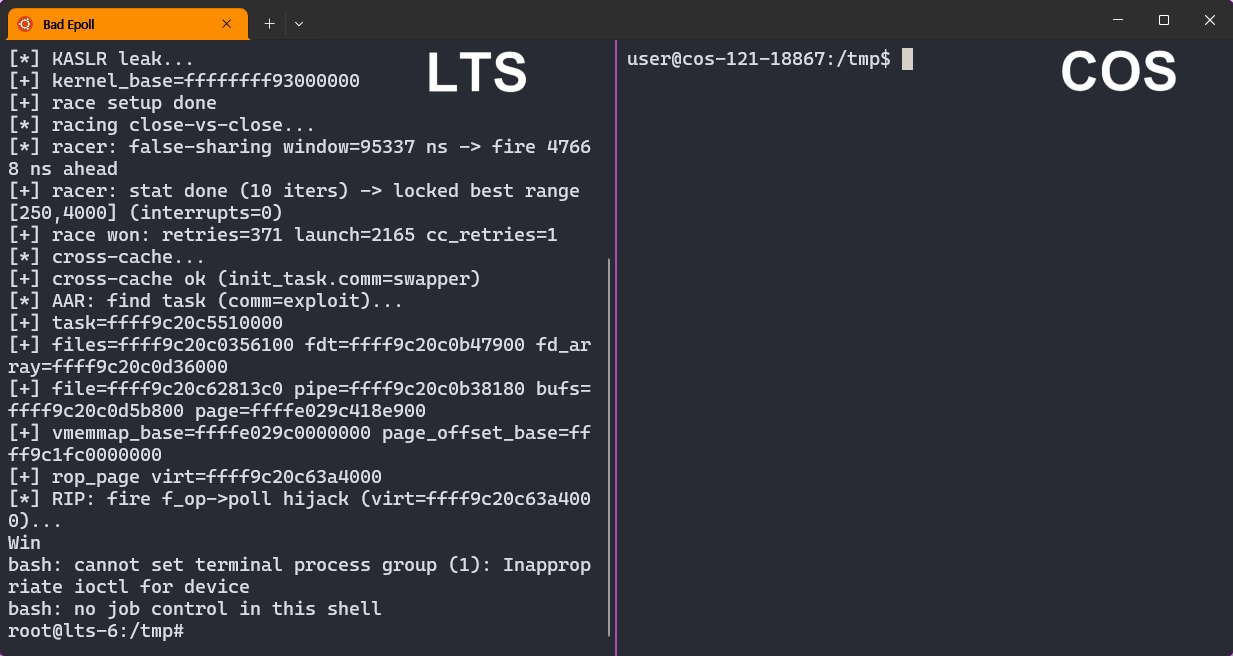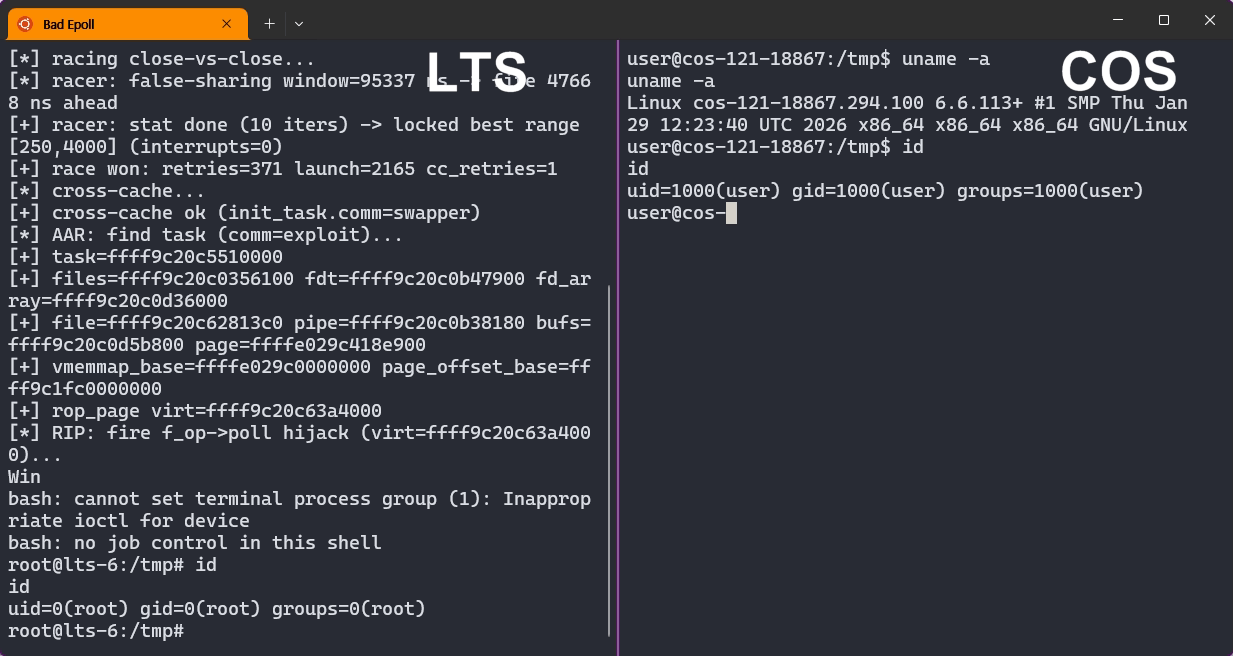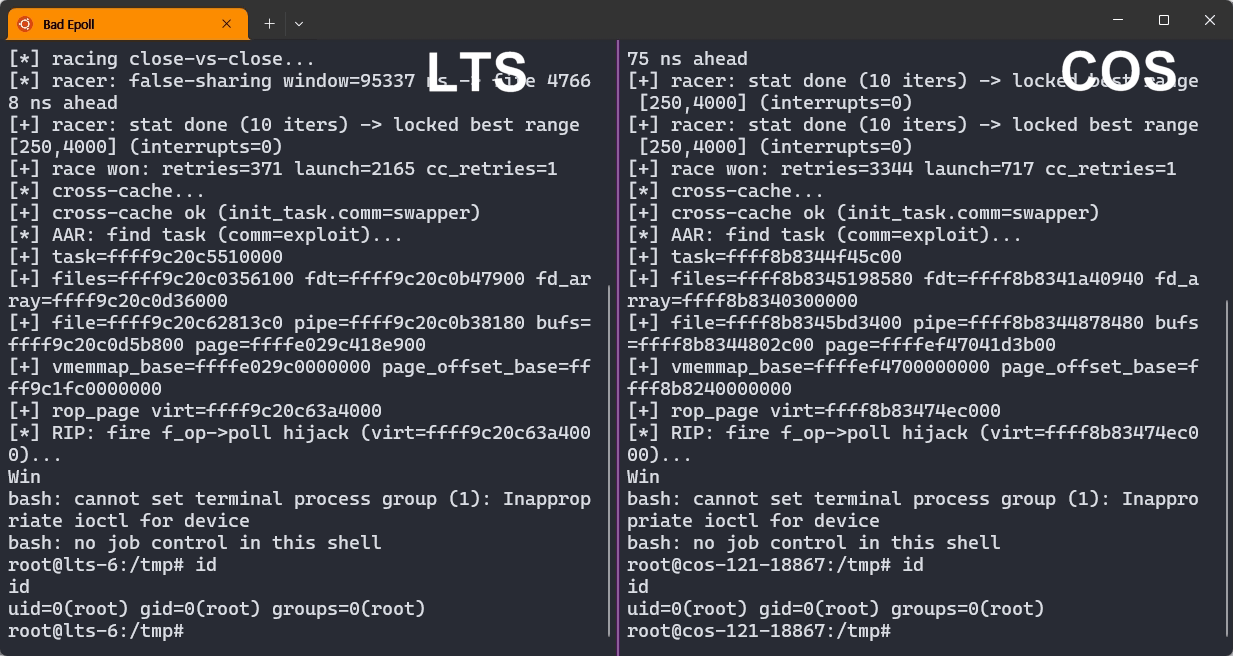 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 farazsth98/chronomaly
Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 szymonh/android-gadget
CVE-2022-20009 - Description and sample exploit for Android USB Gadgets
 nanopathi/system_bt_aosp10_r33_cve-2020-0225
Exploit for CVE-2020-0225 in the Android Fluoride Bluetooth stack, enabling remote code execution via a crafted Bluetooth packet. Includes build…
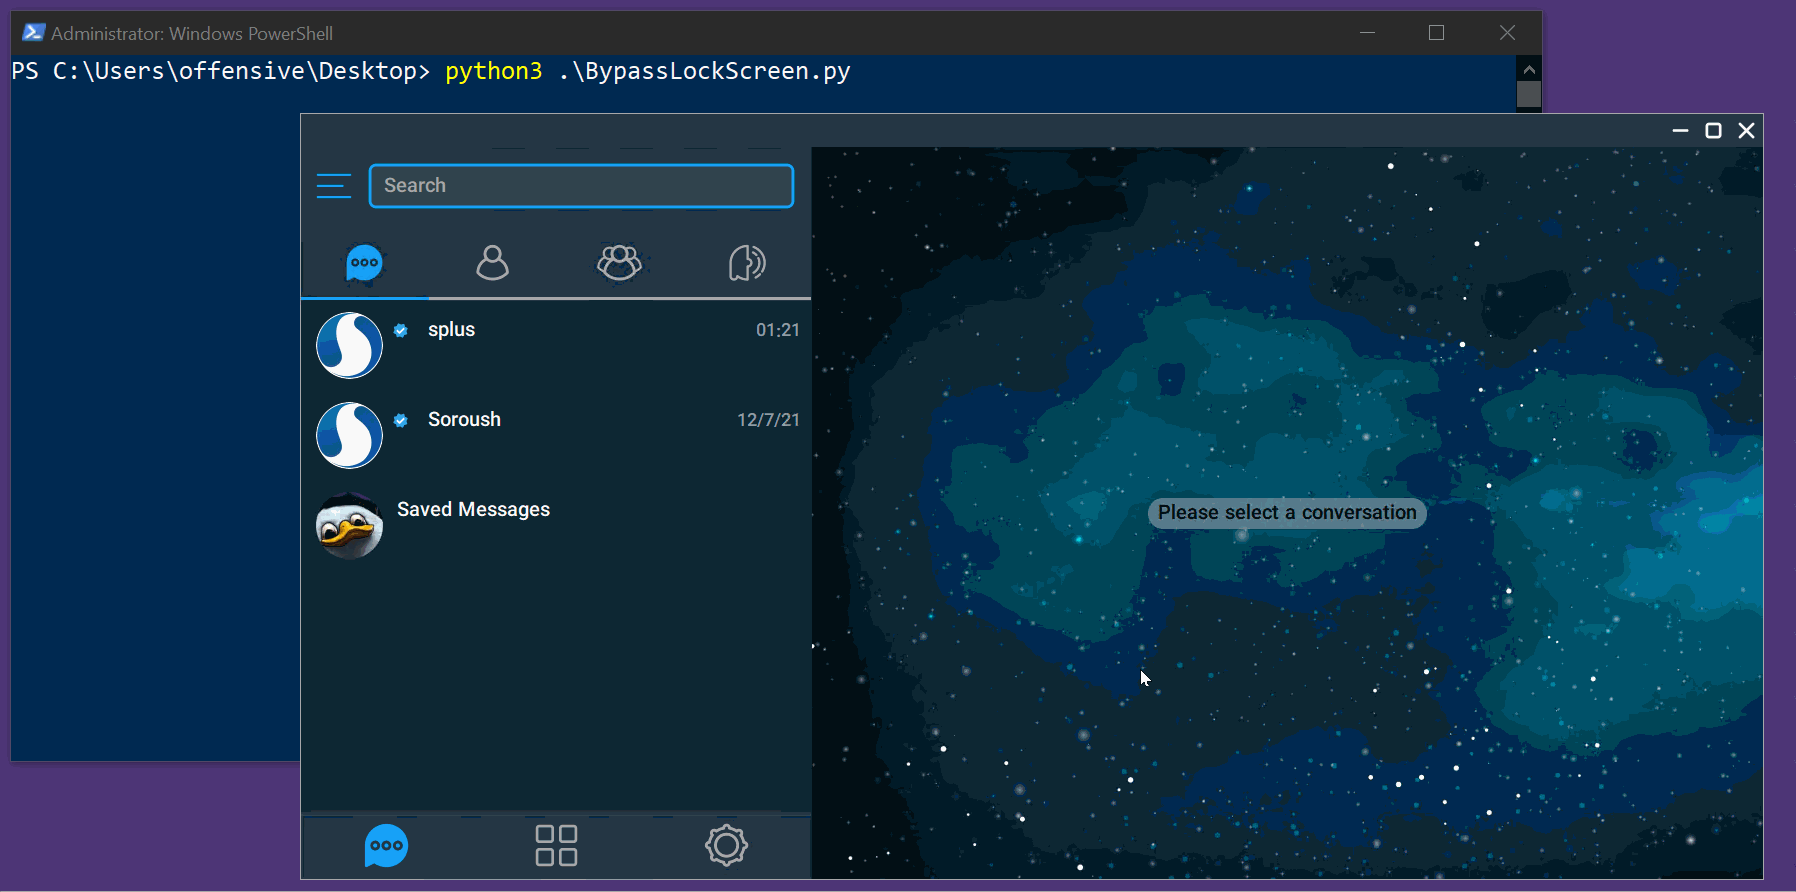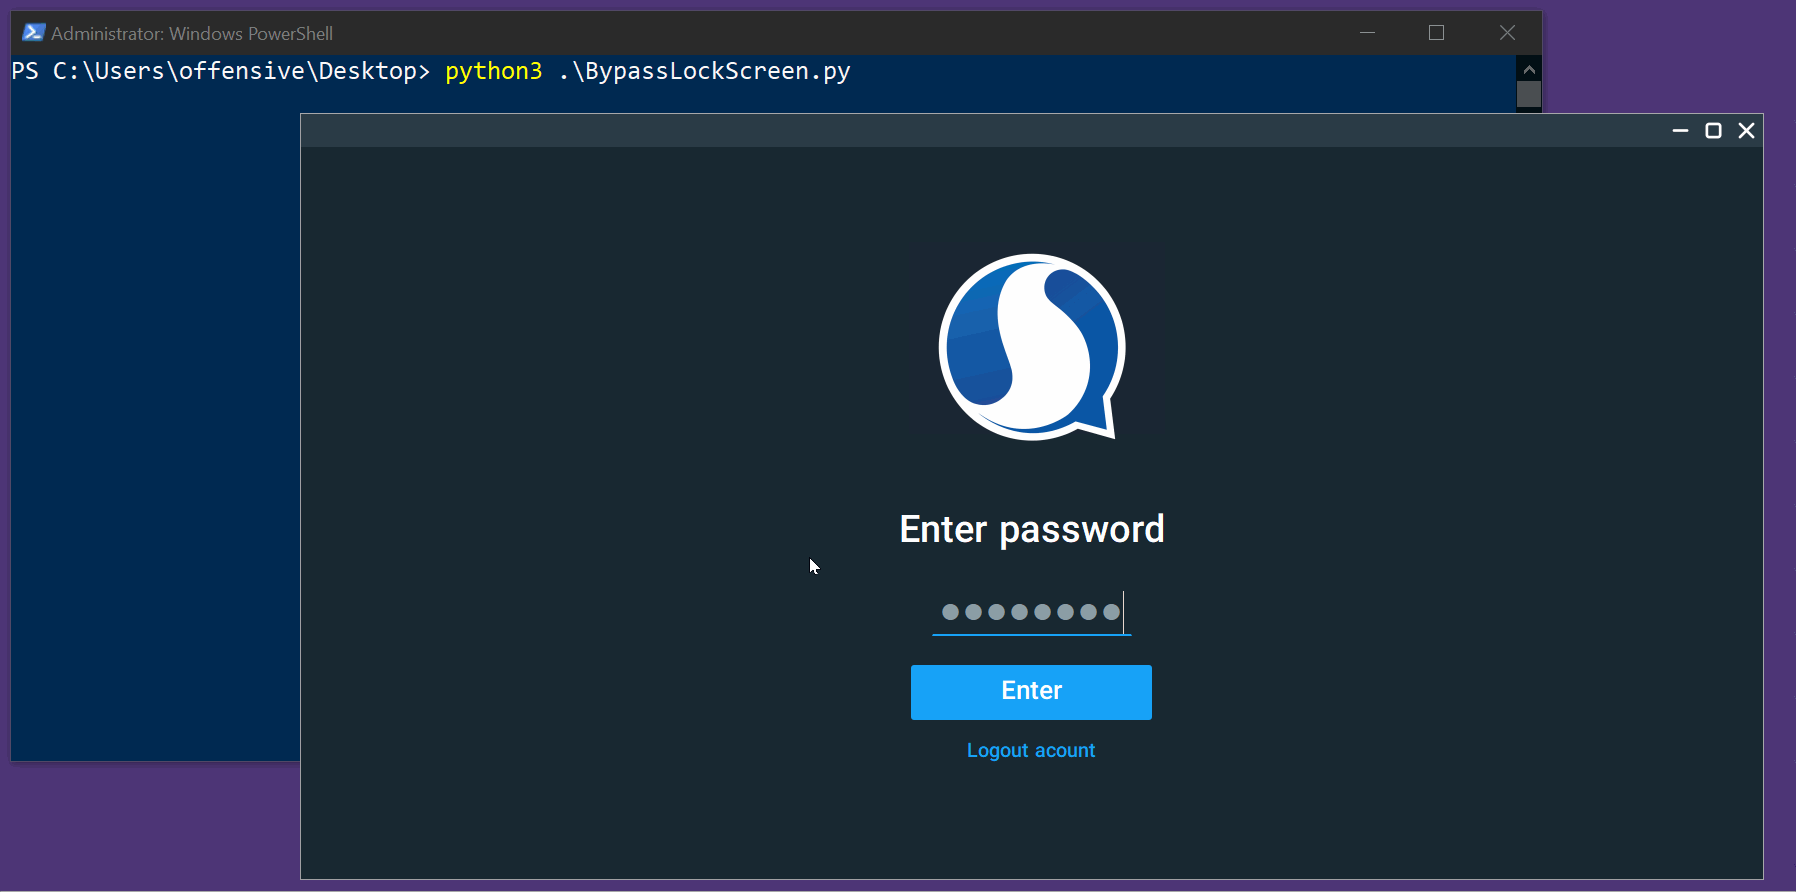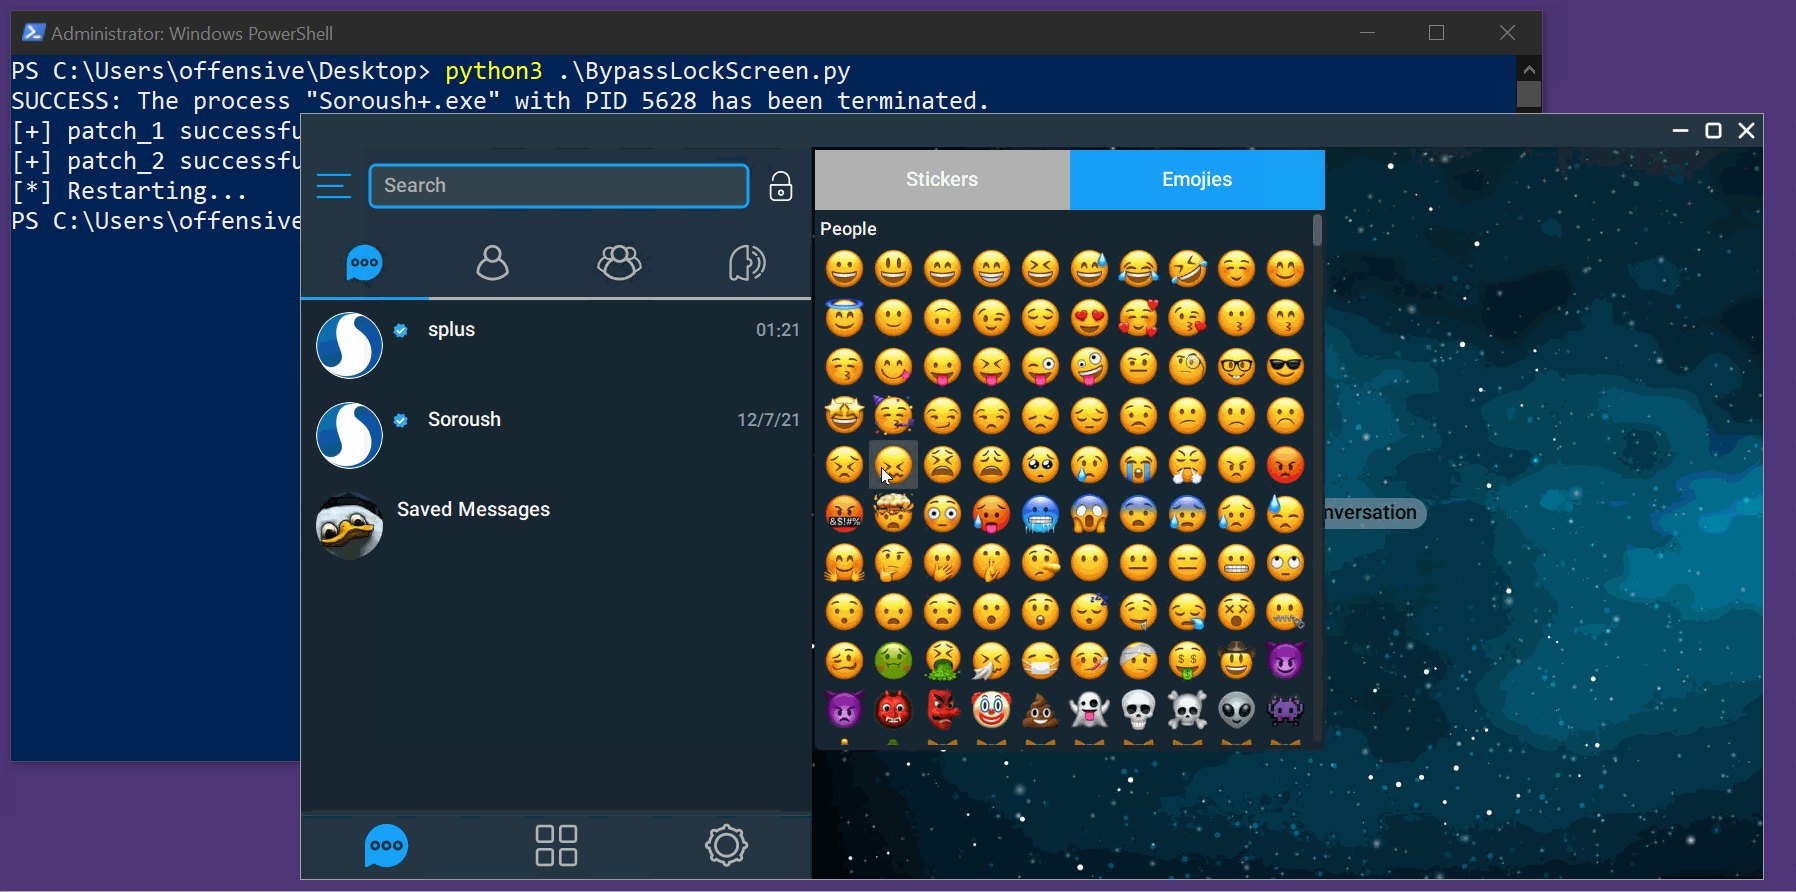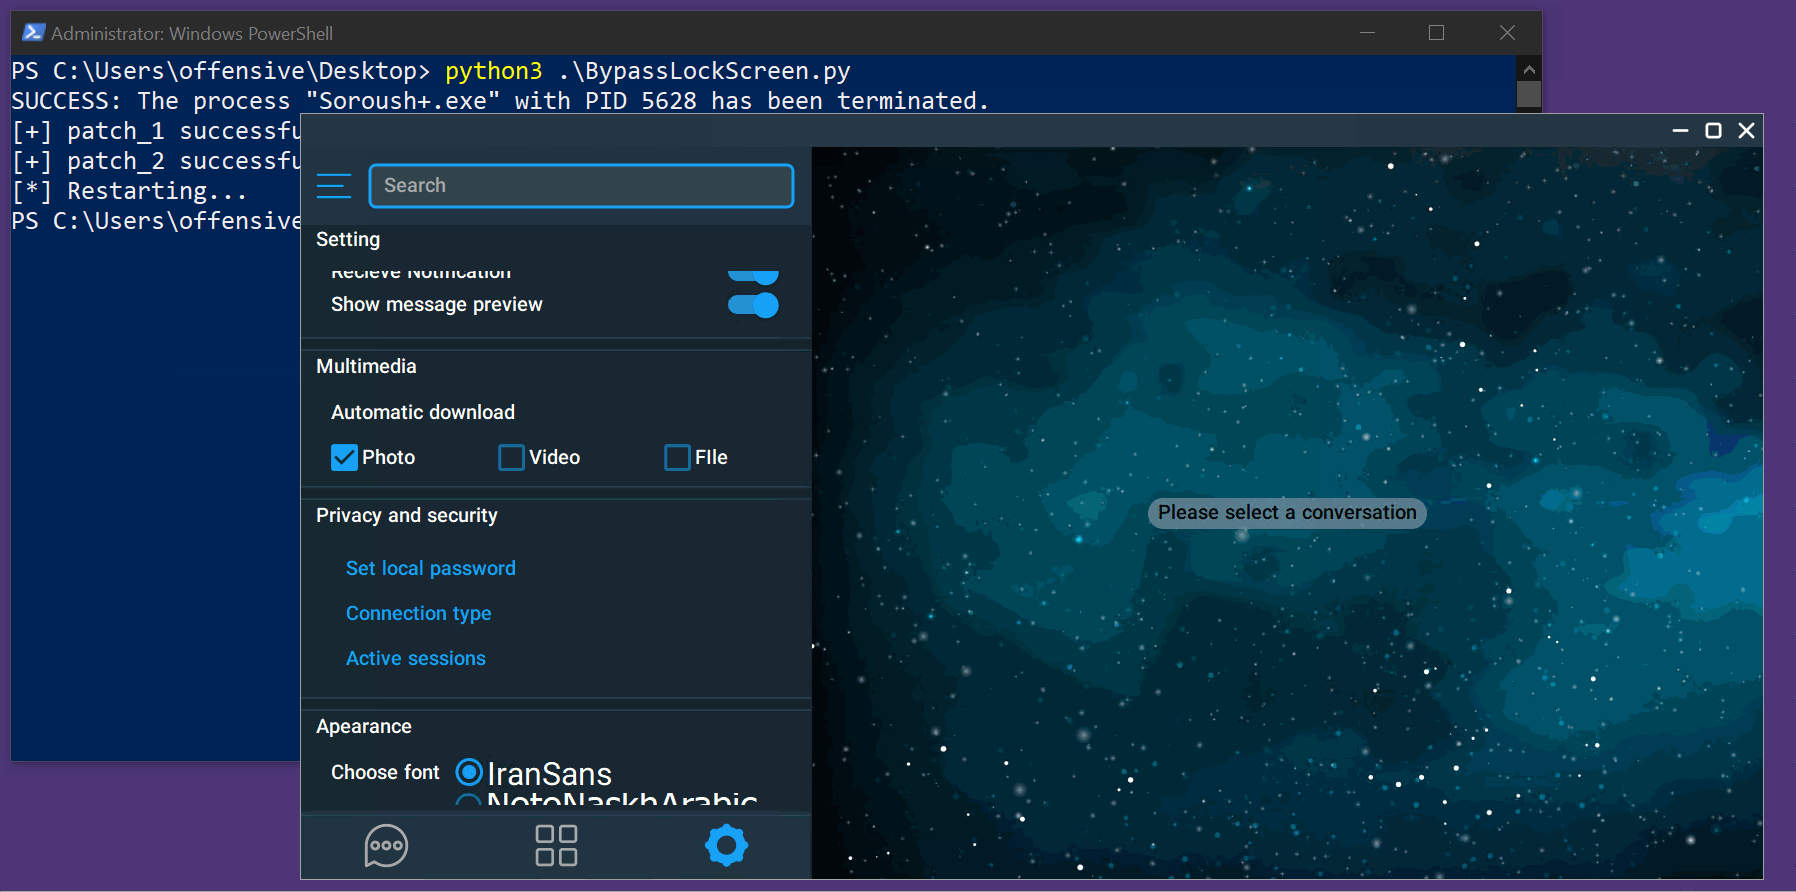 scopion/cve-2022-26629
PoC exploit for CVE-2022-26629: bypasses the lock screen on SoroushPlus+ Messenger 1.0.30 via improper access control. Includes an auto-exploit…