
Broadpwn
 mailinneberg/broadpwn
Broadpwn bug (CVE-2017-9417)
android-securityembedded-systems-securityexploitation+6
mailinneberg/broadpwnBroadpwn bug (CVE-2017-9417)
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

 guardianproject/tormobile/arti-mobile
Rust-based Tor library for Android and iOS, providing a standard API to integrate the Arti Tor runtime into mobile apps for private,…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 vaib25vicky/awesome-mobile-security
An effort to build a single place for all useful android and iOS security related stuff. All references and tools belong to their respective owners.…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 hahwul/mobilehackersweapons
Mobile Hacker's Weapons / A collection of cool tools used by Mobile hackers. Happy hacking , Happy bug-hunting
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 chichou/vscode-frida
Unofficial frida extension for VSCode
 romainthomas/the-poor-mans-obfuscator
Binary & scripts associated with "The Poor Man's Obfuscator" presentation
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
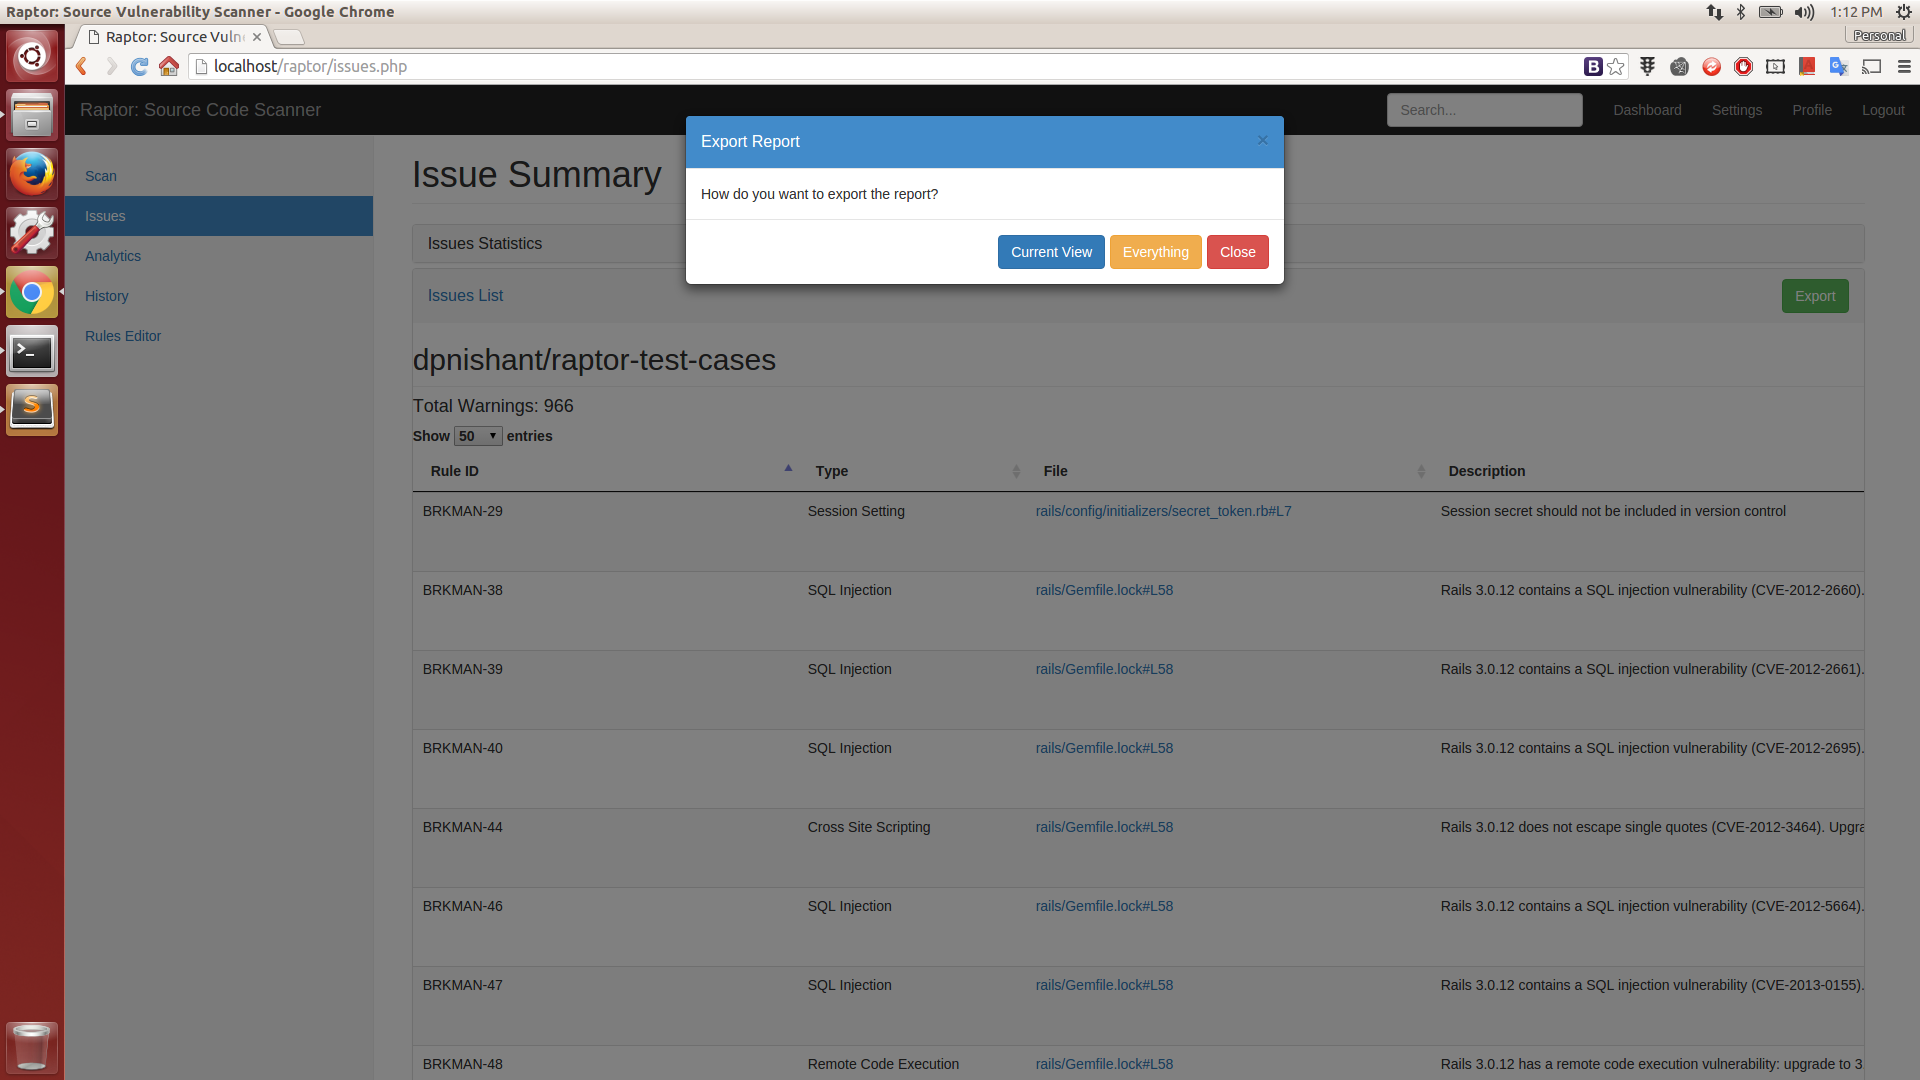 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
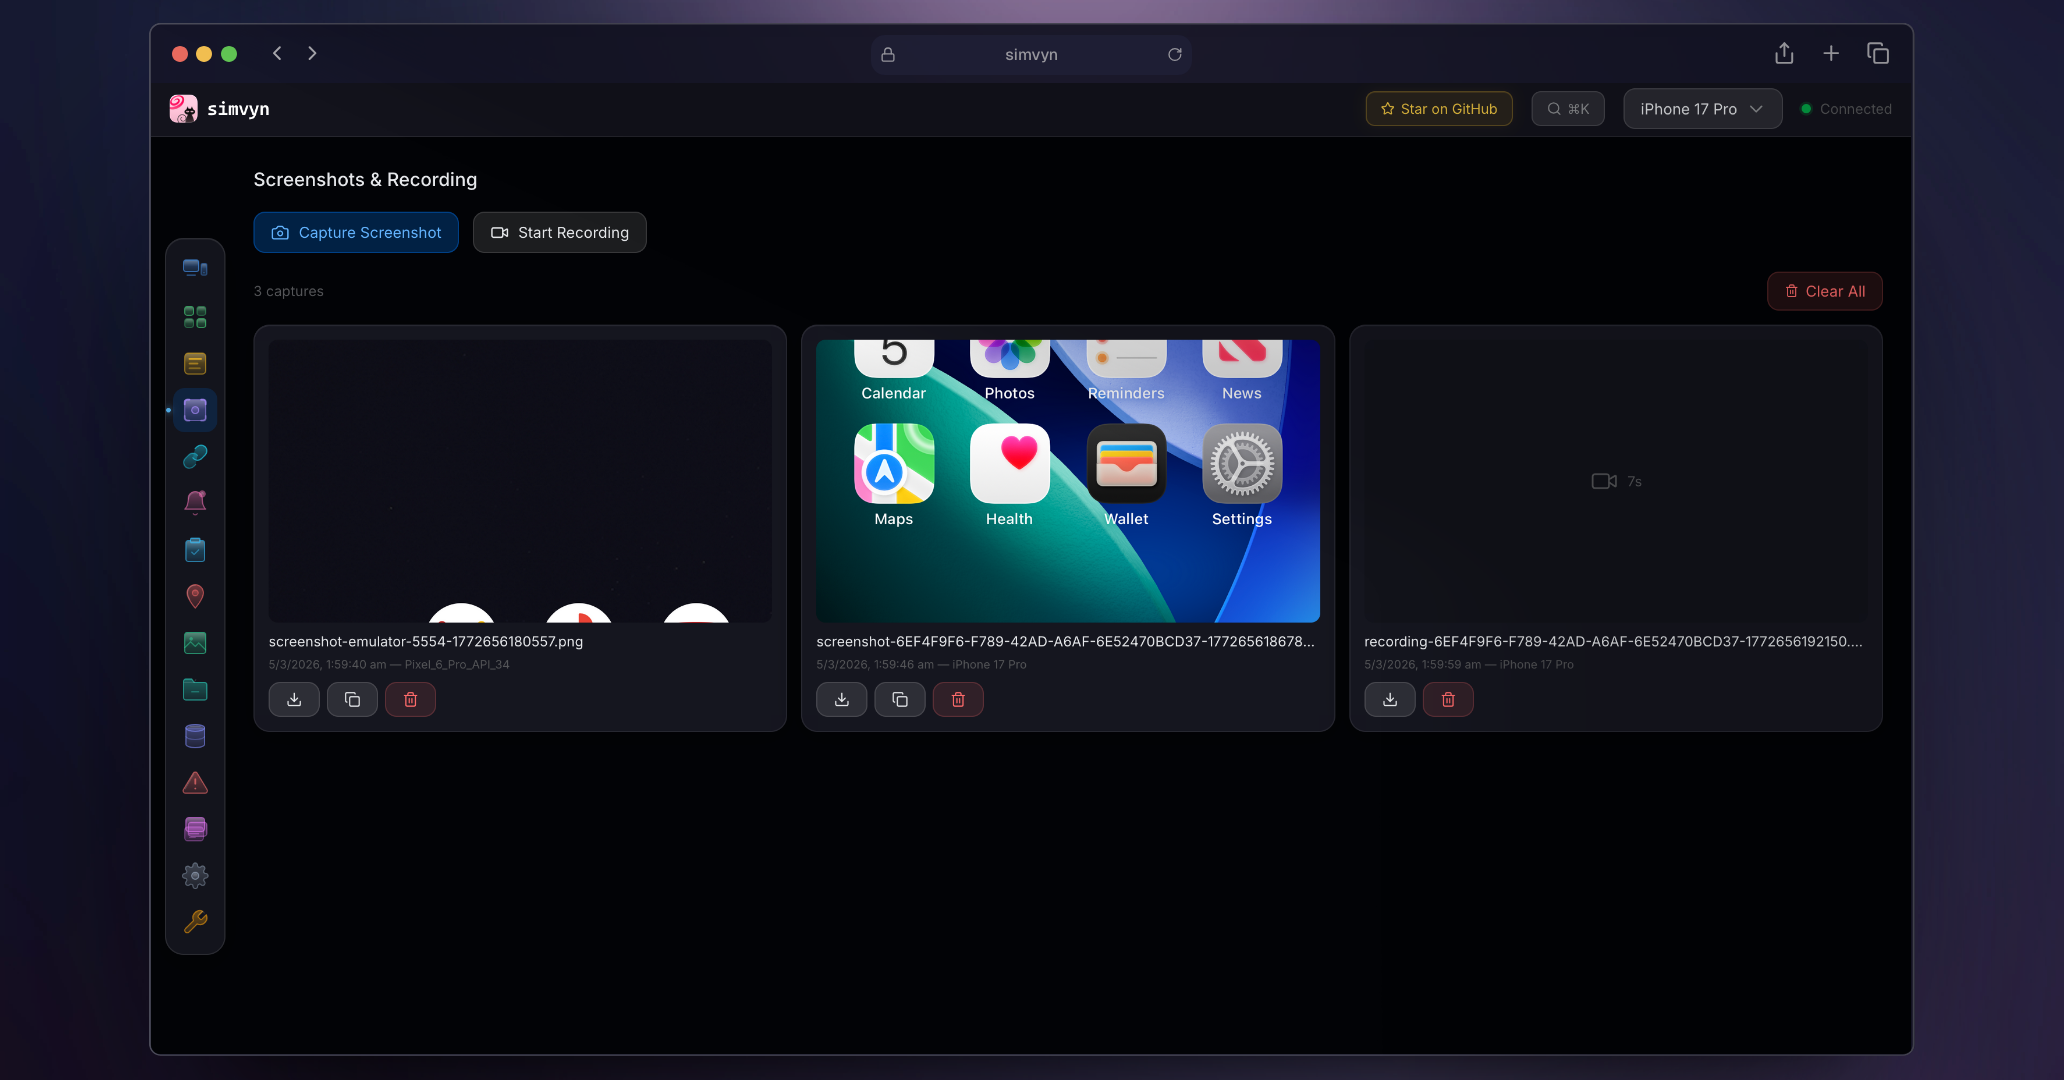 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI